
CVE-2025-69985
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
authentication-authorizationexploitationpayload-development+5
kaleth4/cve-2025-69985PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
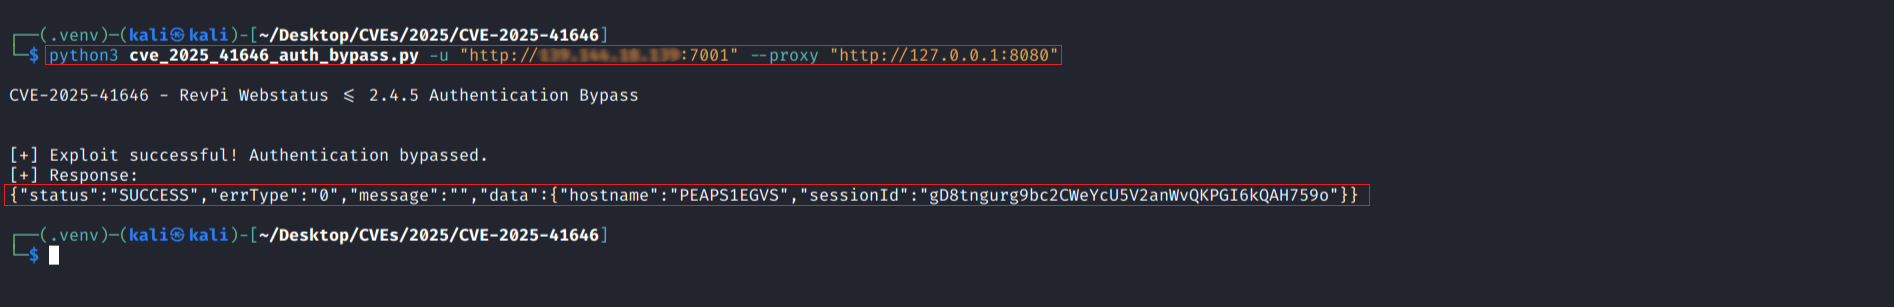 r0otk3r/cve-2025-41646
Python exploit script for CVE-2025-41646, an authentication bypass in RevPi Webstatus <= 2.4.5. Supports single/mass exploitation, proxy, silent…

 kavryxdev-group/enterprise-abac-gateway
Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.
 szybnev/cve-2026-20896-gitea-poc
CVE-2026-20896 Gitea Docker X-WEBAUTH-USER auth bypass checker
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
 covepseng/cve-2026-49352-poc
Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)
 goauthentik/authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…
 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software