CVE-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…

Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…

Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.

Wordpress REST API | Custom API Generator For Cross Platform And Import Export In WP 1.0.0 - 2.0.3 - Missing Authorization to Unauthenticated…

Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)

CVE-2025-31161

Just poc for CVE 2024-54085

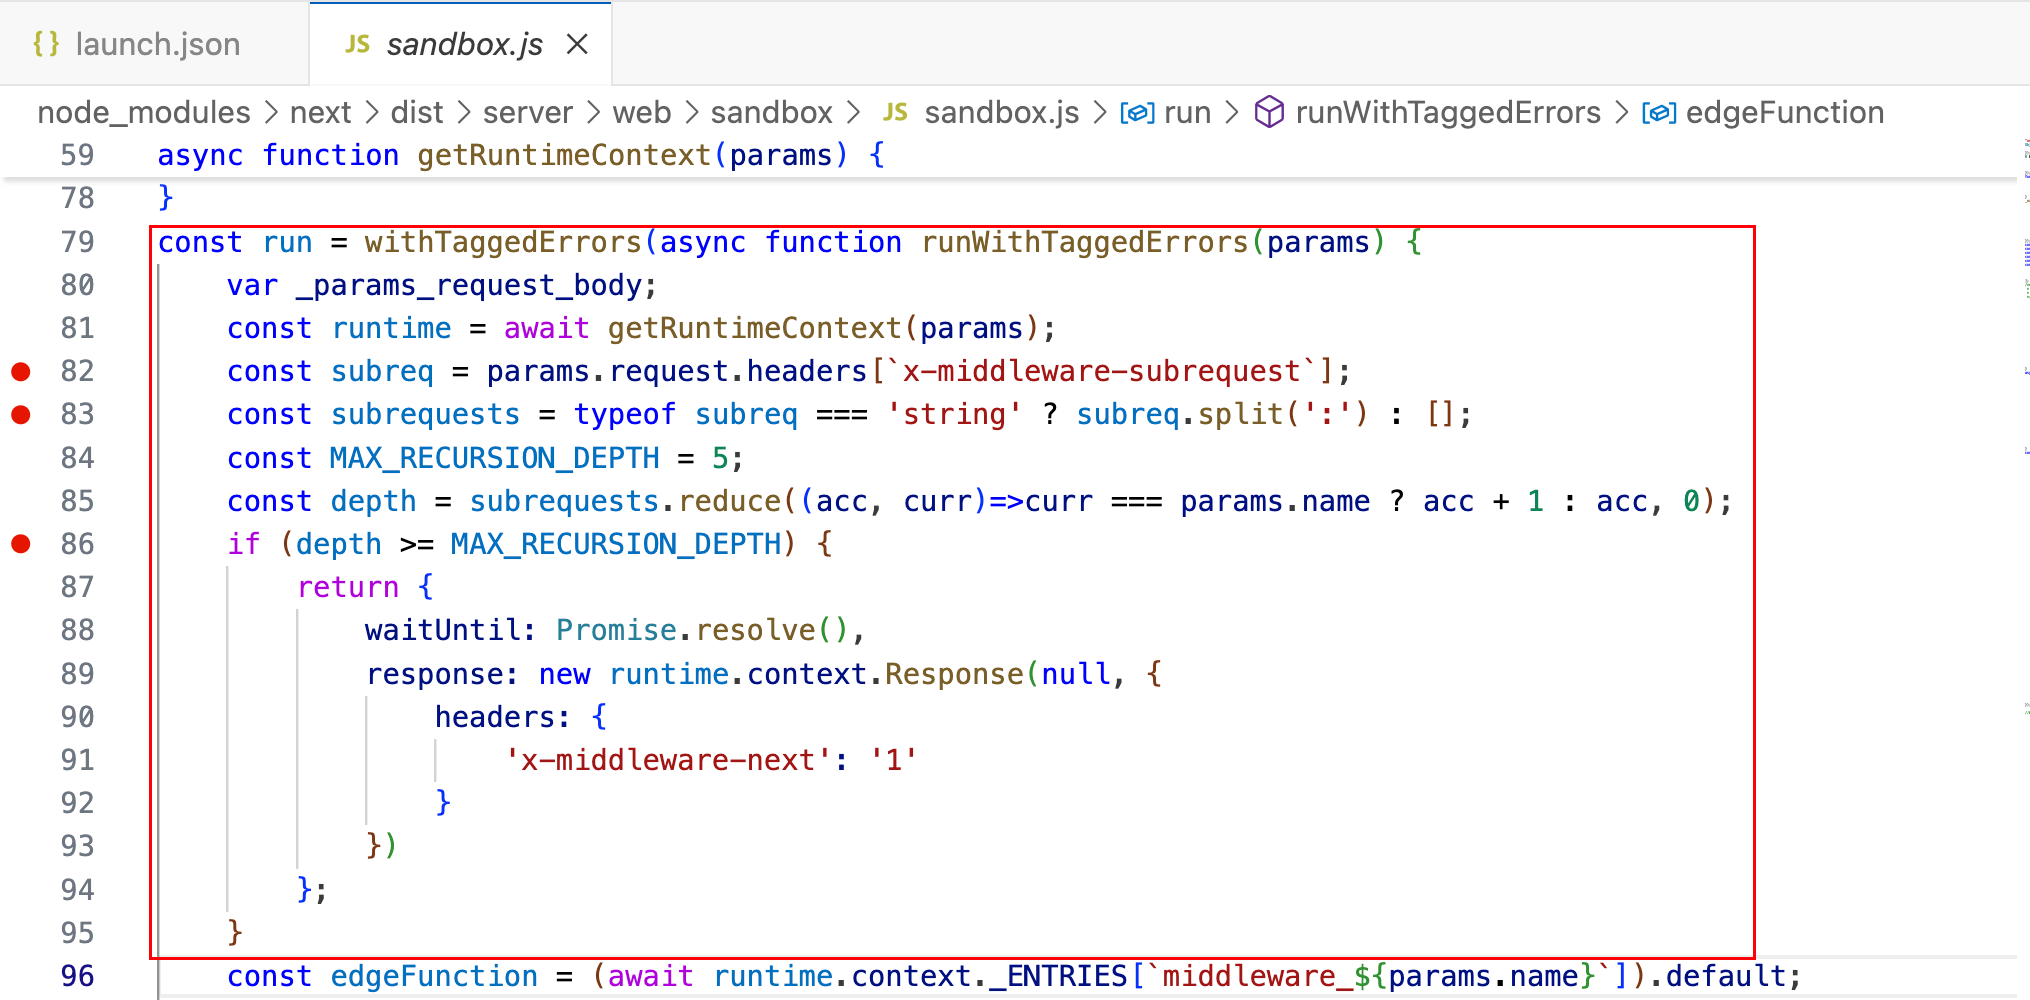
CVE-2025-29927 Authorization Bypass in Next.js Middleware

CVE-2026-82329 — JFrog Artifactory unauthenticated authentication bypass ("phantom join key" -> forged service admin token)

Next.js Middleware Auth Bypass

Exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM, allowing unauthenticated attackers to gain root access via session injection and…

0-Click RCE Android Adb TLS Wireless Debugging

Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…

Proof-of-concept exploit for CVE-2026-41940, a critical cPanel/WHM authentication bypass via CRLF injection, enabling unauthenticated root access and…

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token

A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys

Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…

Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…