
CVE-2026-34048
 0xmrma/cve-2026-34048
Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…
authentication-authorizationcloud-securitycommand-and-control+6
0xmrma/cve-2026-34048Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
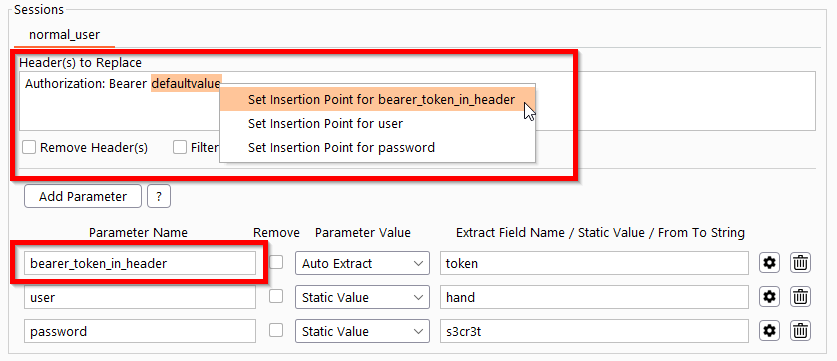 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
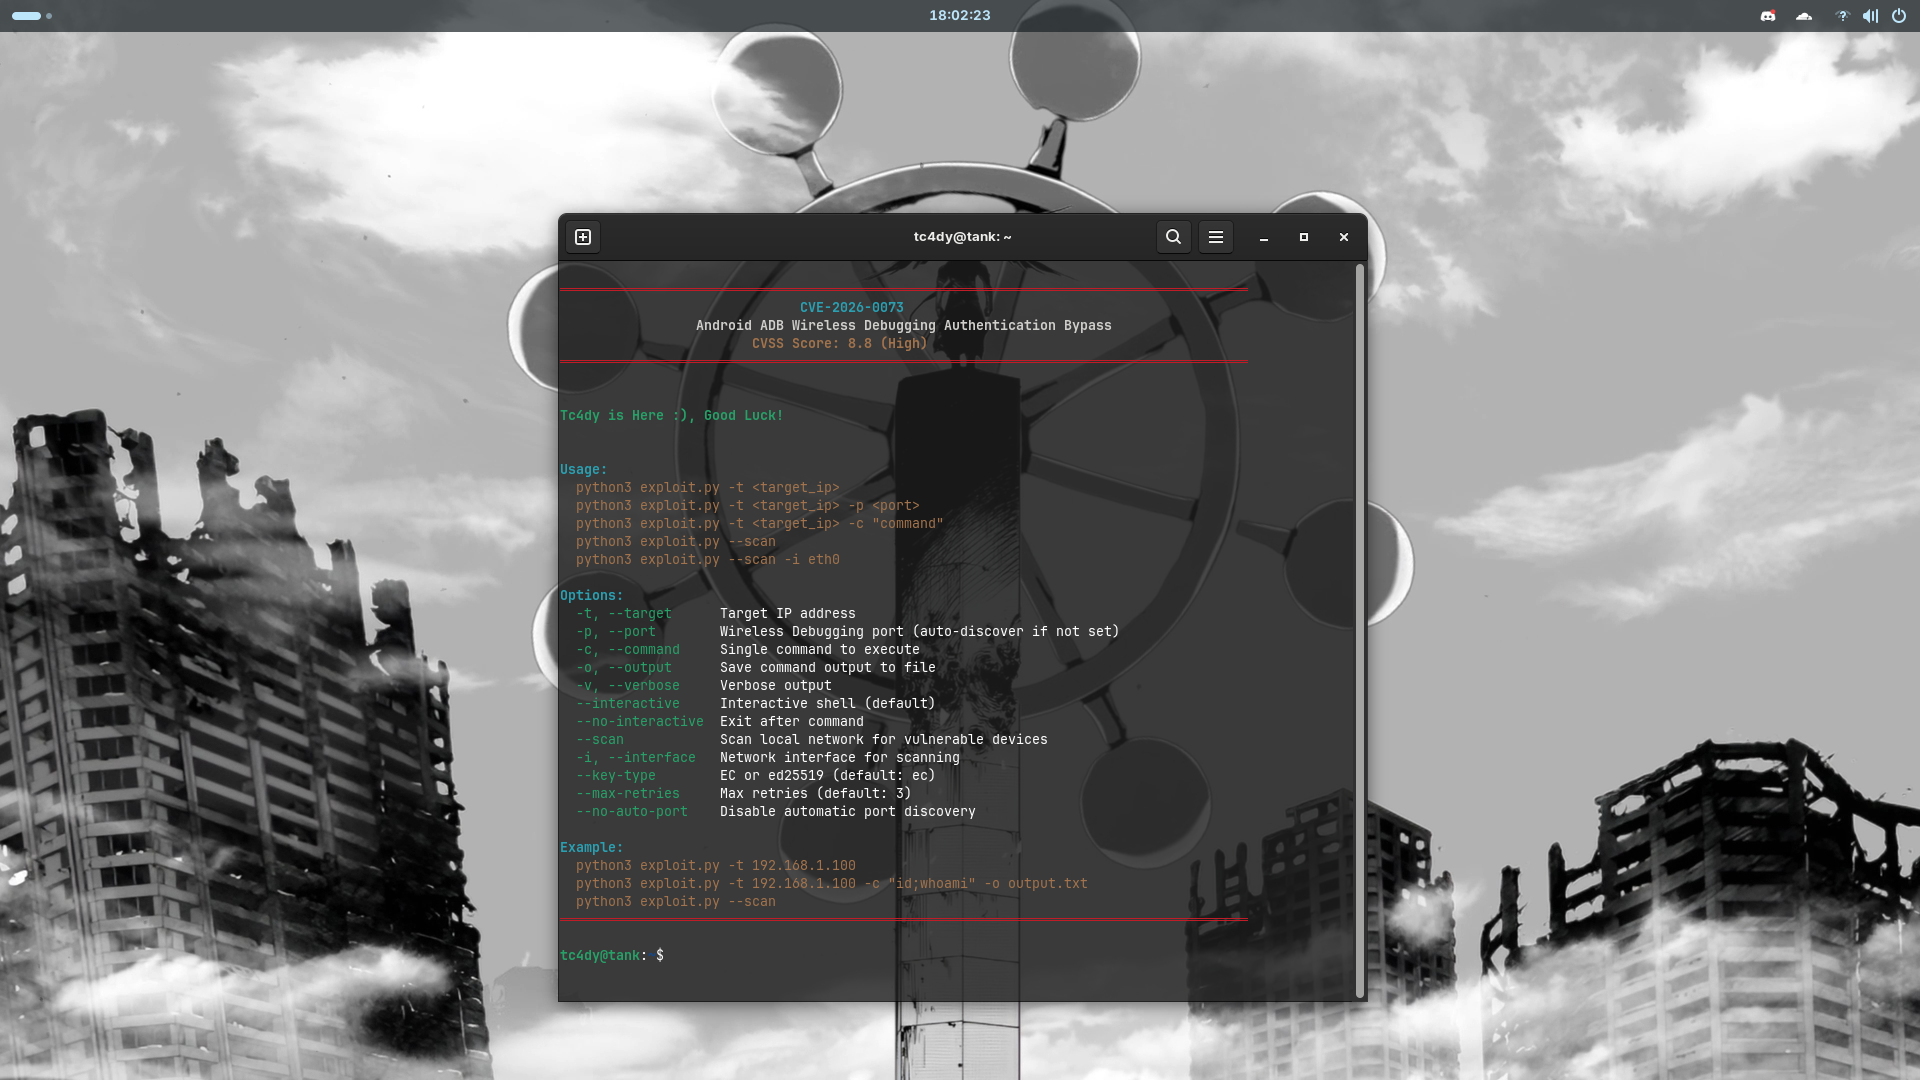 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 irsl/lgosp-poc
LG On Screen Phone authentication bypass PoC (CVE-2014-8757)
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 quarkslab/android-hardware-attestation-demo
An Android HW Attestation demo
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging