
CVE-2025-49901
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
authentication-authorizationexploitationpassword-attacks+3
nxploited/cve-2025-49901WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
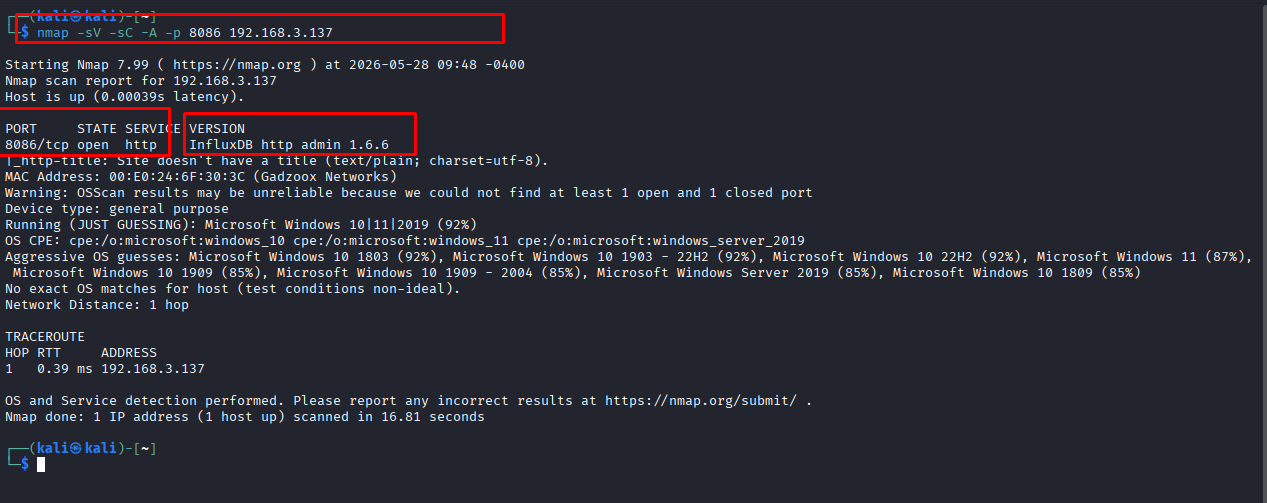 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 0xblackash/cve-2026-35616
CVE-2026-35616
 blueisbeautiful/cve-2025-54309
CrushFTP AS2 Authentication Bypass
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…
 randomrobbiebf/cve-2024-5324
Login/Signup Popup ( Inline Form + Woocommerce ) 2.7.1 - 2.7.2 - Missing Authorization to Arbitrary Options Update
 randomrobbiebf/cve-2024-52429
WP Quick Setup <= 2.0 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Plugin/Theme Installation
 jenderal92/owa-valid-login-checker
Owa Valid Login Checker
 randomrobbiebf/cve-2023-30486
Square <= 2.0.0 - Missing Authorization via activate_plugin
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 greenforcenetworks/cve-2025-41646---critical-authentication-bypass-
CVE-2025-41646 - Critical Authentication bypass
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
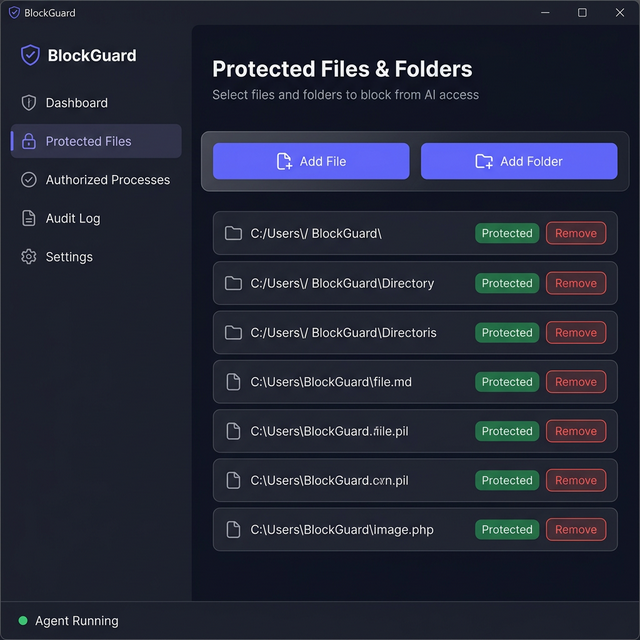 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 amalpvatayam67/day10-nextjs-middleware-lab
Next.js middleware auth-bypass lab (CVE-2025-29927 simulation)
 tanarchytan/cve-2021-1675
Fix without disabling Print Spooler
 shoucheng3/asf__karaf_cve-2022-22932_4-3-5
Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…