

pomerium
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
authenticationauthentication-authorizationcloud-security+6
5.0k
pomerium/pomeriumIdentity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
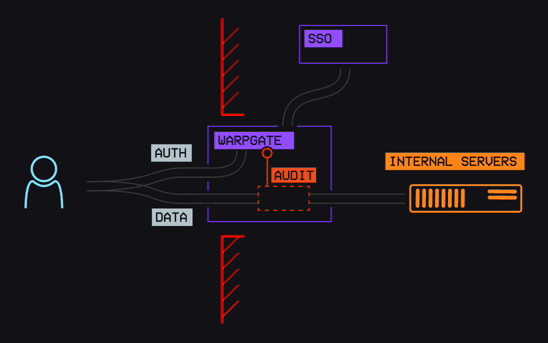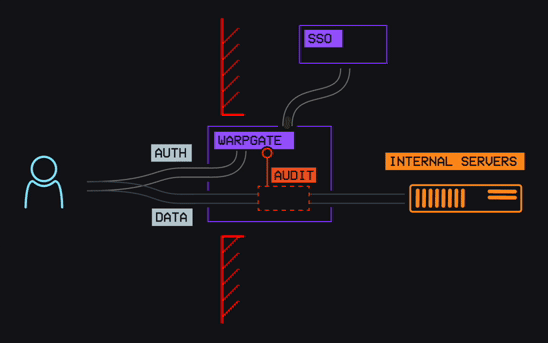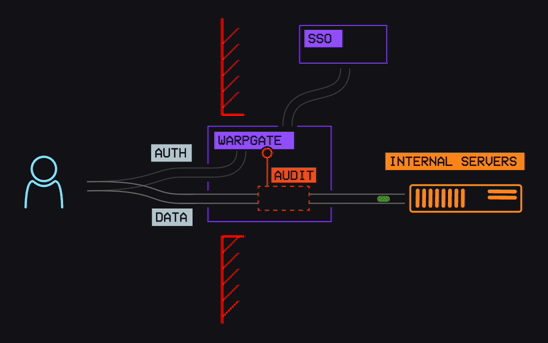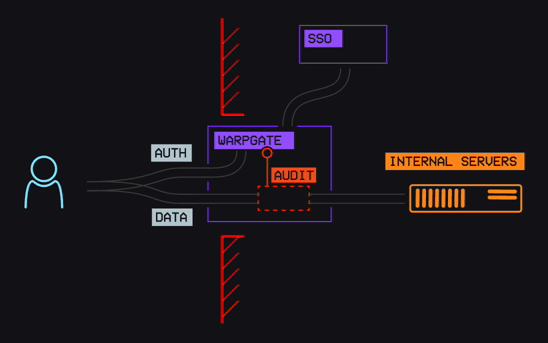 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
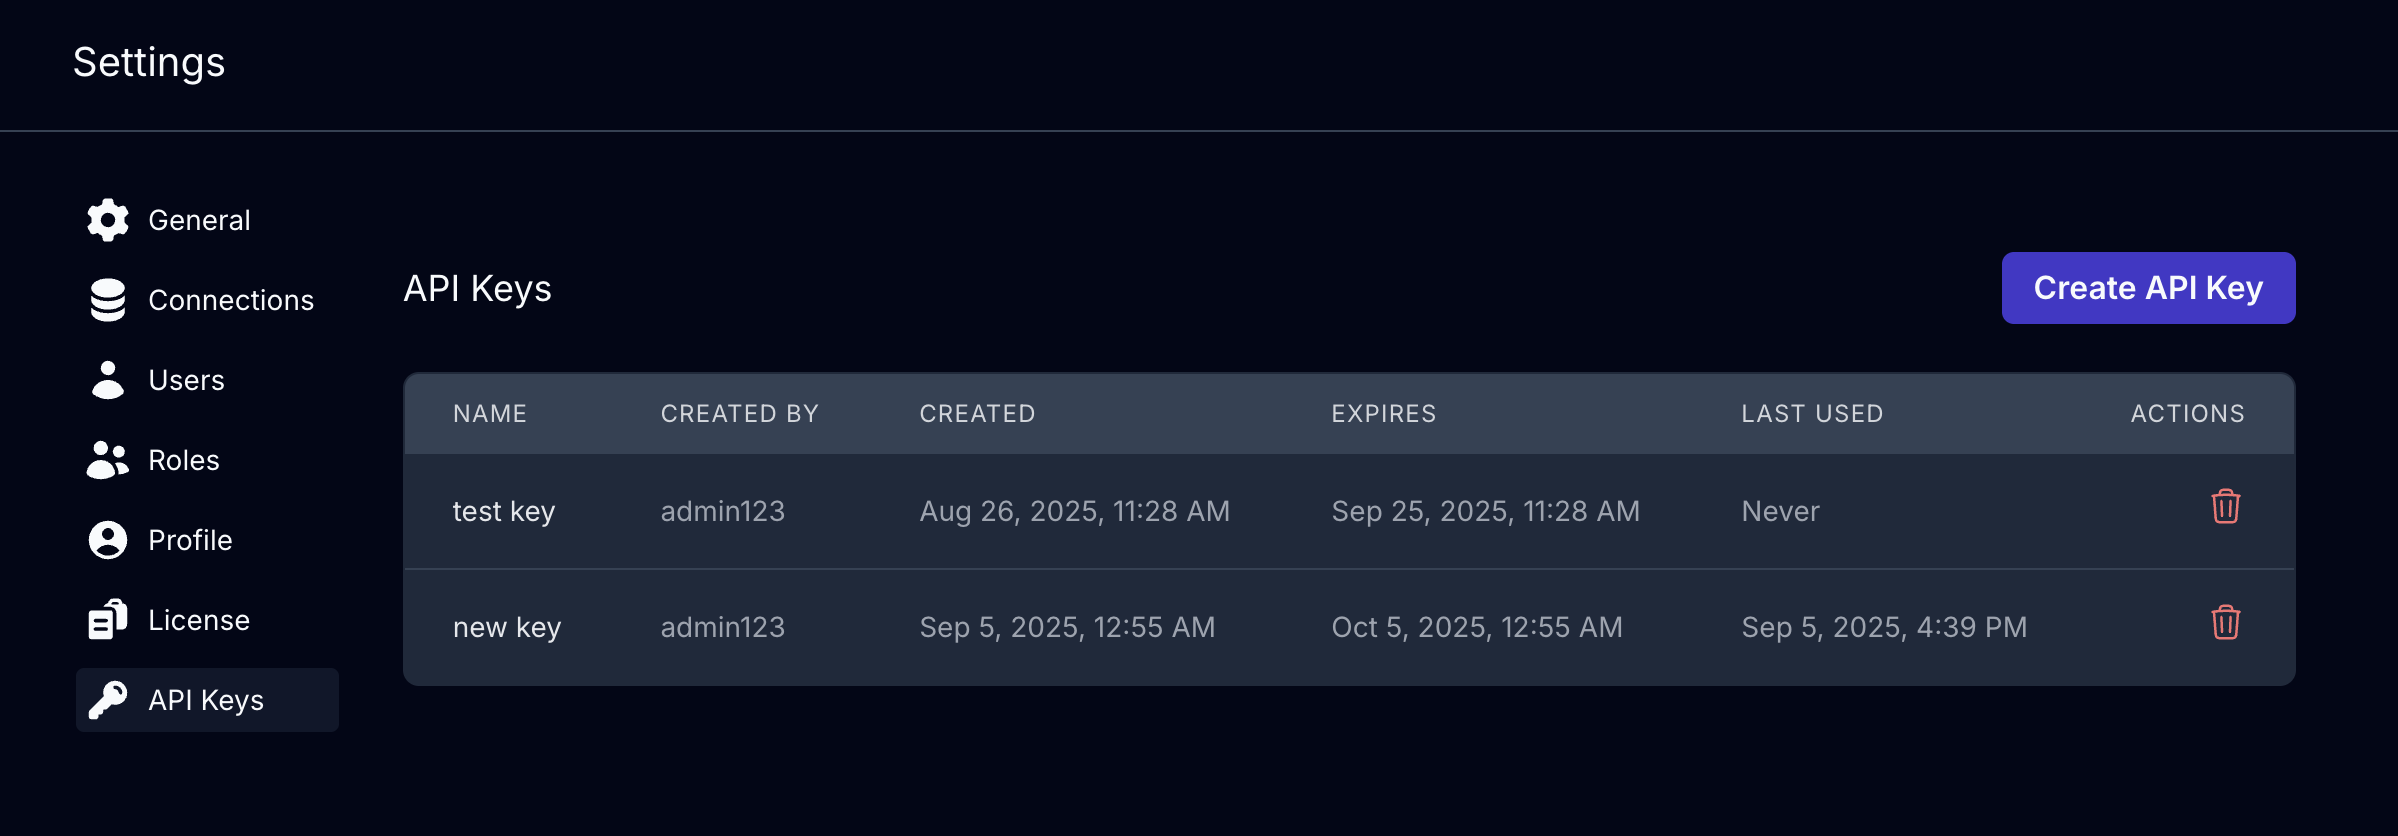 kviklet/kviklet
Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
 oauth2-proxy/oauth2-proxy
A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.
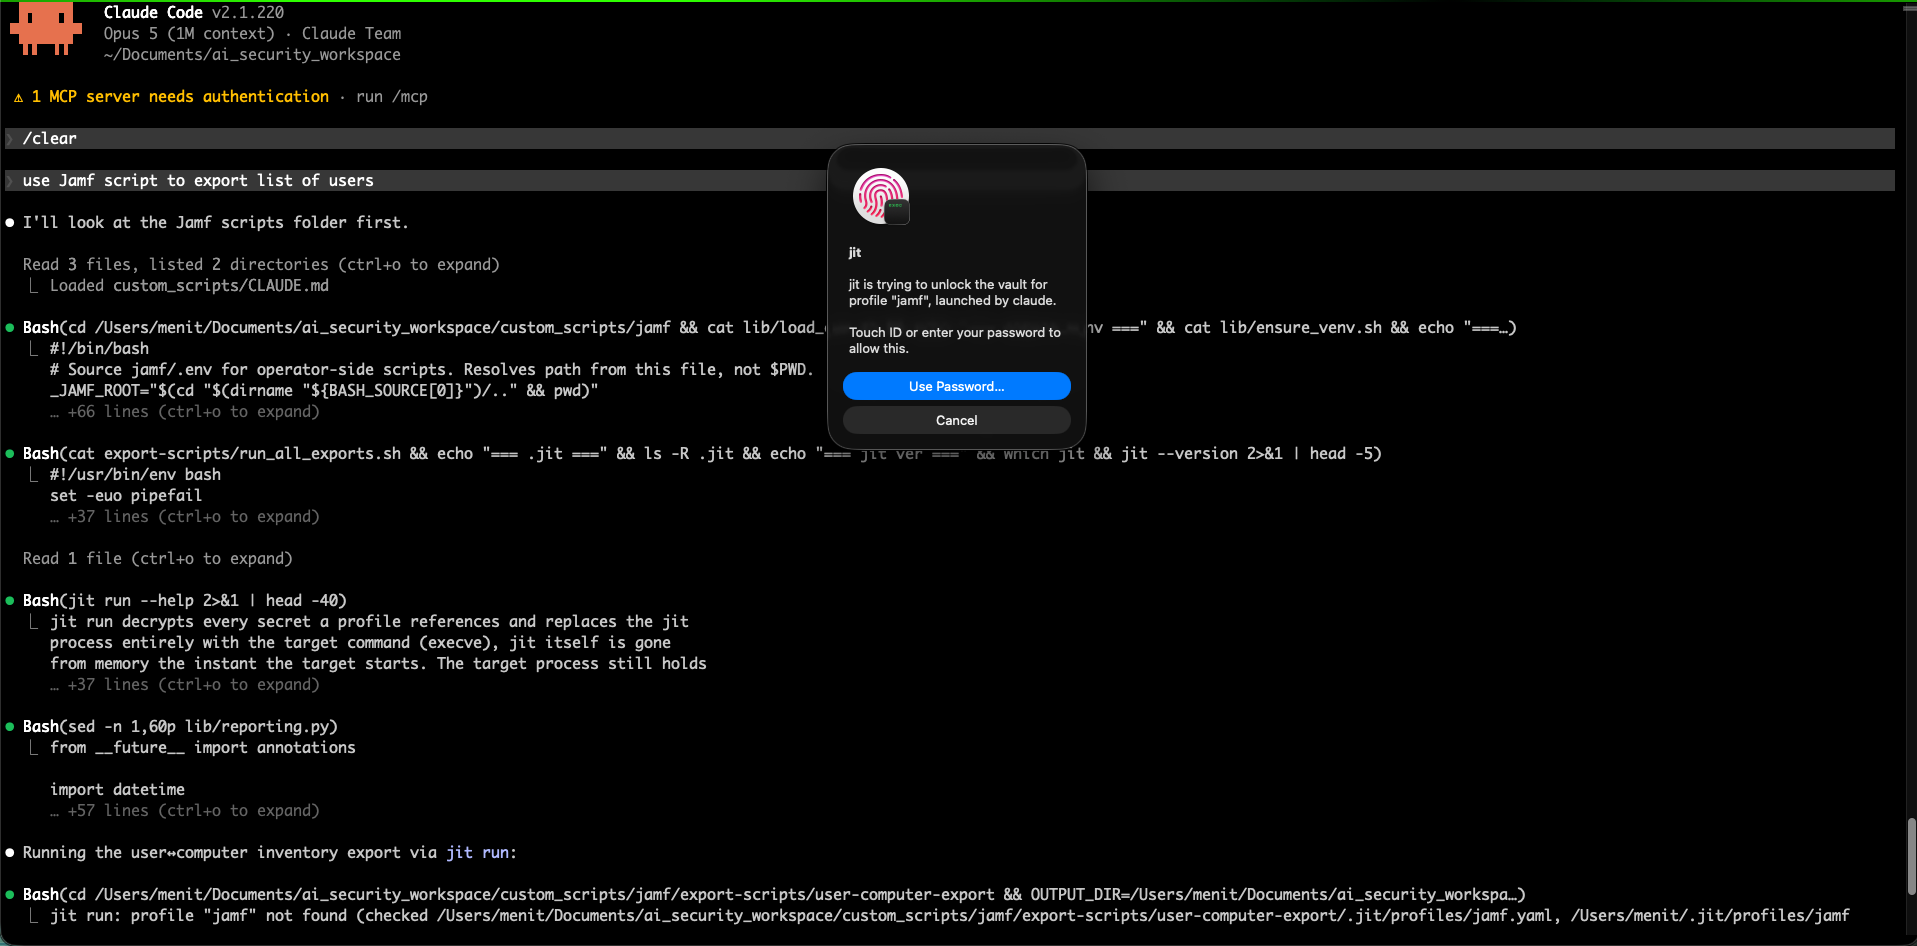 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 htrxuan/hdwebmobile-booking-appointments
Sell bookable services and appointments through WooCommerce -- closes CVE-2026-2931 by construction.
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 dexidp/dex
OpenID Connect (OIDC) identity and OAuth 2.0 provider with pluggable connectors
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.