

Certify
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
authentication-authorizationexploitationpenetration-testing+3
2.0k
ghostpack/certifyC# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 sag-asab/cve-2026-19598
Custom Content Types and Fields plugin for WordPress
 george0papasotiriou/cve-2026-21017-ldap-anonymous-bind-privilege-escalation
Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
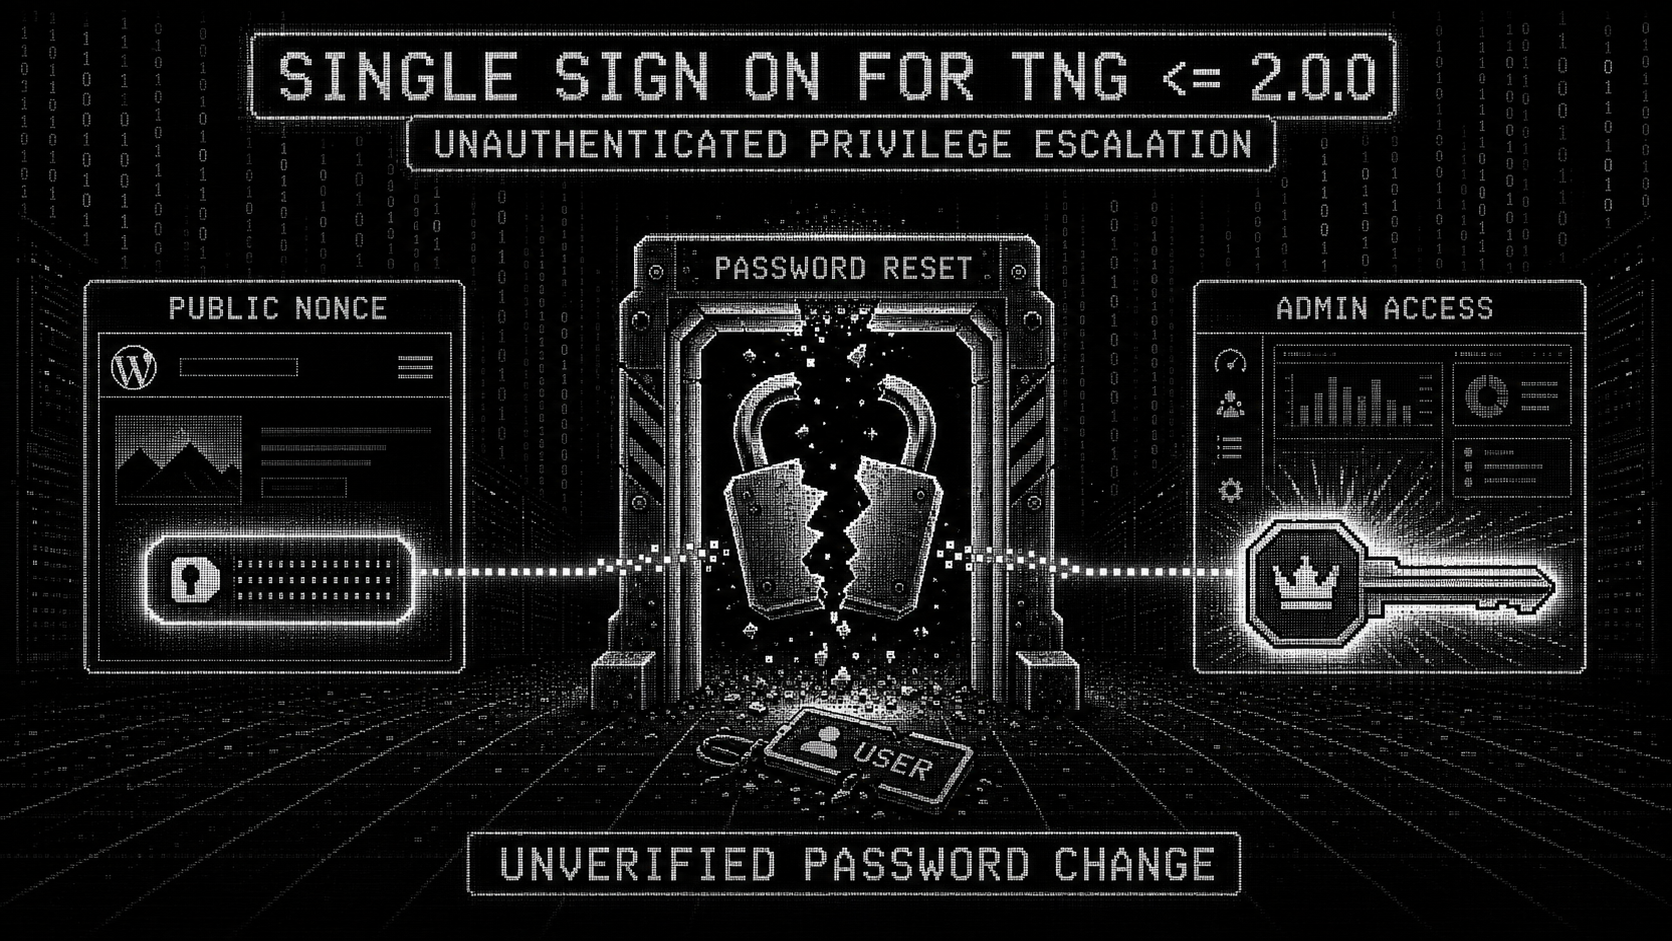 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 redteambrasil/cve-2020-24030
Disclosure of CVE-2020-24030: weak token expiration in ForLogic Qualiex enabling remote privilege escalation and sensitive data access through token…
 razureink/cve-2024-0012_9474-panos_authbypass_reproduction
CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction
 a17-ba/cve-2026-51119
Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 jenderal92/cve-2026-8732
WP Maps Pro <= 6.1.0 - Unauthenticated Privilege Escalation via Administrator Account Creation to wpgmp_temp_access_ajax AJAX Action
 nxploited/cve-2026-4484
Masteriyo LMS <= 2.1.6 - Missing Authorization to Authenticated (Student+) Privilege Escalation to Administrator
 rootx111/cve-2026-29000
Exploit for CVE-2026-29000, a JWT authentication bypass in pac4j-jwt via JWE-wrapped PlainJWT, allowing token forgery and privilege escalation.
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…