
jsch
 mwiede/jsch
fork of the popular jsch library
authentication-authorizationencryption-decryption-toolsnetwork-security+2
mwiede/jschfork of the popular jsch library
 boreas37/cve-2026-41452-poc
CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5
 a17-ba/cve-2026-51119
Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 mrcord77/rust_citadel
Post-quantum hybrid encryption library combining X25519 + ML-KEM-768 with AES-256-GCM
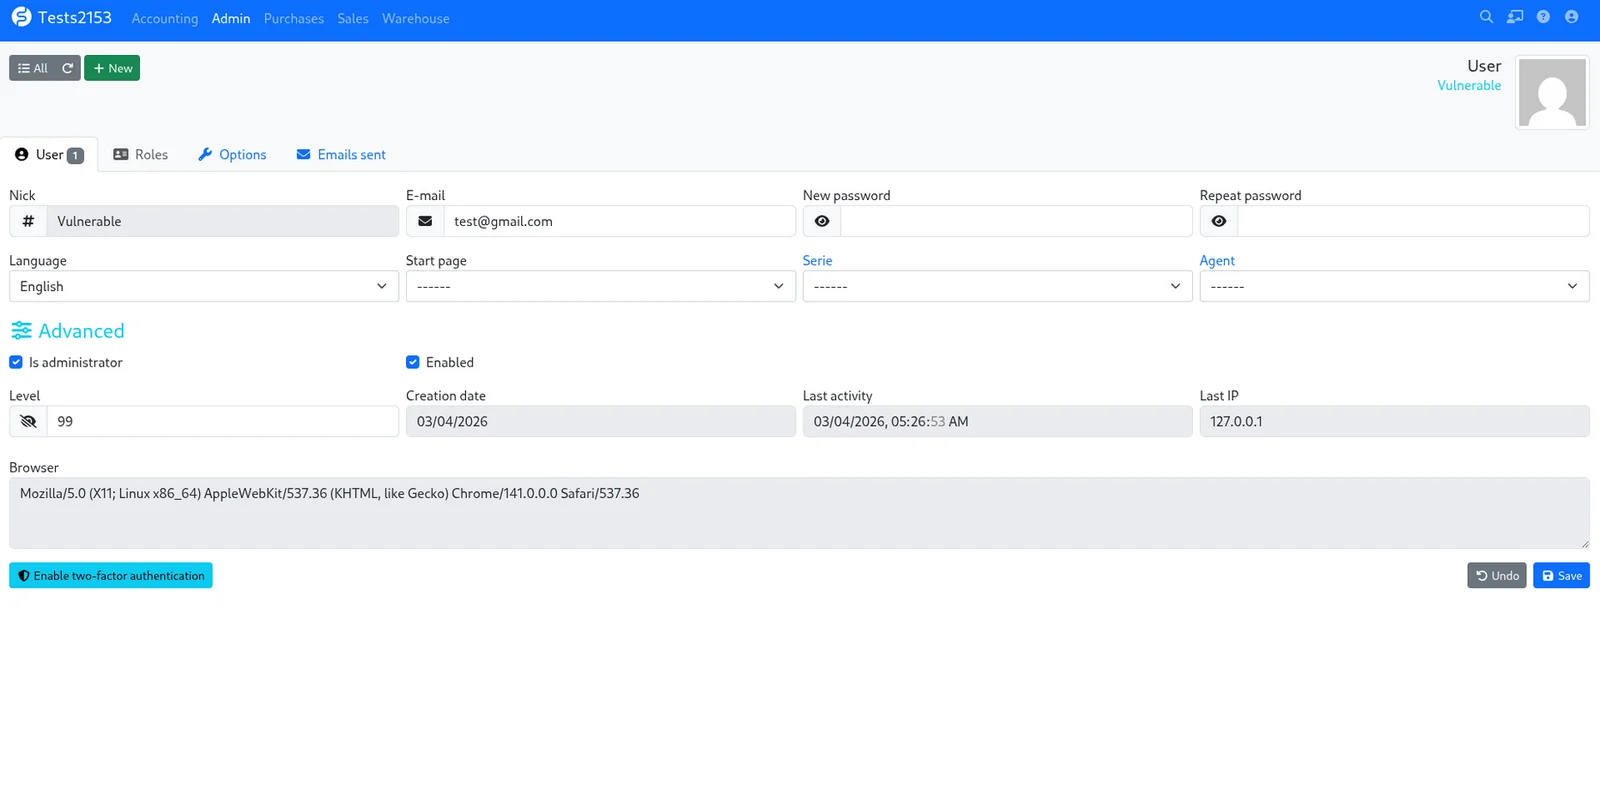 turkios/cve-2026-32699-facturascripts-nick-bypass
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 0xgh057r3c0n/cve-2025-3102
SureTriggers <= 1.0.78 - Authorization Bypass Exploit
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0011
Python script for checking authentication bypass vulnerability (WT-2025-0011) in Kentico Xperience 13 CMS Staging Service via POST request analysis.
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0006
Authentication bypass detection script for Kentico Xperience 13 CMS Staging Service using a single POST request to verify vulnerability.
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 watchtowrlabs/mitel-micollab-auth-bypass_cve-2024-41713
Proof-of-concept exploit for CVE-2024-41713, demonstrating authentication bypass in Mitel MiCollab leading to arbitrary file read. Includes a Python…
 watchtowrlabs/palo-alto-panos-cve-2024-0012
Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…
 cve-2024/cve-2024-5326-poc
Proof-of-concept exploit for CVE-2024-5326, a missing authorization vulnerability in the PostX WordPress plugin allowing authenticated attackers to…
 rampantspark/cve-2024-27198
A PoC for CVE-2024-27198 written in Go
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 vidvansh/cve-2021-41511
Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…
 fa1c0n35/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7 https://www.guardicore.com/2020/04/pwning-vmware-vcenter-cve-2020-3952/