
FreeRDP
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
authentication-authorizationencryption-decryption-toolsnetwork-security+2
13.7k10h 50m ago
freerdp/freerdpFreeRDP is a free remote desktop protocol library and clients
 firezone/firezone
WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…
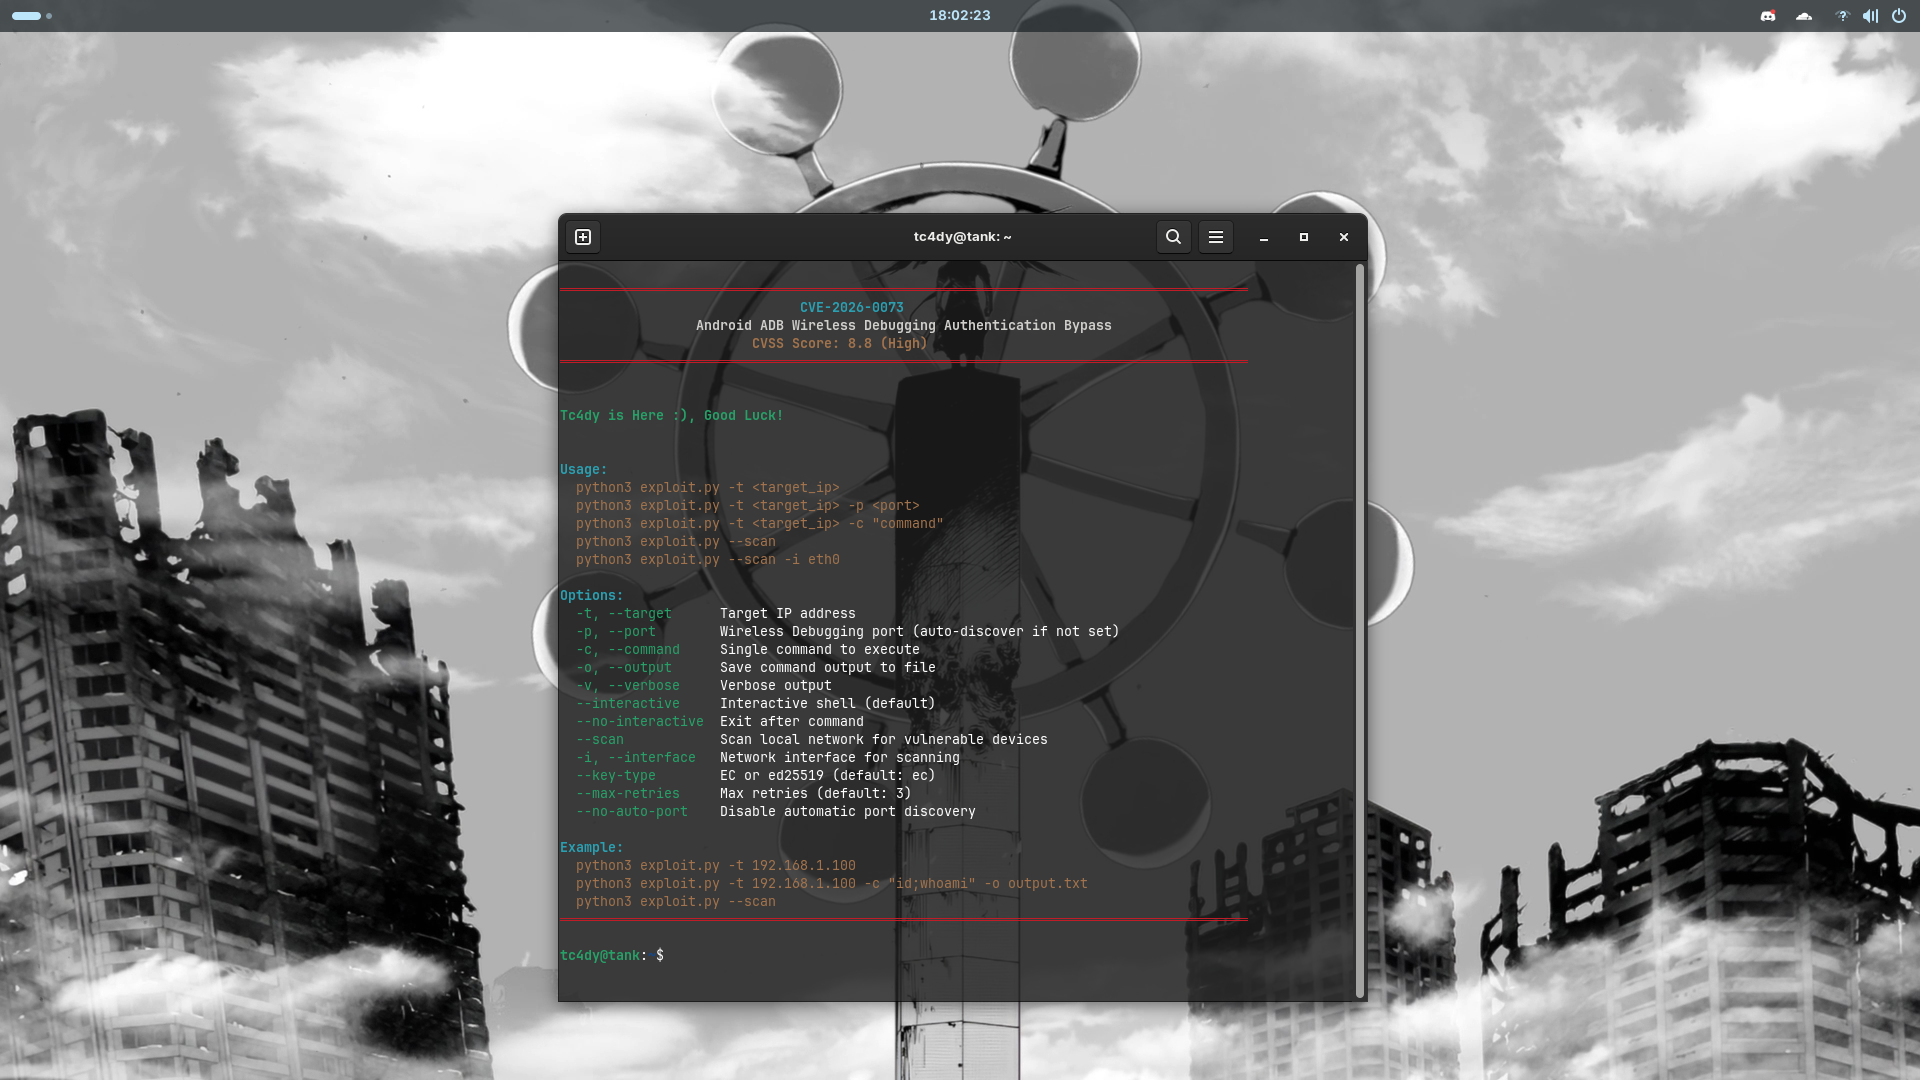 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 redteambrasil/cve-2020-24030
Disclosure of CVE-2020-24030: weak token expiration in ForLogic Qualiex enabling remote privilege escalation and sensitive data access through token…
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…
 razureink/cve-2024-0012_9474-panos_authbypass_reproduction
CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction
 mirackayikci/cve-2026-55584
CVE-2026-55584 — phpSysInfo IP Allowlist Bypass
 blackhatexploitation/buk_ts_killer
Exploit for BUK-TS authentication bypass and remote code execution, with steps to intercept responses and manipulate userid to gain unauthorized…
 fevar54/cve-2026-50751---check-point-ikev1-authentication-bypass-exploit
Vulnerability: Logic flow weakness in Remote Access and Mobile Access
 k3ystr0k3r/cve-2026-24061
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 offseckit/cve-2026-23813
CVE-2026-23813 — AOS-CX pre-auth bypass via nginx regex. Detection script, bypass demo, config-disclosure PoC, and IDS rules.
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 dhiaelhak-rached/cve-2026-39987-lab-or-marimo-cve-lab
Educational Docker lab demonstrating CVE-2026-39987, a pre-auth RCE via WebSocket authentication bypass in marimo, with exploit script and patch…