CVE-2026-0073-PoC-Exploit

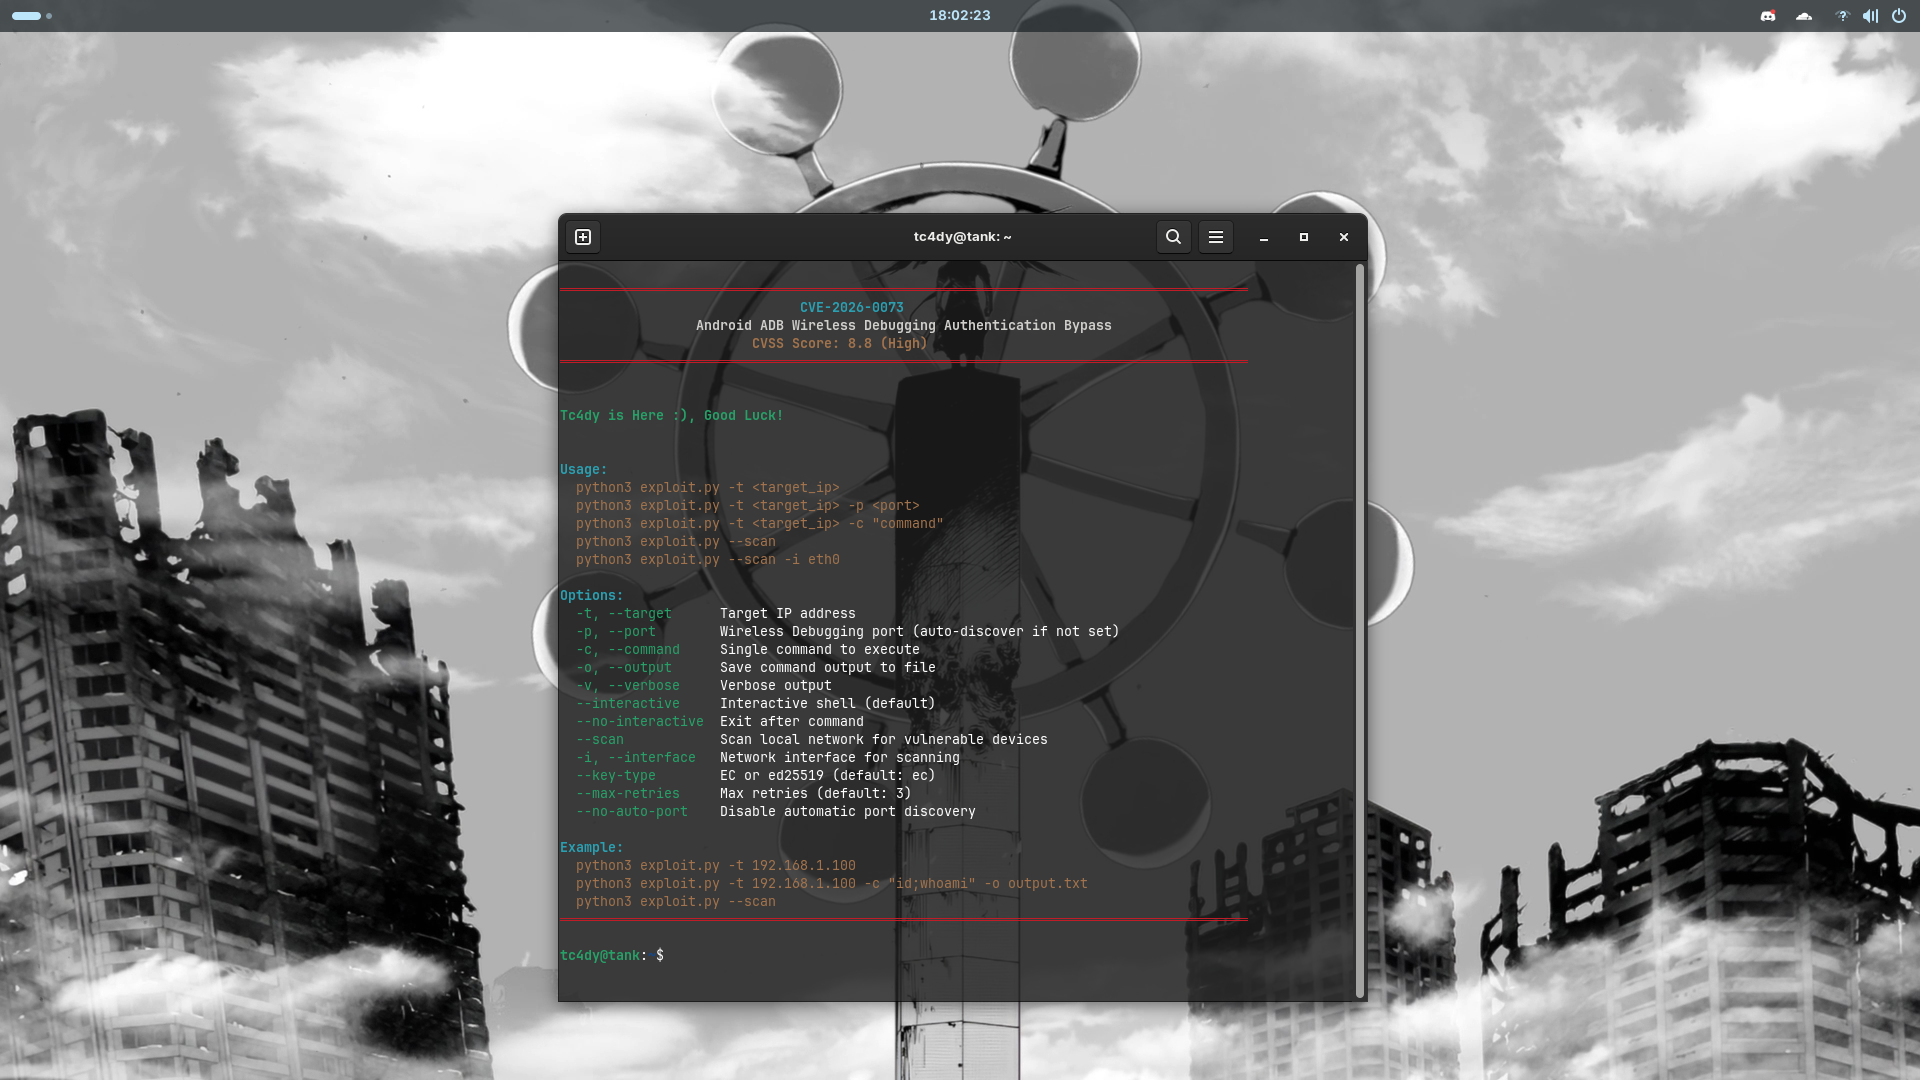
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…

Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Corelight Sensor API command-line client

Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…

PoC exploit for FortiWeb CVE-2025-64446 (authentication bypass via path traversal) and CVE-2025-58034 (OS command injection) with detailed analysis…

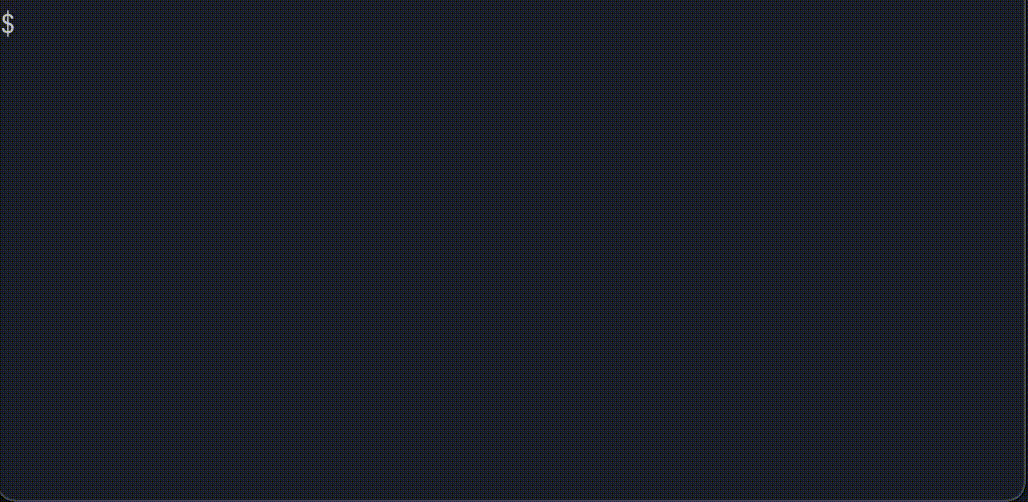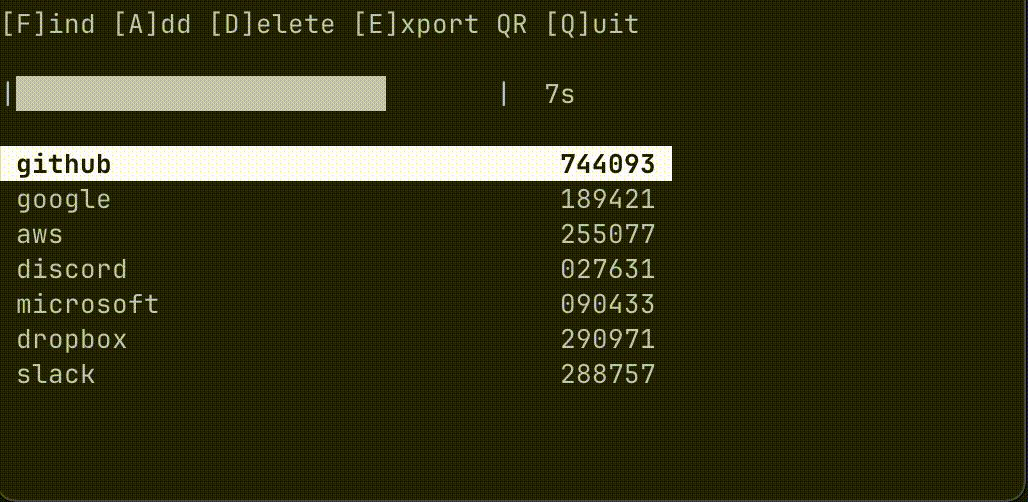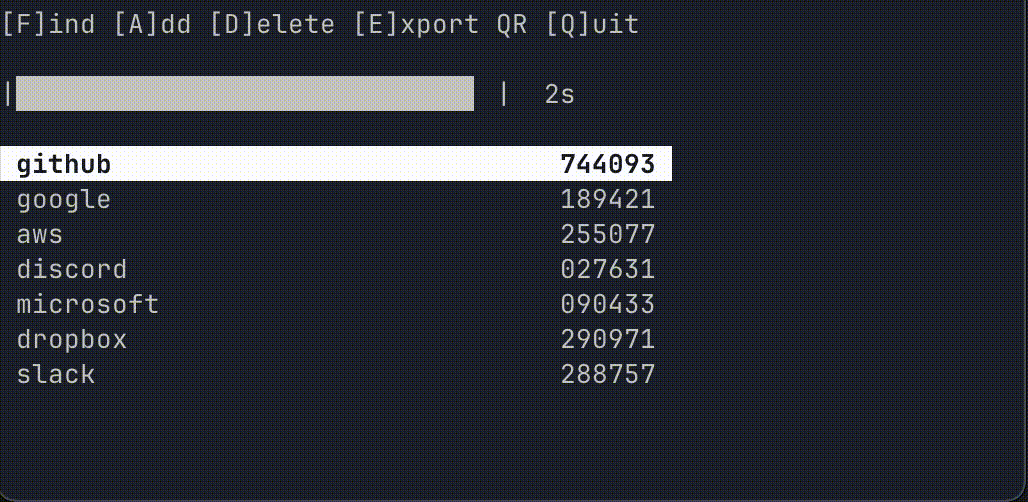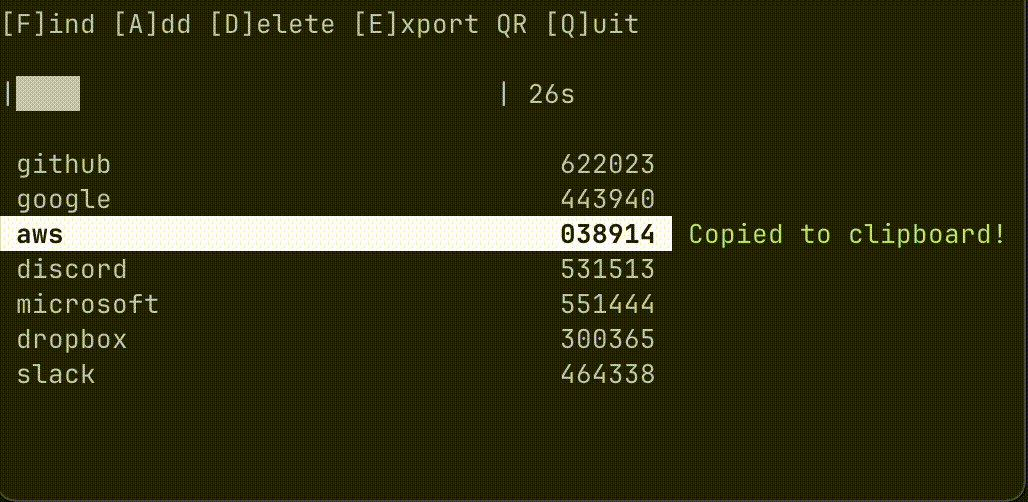
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.

The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP

PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

A terminal based tool for managing secrets with both tui and cli support

Catch what's lurking in your Kafka clusters.

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

Ivanti Neurons for ITSM (On Premise) exploits

ScriptCase Pre-Authenticated Remote Command Execution exploitation script (CVE-2025-47227, CVE-2025-47228).

Python script for CVE-2024-0012 / CVE-2024-9474 exploit

Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.