cve-2026-32699-facturascripts-nick-bypass

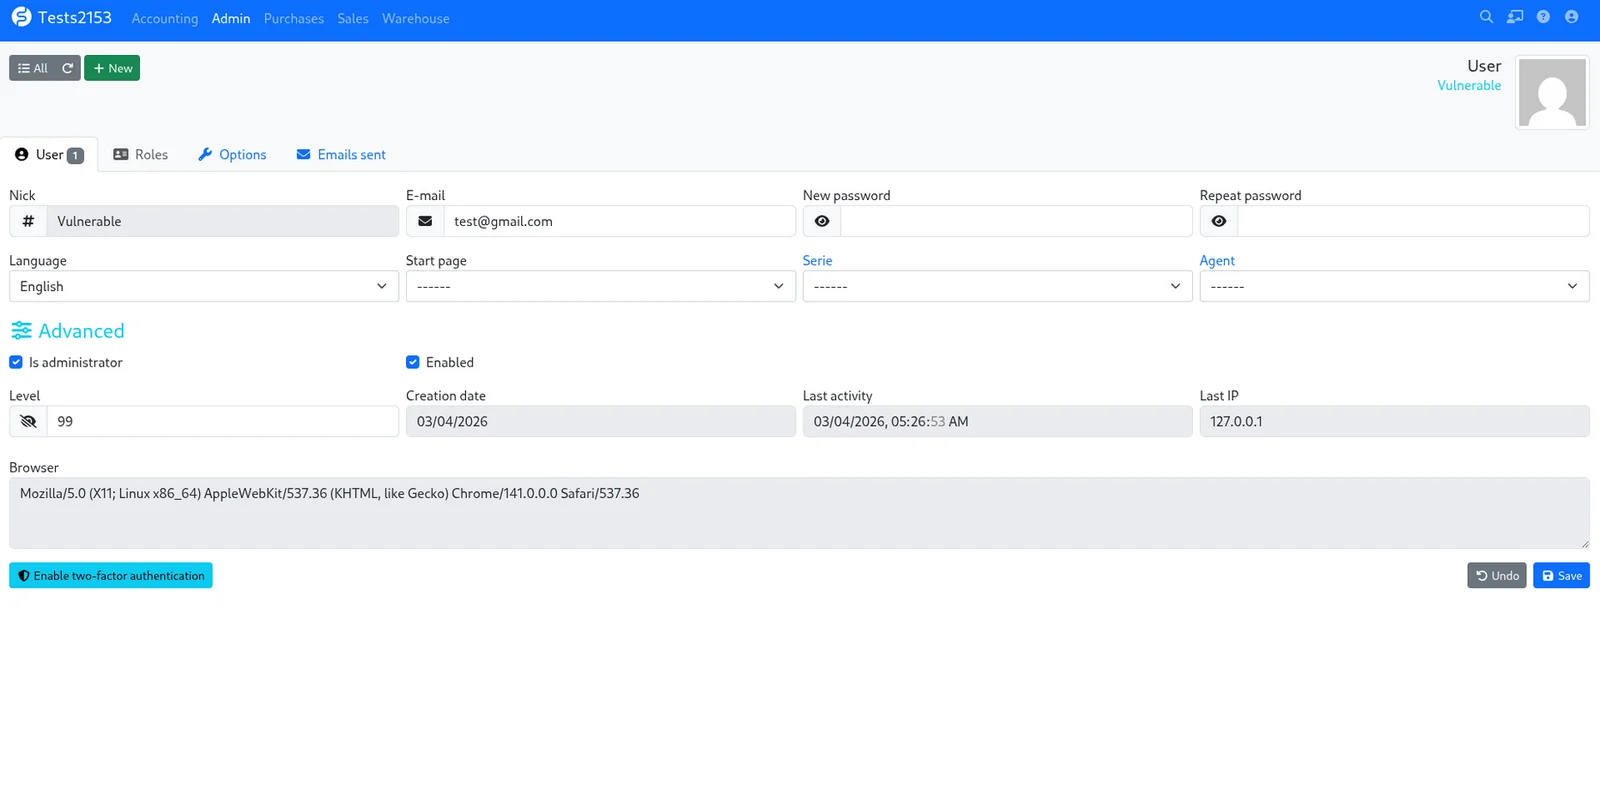
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…

Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…

CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5

SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)

Authentication bypass detection script for Kentico Xperience 13 CMS Staging Service using a single POST request to verify vulnerability.

Python script for checking authentication bypass vulnerability (WT-2025-0011) in Kentico Xperience 13 CMS Staging Service via POST request analysis.

fork of the popular jsch library

A PoC for CVE-2024-27198 written in Go

Exploit for CVE-2020-3952 in vCenter 6.7 https://www.guardicore.com/2020/04/pwning-vmware-vcenter-cve-2020-3952/

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

Proof-of-concept exploit for CVE-2024-41713, demonstrating authentication bypass in Mitel MiCollab leading to arbitrary file read. Includes a Python…

Post-quantum hybrid encryption library combining X25519 + ML-KEM-768 with AES-256-GCM

Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection

Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…

Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…

Exploit for CVE-2020-3952 in vCenter 6.7

Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…

Proof-of-concept exploit for CVE-2024-5326, a missing authorization vulnerability in the PostX WordPress plugin allowing authenticated attackers to…

SureTriggers <= 1.0.78 - Authorization Bypass Exploit