CVE-2026-55040-Mass-Exploit

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

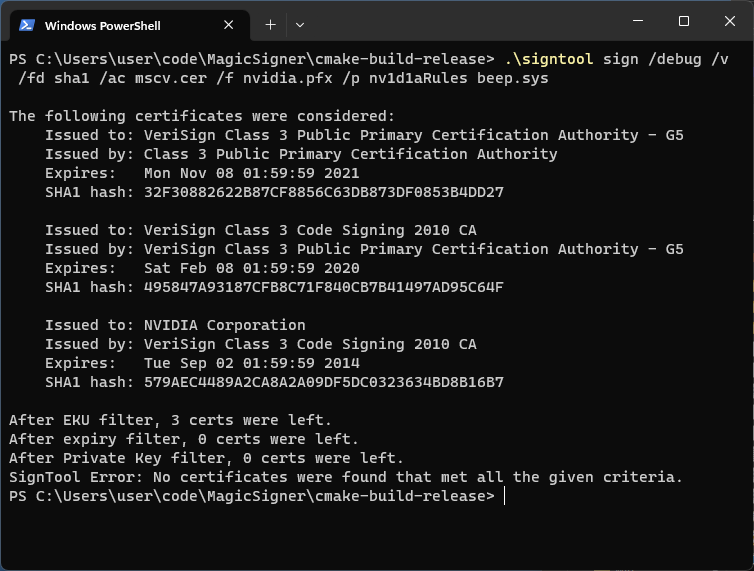
Signtool for expired certificates

Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…

Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…

Production AI defense with 7-layer protection: mathematical constraints, object-capability access, distributed O2 consensus, SVETILO ethics. First…

Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…

In-depth IDOR write-up for Concrete CMS, covering the message_detail endpoint, missing authorization root cause, attack scenarios, impact, and fix.

SecOpsMaesttro POC

CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.

This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…

Educational lab demonstrating CVE-2022-39227 JWT authentication bypass in python-jwt. Step-by-step attack against vulnerable and patched Flask apps…

Discource POC

Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…

a plugin that protects your wp site from the CVE-2017-8295 vulnerability

Simulates an attack exploiting CVE-2024-32962 to forge SAML messages and gain unauthorized permissions, demonstrating the vulnerability's impact.

Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user…

Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…