phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

A free, secure and open source app for Android to manage your 2-step verification tokens.

An Android HW Attestation demo

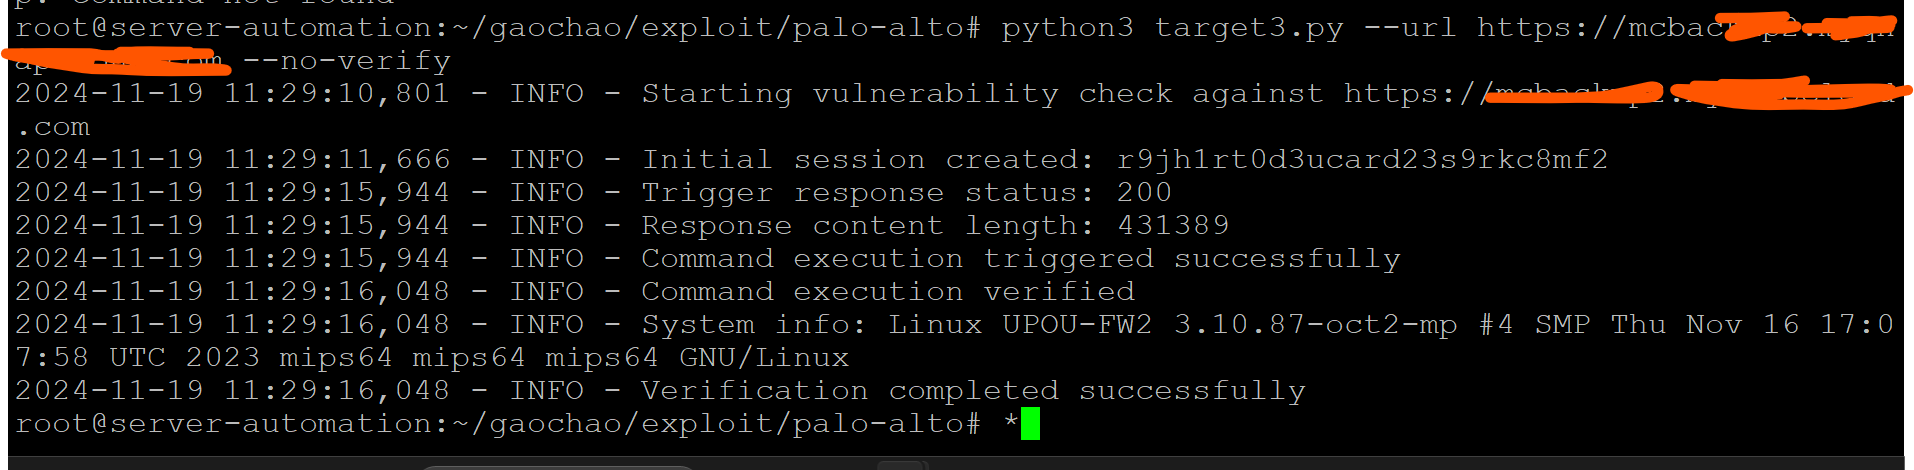
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

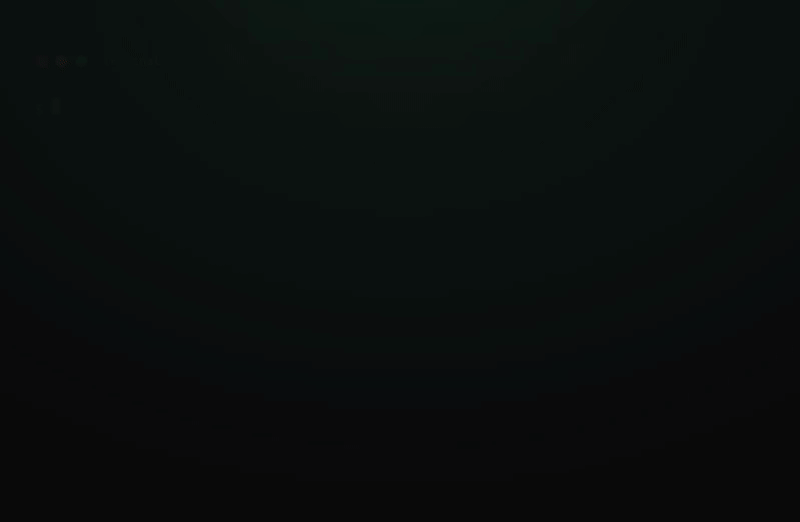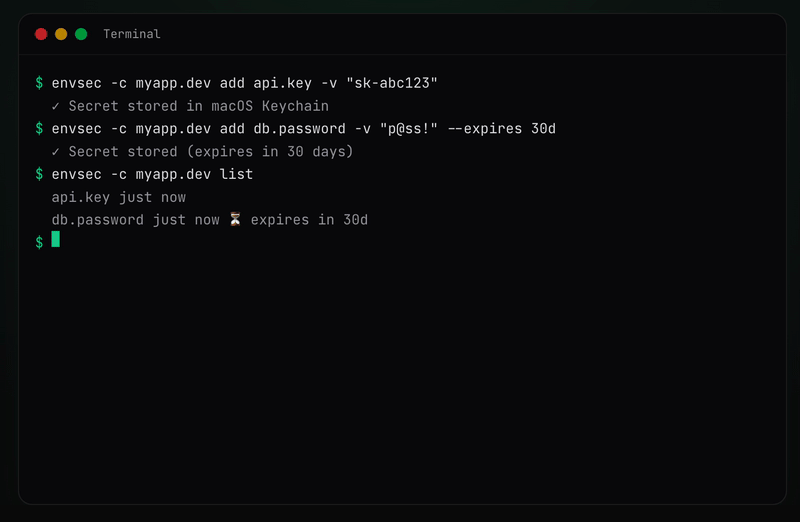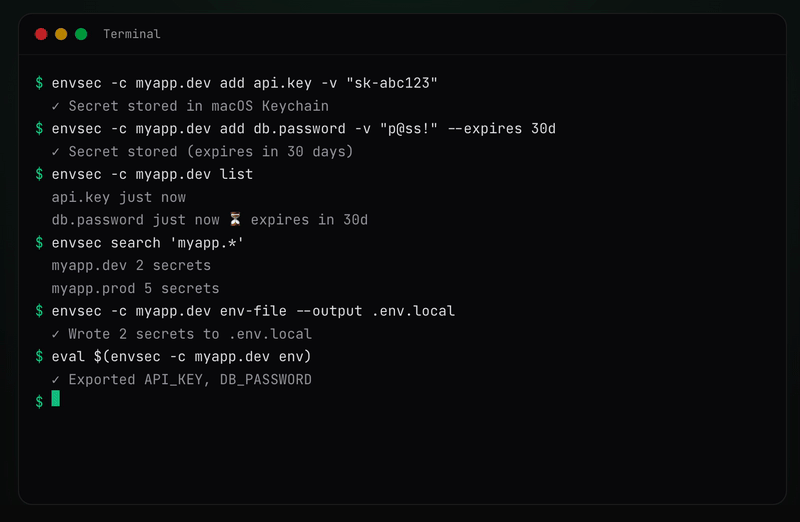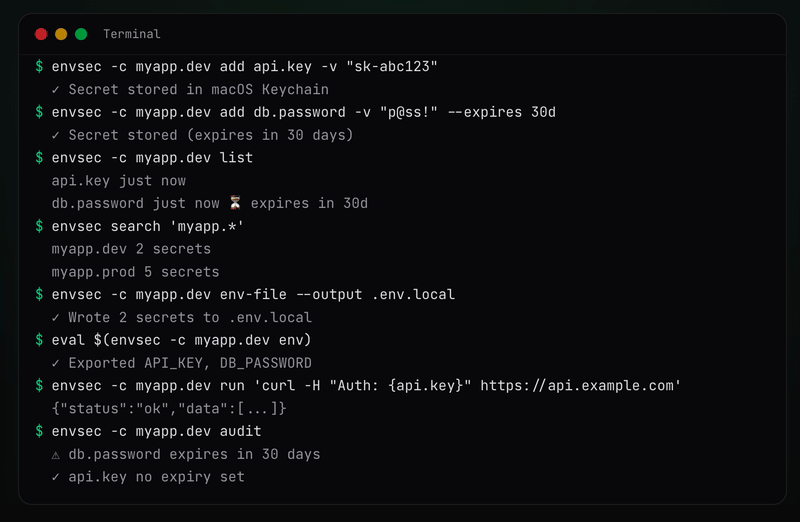
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)

Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

DLL Injection tool to unlock guest VMs

0-Click RCE Android Adb TLS Wireless Debugging

Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass

LG On Screen Phone authentication bypass PoC (CVE-2014-8757)

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction

Exploit for CVE-2024-47533, a critical authentication bypass in Cobbler XML-RPC API, granting unauthenticated admin access for educational security…

PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

Python script for CVE-2024-0012 / CVE-2024-9474 exploit