
op4
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
authenticationauthentication-authorizationcryptography+3
opfour/op4Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 sfewer-r7/cve-2026-16232
A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
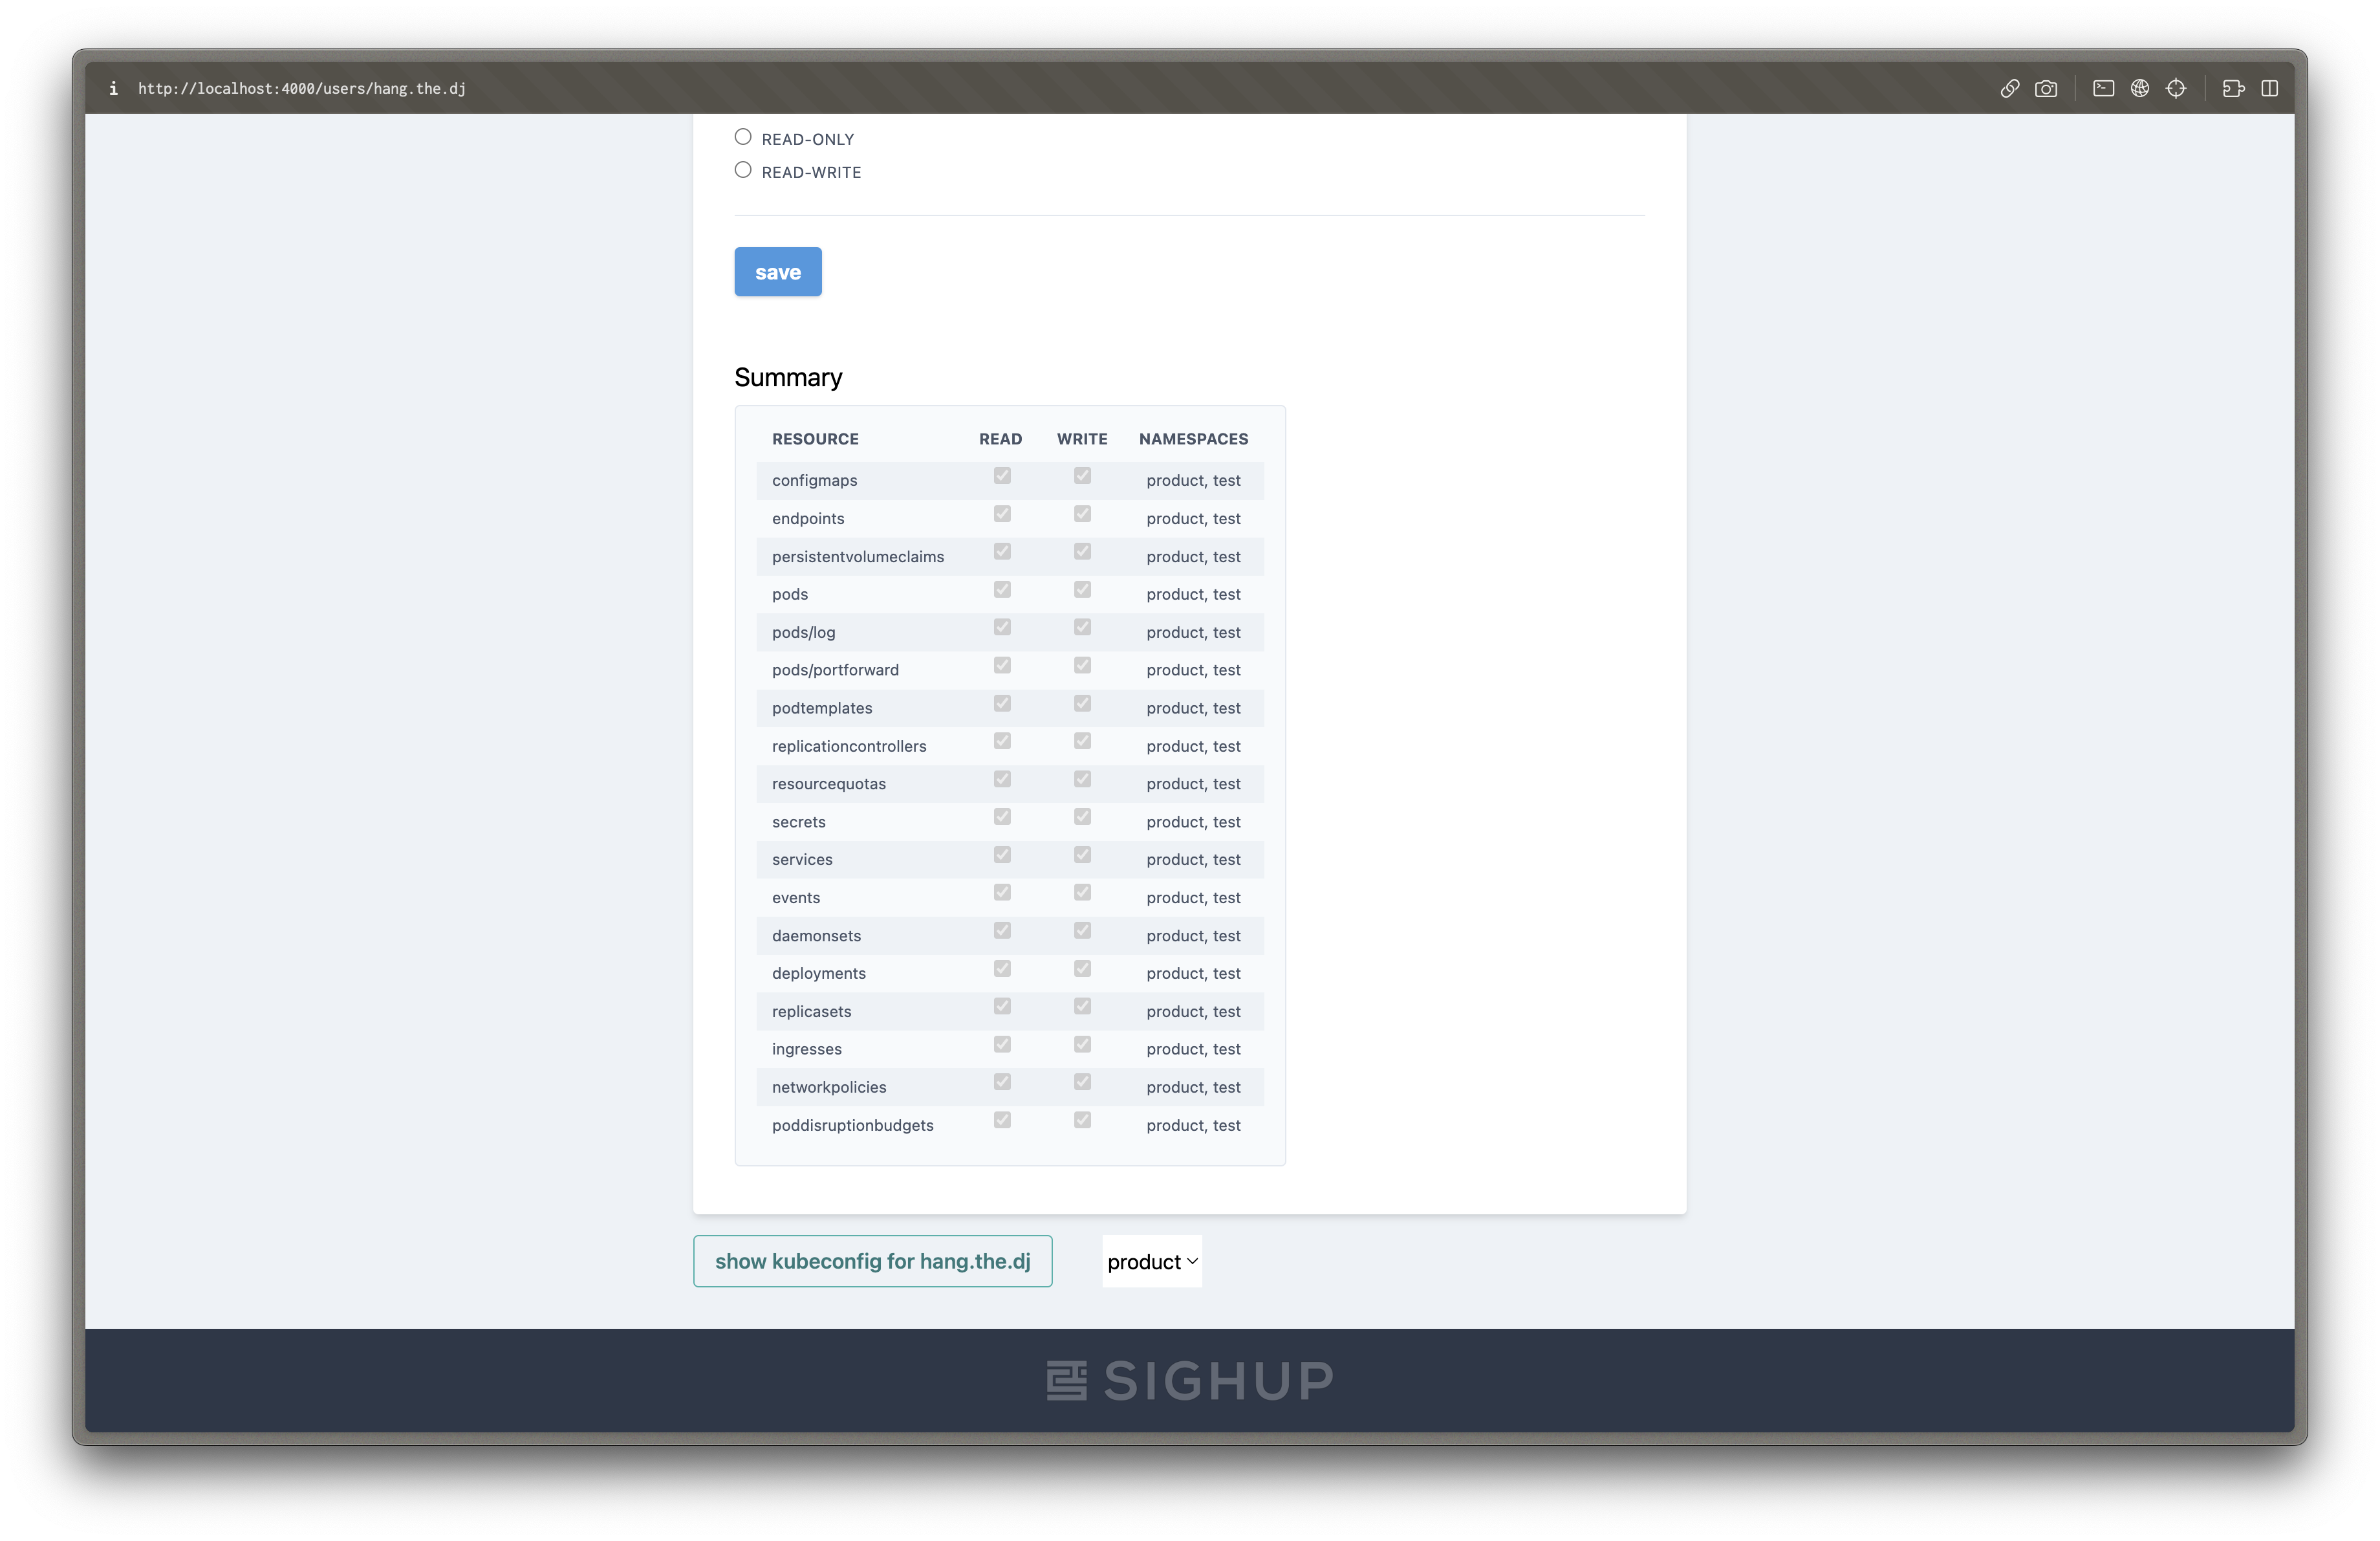 sighupio/permission-manager
Permission Manager is a project that brings sanity to Kubernetes RBAC and Users management, Web UI FTW
 sugib3o/vulnerable-nextjs-14-cve-2025-29927
vulnerable-nextjs-14-CVE-2025-29927
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 styx00/dnn_cve-2015-2794
NSE plugin for Nmap that scans a DotNetNuke (DNN) web application for an Administration Authentication Bypass vulnerability (CVE-2015-2794, EDB-ID:…
 shoucheng3/apache__shiro_cve-2023-34478_1-11-0
Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…
 ricsirigu/cve-2025-29927
A deliberately Next.js app, vulnerable to CVE-2025-29927, Authorization Bypass
 lirantal/vulnerable-nextjs-14-cve-2025-29927
Reproduction environment for CVE-2025-29927, demonstrating Next.js middleware authorization bypass via the x-middleware-subrequest header. Includes…
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692