
CVE-2025-40554
 skynoxk/cve-2025-40554
CVE-2025-40554 Exploitation
authenticationexploitationinformation-gathering+4
skynoxk/cve-2025-40554CVE-2025-40554 Exploitation
 karthi-the-hacker/cve-2023-27524
Exploit tool for CVE-2023-27524, an authentication bypass vulnerability in Apache Superset. Enables unauthenticated access to Superset instances for…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 ninjazan420/cve-2025-52691-poc-smartermail-authentication-bypass-exploit-wt-2026-0001
CVE-2025-52691 PoC: Based on watchtowr's article WT-2026-0001 about an authentication bypass exploit, this one is a functional Python attack script.
 shisones/cve-2025-31161
A proof of concept for CVE-2025-31161, using mangled HTTP header to perform unauthenticated impersonation of any user in Crush FTP server.
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
 jenderal92/cve-2026-5118
CVE-2026-5118 – Python2 mass exploit for Divi WordPress plugin Unauthenticated administrator registration via admin-ajax.php. Multi‑threaded scanner…
 cipher1x1/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via JWE-wrapped unsigned JWT, enabling privilege escalation.
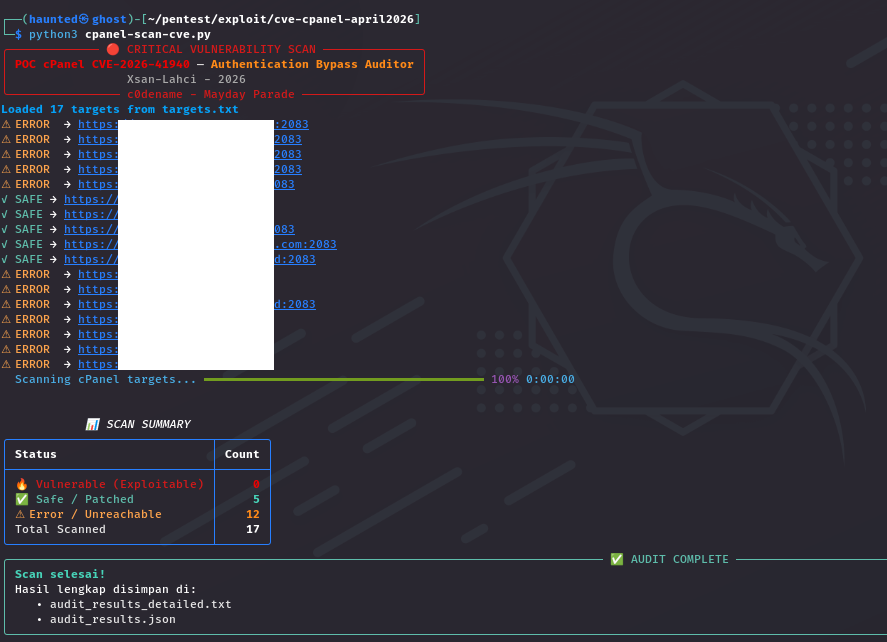 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 murrez/cve-2026-8181
CVE-2026-8181 PoC: Burst Statistics (3.4.0–3.4.1.1) authentication bypass. Python tool — single & multi-target scans, threaded workers, TXT reports.…
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
 realbatuhan/jwt-bruteforcer
Jwt Bruteforcer with CVE-2018-1000531 Test
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 jtesta/ssh-mitm
SSH man-in-the-middle tool
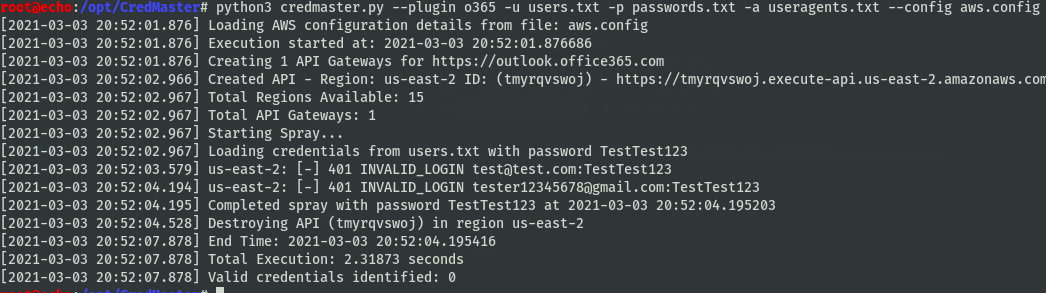 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 logisek/huntcyberark
CyberArk Security Audit
 optionalctf/ssoh-no
User enumeration and password spraying tool for testing Azure AD
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…