
CVE-2026-24061-GNU-InetUtils-telnetd
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
authenticationcommand-and-controlexploitation+3
anxs3c/cve-2026-24061-gnu-inetutils-telnetdGNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 karammahmad/cve-2021-40113
CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
 asterisk/asterisk
The official Asterisk Project repository.
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 ake13-art/secfesc
Lightweight security state inspector for Linux — bridging the gap between pretty fetch tools and heavy-duty audit frameworks.
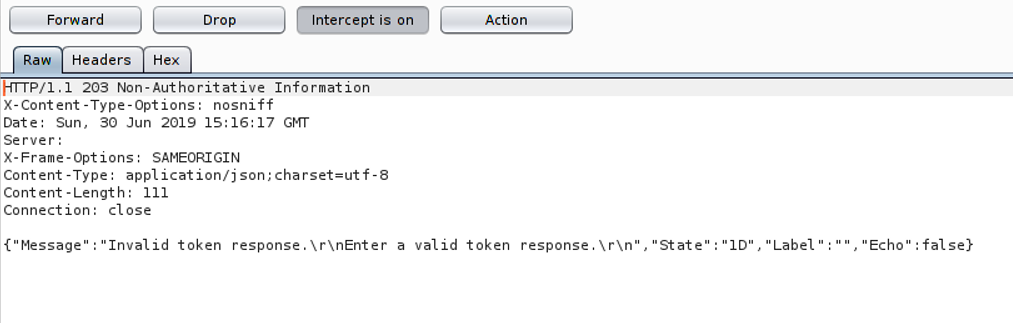 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
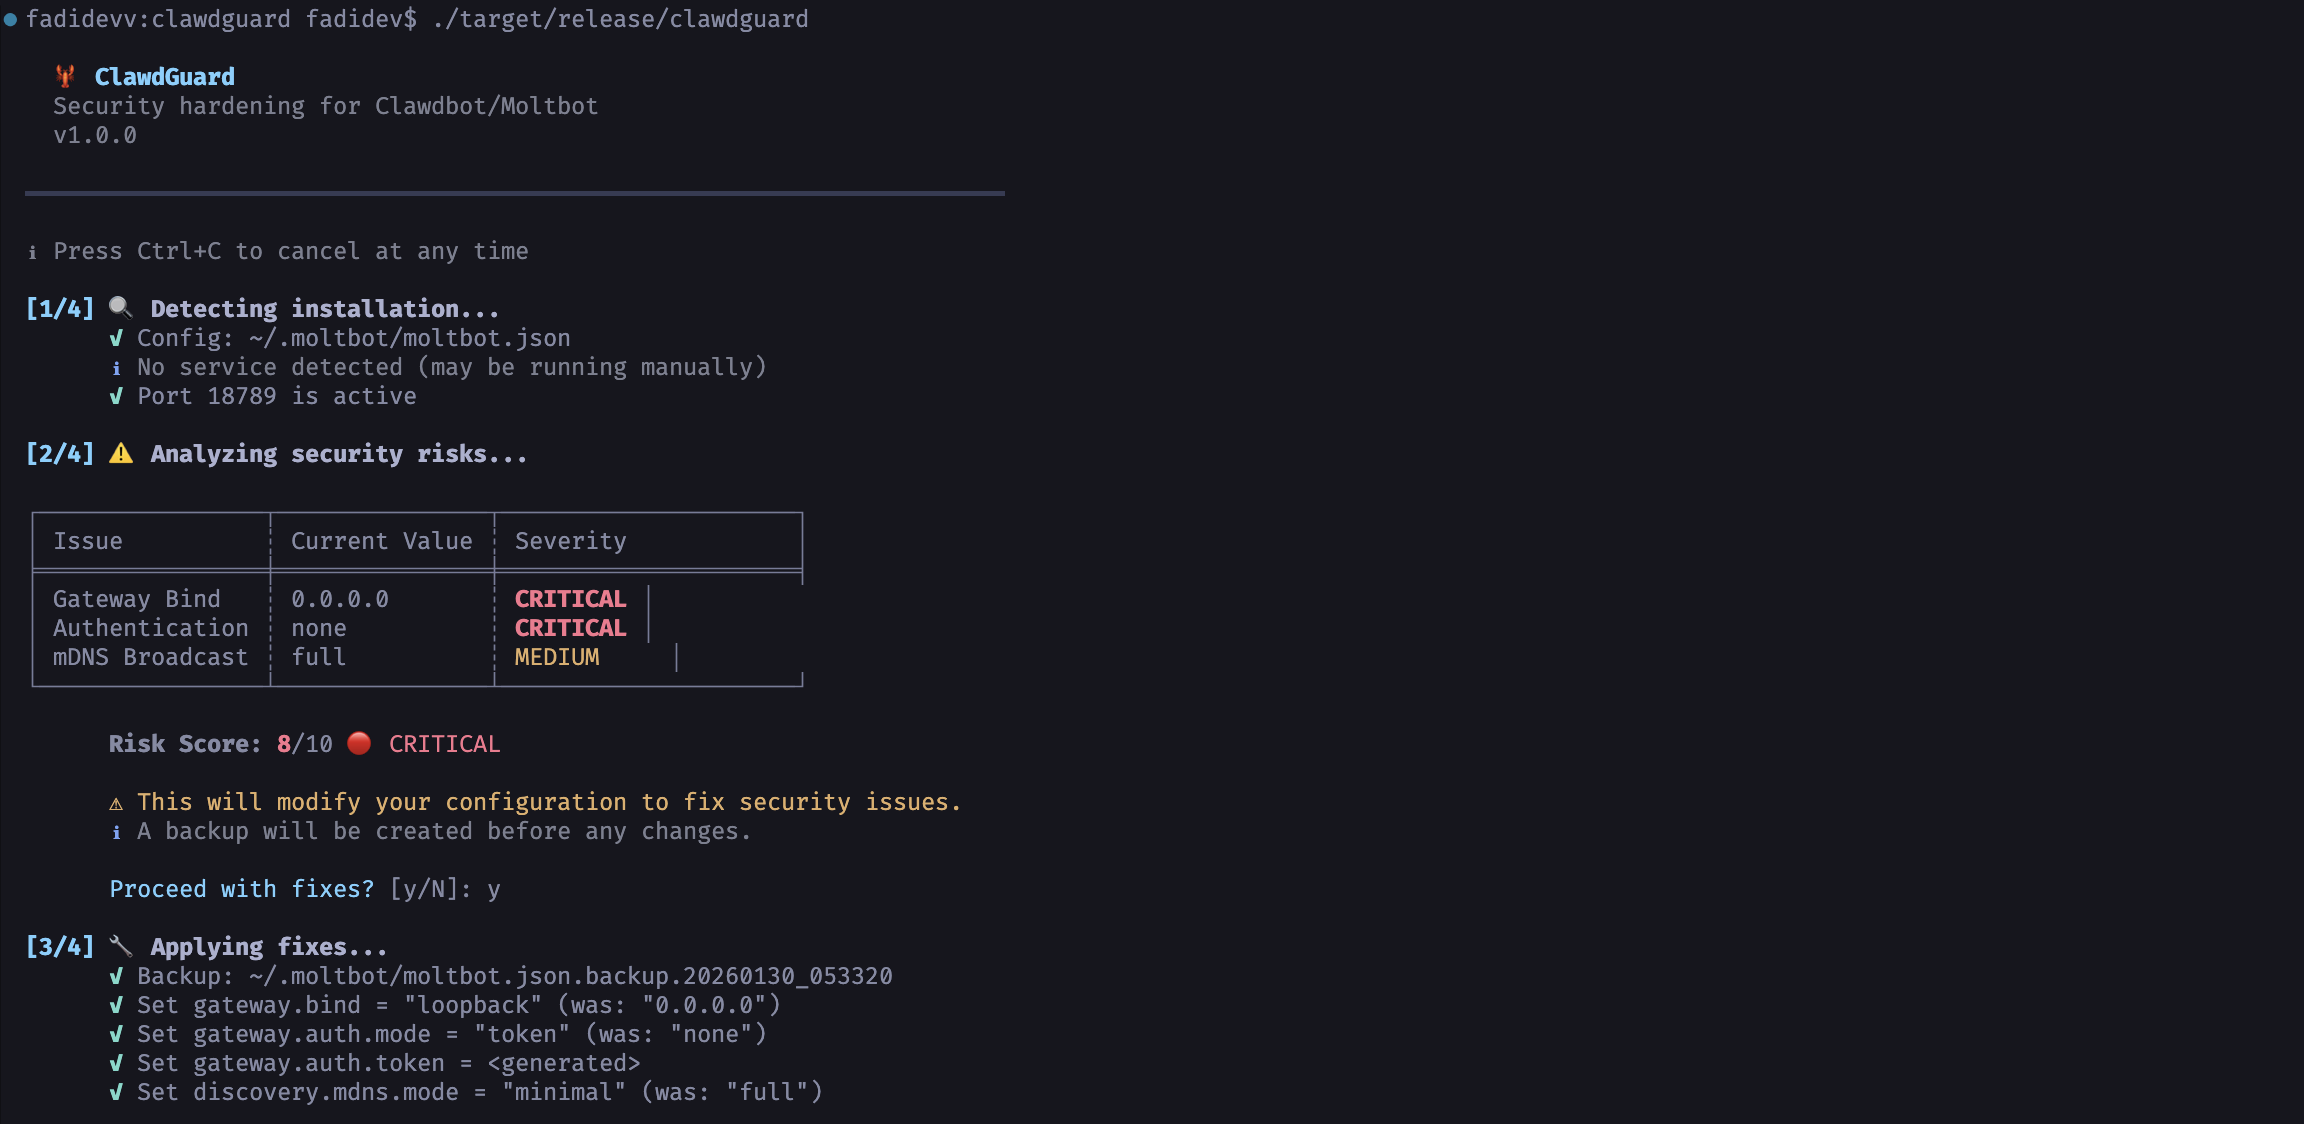 fadidevv/clawdguard
🦞 Security hardening patch for Clawdbot/Moltbot. Detects and fixes exposed gateways automatically.
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…