
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
Koh preview

Koh

GitHubghostpack/koh

Captures Windows logon session tokens via token leakage to enable credential reuse and impersonation, with Cobalt Strike BOF integration for…
authenticationpost-exploitationred-teaming
5214 years ago
ridenum preview

ridenum

GitHubtrustedsec/ridenum

Rid_enum is a null session RID cycle attack for brute forcing domain controllers.
authenticationinformation-gatheringnetwork-security+3
3176 years ago
jwt-reauth preview

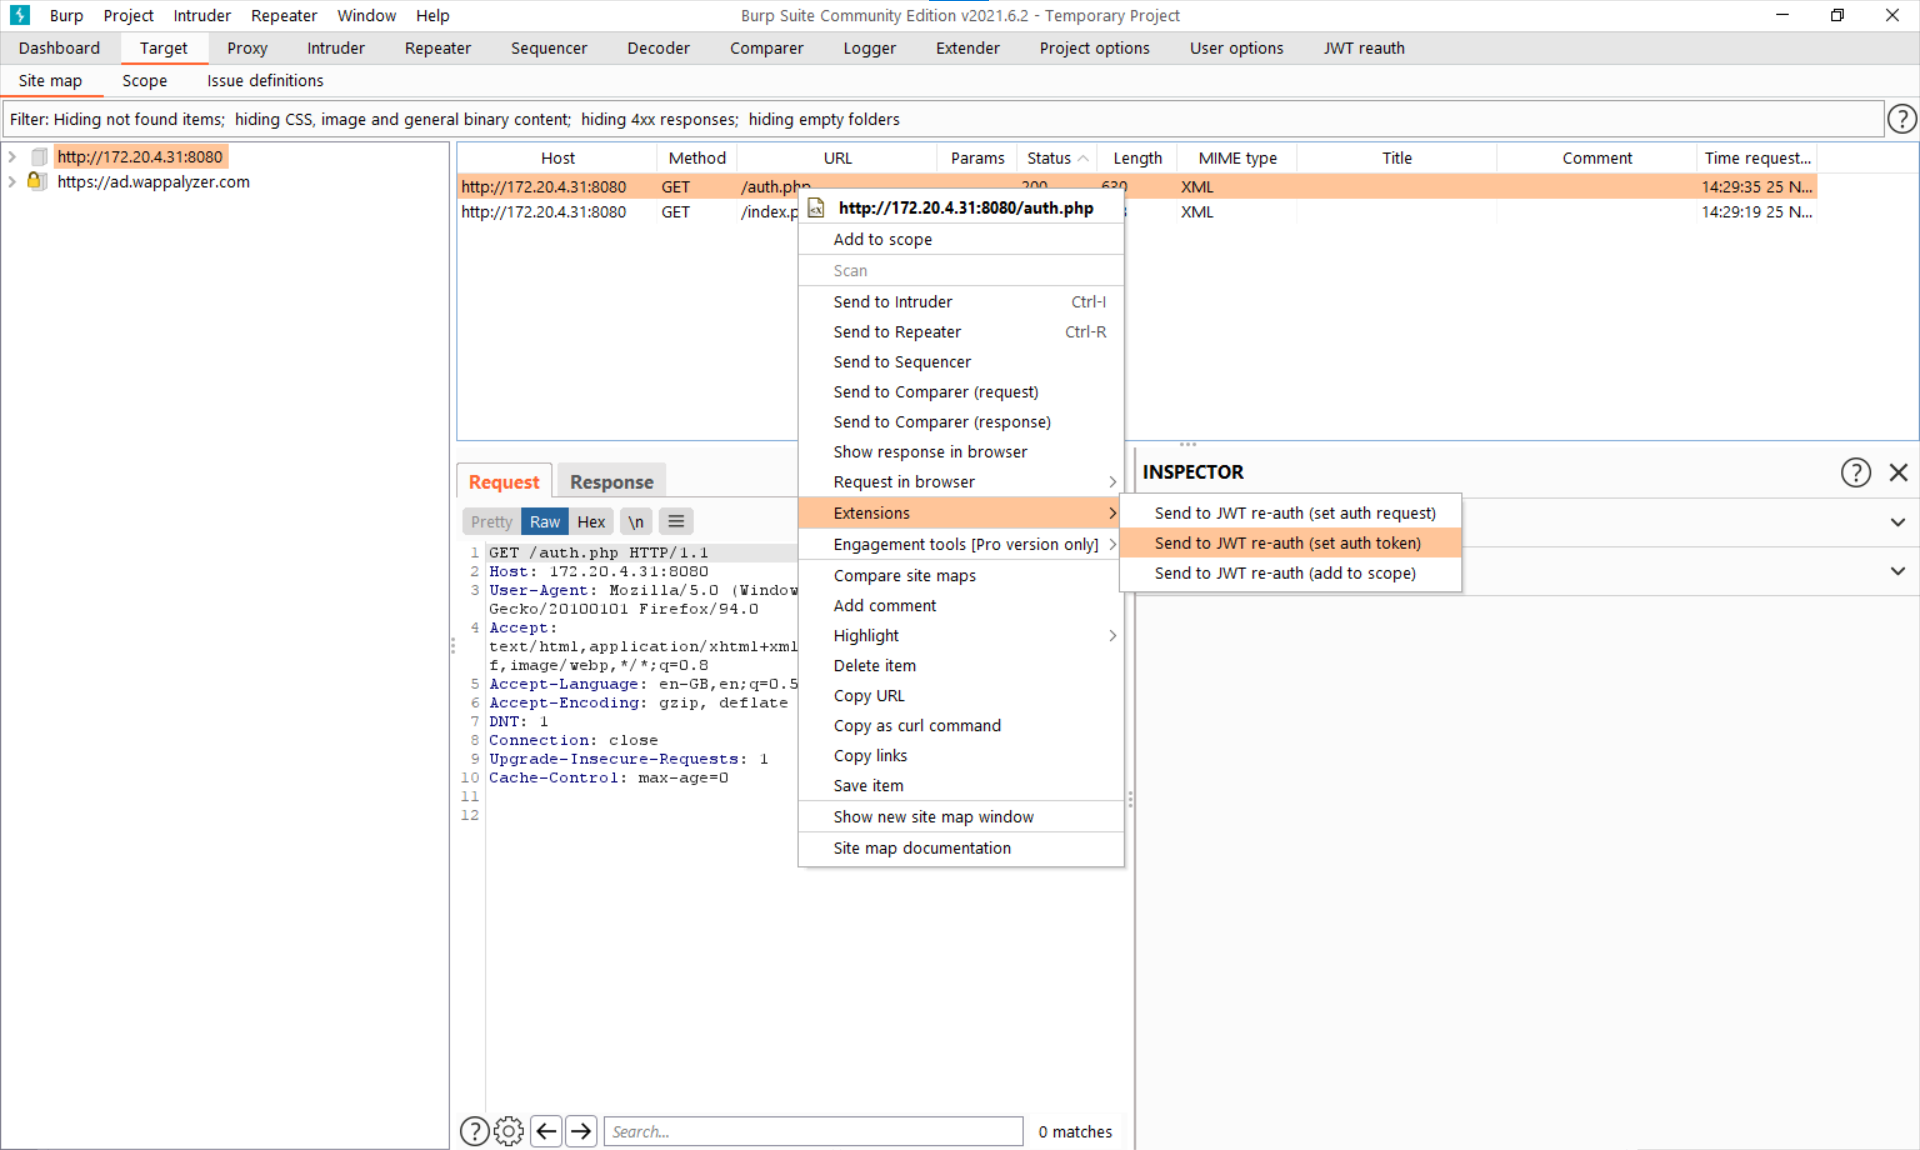
jwt-reauth

GitHubnccgroup/jwt-reauth

Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
api-securityauthenticationpenetration-testing+3
1063 years ago
WonkaVision preview

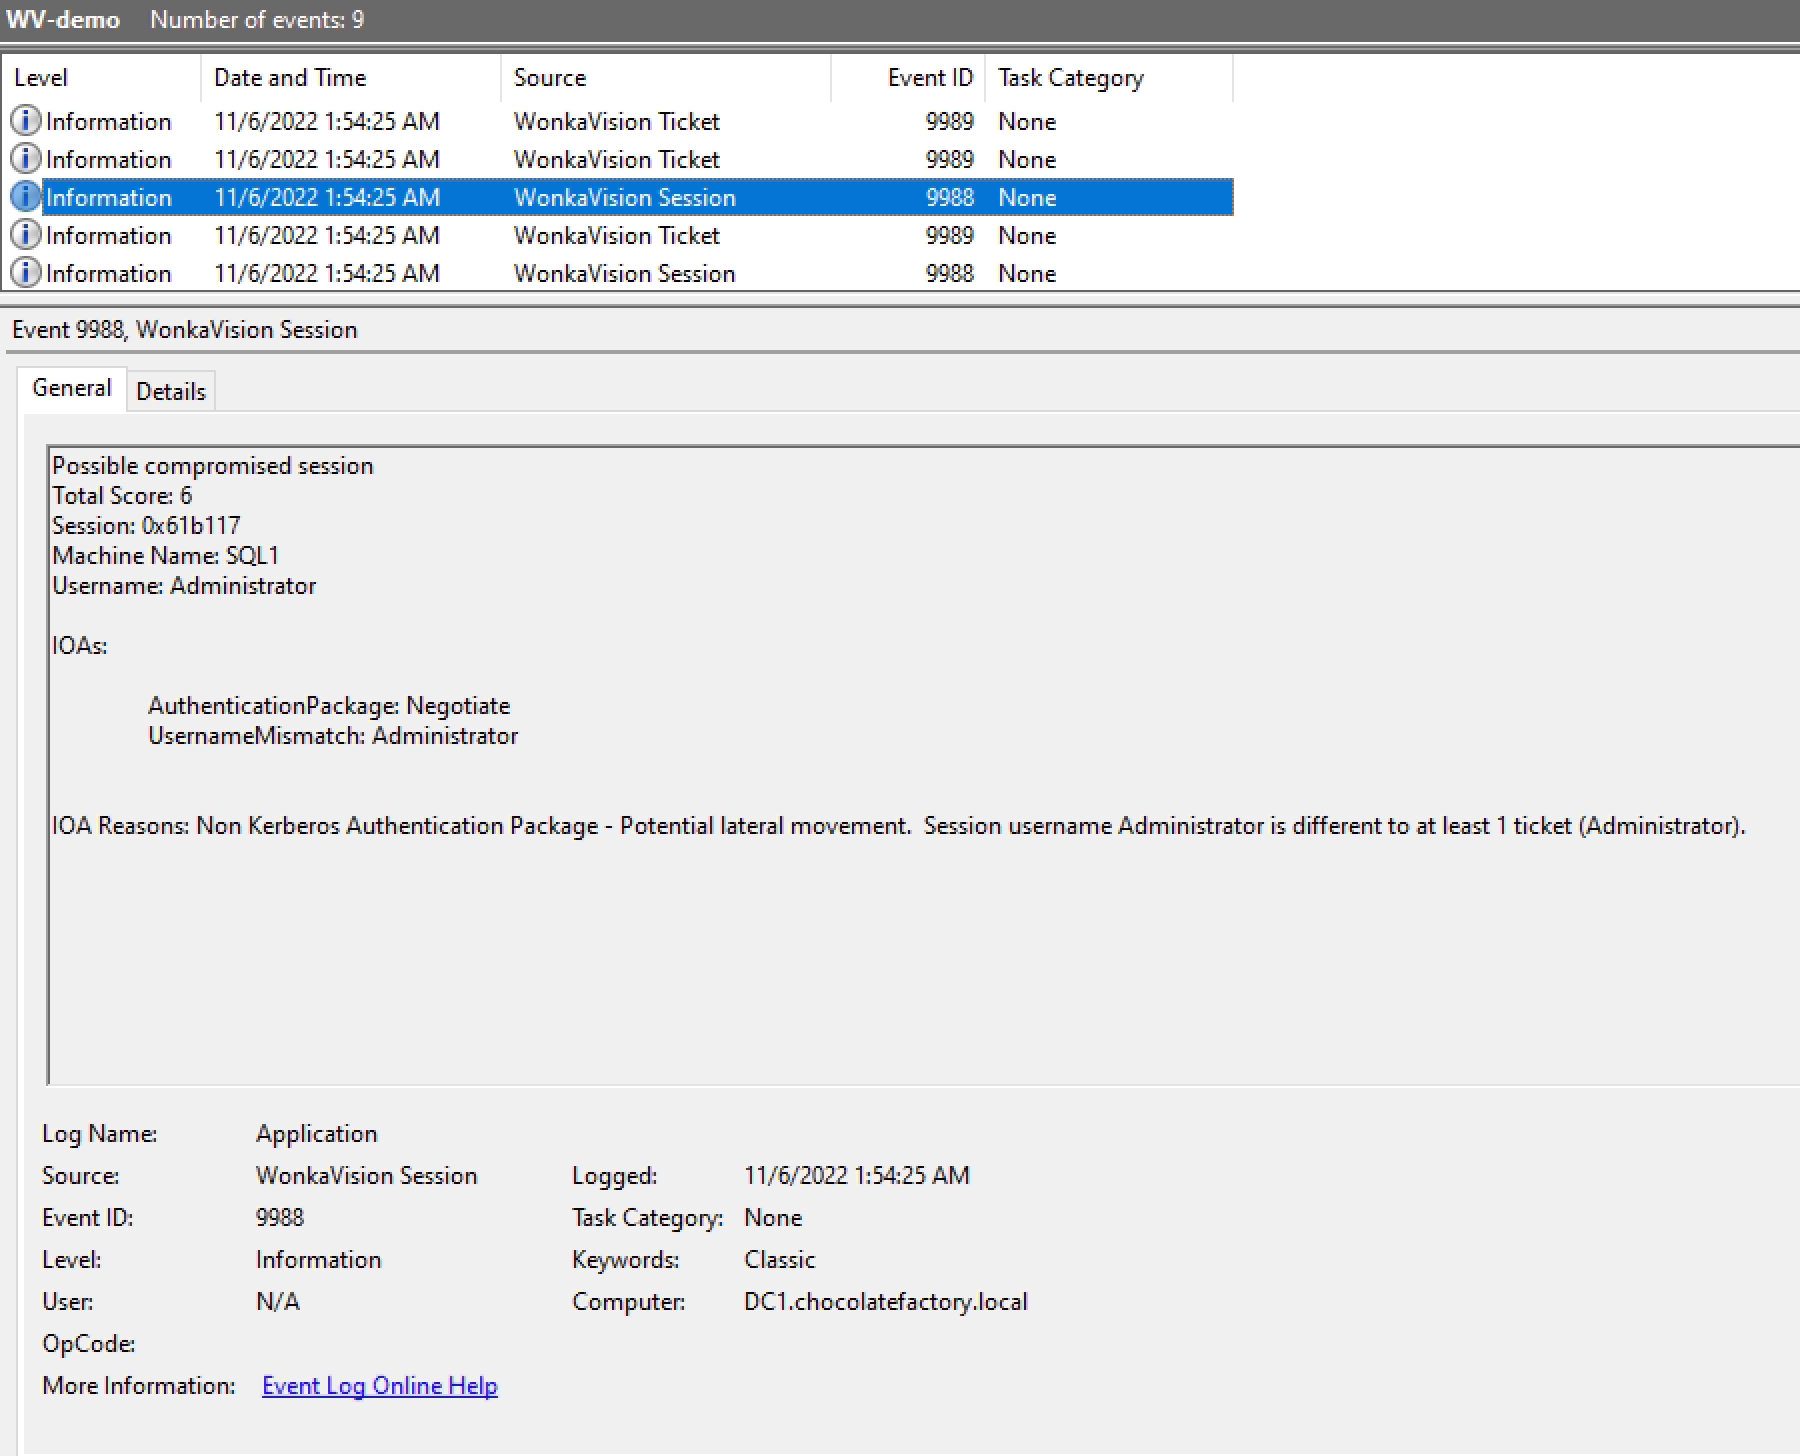
WonkaVision

GitHub0xe7/wonkavision

Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
anomaly-detectionauthenticationdefensive-tools+4
893 years ago
agensic preview

agensic

GitHubalex188dot/agensic

Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
ai-securityauthenticationdigital-forensics+5
292 months ago
TOTPAuthenticate preview

TOTPAuthenticate

GitHubhannah-portswigger/totpauthenticate

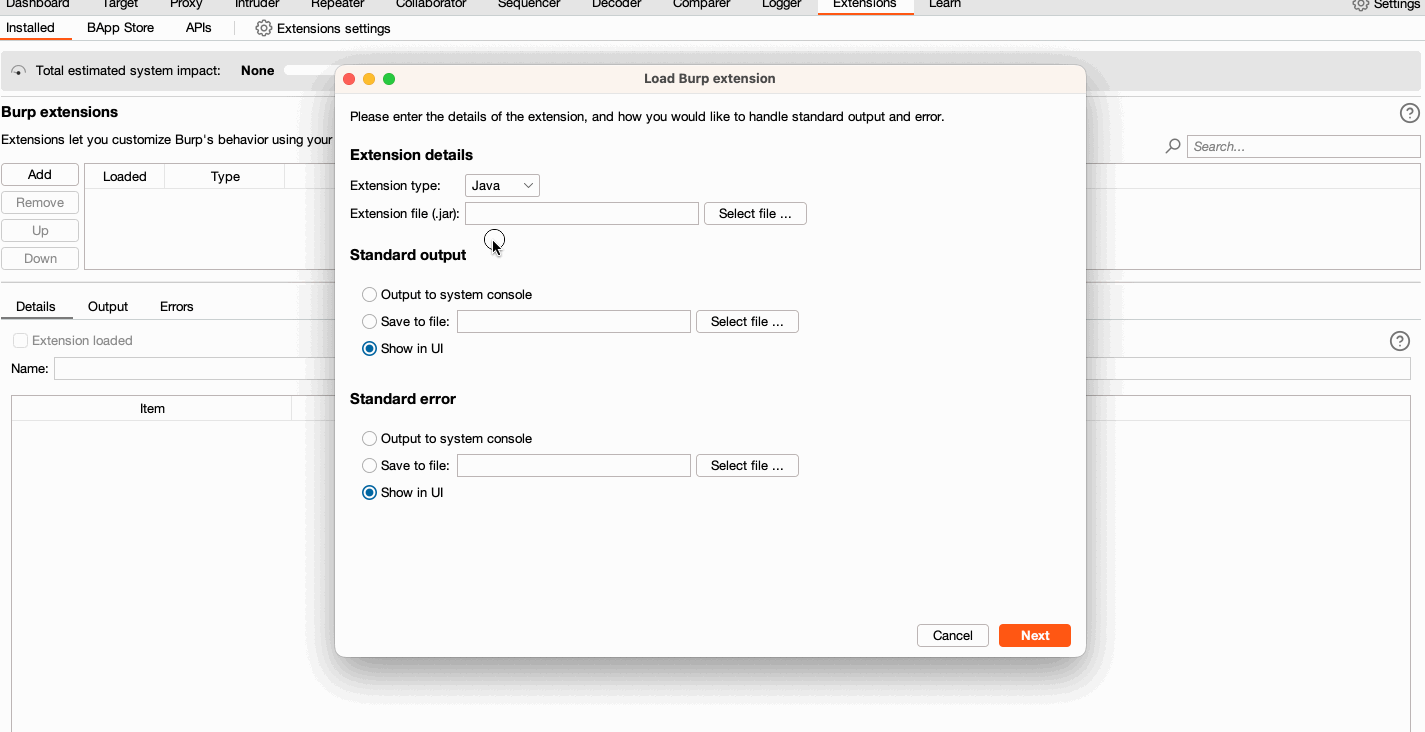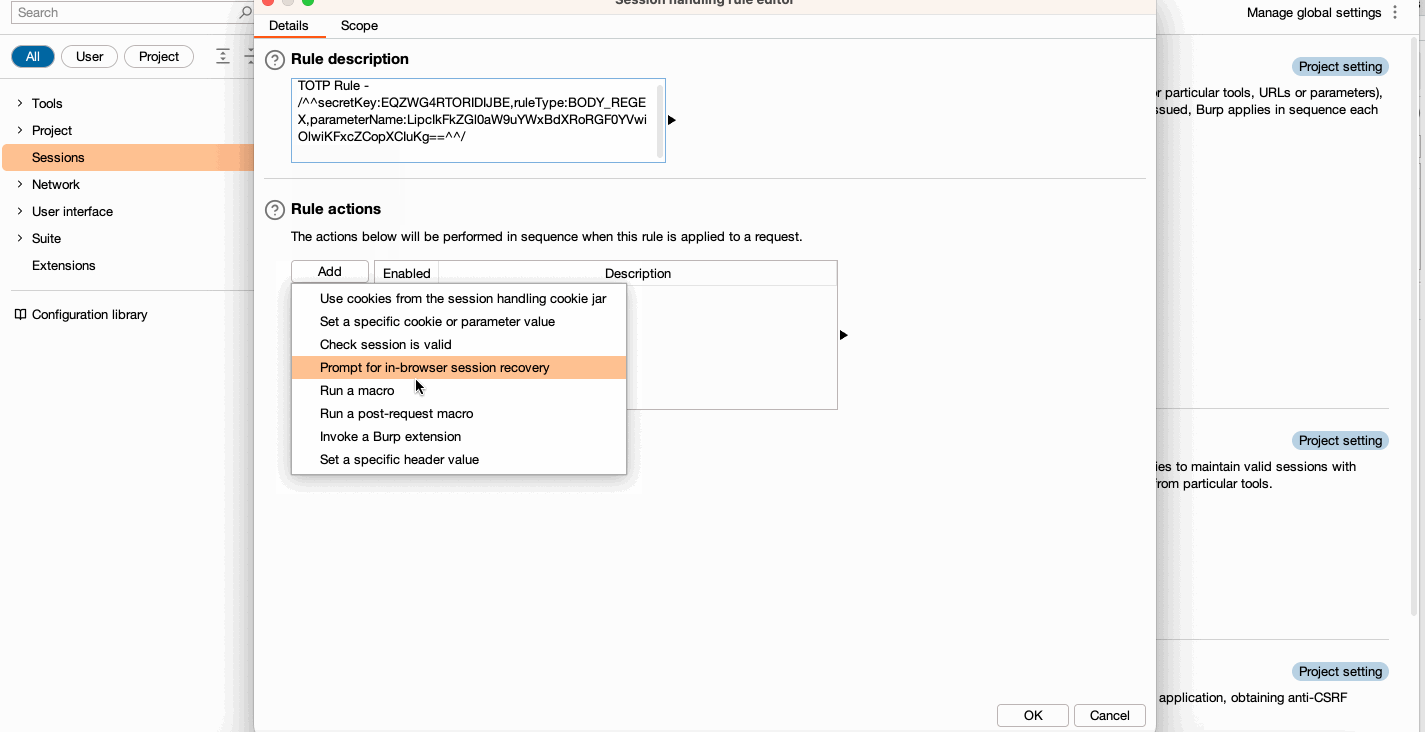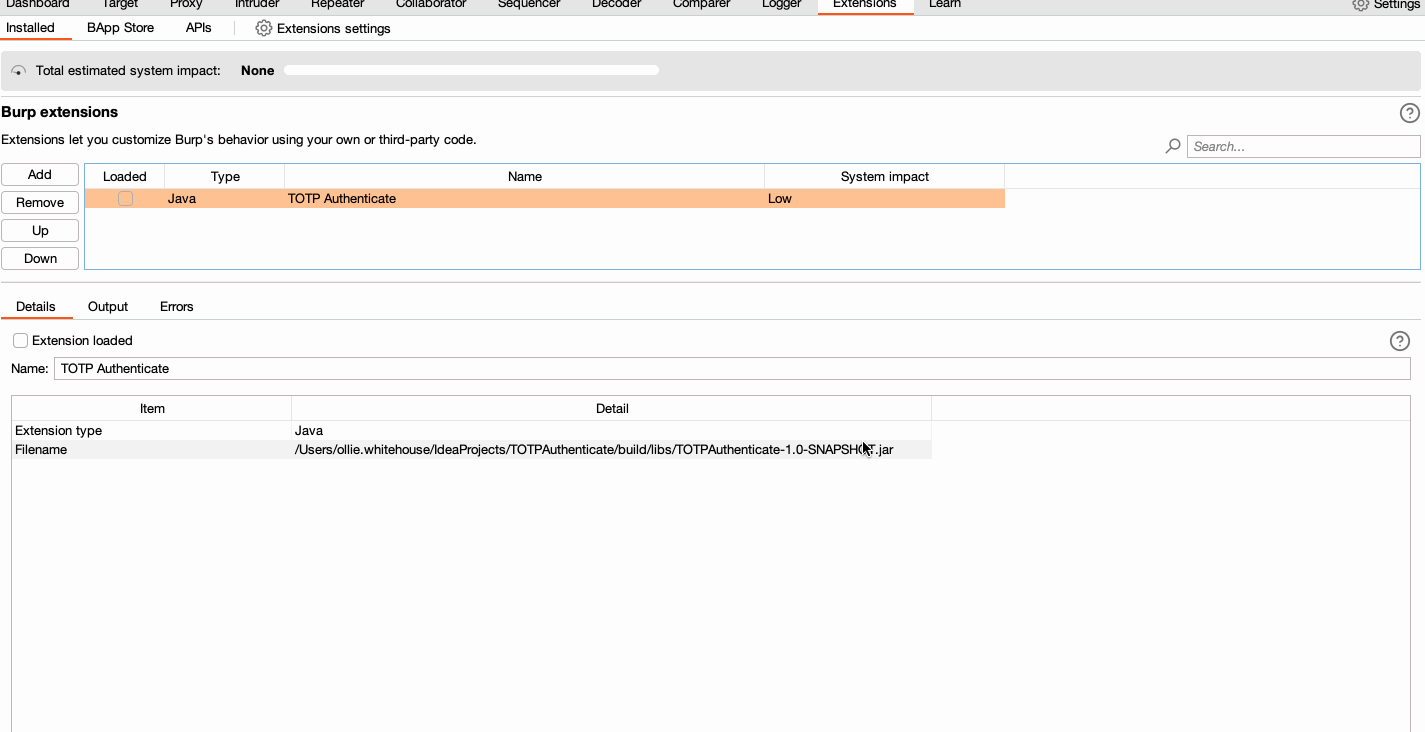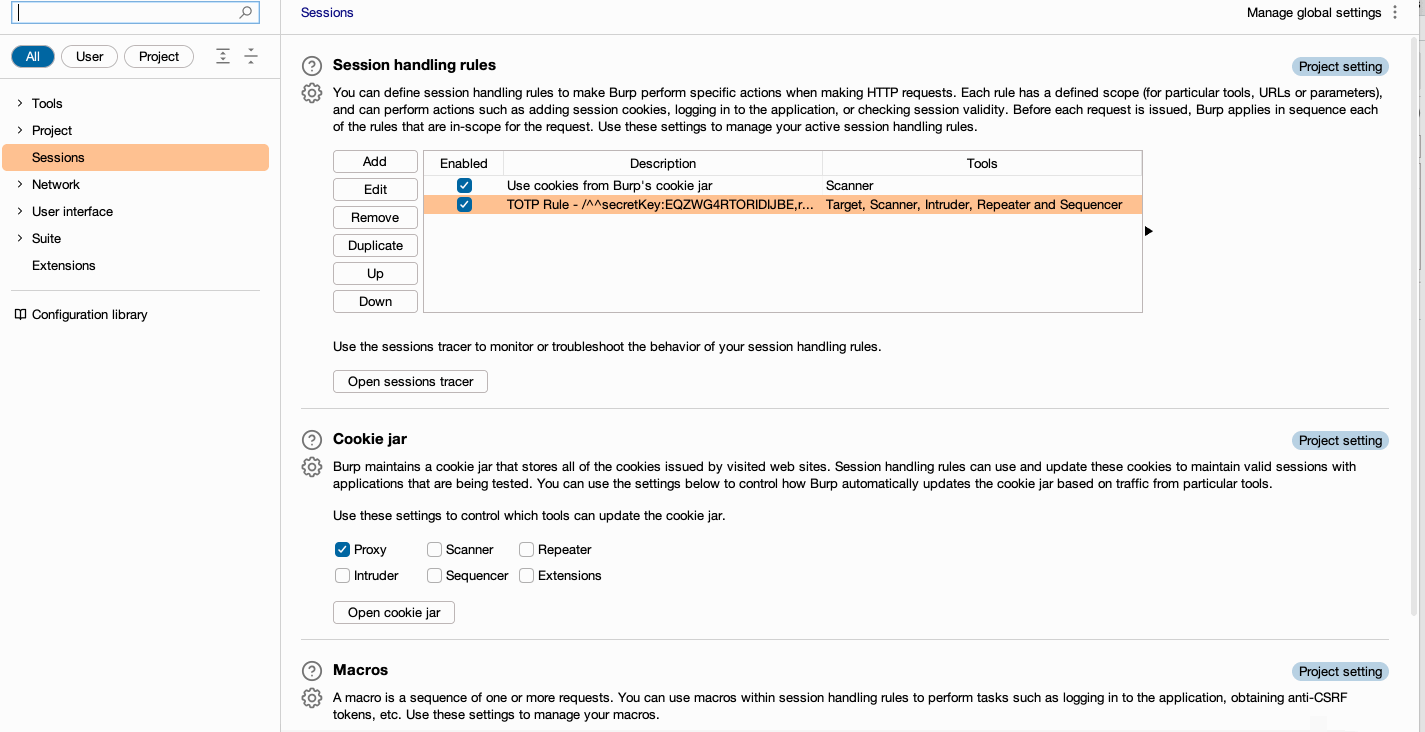
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
api-security-testingauthenticationpenetration-testing+1
92 years ago
CVE-2017-14263 preview

CVE-2017-14263

GitHubzzz66686/cve-2017-14263

Proof-of-concept exploit for CVE-2017-14263 in Honeywell NVR devices. Demonstrates session hijacking and privilege escalation from guest to admin via…
authenticationexploitationiot-security+3
59 years ago
By-Poloss..-..CVE-2026-19125 preview

By-Poloss..-..CVE-2026-19125

GitHubpolosss/by-poloss..-..cve-2026-19125

Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
authenticationexploitationpassword-attacks+5
15 days ago
CVE-2026-20079-checker preview

CVE-2026-20079-checker

GitHubdiegoarias008/cve-2026-20079-checker

Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
authenticationdefensive-toolsinformation-gathering+5
24 days ago
CVE-2026-78905-Facebook-Account-Takeover preview

CVE-2026-78905-Facebook-Account-Takeover

GitHubvxssroott/cve-2026-78905-facebook-account-takeover

Social Media Infrastructure Vulnerability Research. CVE-2026-78905: OAuth token reuse and session hijacking in Facebook's Graph API.
authenticationexploitationvulnerability-analysis+1
31 month ago
pocKeycloakCVE-2023-0264 preview

pocKeycloakCVE-2023-0264

GitHubeliangonzi00/pockeycloakcve-2023-0264

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
authenticationdefensive-toolsexploitation+7
2 months ago
CVE-2025-23048-POC preview

CVE-2025-23048-POC

GitHubabsholi7ly/cve-2025-23048-poc

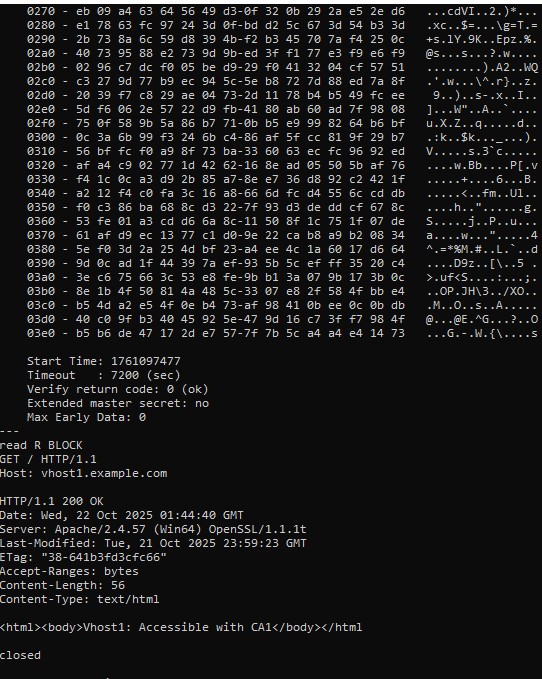
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
authenticationexploitationpenetration-testing+3
411 months ago
Kerberos_CVE-2022-33679 preview

Kerberos_CVE-2022-33679

GitHubnotareaperbutdr34p3r/kerberos_cve-2022-33679

Python exploit for CVE-2022-33679 targeting Kerberos authentication to perform privilege escalation on Windows domain controllers via RC4 session key…

authenticationexploitationnetwork-security+2
43 years ago
magento2-session-reaper-patch preview

magento2-session-reaper-patch

GitHubwubinworks/magento2-session-reaper-patch

Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…
authenticationexploitationvulnerability-analysis+2
411 months ago
CVE-2026-20896-Gitea-Authentication-Bypass preview

CVE-2026-20896-Gitea-Authentication-Bypass

GitHubjudgedbykira/cve-2026-20896-gitea-authentication-bypass

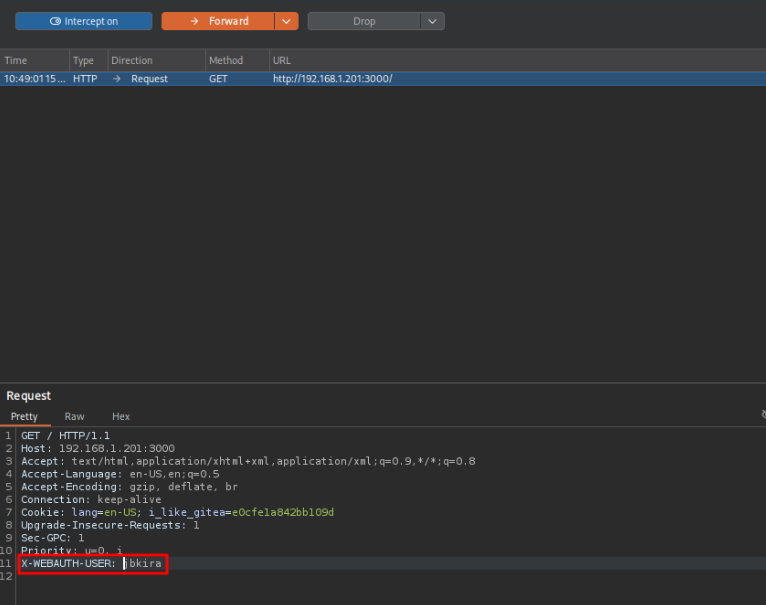
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
authenticationeducationexploitation+5
11 month ago
Research-CVE-2026-21858 preview

Research-CVE-2026-21858

GitHubbannt08/research-cve-2026-21858

Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
authenticationexploitationremote-access-trojan+2
5 months ago
cPanel-WHM-CVE-2026-41940-AuthBypass preview

cPanel-WHM-CVE-2026-41940-AuthBypass

GitHubisee857/cpanel-whm-cve-2026-41940-authbypass

Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…
authenticationexploitationpenetration-testing+4
5 months ago
cve-2022-23131 preview

cve-2022-23131

GitHubwr0x00/cve-2022-23131

Exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Generates a signed session cookie to gain unauthorized admin access.

authenticationexploitationpenetration-testing+2
13 years ago
Previous123Next