
copyfail-rs
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
authenticationbinary-exploitationexploitation+7
liverwortenuresis371/copyfail-rsExploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 sajaljat/cve-2023-46449
Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
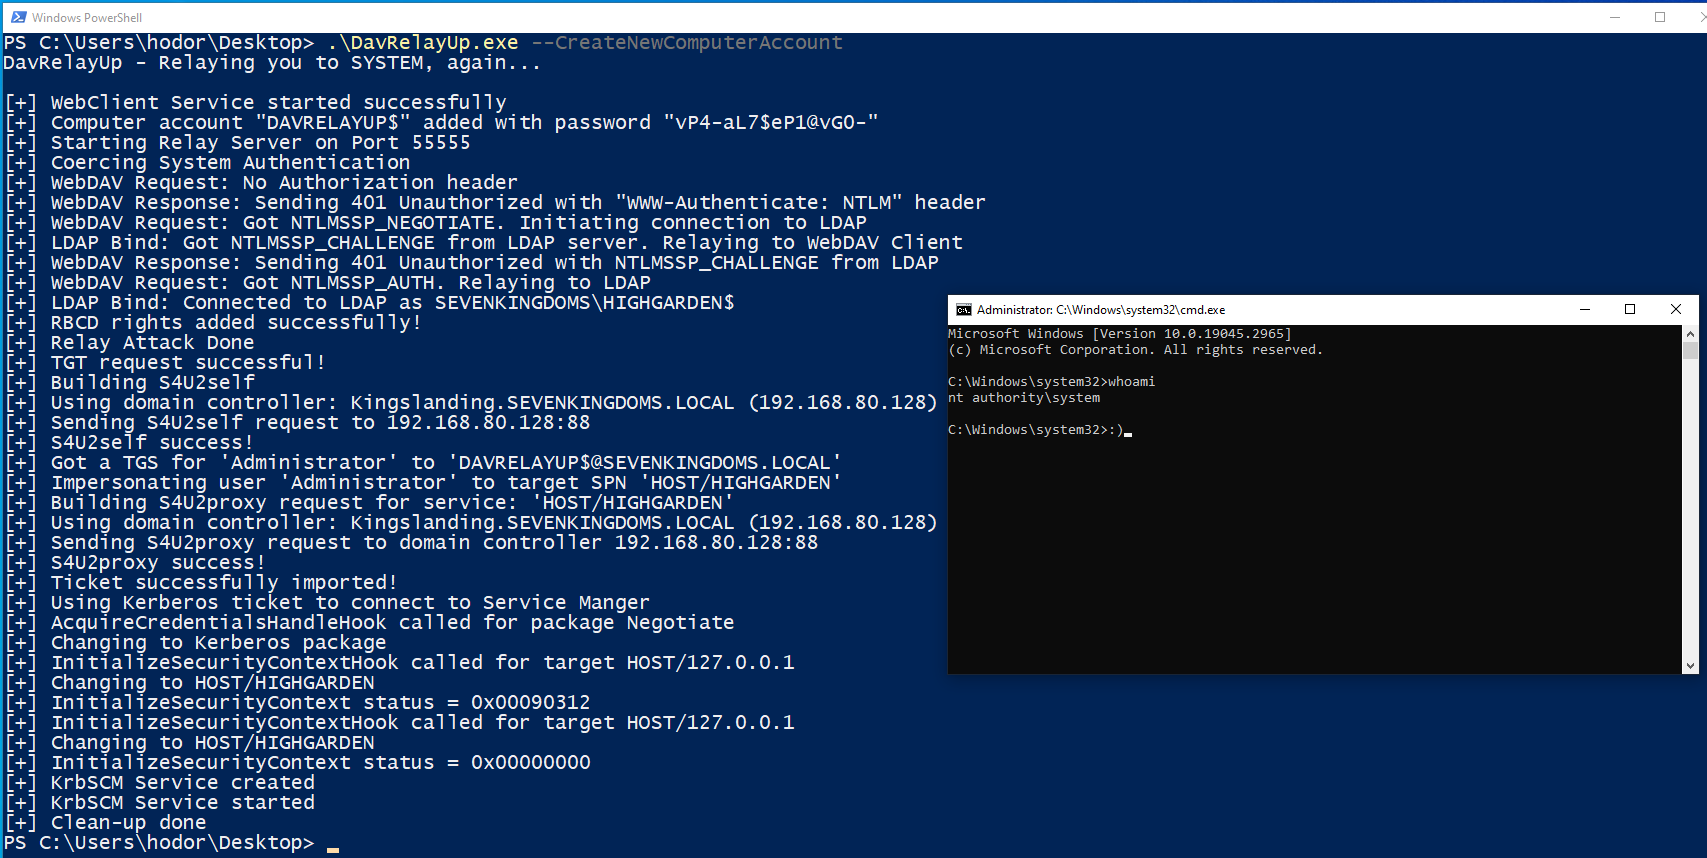 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
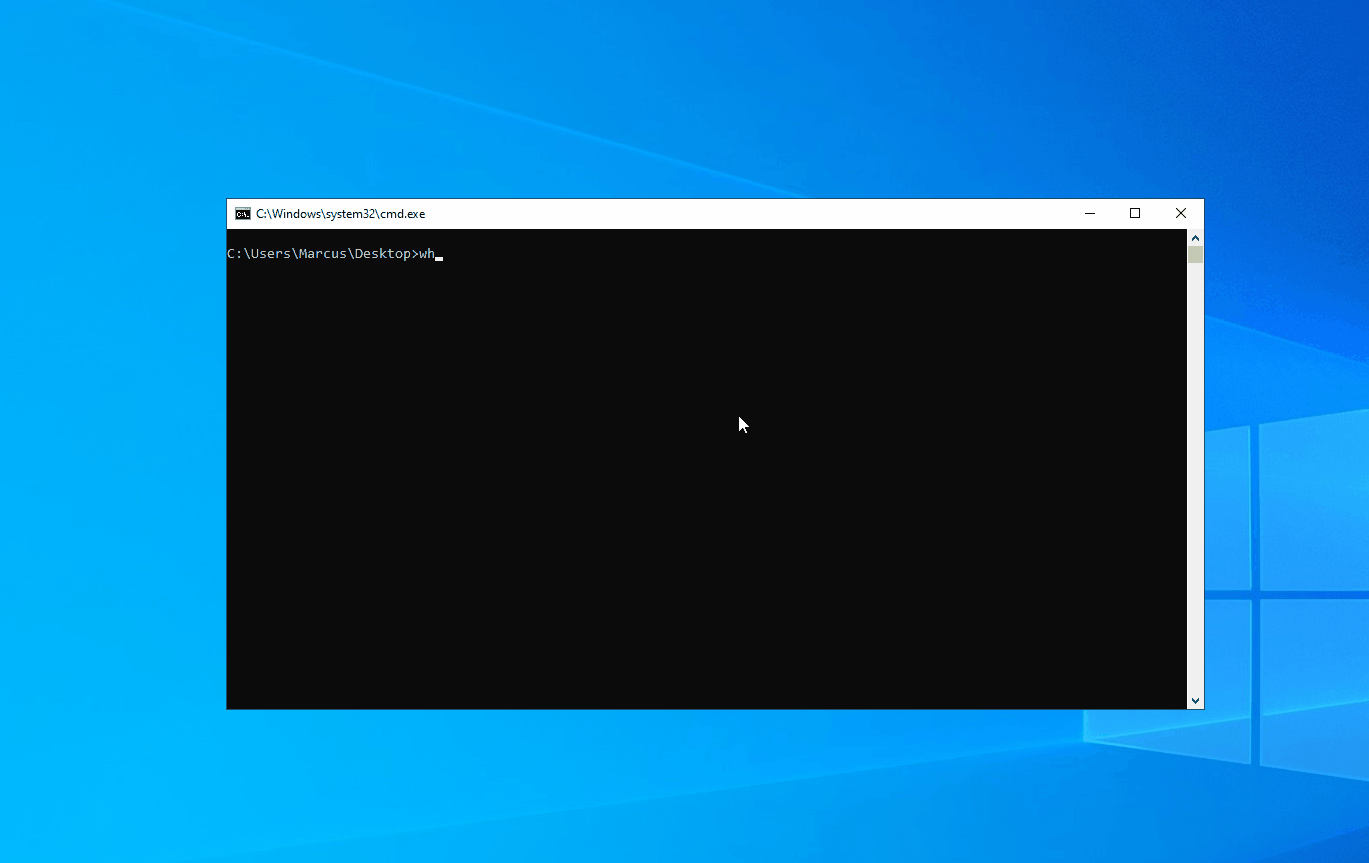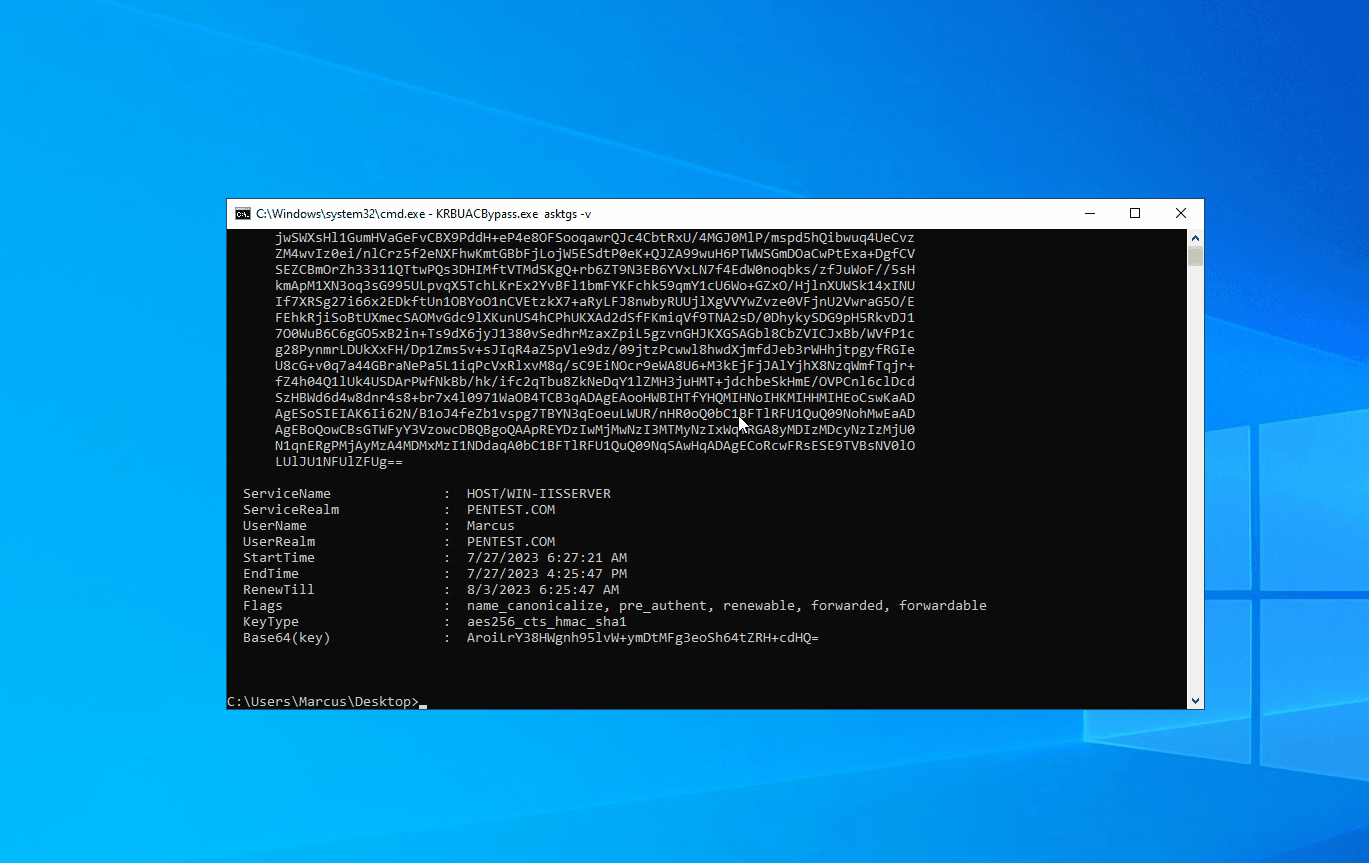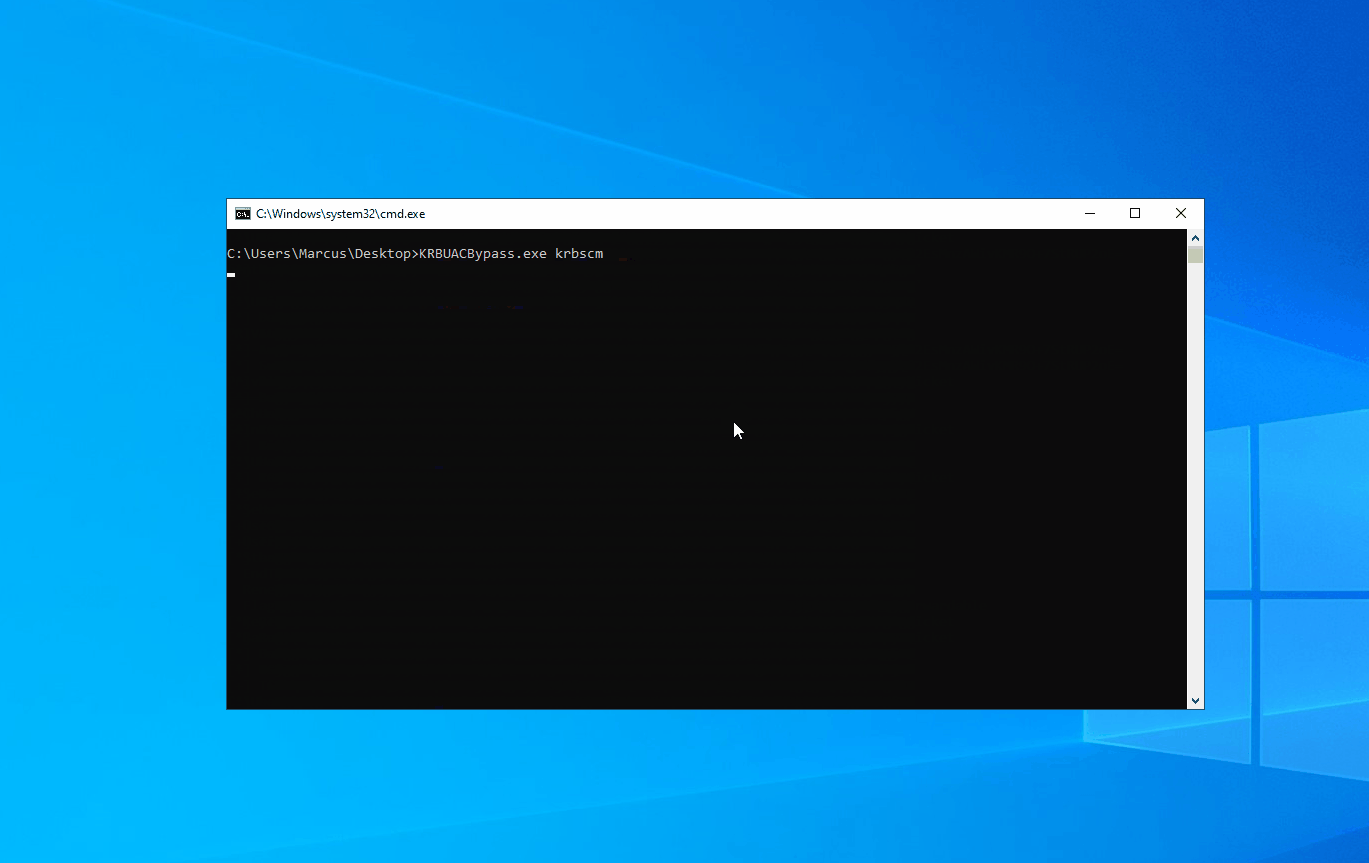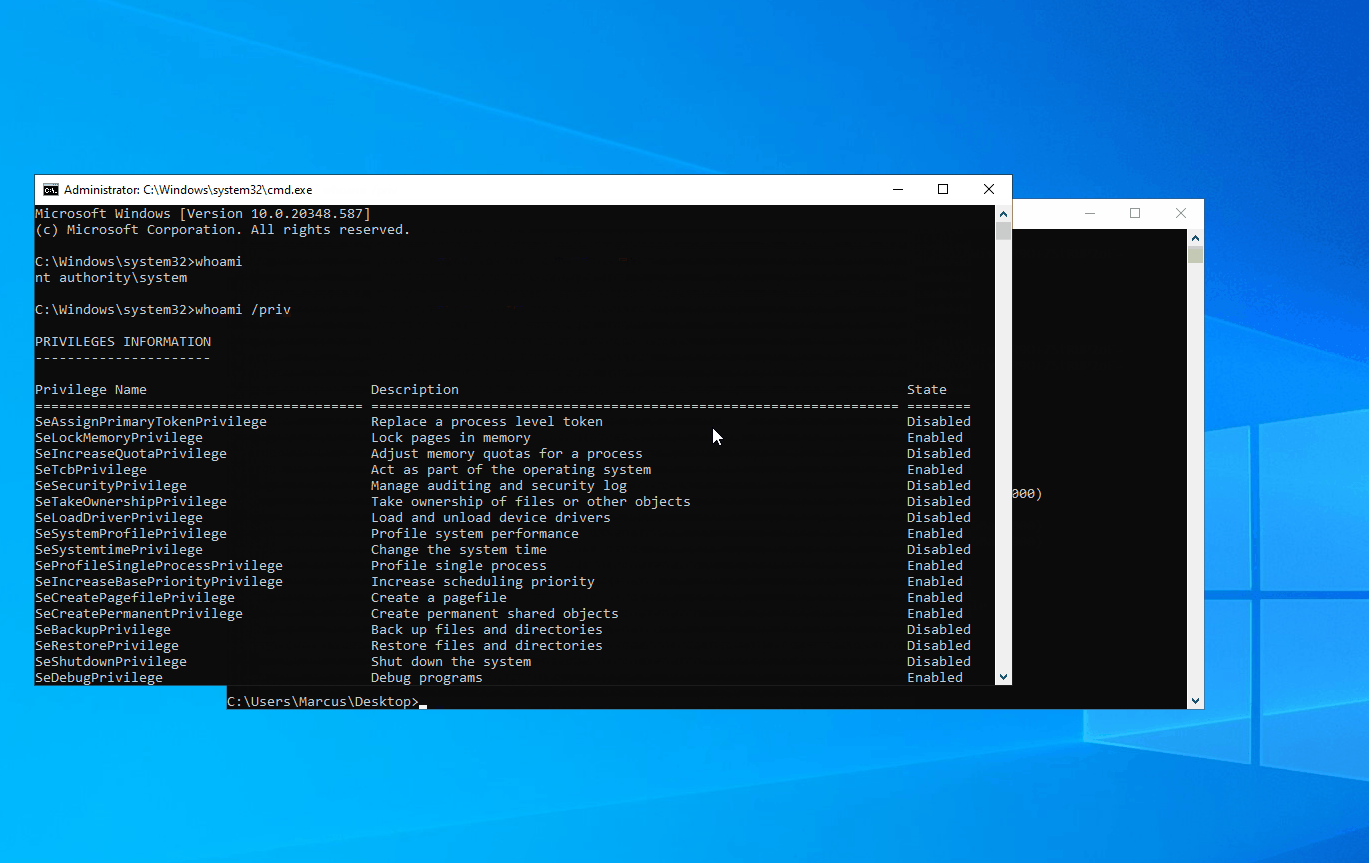 wh0amitz/krbuacbypass
Abuses Kerberos tickets to bypass Windows UAC and gain SYSTEM privileges by injecting a fake MachineID into service tickets, leveraging the tgtdeleg…
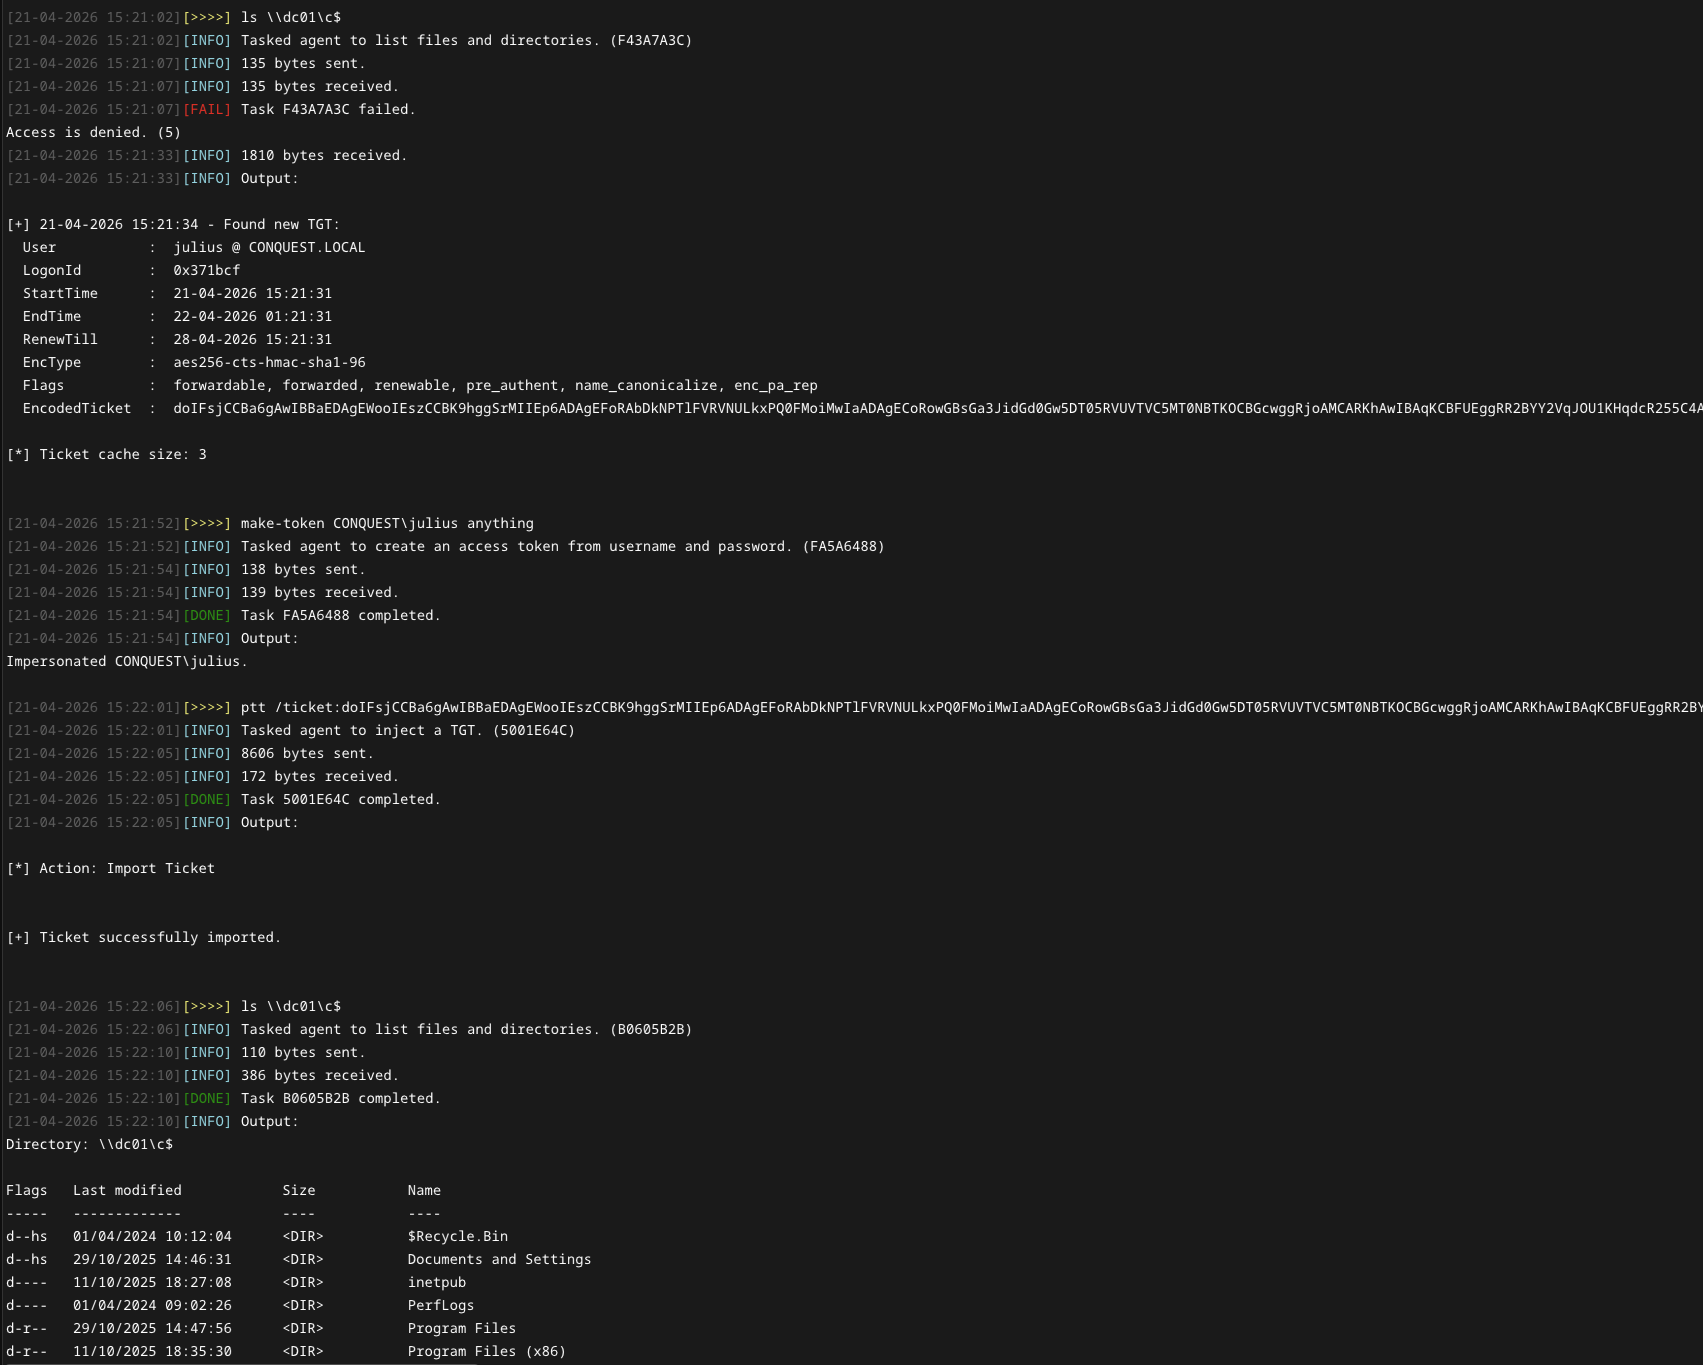 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
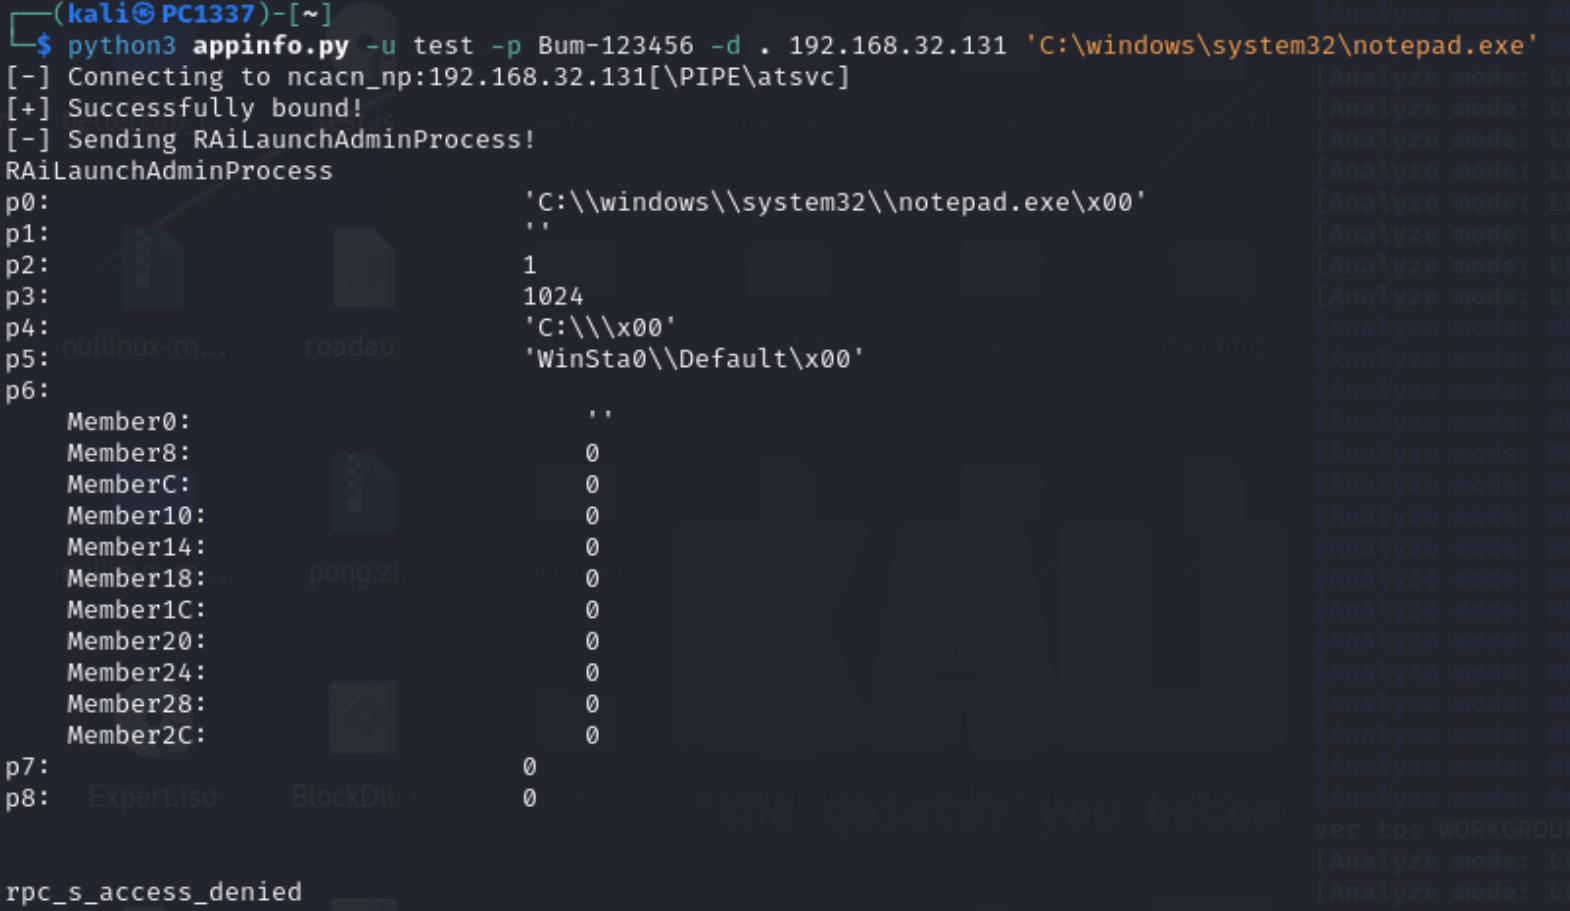 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
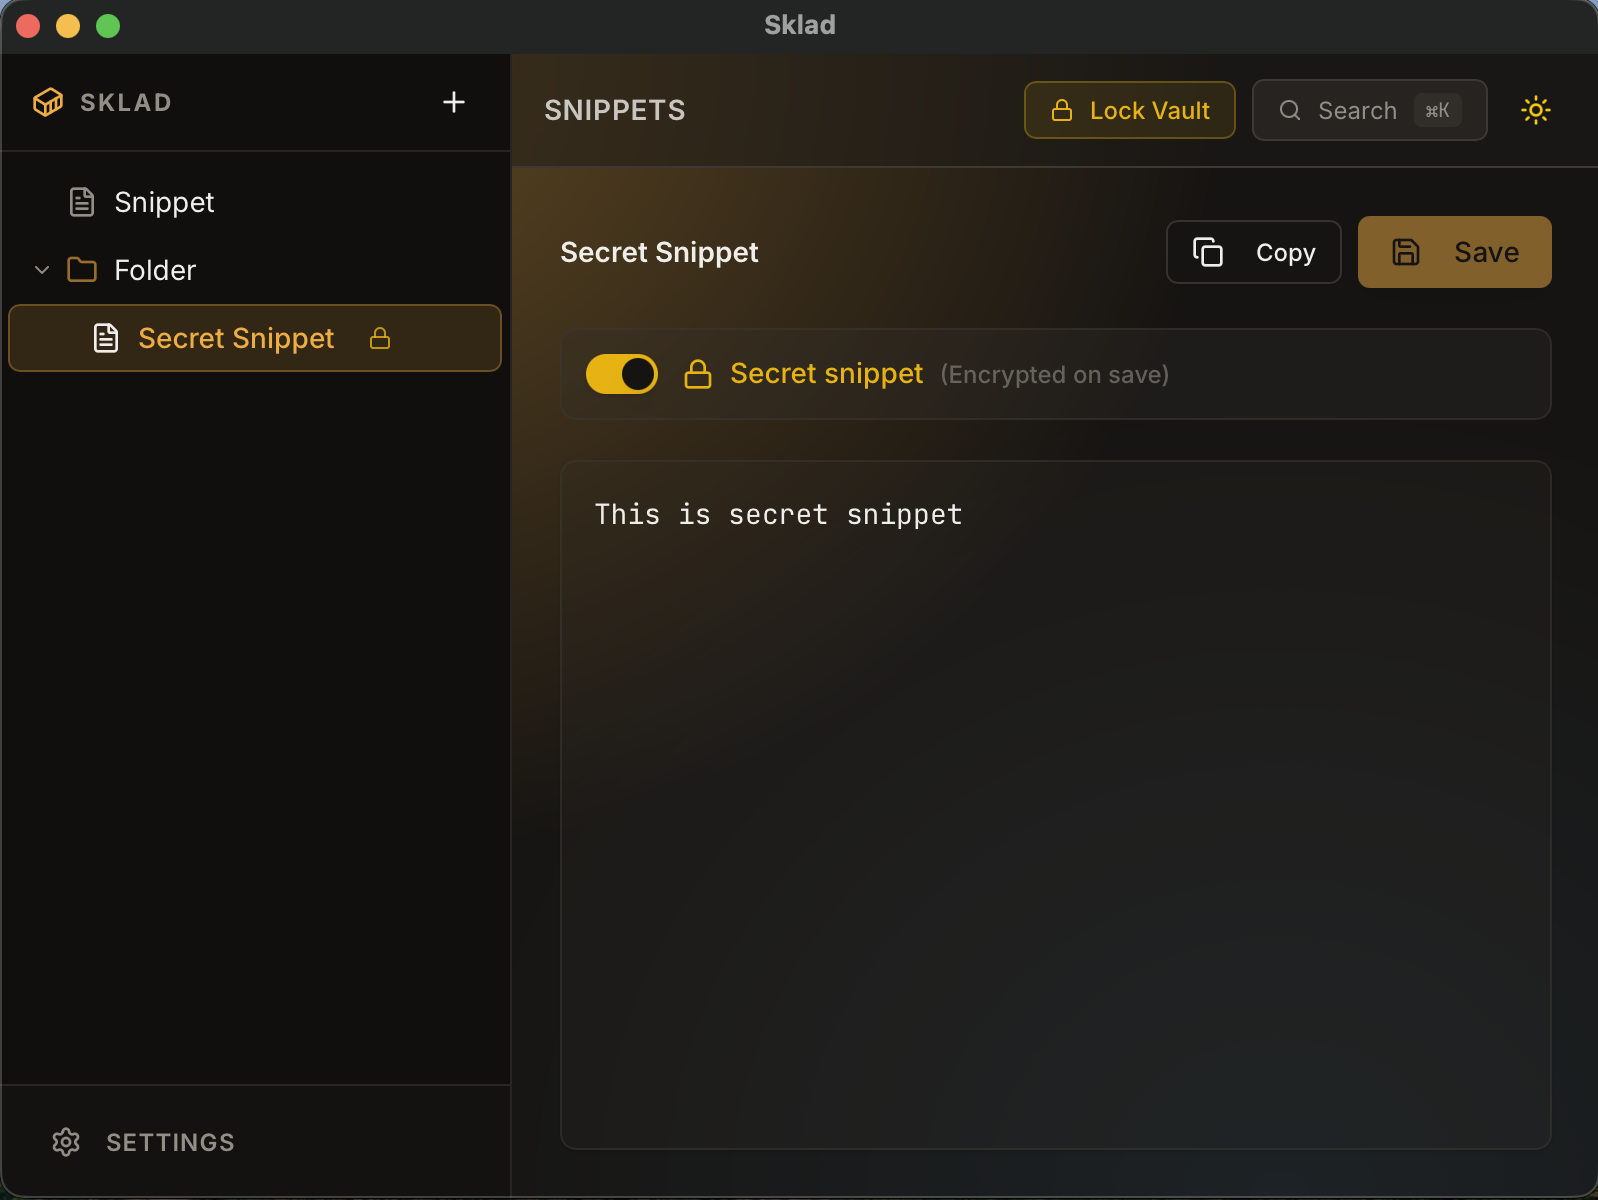 rench321/sklad
Industrial-grade secure snippet warehouse for your system tray. 📦 Built with Rust (Tauri v2) & React. Offline-first, AES-256 encrypted, and…
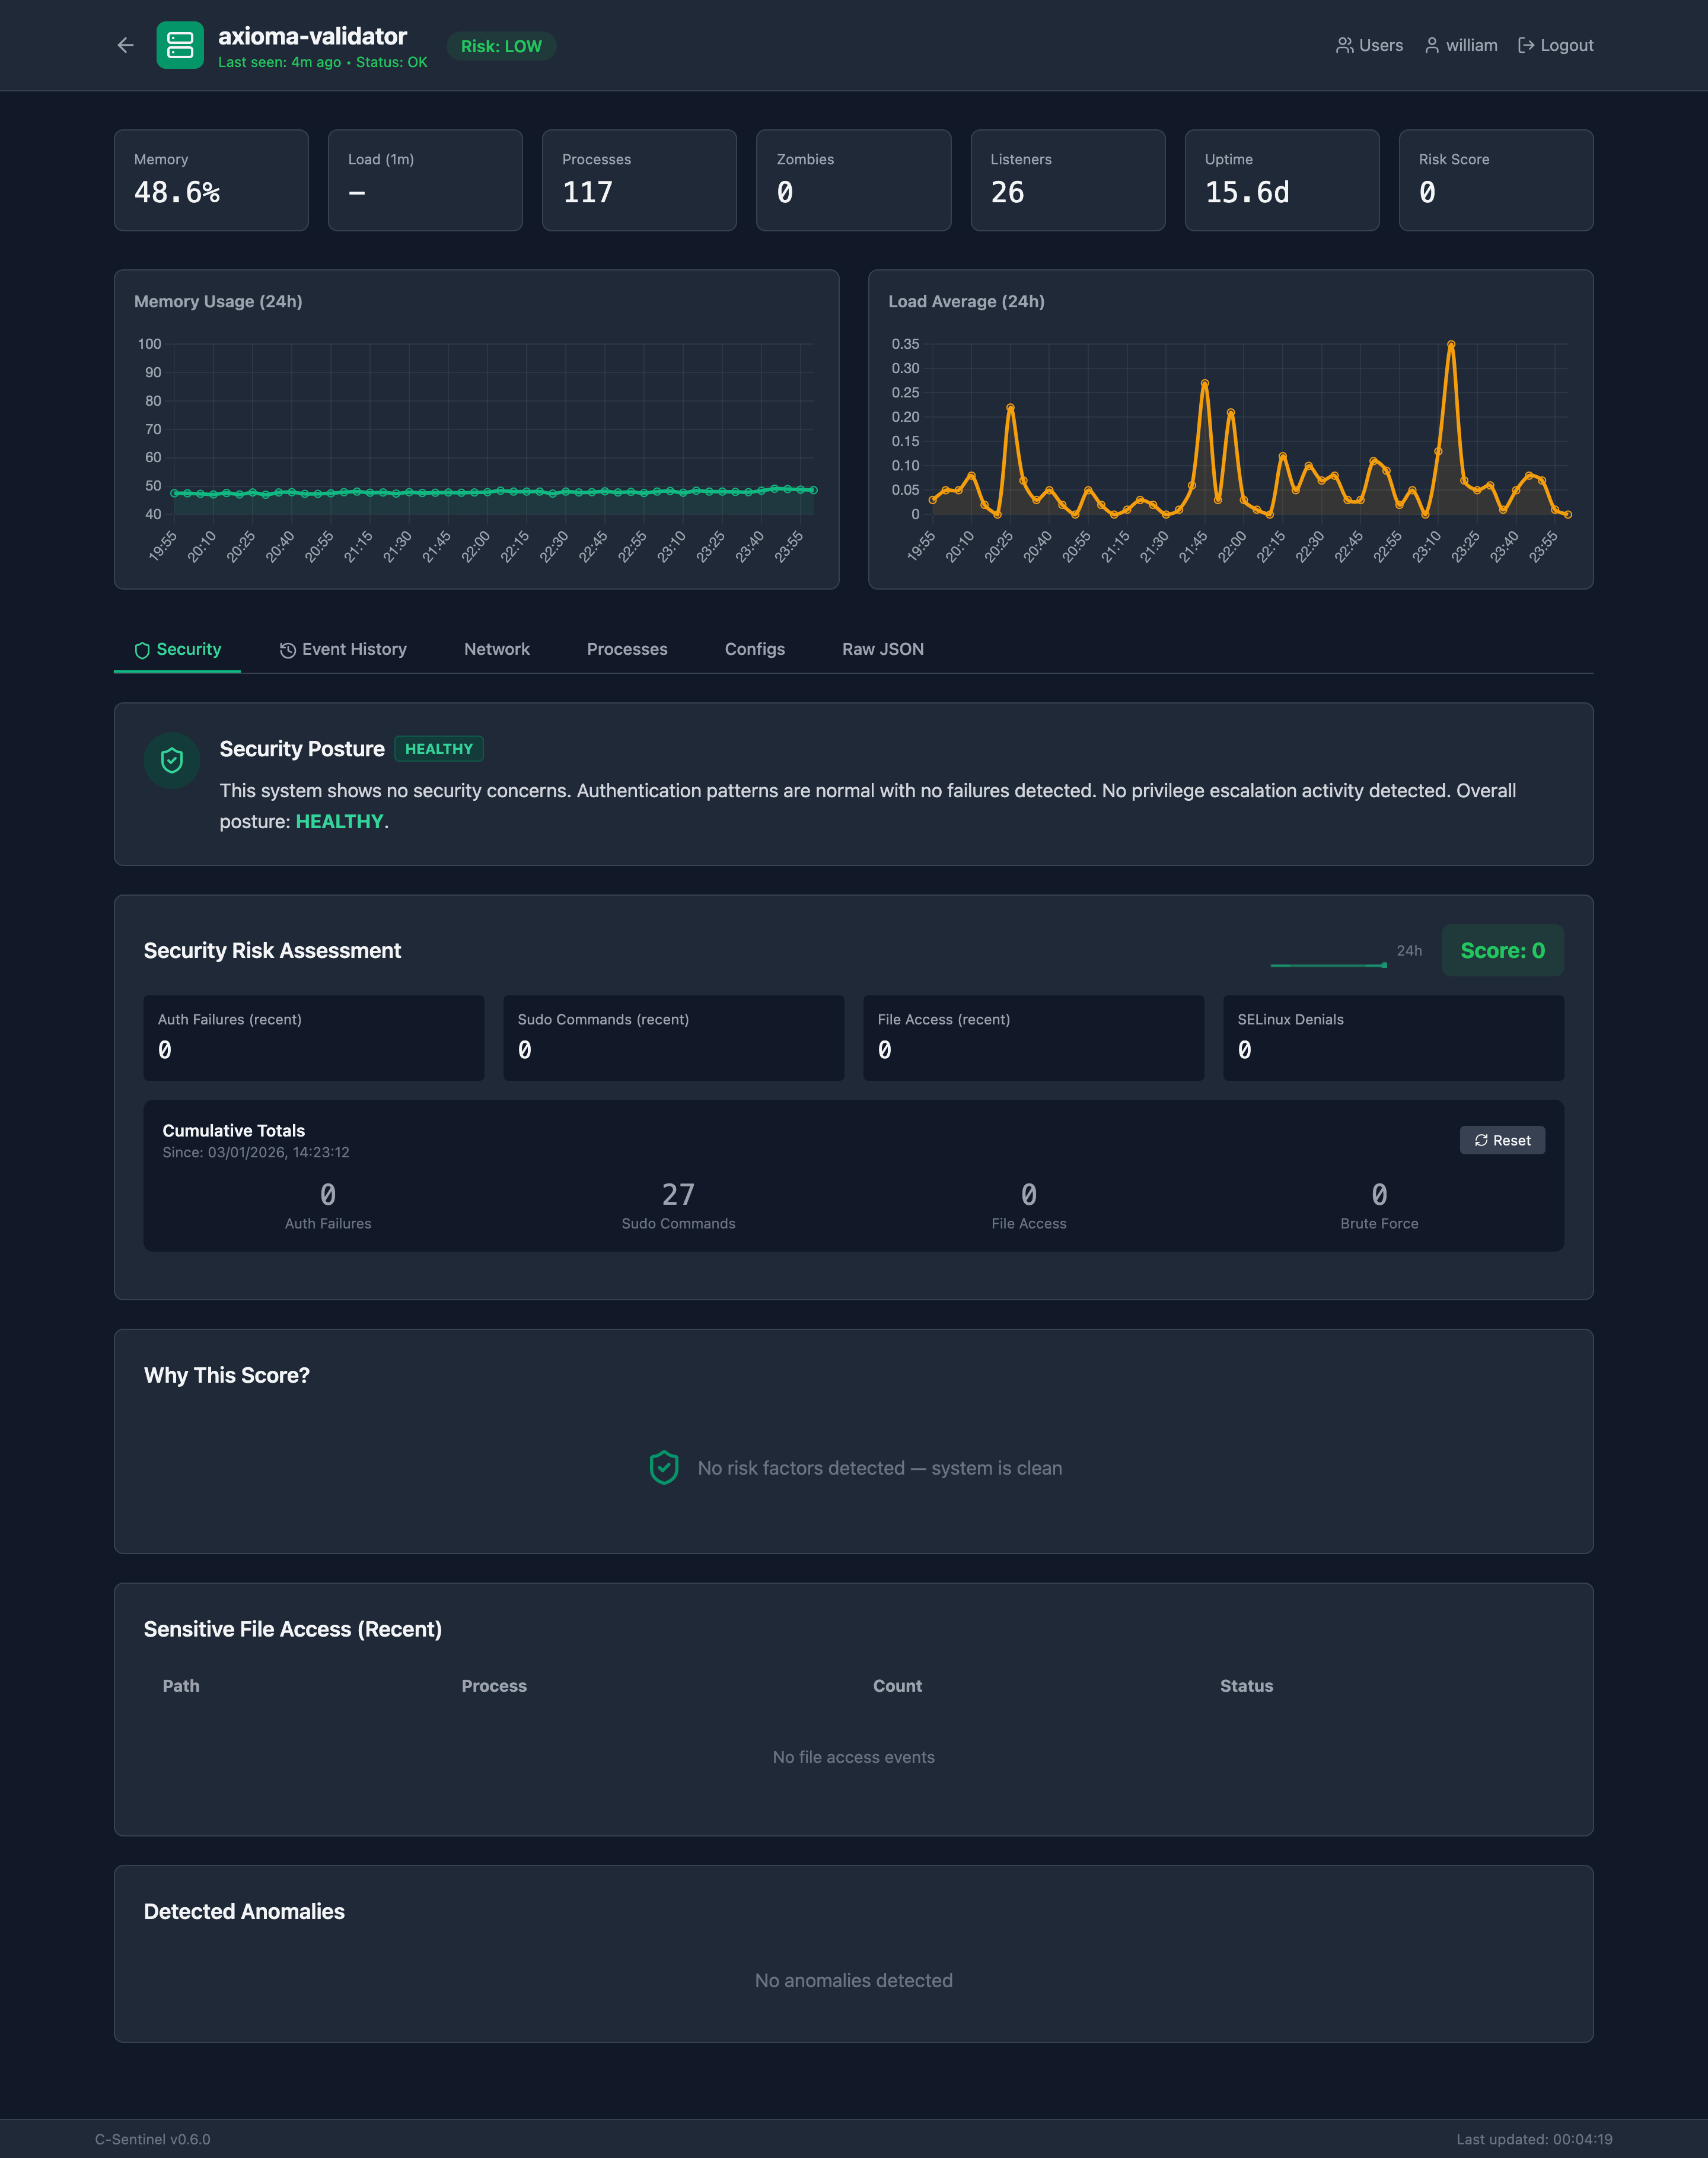 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 0katz/cve-2019-12476
PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 watchtowrlabs/watchtowr-vs-bmc-footprints-rce-cve-2025-71257-cve-2025-71260
Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…
 rashidkhanpathan/cve-2022-38813
Authenticated Vertical Privilege Escalation Vulnerability in Blood Donor Management System
 retrymp3/openbsd-privilege-escalation
Script that automates the process of escalating privileges on openbsd system (CVE-2019-19520) by exploiting the xlock binary and againing it's sgid…
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.