

web2py-e94946d-CVE-2016-3957
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
authenticationcode-analysisdatabase-security+3
sj/web2py-e94946d-cve-2016-3957web2py/web2py @ e94946d
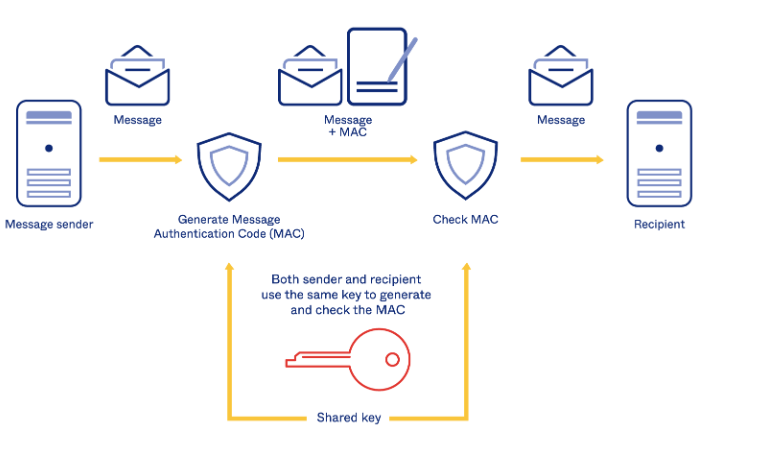 password123456/about-hmac
HMAC Implementation Example and Explanation
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 crowecybersecurity/ad-ldap-enum
An LDAP based Active Directory user and group enumeration tool
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
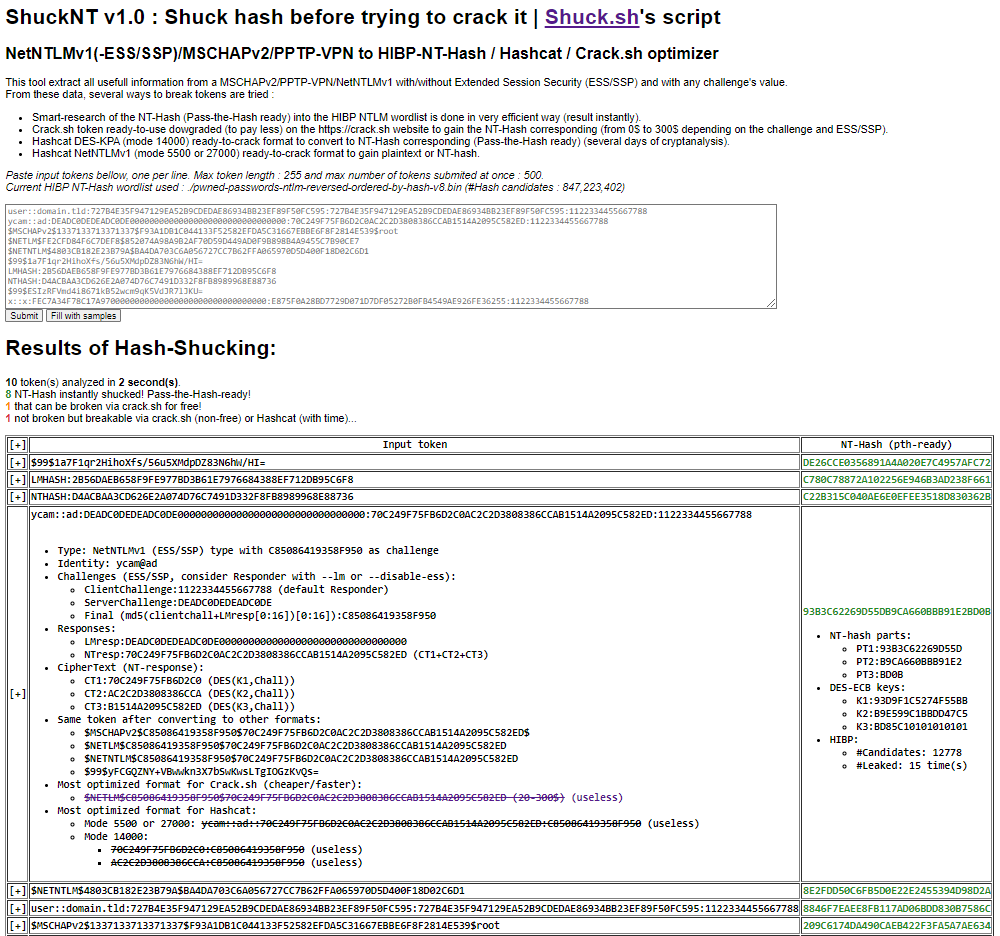 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 jazzpizazz/bloodhound.py-kerberos
A Python based ingestor for BloodHound
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 ninjazan420/cve-2025-52691-poc-smartermail-authentication-bypass-exploit-wt-2026-0001
CVE-2025-52691 PoC: Based on watchtowr's article WT-2026-0001 about an authentication bypass exploit, this one is a functional Python attack script.