
ntlmscout
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
56
boydhacks/ntlmscoutUnauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 initroot/cve-2022-23342
Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…
 curtishoughton/cve-2025-20362-cisco-scanner
Safe Python scanner for CVE-2025-20362 (Cisco ASA/FTD WebVPN Authentication Bypass)
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
 pwnfoo/ntlmrecon
Enumerate information from NTLM authentication enabled web endpoints 🔎
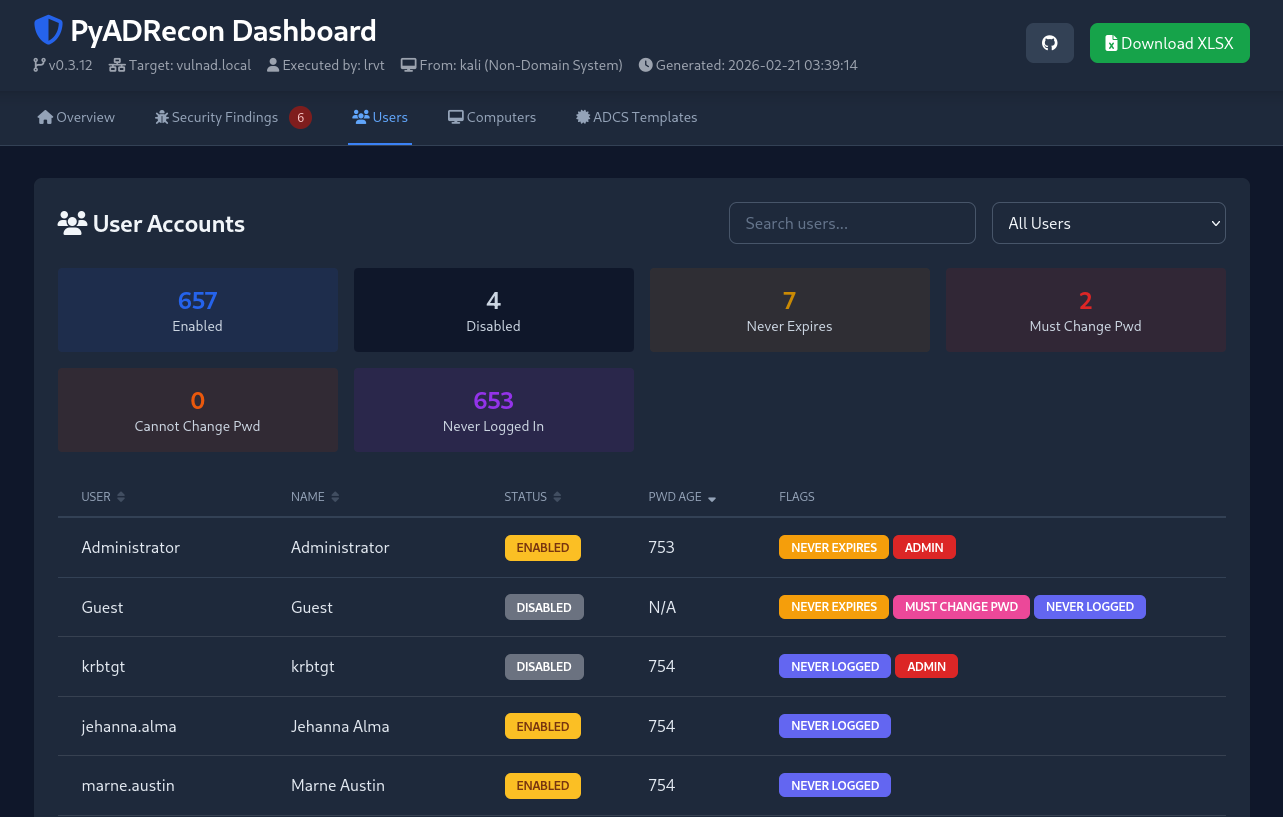 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
 evilsocket/legba
The fastest and more comprehensive multiprotocol credentials bruteforcer / password sprayer and enumerator. 🥷
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
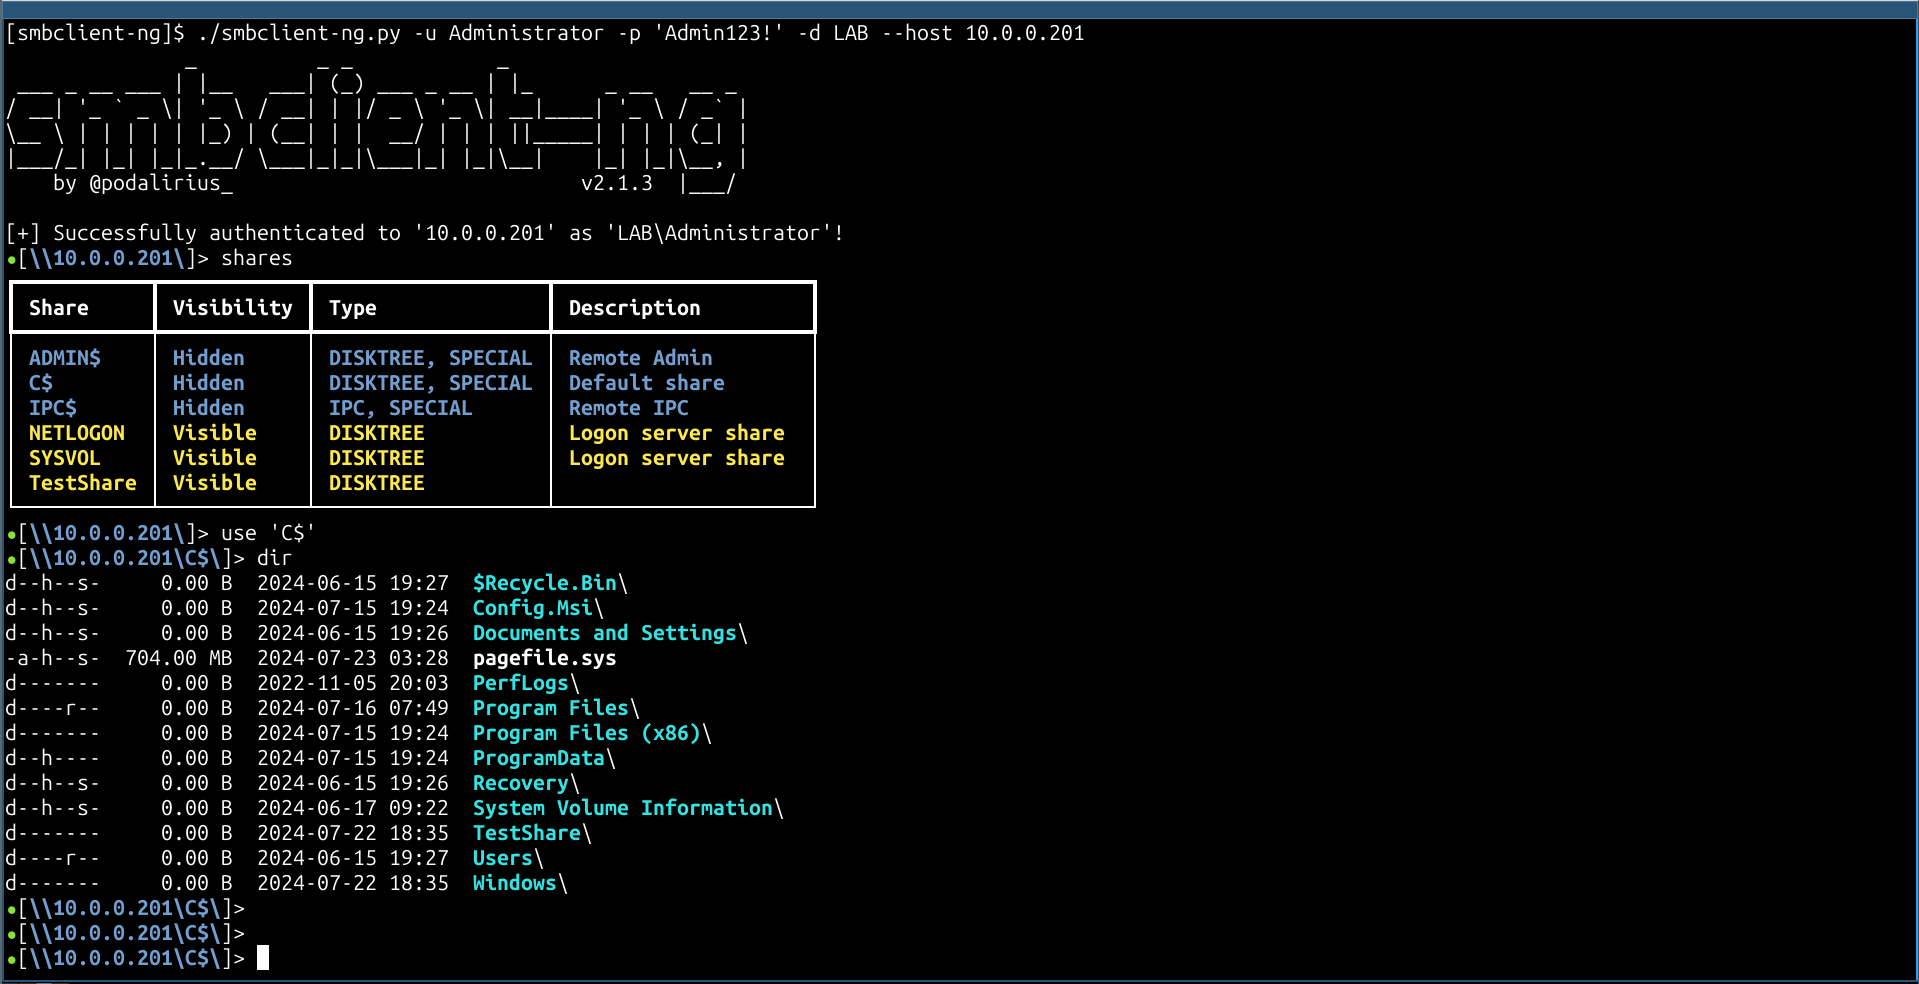 p0dalirius/smbclient-ng
smbclient-ng, a fast and user friendly way to interact with SMB shares.
 greenwolf/spray
A Password Spraying tool for Active Directory Credentials by Jacob Wilkin(Greenwolf)
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
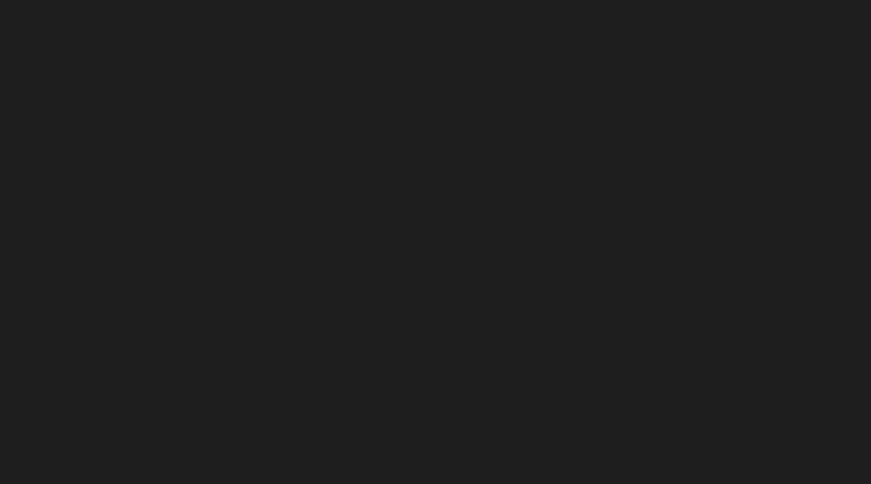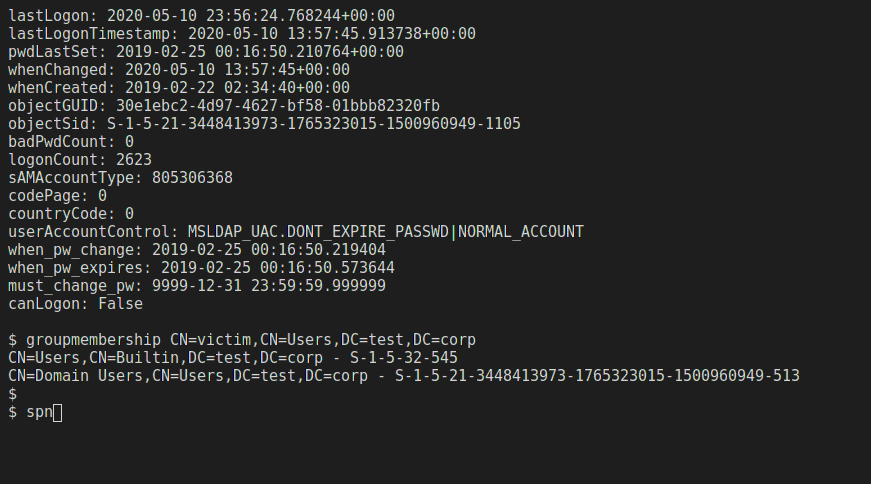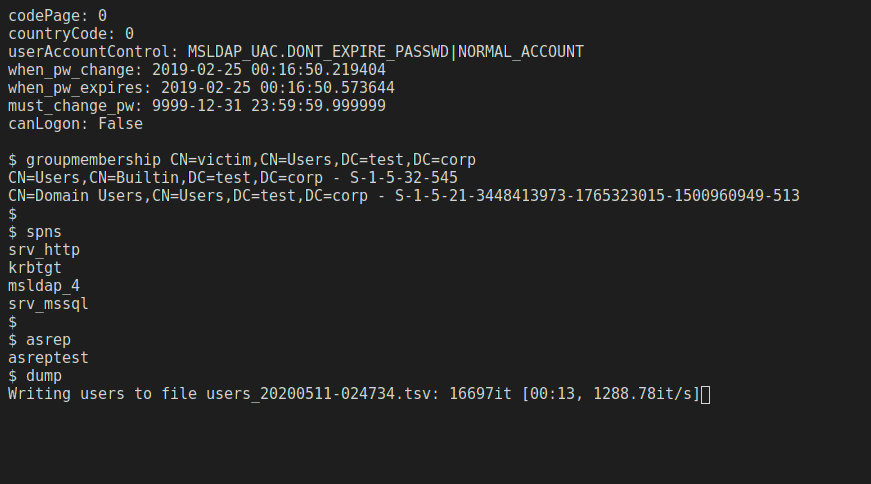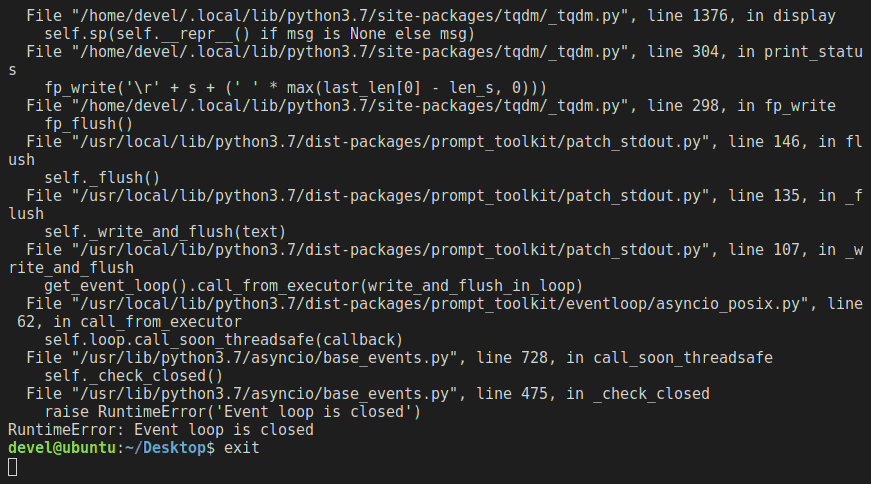 skelsec/msldap
Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)