

TelnetdBypass-
 ahmadsadeeq/telnetdbypass-
CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
authenticationexploitationinformation-gathering+3
ahmadsadeeq/telnetdbypass-CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
 saladin0x1/cve-2025-53770
Proof-of-concept exploit toolkit for SharePoint ToolPane RCE (CVE-2025-53770) with scanner, payload analysis, and multiple exploitation methods for…
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
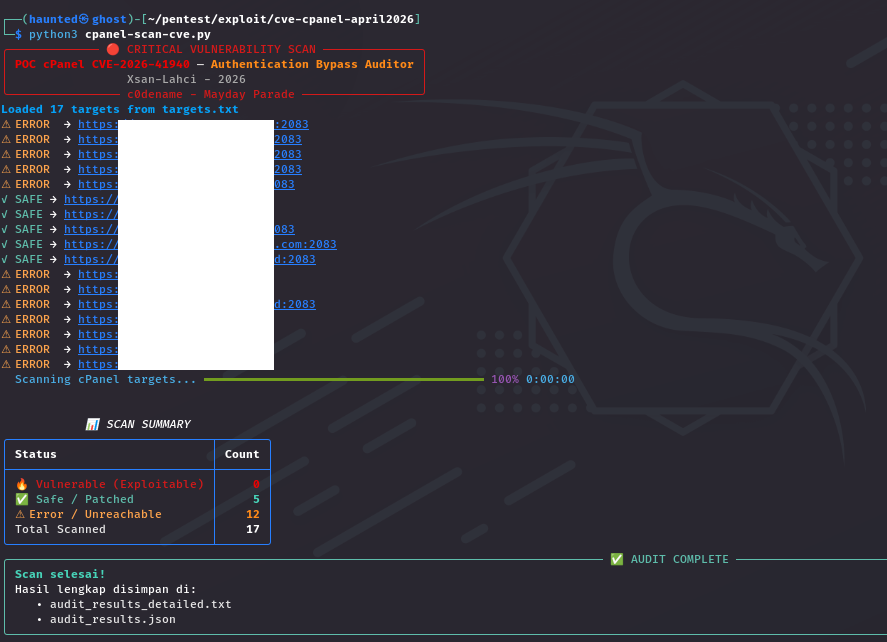 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…