CVE-2025-58434-AND-59528-POC

Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…

Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…

Python exploit for CVE-2026-76504, a Cisco Catalyst SD-WAN Manager authentication bypass via percent-encoded j_security_check, with token theft, API…

Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…

A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…

Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.

Python proof-of-concept for the CVE-2026-123158 SSHole OpenSSH authentication bypass, sending an oversized password to trigger a reverse shell to a…

SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO

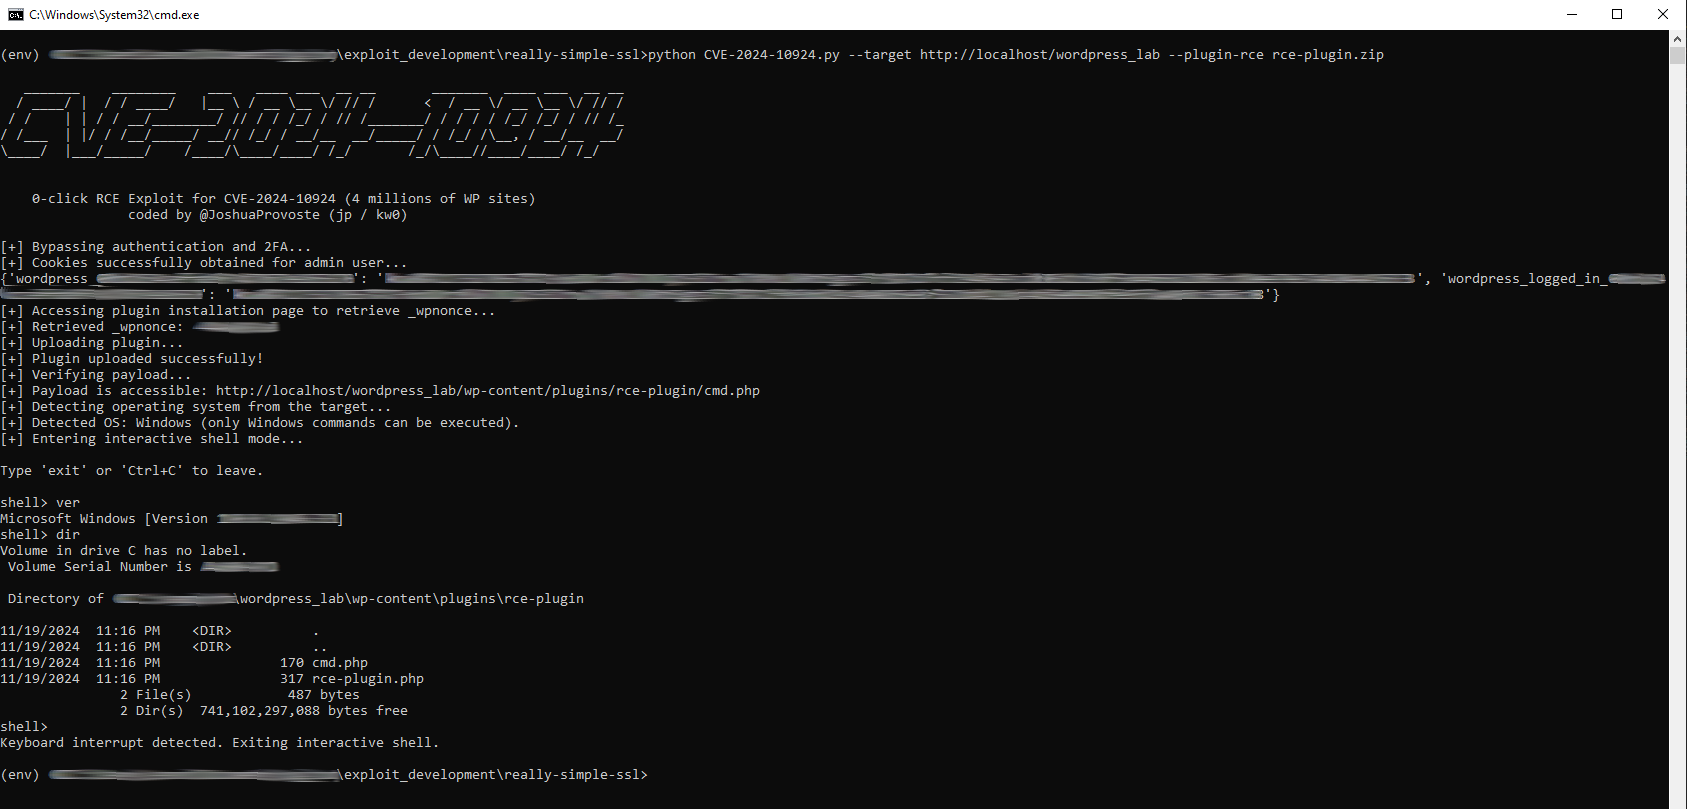
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…

The ultimate WinRM shell for hacking/pentesting

A lightweight CLI tool to interactively search and access your KeePassXC database entries using fzf. Fast, secure, and terminal-centric.

Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

Fast, secure shell protocol built on HTTP/3, QUIC, and TLS 1.3. Supports OAuth2, OpenID Connect, and classical SSH authentication with UDP port…

Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…

Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…