

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.6k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
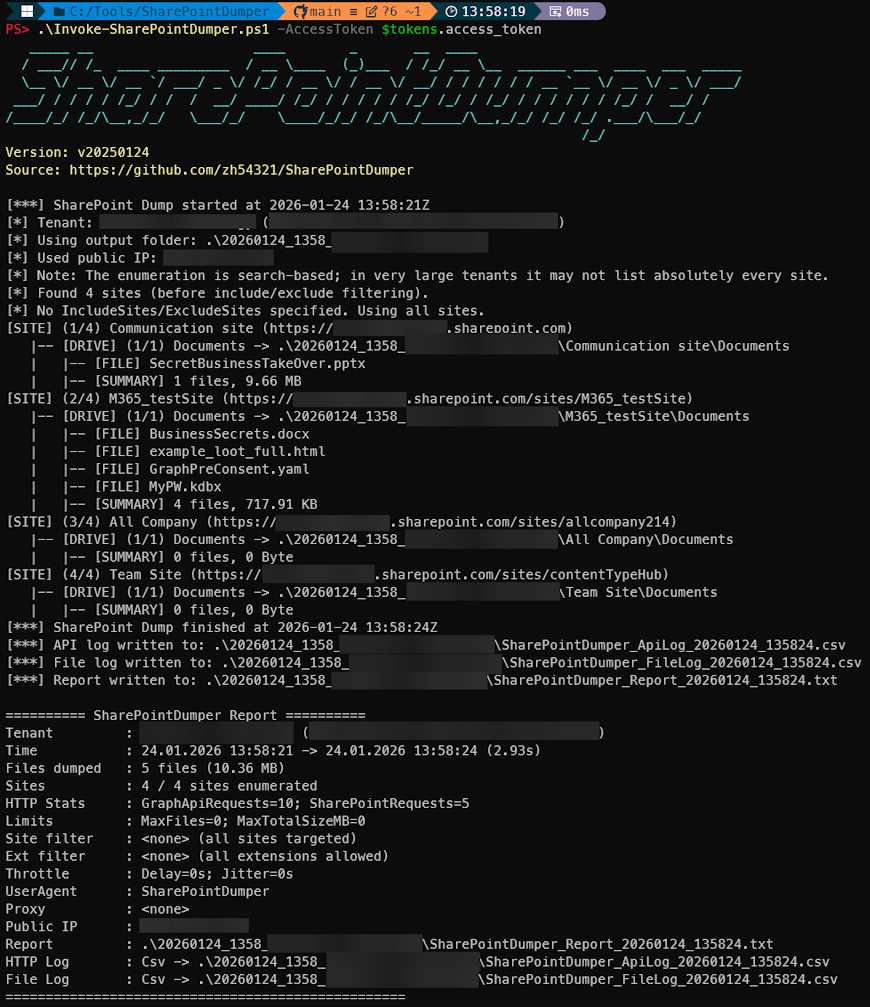 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
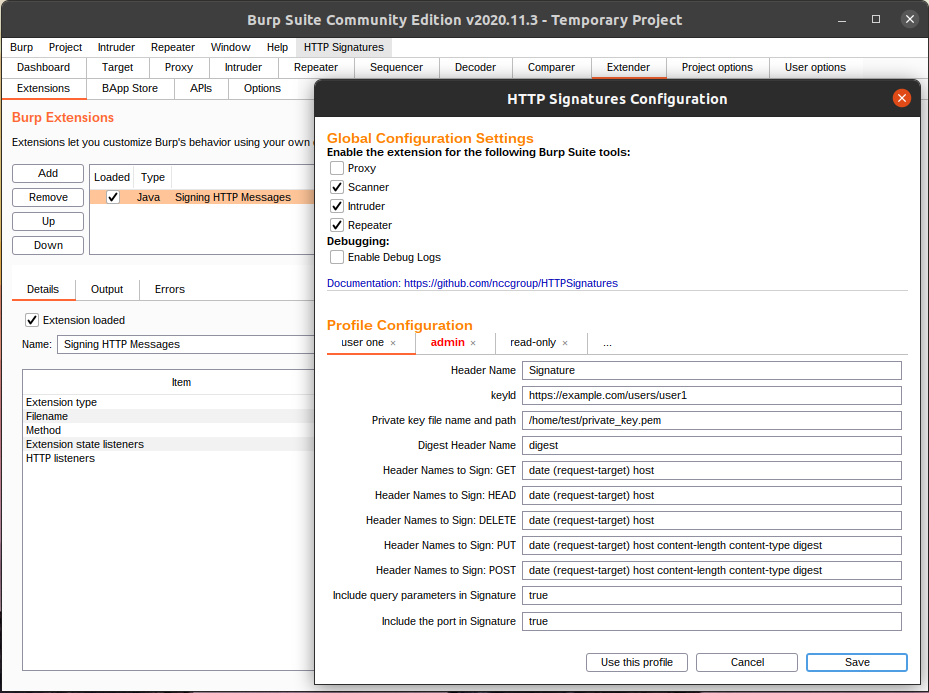 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 lukaszstu/pritunl-cve-2020-25200
Exploit for CVE-2020-25200: enumerates valid Pritunl VPN usernames by analyzing HTTP response code changes after repeated login attempts.
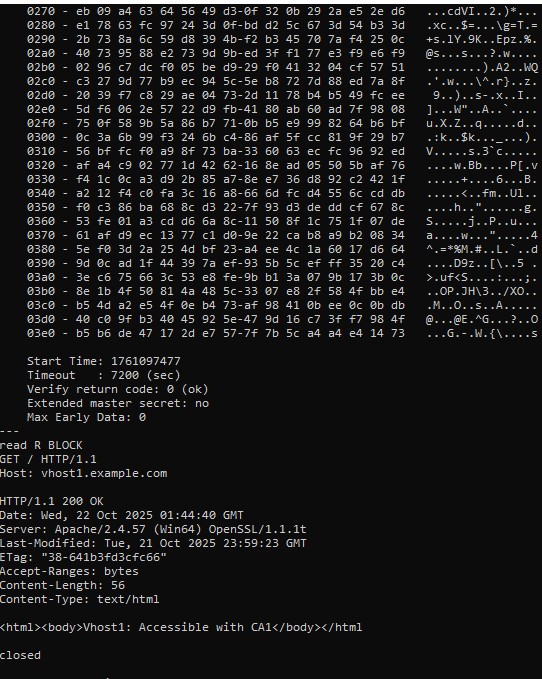 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 faizzaidi/typo3-v7.6.15-unencrypted-login-request
Proof-of-concept exploit for TYPO3 v7.6.15 unencrypted login request vulnerability (CVE-2017-6370), demonstrating plaintext credential exposure over…
 itres-labs/cve-2025-1868
CVE-2025-1868: Advanced IP Scanner & Advanced Port Scanner NTLM Leakage HTTP Tester