
pritunl
 pritunl/pritunl
Provides distributed enterprise VPN connectivity using OpenVPN, with centralized management, authentication, and encrypted tunnels for cloud and…
authenticationnetwork-access-controlnetwork-security+2
5.0k
pritunl/pritunlProvides distributed enterprise VPN connectivity using OpenVPN, with centralized management, authentication, and encrypted tunnels for cloud and…
 minanagehsalalma/zyxel-social-login-bypass-cve-2026-8508
Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.
 rub-softsec/onelogon
Code and data for our paper "Onelogon: Taking over Active Directory Accounts via Netlogon" (WOOT’26).
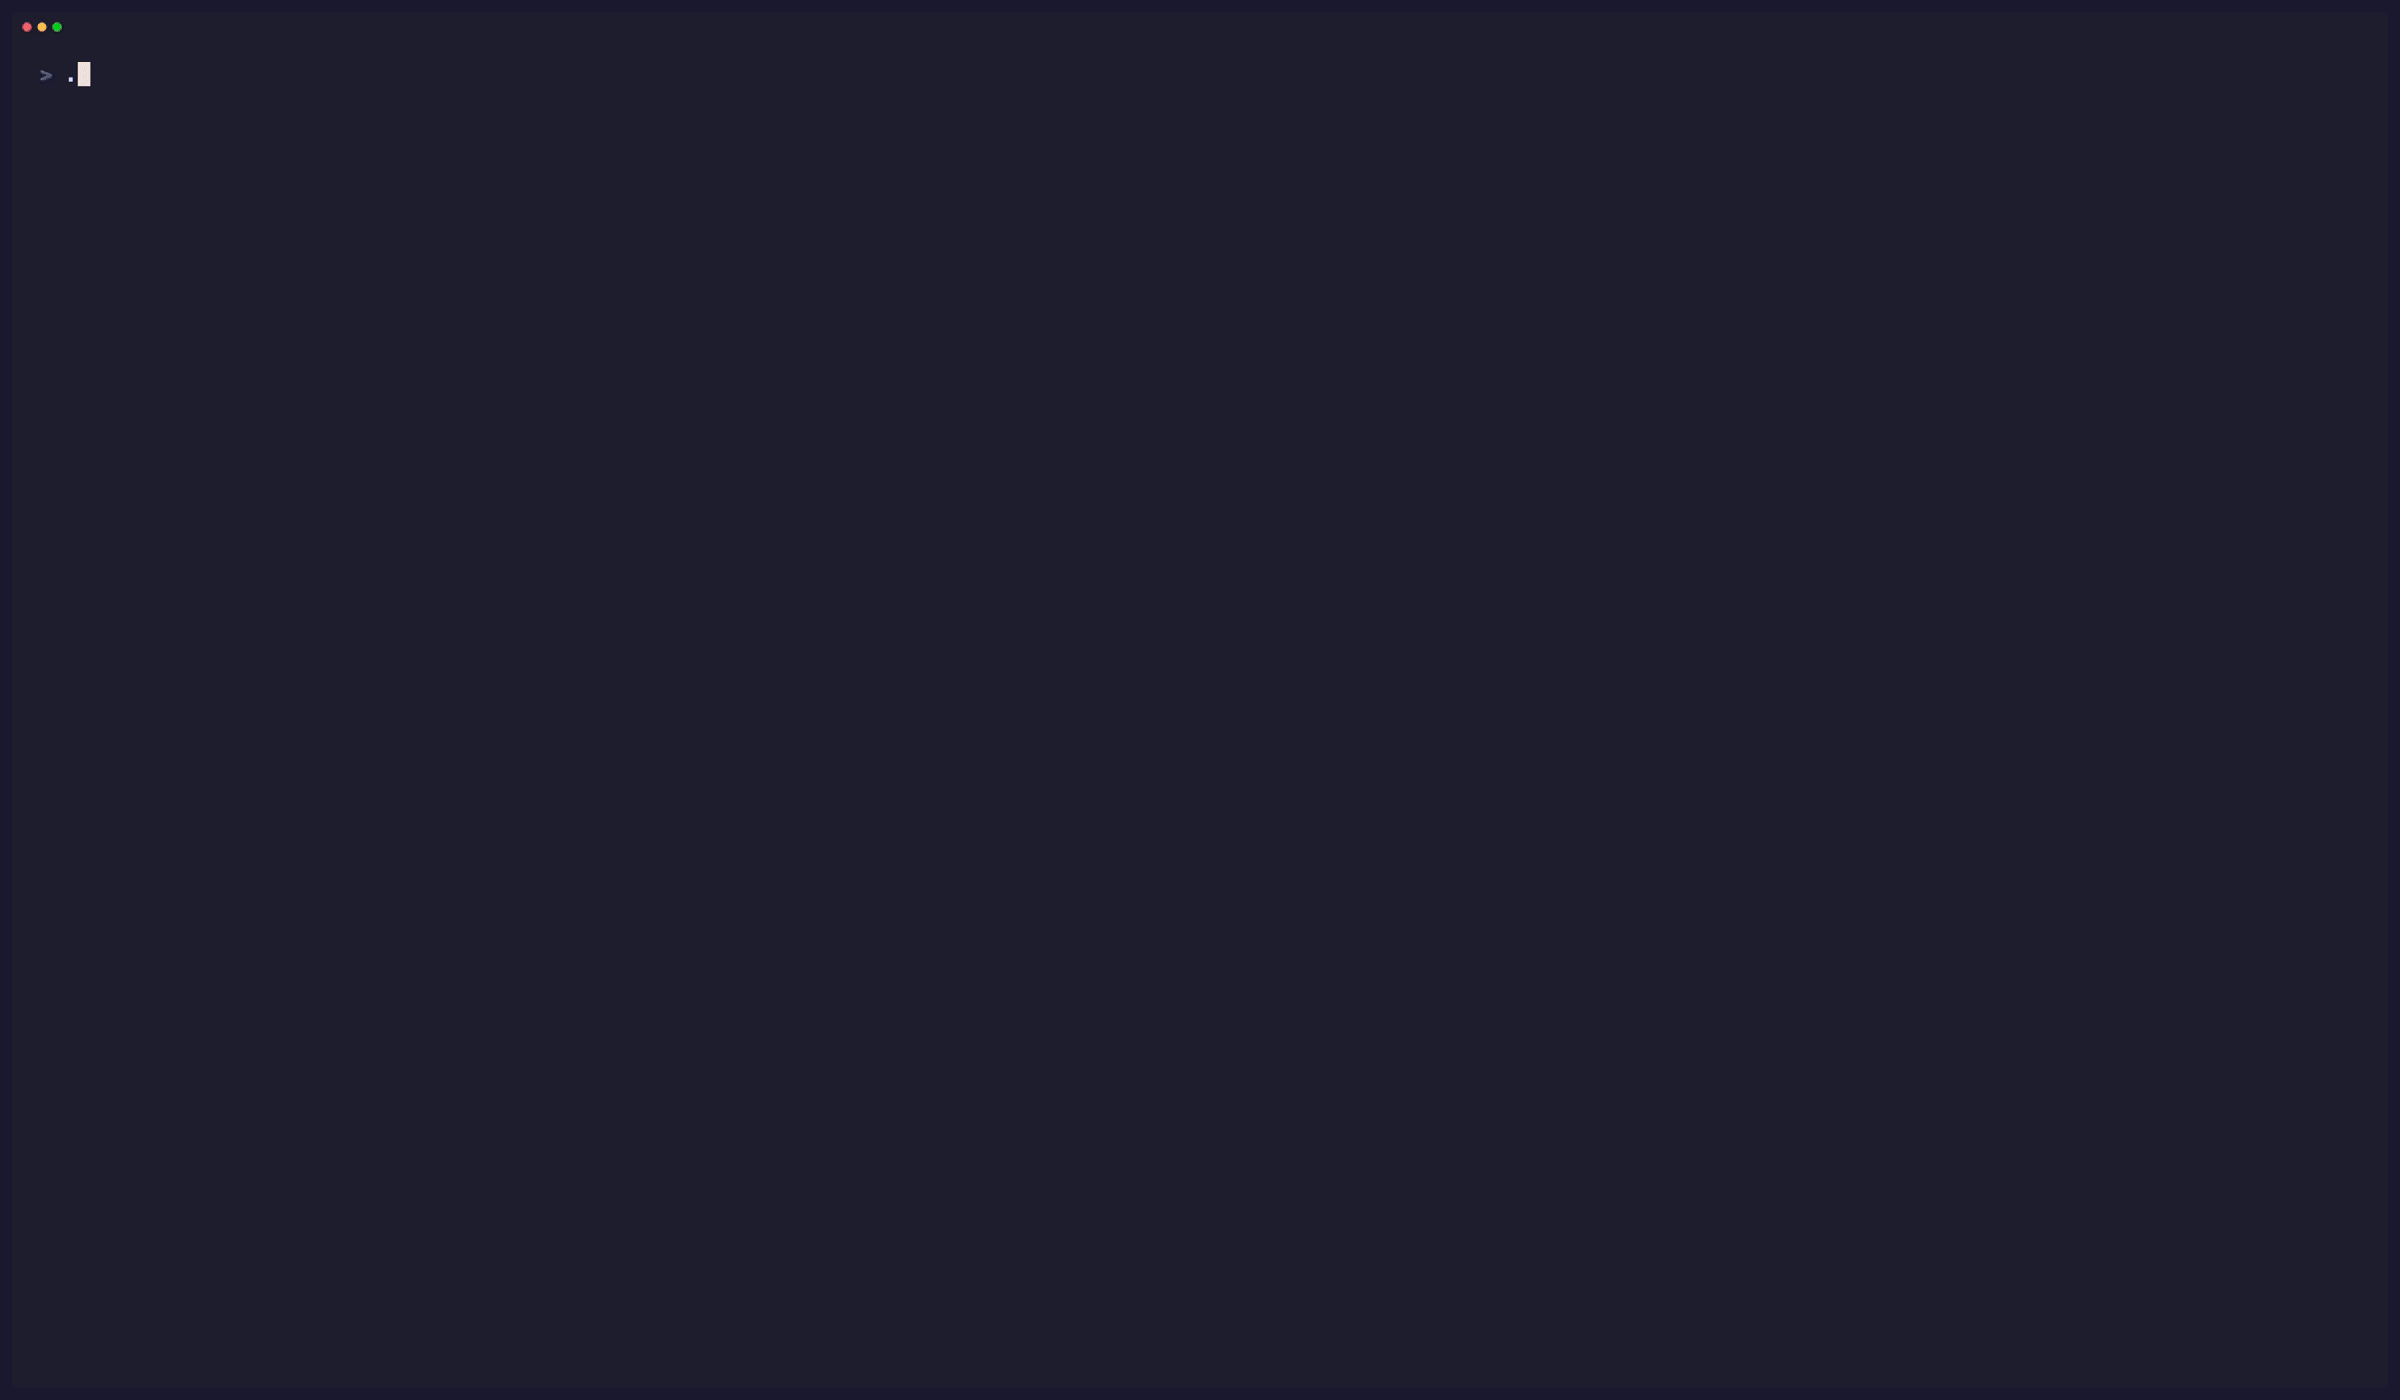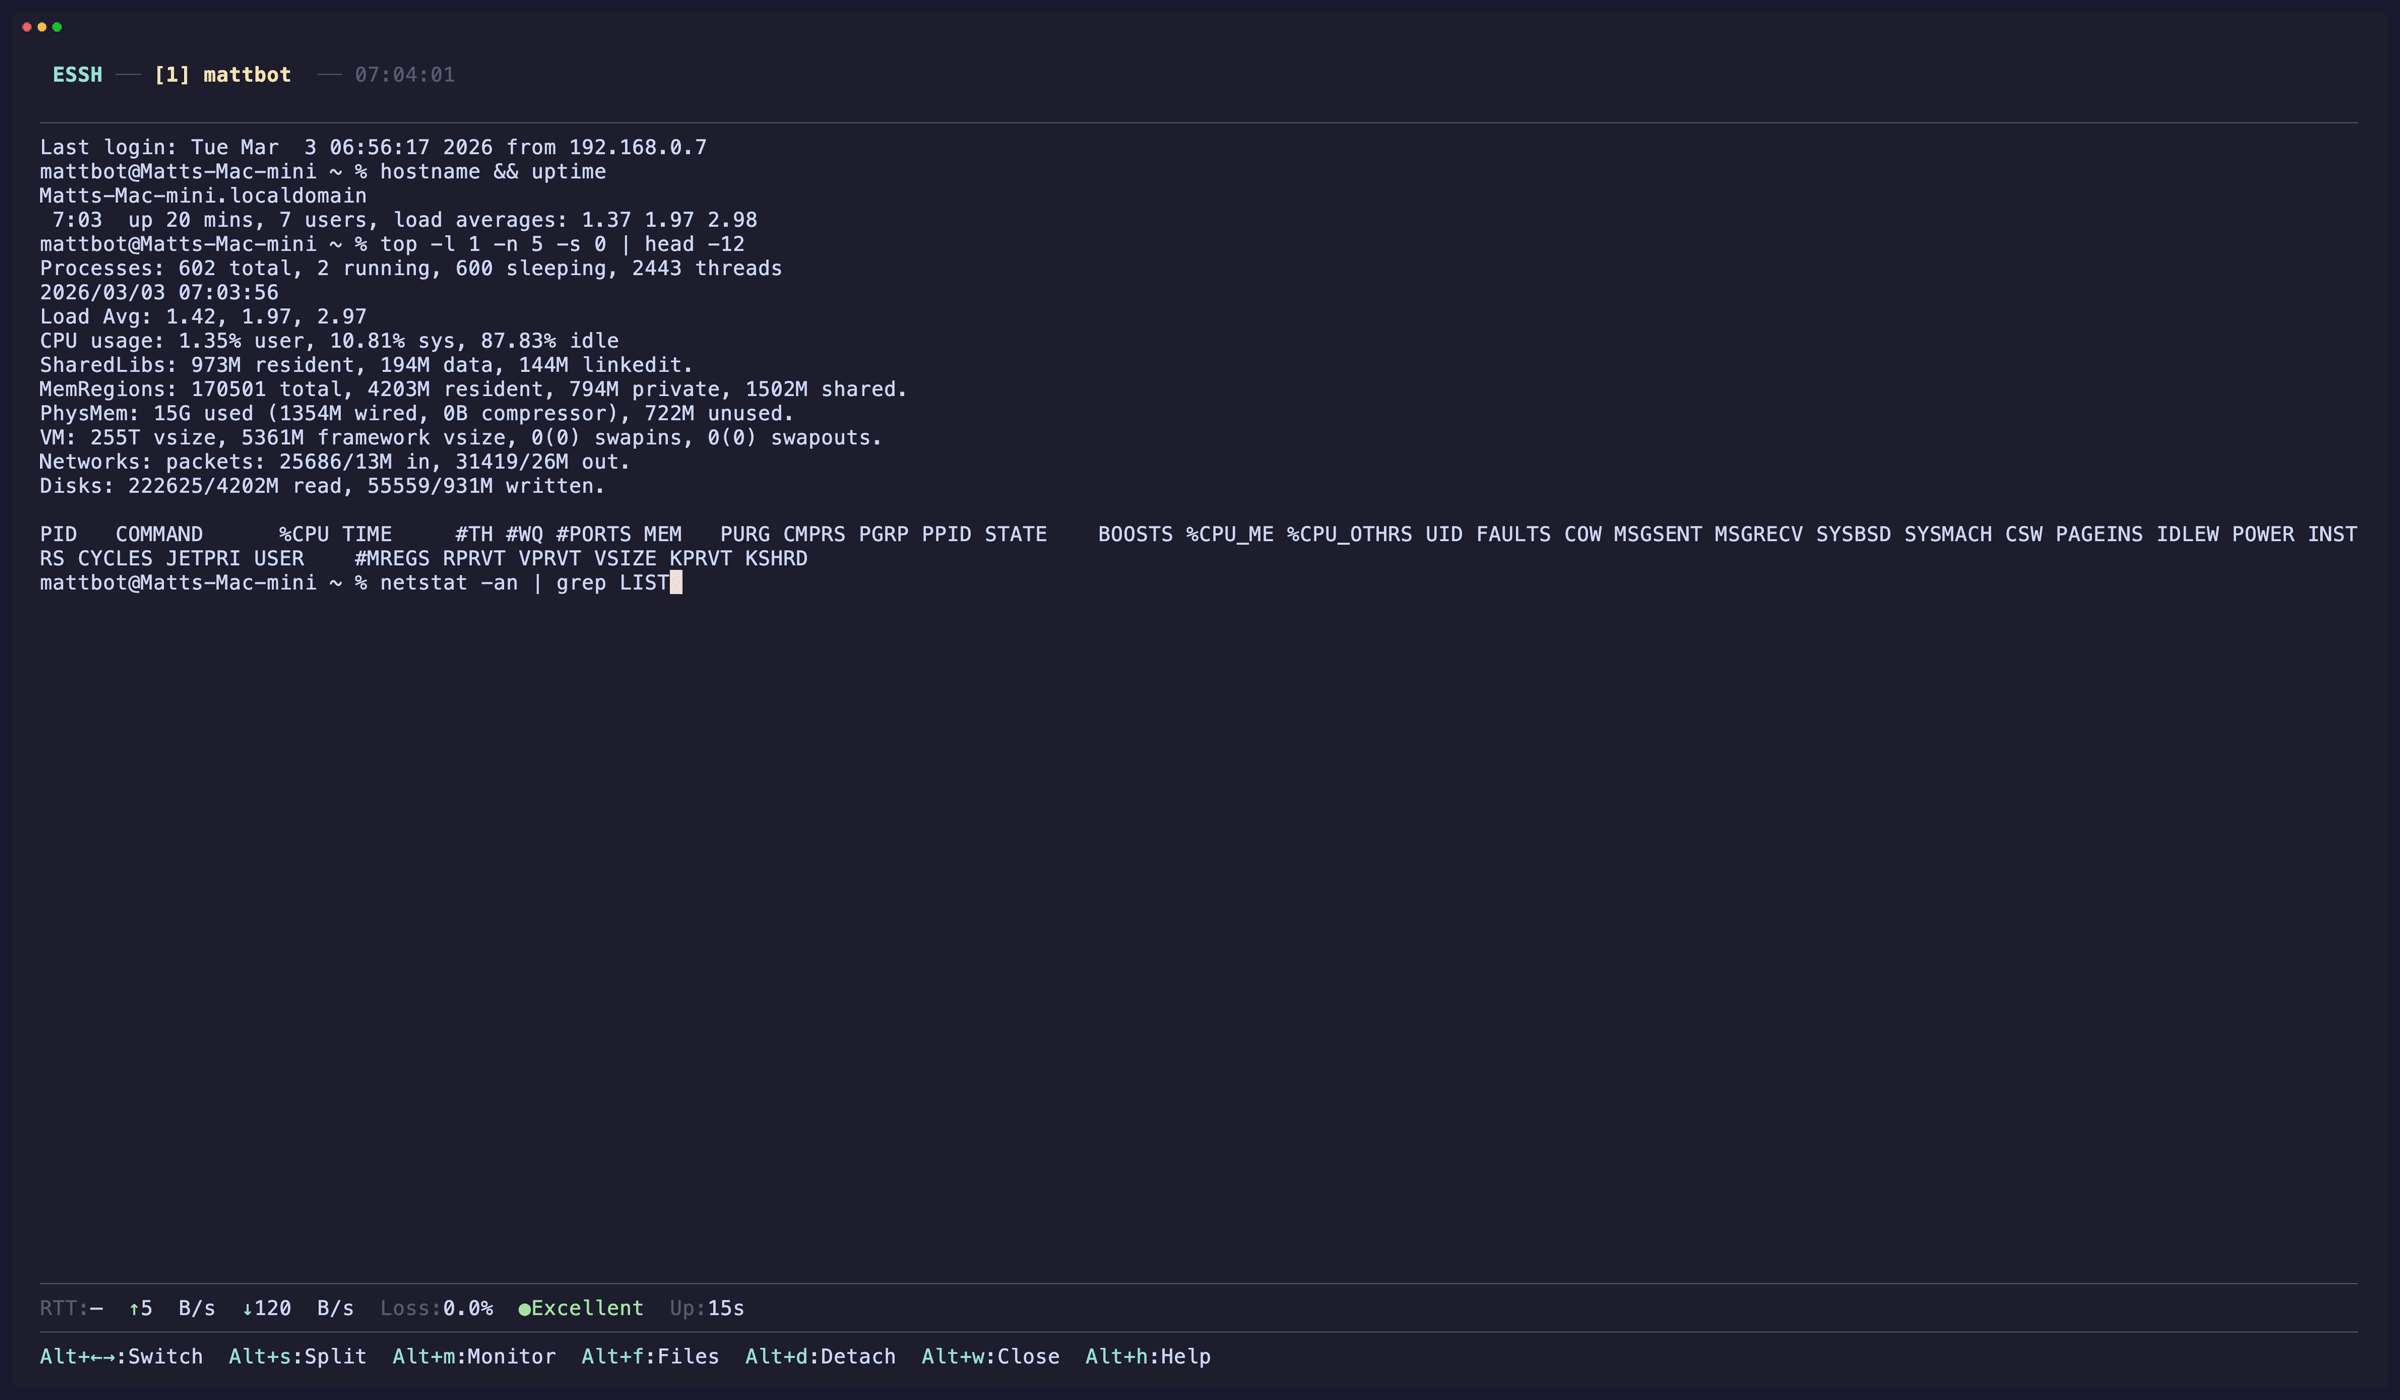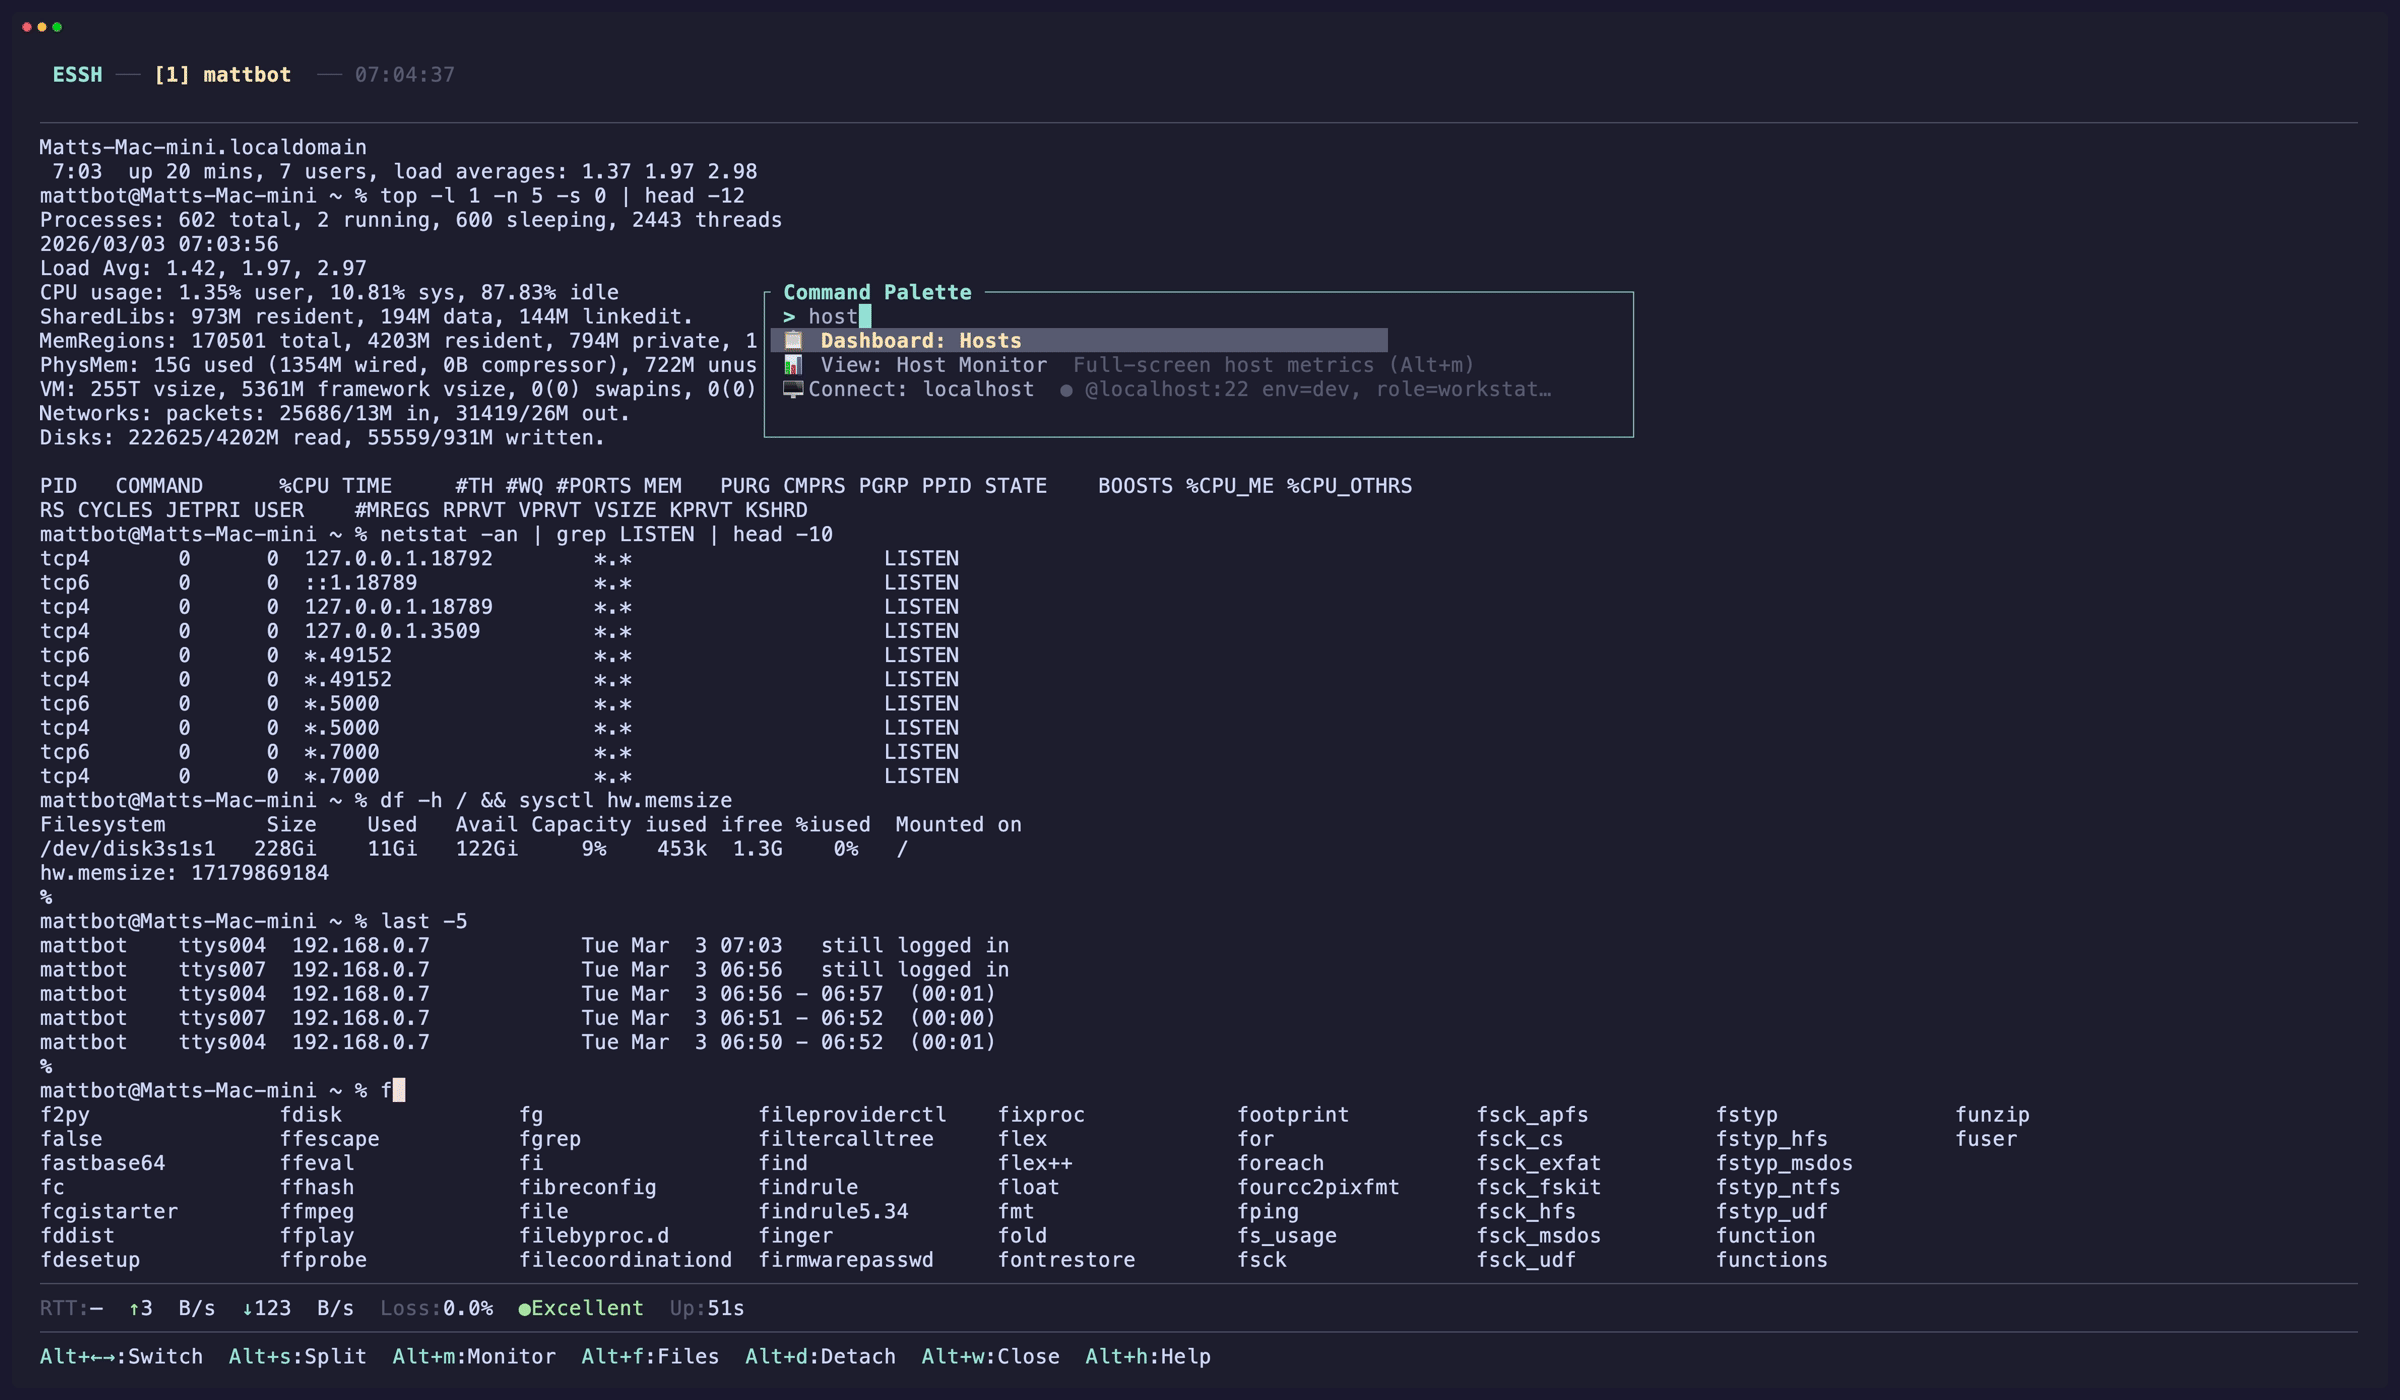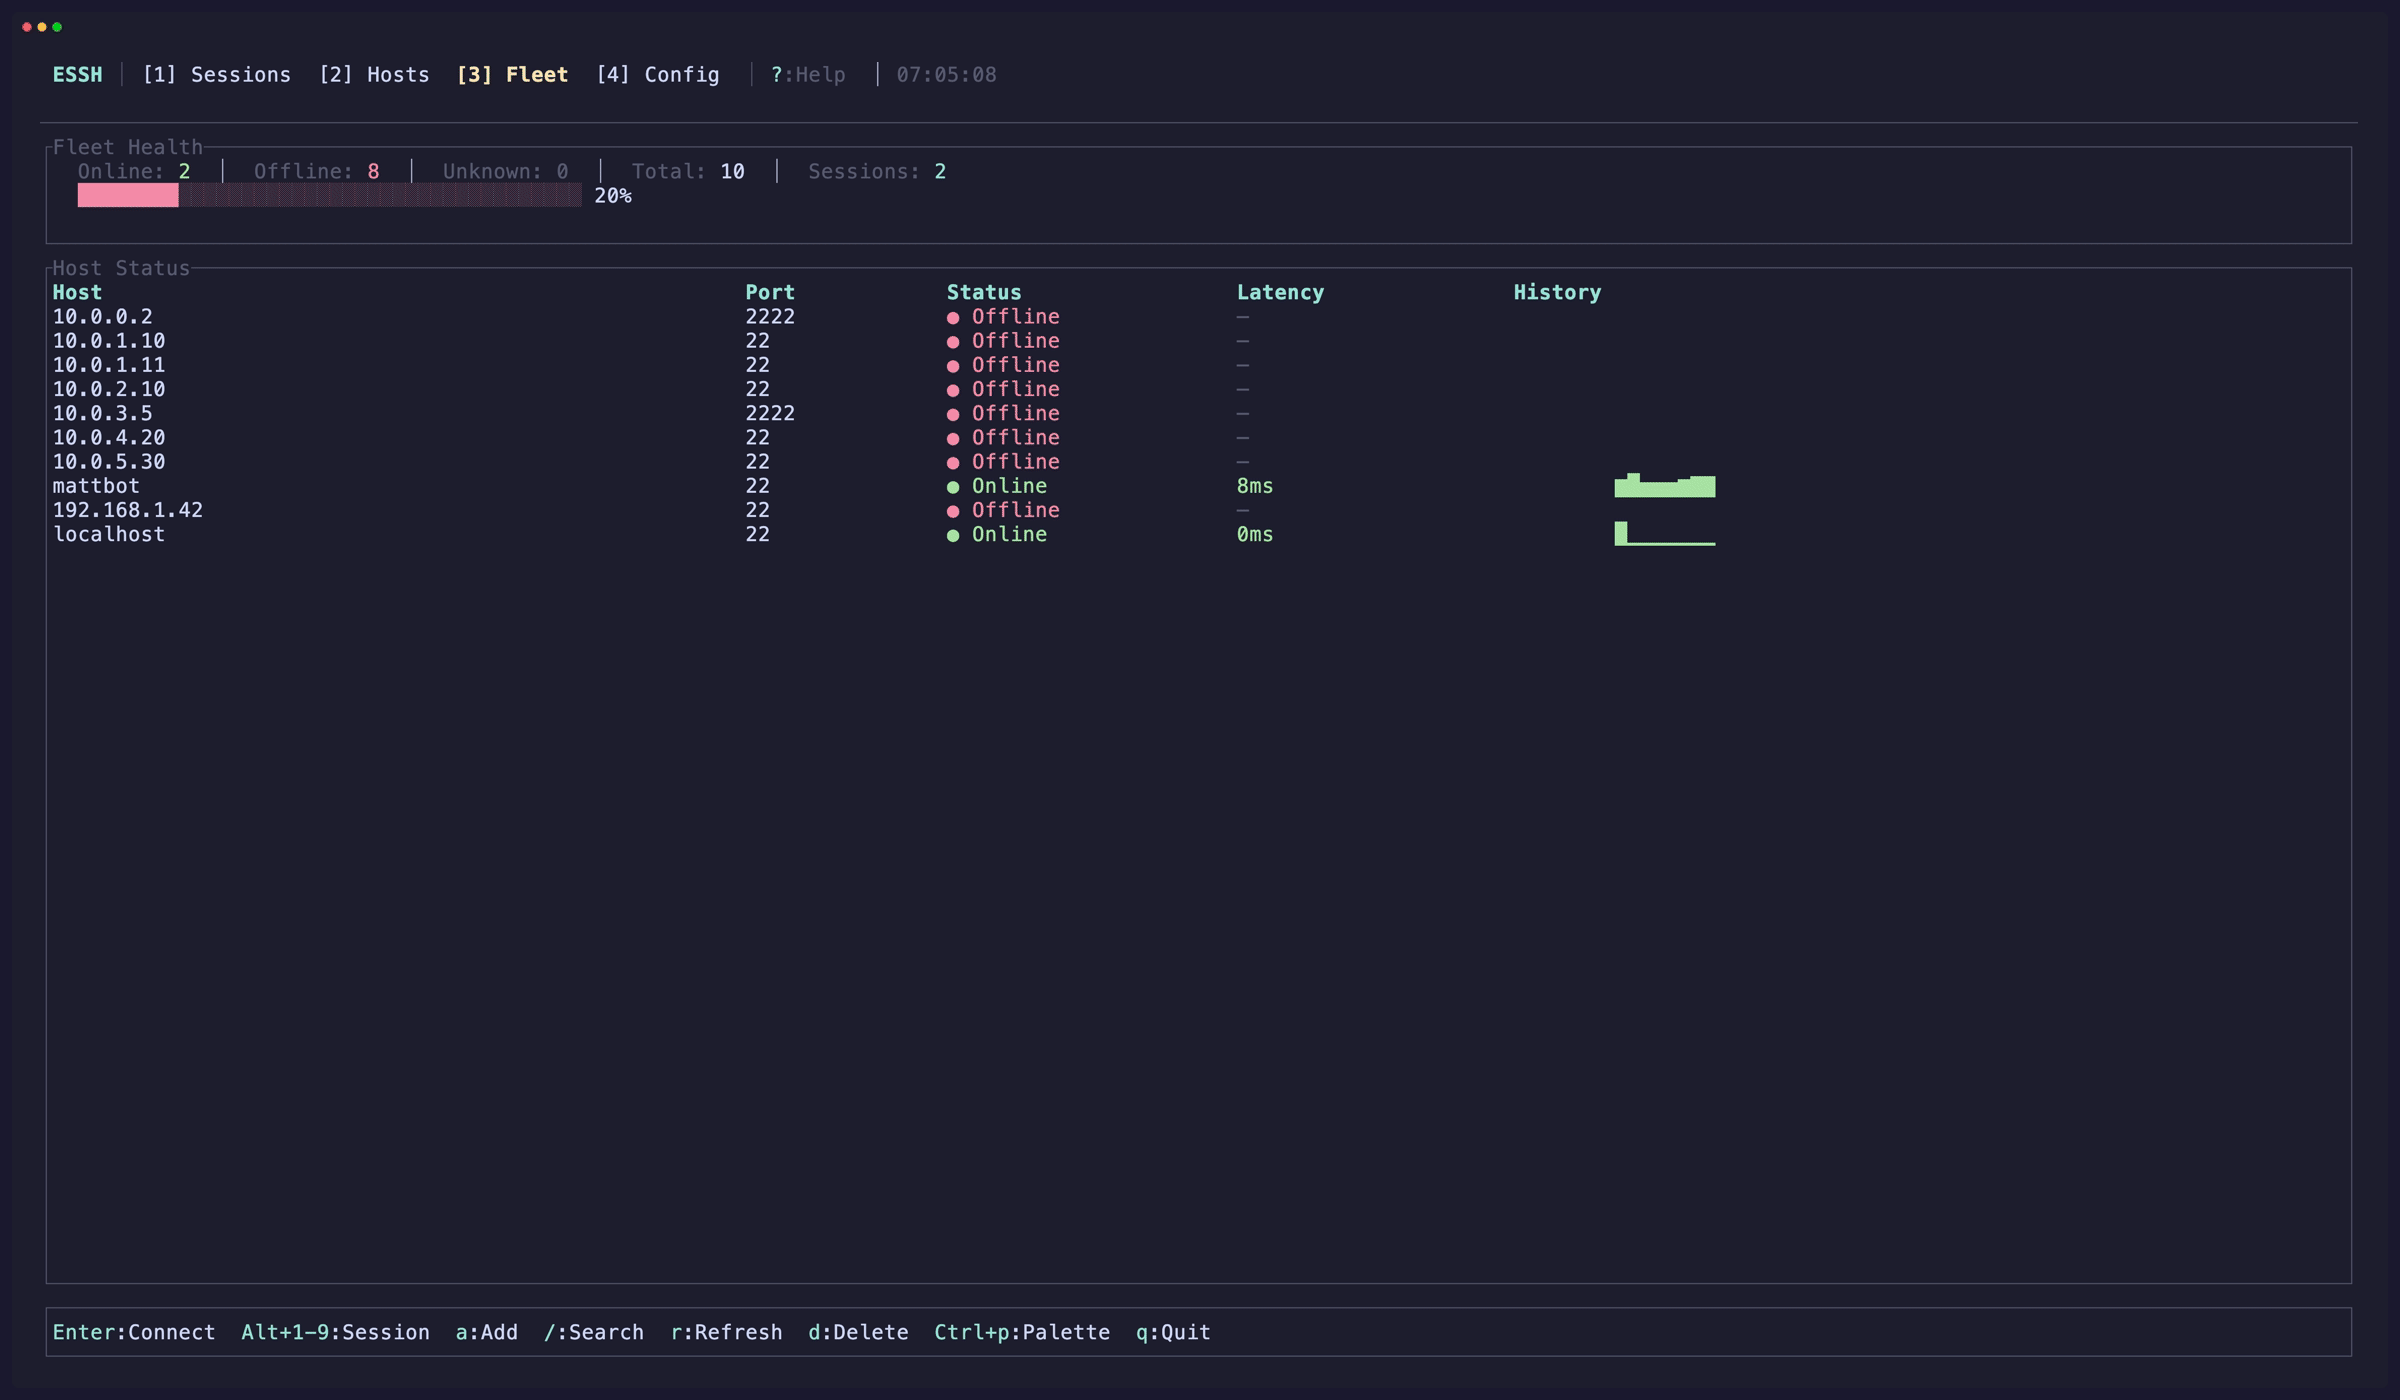 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
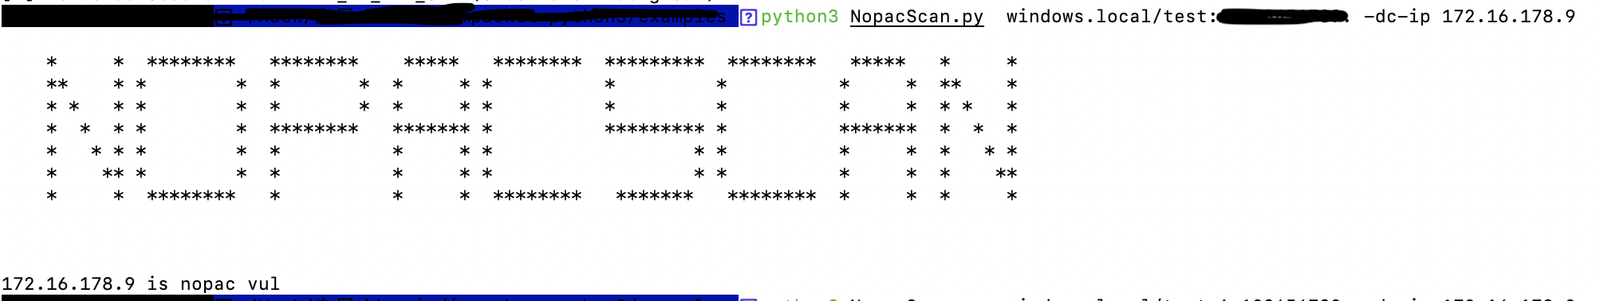 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
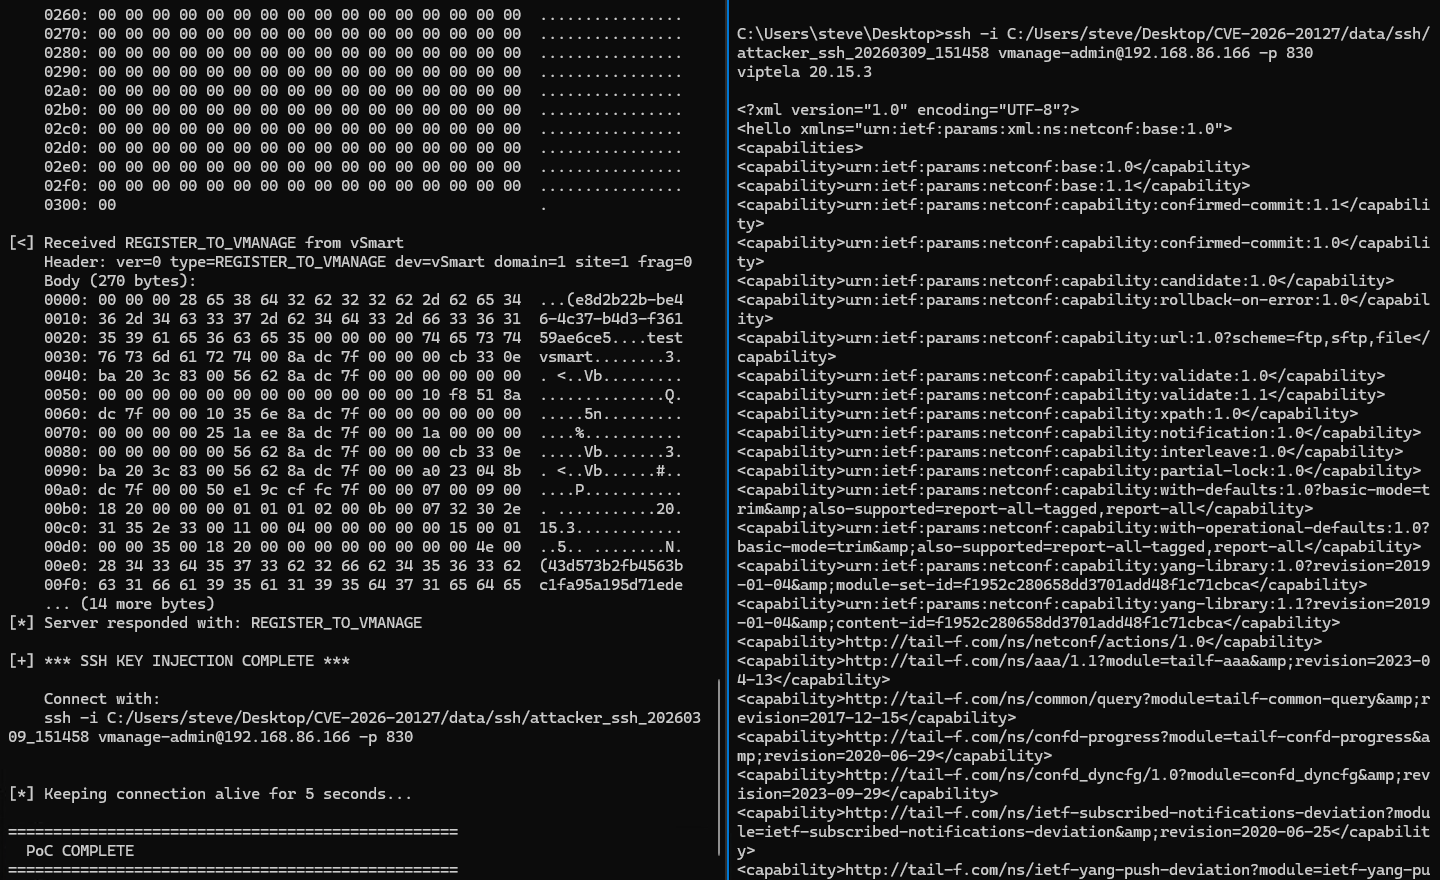 sfewer-r7/cve-2026-20127
Exploit for Cisco Catalyst SD-WAN Controller authentication bypass (CVE-2026-20127) that forges DTLS CHALLENGE_ACK_ACK messages to gain unauthorized…
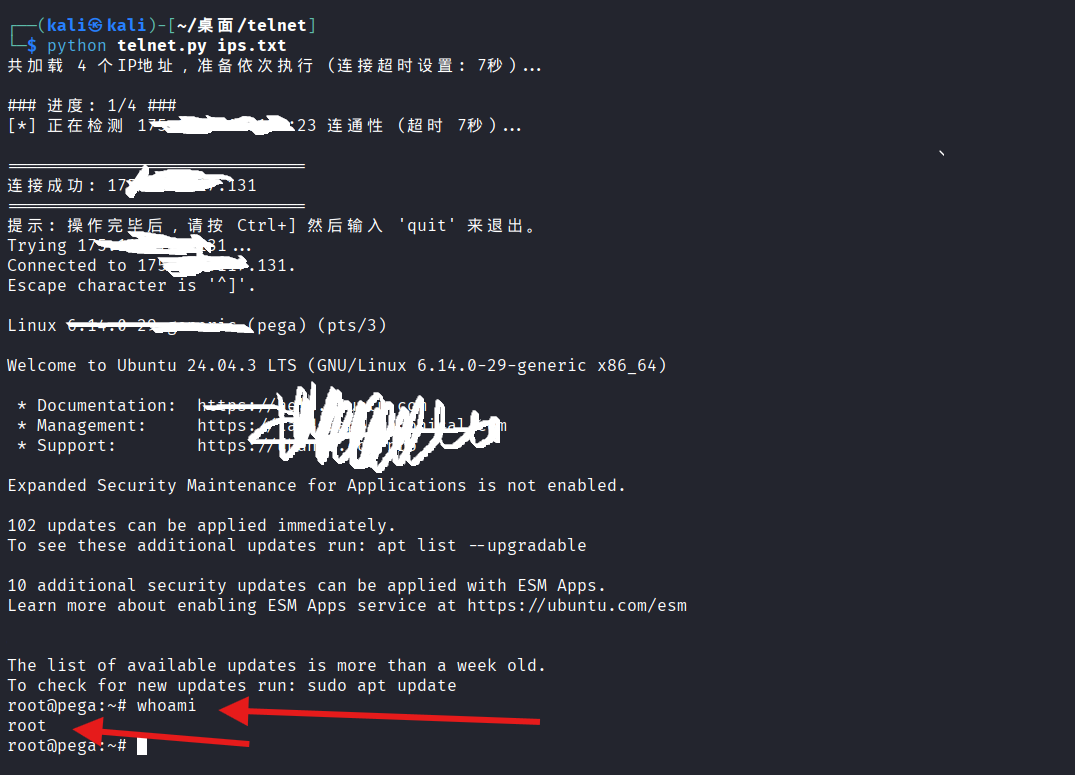 parameciumzhang/tell-me-root
Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration…
 watchtowrlabs/watchtowr-vs-check-point-cve-2026-50751
Detection artifact generator for Check Point VPN IKEv1 certificate-authentication bypass (CVE-2026-50751). Validates gateway exposure and…
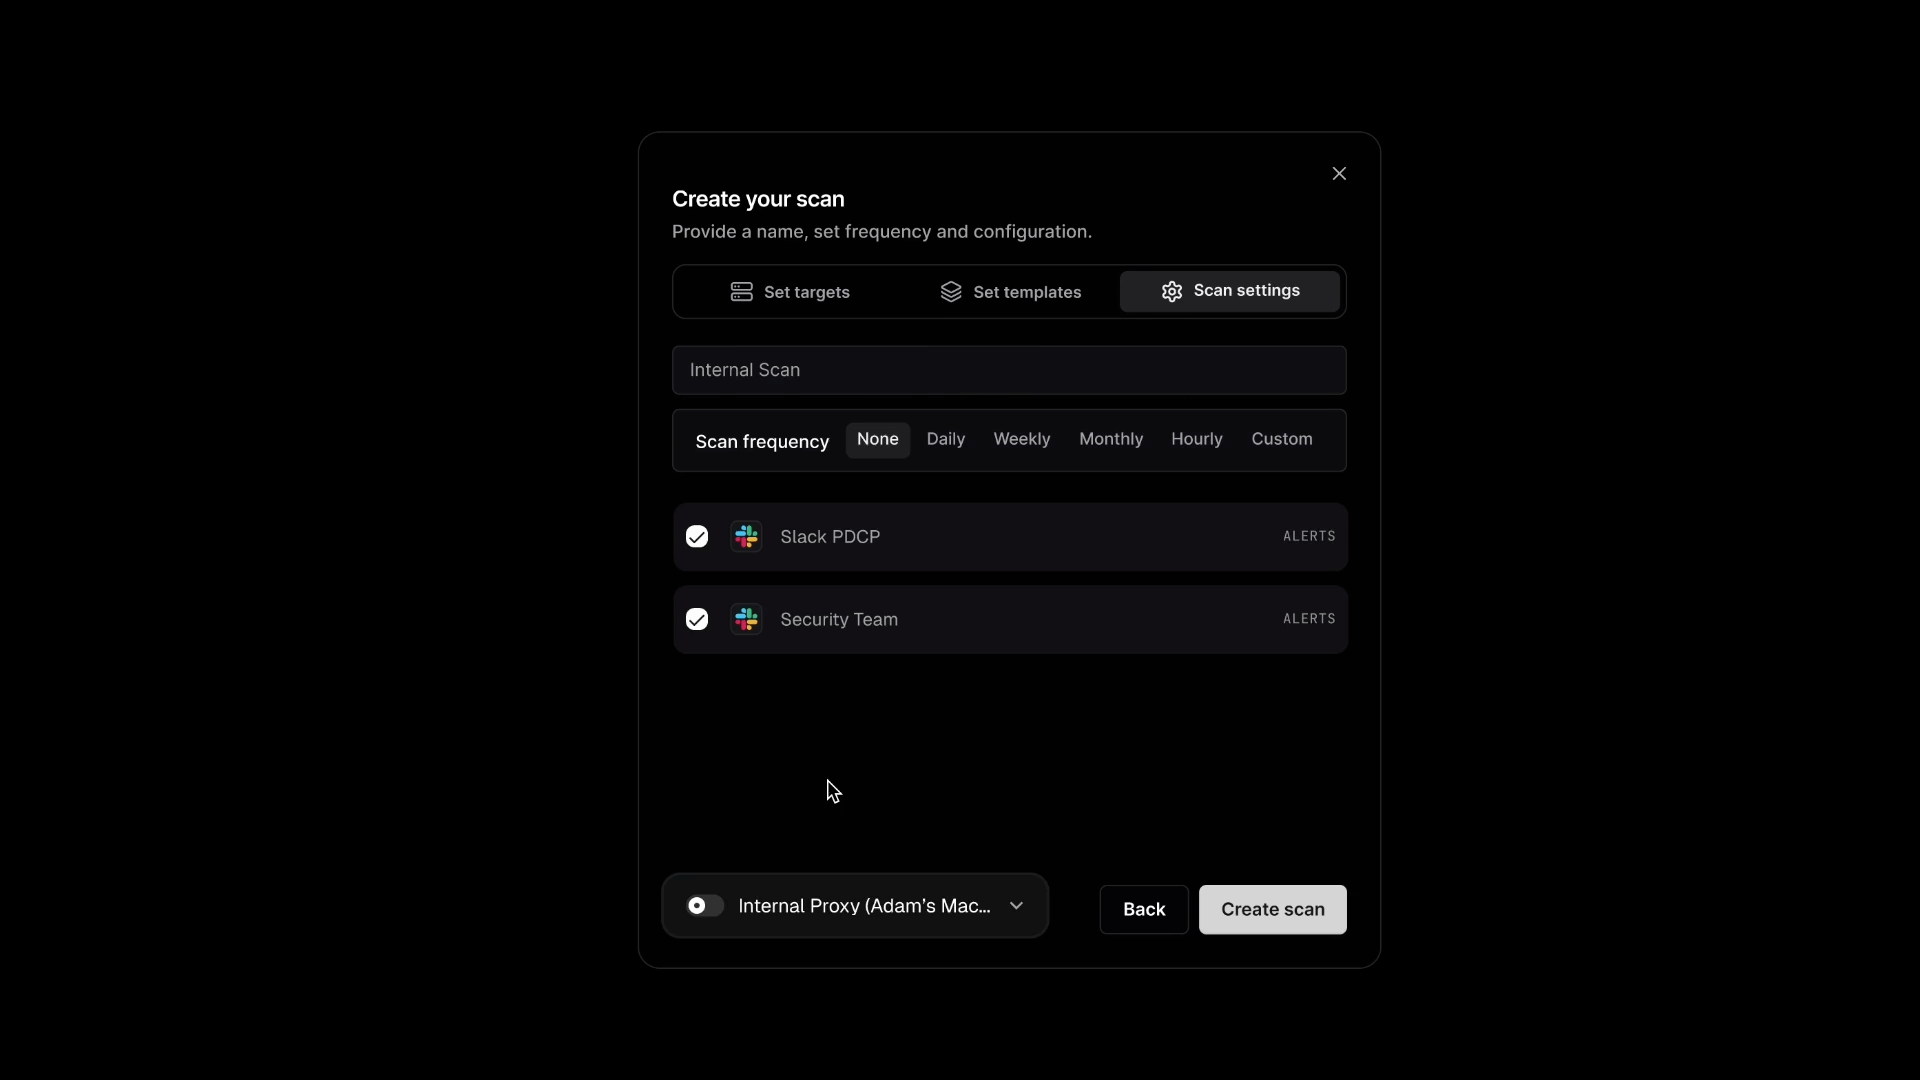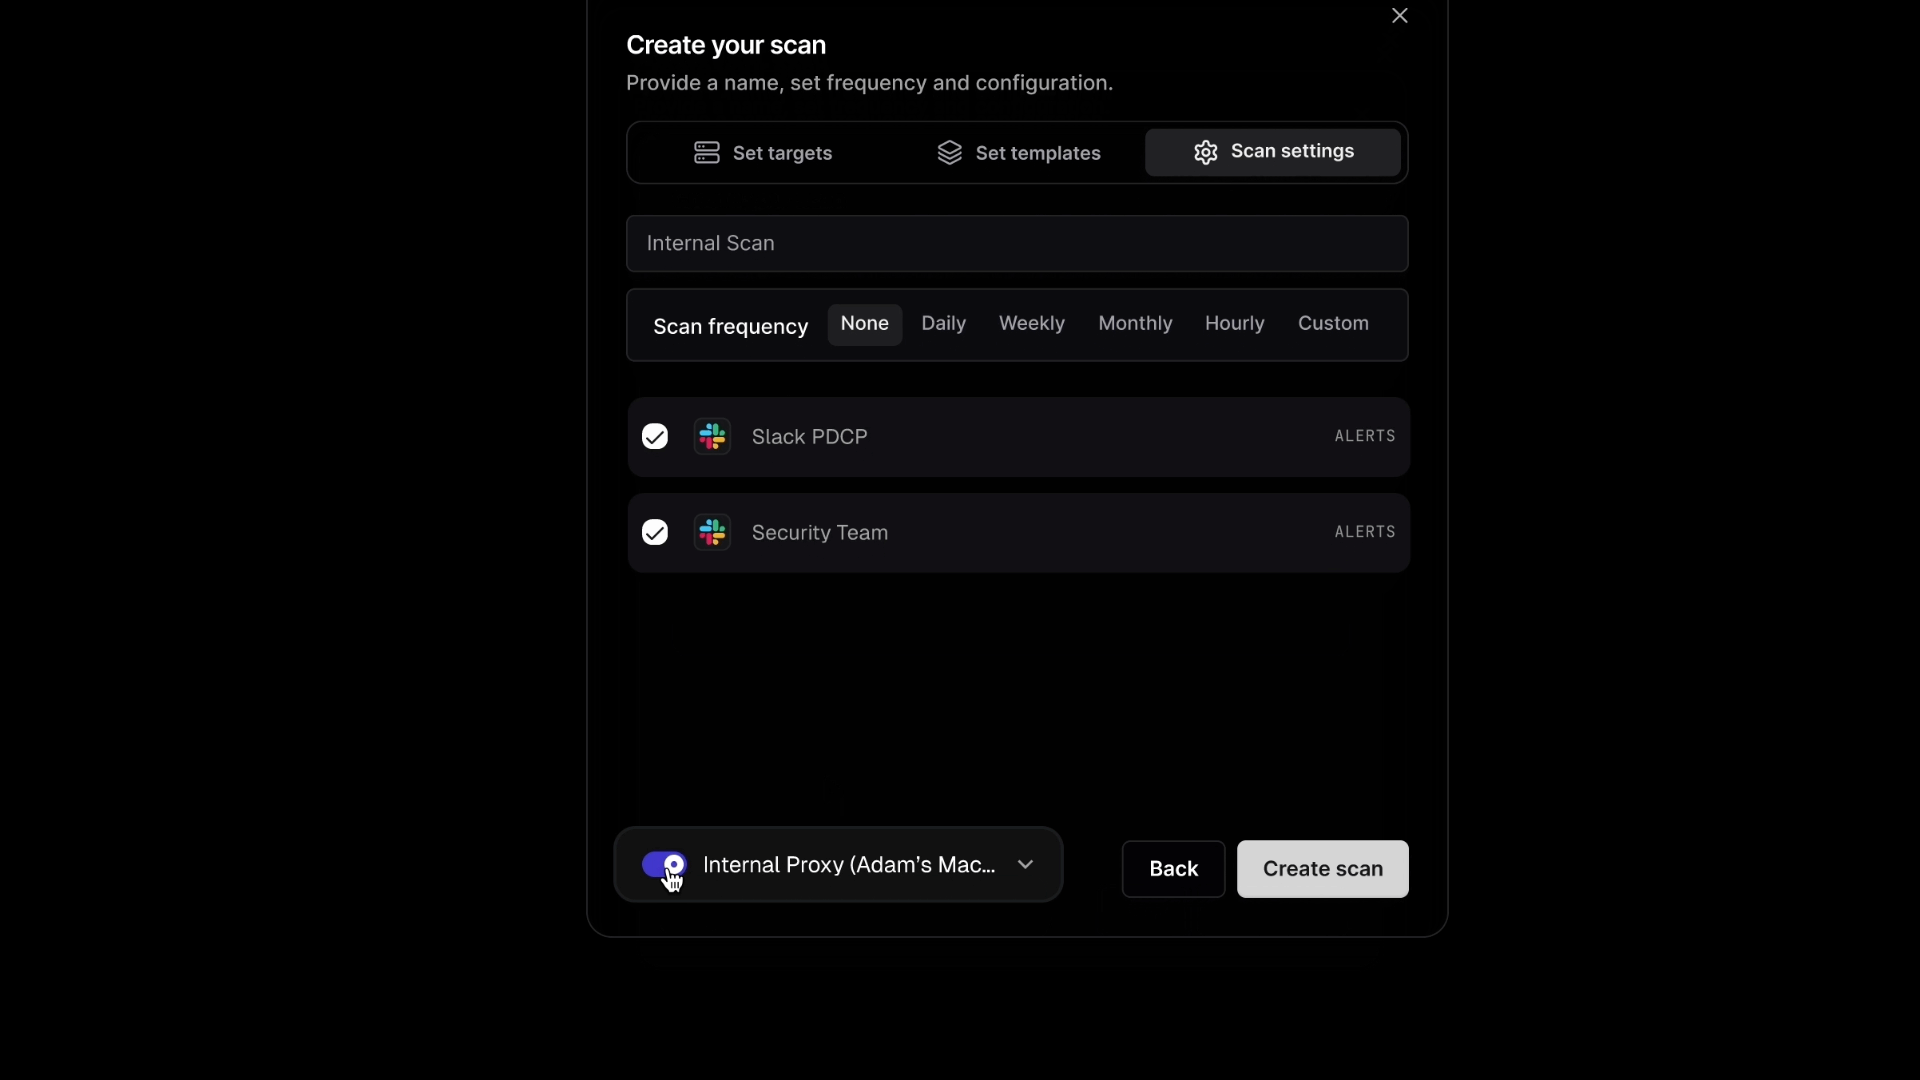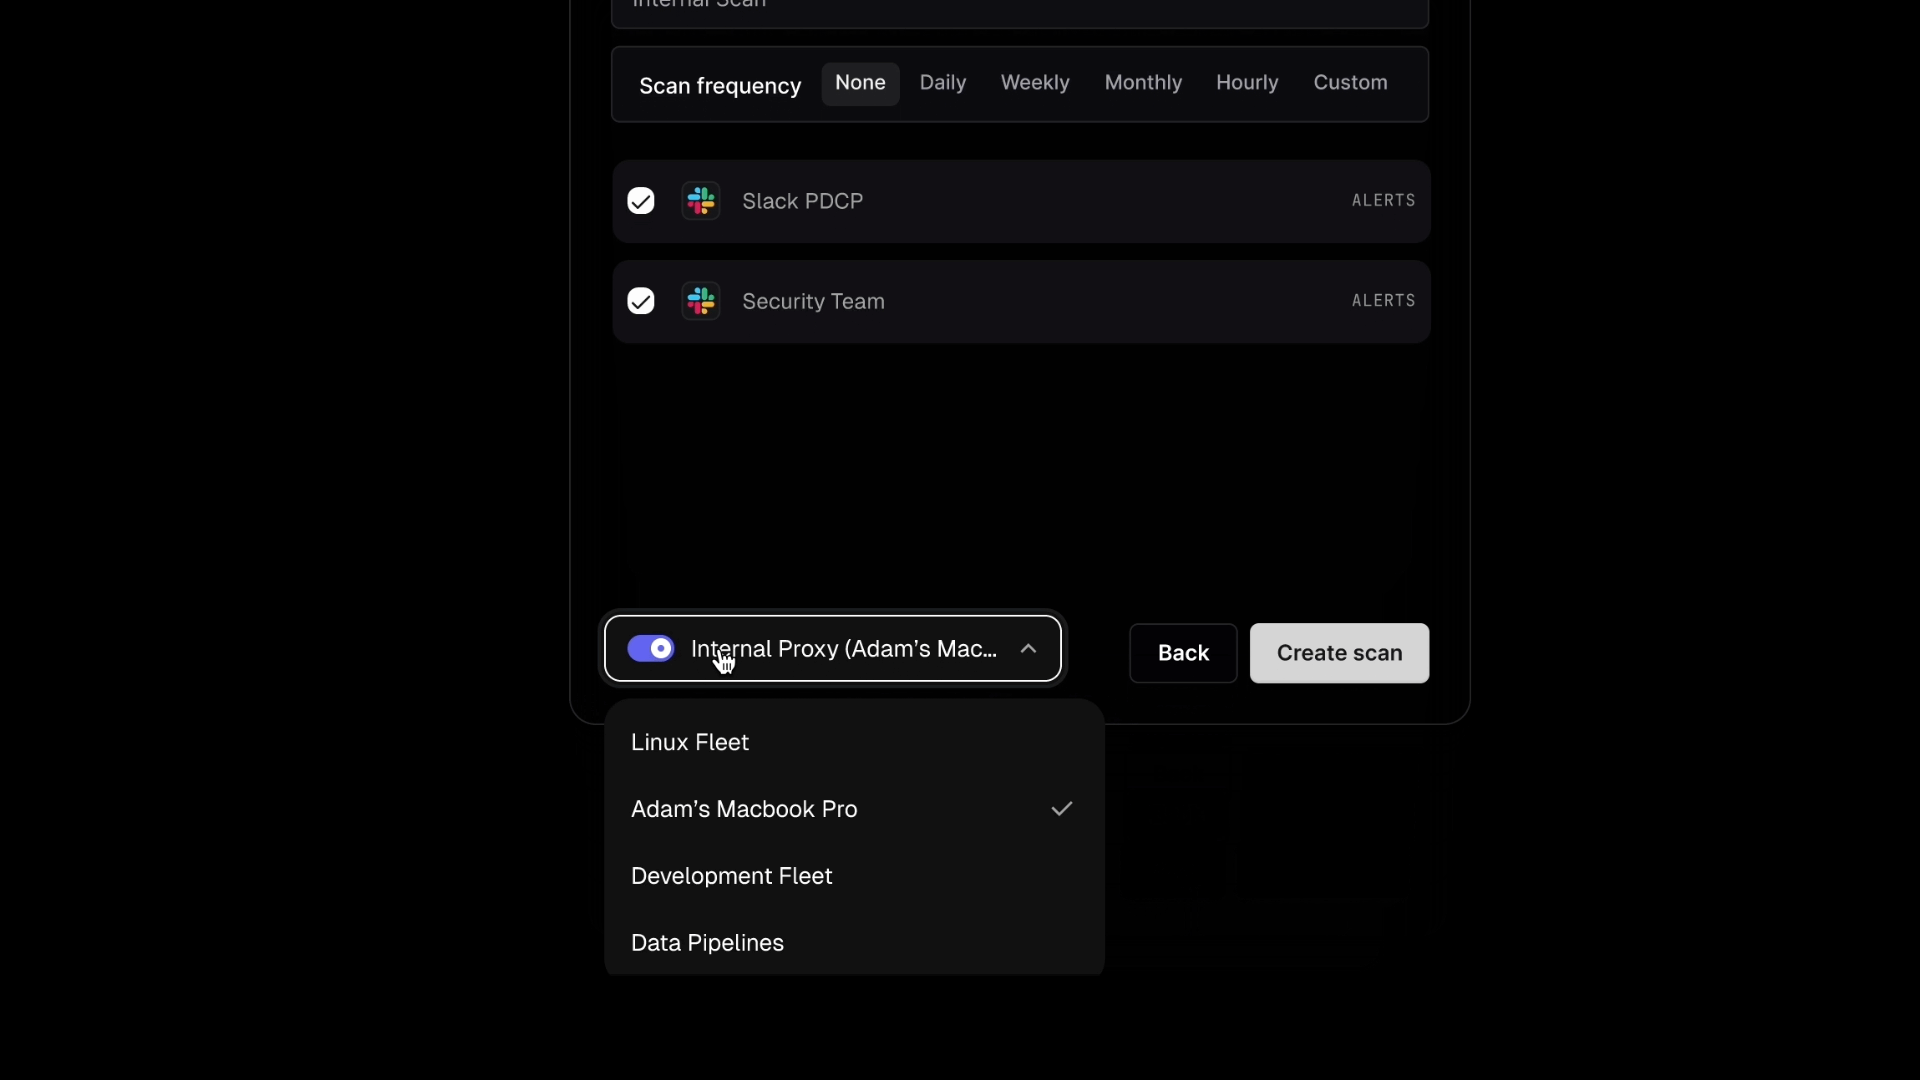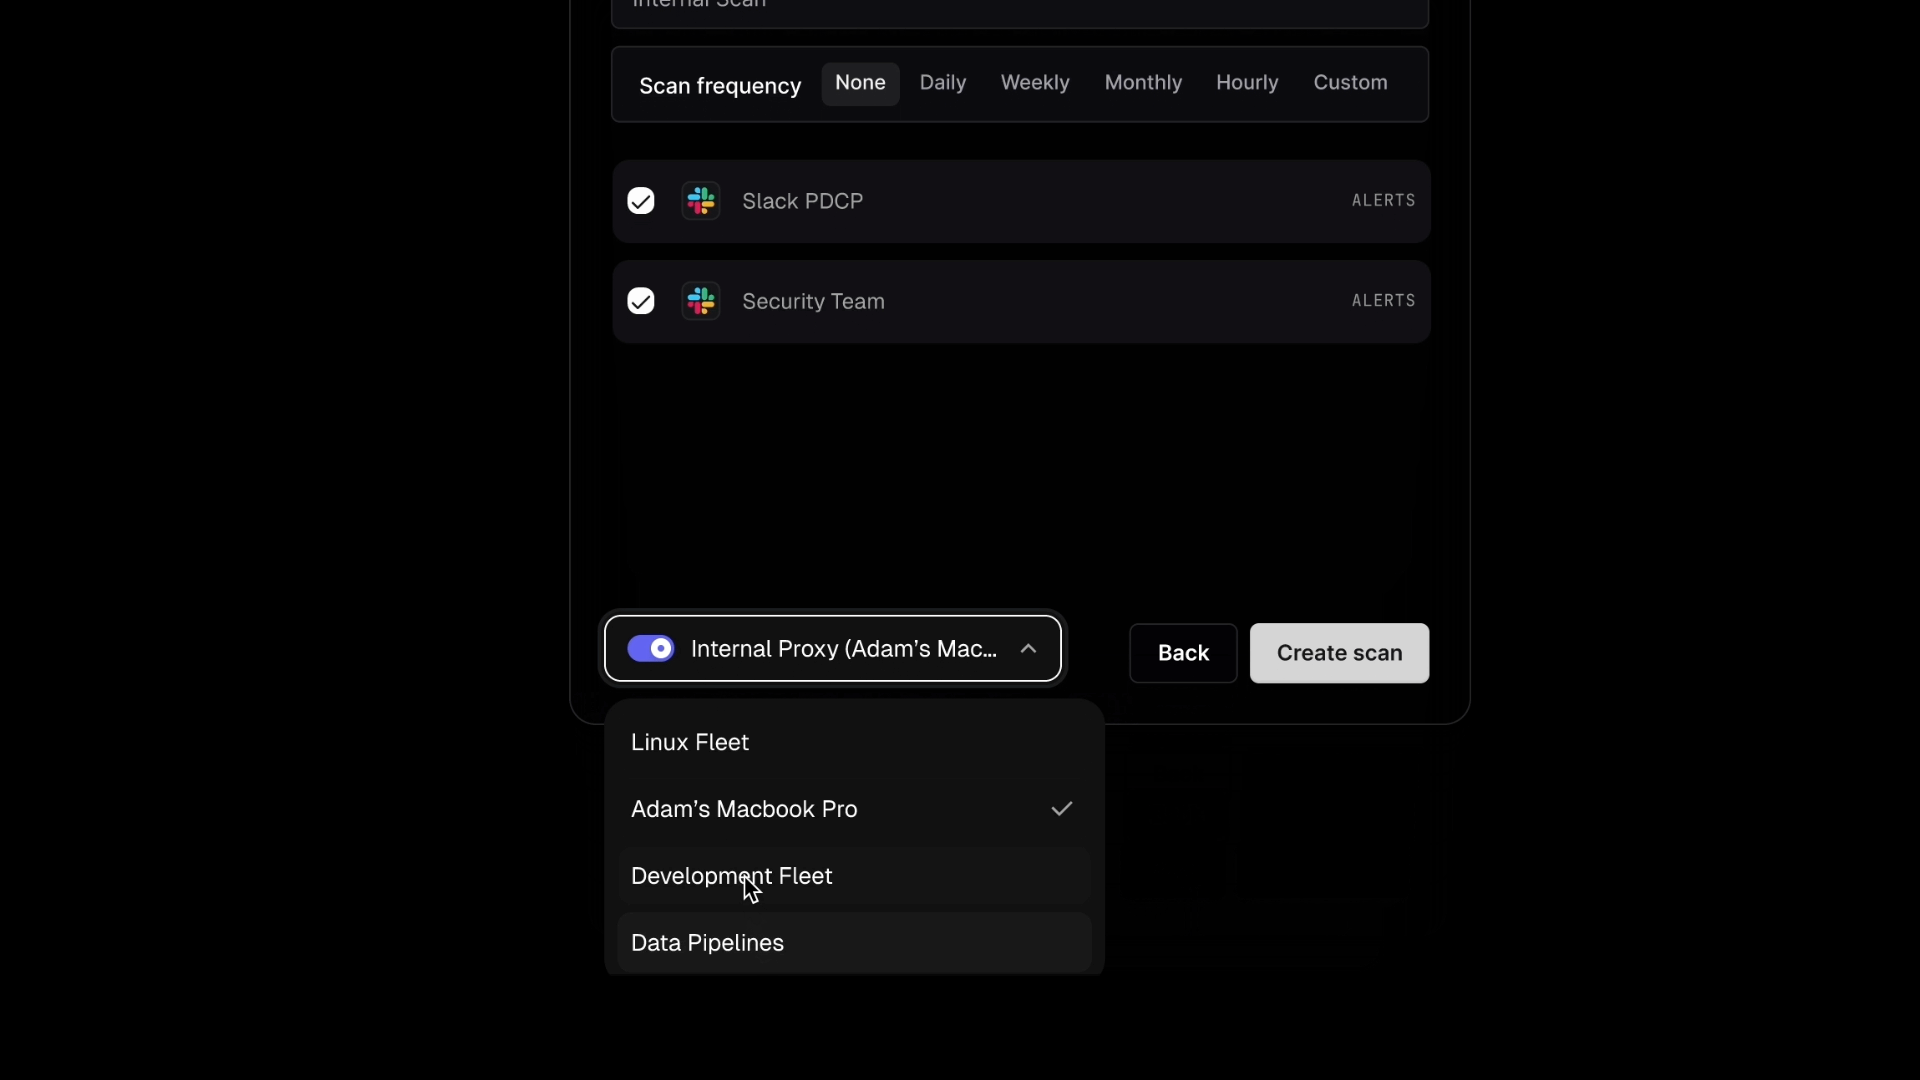 projectdiscovery/tunnelx
TunnelX is a lightweight ingress tunneling tool designed to create a secure SOCKS5 proxy server for routing network traffic.
 tushargurav28/cve-2026-0257
Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 george0papasotiriou/cve-2026-22002-vnc-authentication-bypass-via-protocol-version-confusion
Python PoC demonstrating CVE-2026-22002 VNC authentication bypass by forcing protocol version downgrade to RFB 3.3, including a simulated vulnerable…
 akash7350/cve-2020-1472
Python exploit that tests domain controllers for Zerologon (CVE-2020-1472) and resets the vulnerable machine account password through Netlogon…
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
 corelight/cve-2022-30216
Zeek package detecting CVE-2022-30216 NTLM relay attacks against Windows Server. Raises notices for exploit attempts and successful exploitation via…
 gpotter2/cve-2024-20674
Exploit for CVE-2024-20674: Kerberos mutual authentication bypass via logic bug in client-side U2U TGT-REP handling. Enables unauthenticated network…