
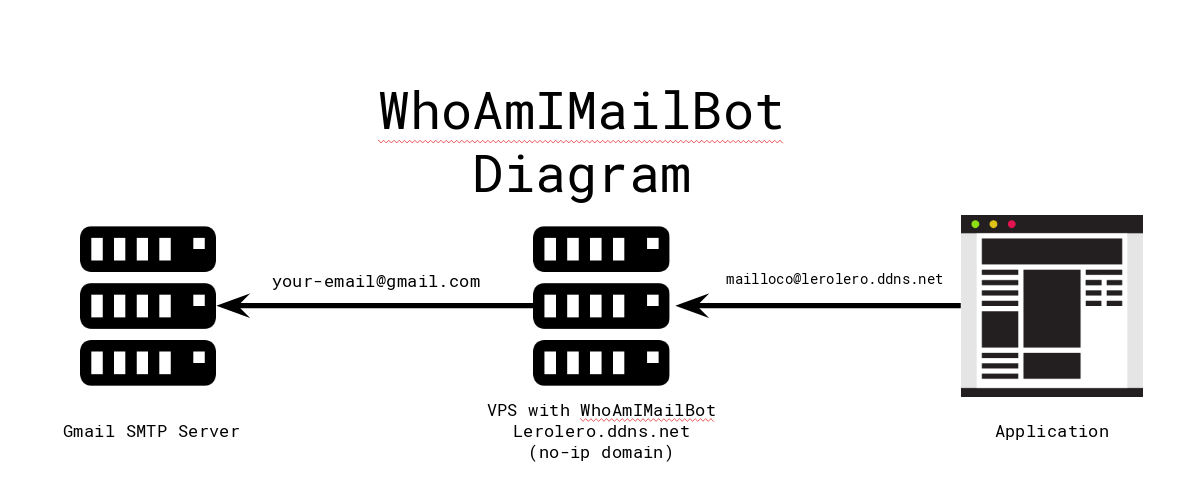
WhoAmIMailBot
 mthbernardes/whoamimailbot
Self-hosted email alias masking service using Postfix and Telegram bot to create disposable addresses for signups, with full control over email…
authenticationemail-securityprivacy+1
68
mthbernardes/whoamimailbotSelf-hosted email alias masking service using Postfix and Telegram bot to create disposable addresses for signups, with full control over email…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 openssl/openssl
General purpose TLS and crypto library
 carlosevieira/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 ccordeiro/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 yzee00/cve-2018-15473
Fix for CVE-2018-15473
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 ayewo/fortios-ldap-mitm-poc-cve-2019-5591
The default configuration of LDAP on FortiOS v6.0.x to v6.2.0 does not check server identity for LDAP/S leading to MITM attacks. This PoC demos full…
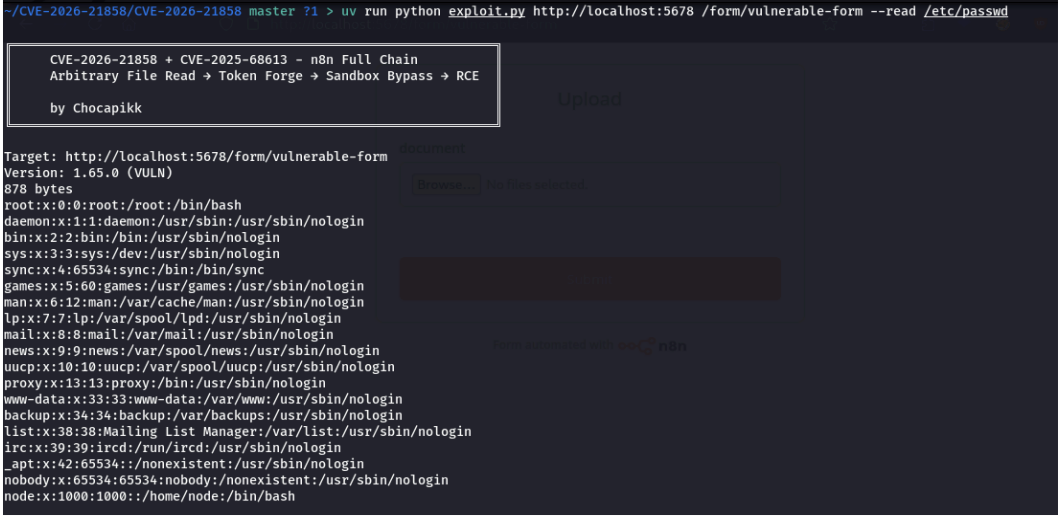 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 wtn-arny/cve-2024-37085
Python exploit for CVE-2024-37085, an authentication bypass in domain-joined ESXi hypervisors, enabling unauthenticated shell upload and full…
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 cravaterouge/bloodyad
LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…