

gitlab-exploit
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
authenticationexploitationpassword-attacks+3
1
hackeremmen/gitlab-exploitExploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
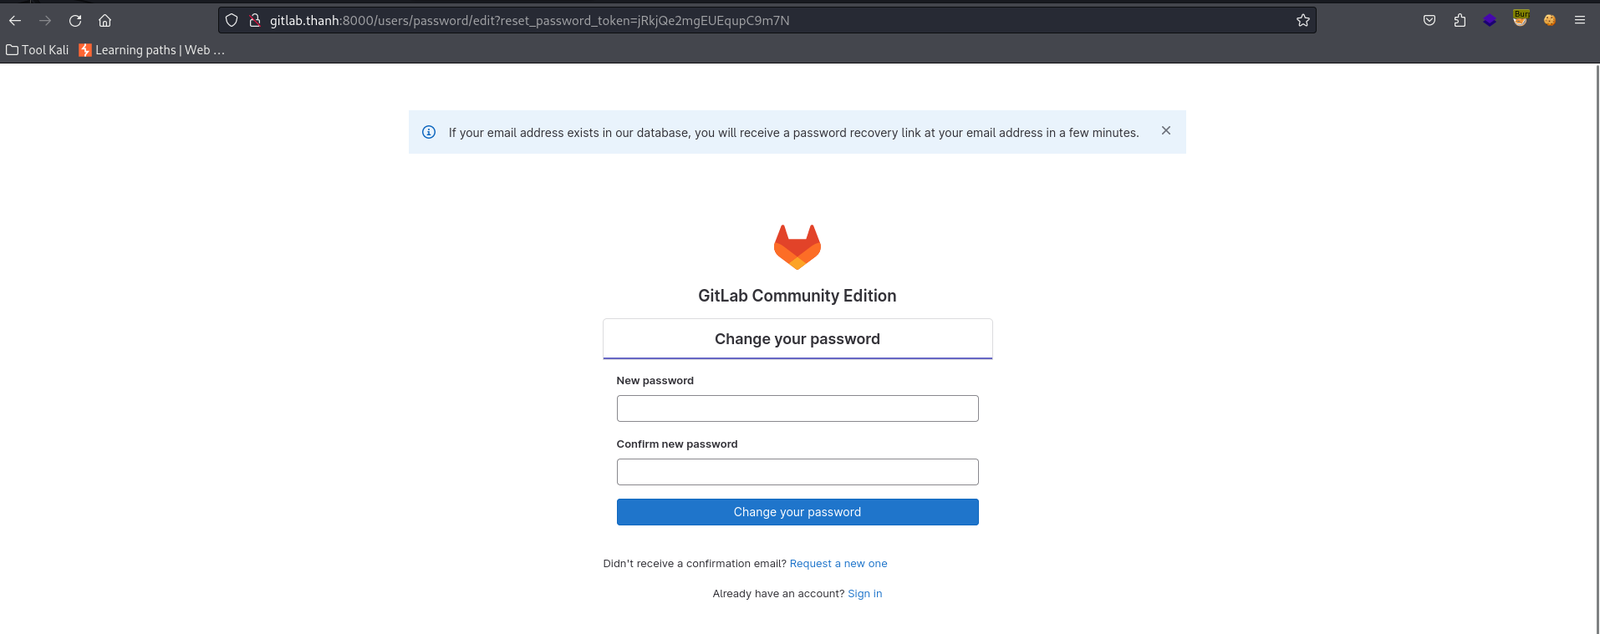 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 h4k6/cve-2023-2982-poc
WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证