
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
CVE-2024-0012 preview

CVE-2024-0012

GitHub0xjessie21/cve-2024-0012

CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC
authenticationcommand-and-controlexploitation+3
3
1 year ago
CVE-2024-3183-POC preview

CVE-2024-3183-POC

GitHubim10n/cve-2024-3183-poc

POC for CVE-2024-3183 (FreeIPA Rosting)
authenticationexploitationpassword-attacks+2
292 years ago
cve-2024-56348 preview

cve-2024-56348

GitHubjoshuavanderpoll/cve-2024-56348

Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
authenticationexploitationpenetration-testing+4
37 months ago
CVE-2024-31964 preview

CVE-2024-31964

GitHubd-raco/cve-2024-31964

Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
authenticationexploitationhardware-security+4
21 year ago
CVE-2024-11680_PoC_Exploit preview

CVE-2024-11680_PoC_Exploit

GitHubd3n14ld15k/cve-2024-11680_poc_exploit

This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
authenticationexploitationmisconfiguration+3
121 year ago
CrushFTP-CVE-2024-4040-illdeed preview

CrushFTP-CVE-2024-4040-illdeed

GitHubill-deed/crushftp-cve-2024-4040-illdeed

Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
authenticationexploitationpayload-generation+3
1 year ago
CVE-2024-55591-POC preview

CVE-2024-55591-POC

GitHubumchacker/cve-2024-55591-poc

Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…
authenticationexploitationpenetration-testing+3
21 year ago
CVE-2024-55591 preview

CVE-2024-55591

GitHubvirus-or-not/cve-2024-55591

An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
authenticationeducationexploitation+3
81 year ago
GenCrushSSTIExploit preview

GenCrushSSTIExploit

GitHubgeniuszly/gencrushsstiexploit

is a PoC for CVE-2024-4040 tool for exploiting the SSTI vulnerability in CrushFTP
authenticationeducationexploitation+3
82 years ago
CVE-2024-29855 preview

CVE-2024-29855

GitHubsinsinology/cve-2024-29855

PoC for the Veeam Recovery Orchestrator Authentication CVE-2024-29855
authenticationexploitationpayload-generation+4
192 years ago
CVE-2024-31218-WEBHOOD-LAB preview

CVE-2024-31218-WEBHOOD-LAB

GitHubchandrimanath04-hue/cve-2024-31218-webhood-lab

Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
authenticationeducationexploitation+4
1 month ago
CVE-2024-10924-Bypass-MFA-Wordpress-LAB preview

CVE-2024-10924-Bypass-MFA-Wordpress-LAB

GitHubd1se0/cve-2024-10924-bypass-mfa-wordpress-lab

Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
authenticationctfeducation+5
41 year ago
CVE-2024-4358 preview

CVE-2024-4358

GitHubsinsinology/cve-2024-4358

Progress Telerik Report Server pre-authenticated RCE chain (CVE-2024-4358/CVE-2024-1800)
authenticationexploitationpayload-development+3
782 years ago
CVE-2024-28987 preview

CVE-2024-28987

GitHubhorizon3ai/cve-2024-28987

Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…
authenticationexploitationinformation-gathering+3
82 years ago
CVE-2024-8698-POC preview

CVE-2024-8698-POC

GitHubhuydoppaz/cve-2024-8698-poc

Proof-of-concept exploit for CVE-2024-8698 targeting Keycloak SAML authentication bypass. Demonstrates vulnerability exploitation in identity…
authenticationexploitationpenetration-testing+2
62 years ago
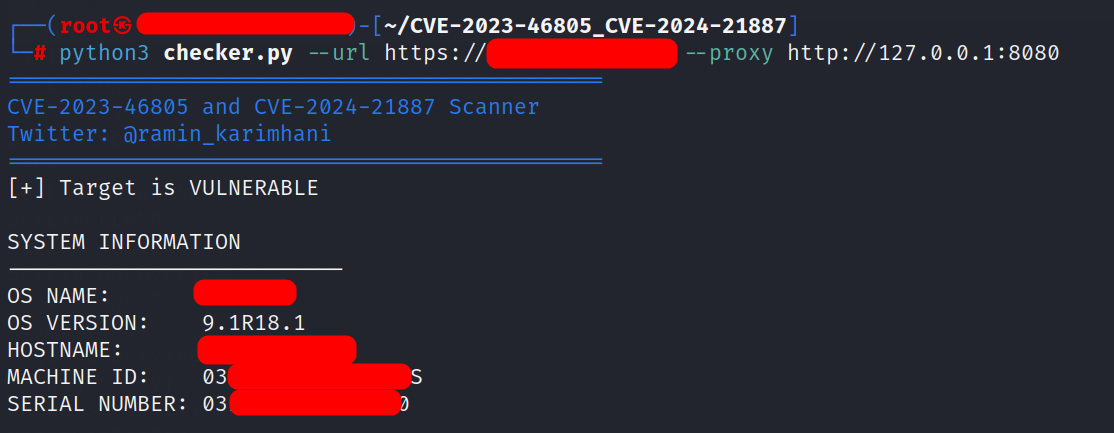
CVE-2023-46805_CVE-2024-21887 preview

CVE-2023-46805_CVE-2024-21887

GitHubraminkarimkhani1996/cve-2023-46805_cve-2024-21887

The script in this repository only checks whether the vulnerabilities specified in the Ivanti Connect Secure product exist.
authenticationexploitationpenetration-testing+2
52 years ago
wordpress-really-simple-security-authn-bypass-vulnerable-application preview

wordpress-really-simple-security-authn-bypass-vulnerable-application

GitHubm3ssap0/wordpress-really-simple-security-authn-bypass-vulnerable-application

WARNING: This is a vulnerable application to test the exploit for the Really Simple Security < 9.1.2 authentication bypass (CVE-2024-10924). Run it…
authenticationexploitationlabs-practice+3
81 year ago
CVE-2024-43468_mTLS_go preview

CVE-2024-43468_mTLS_go

GitHubnikallass/cve-2024-43468_mtls_go

CVE-2024-43468 SCCM SQL Injection Exploit (mTLS unextractable client cert from MacOS keychain version)

authenticationexploitationpenetration-testing+3
51 year ago
Previous123Next