
PowerPriv
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
authenticationexploitationlateral-movement+2
1257 years ago
g0ldengunsec/powerprivA Powershell implementation of PrivExchange designed to run under the current user's context
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
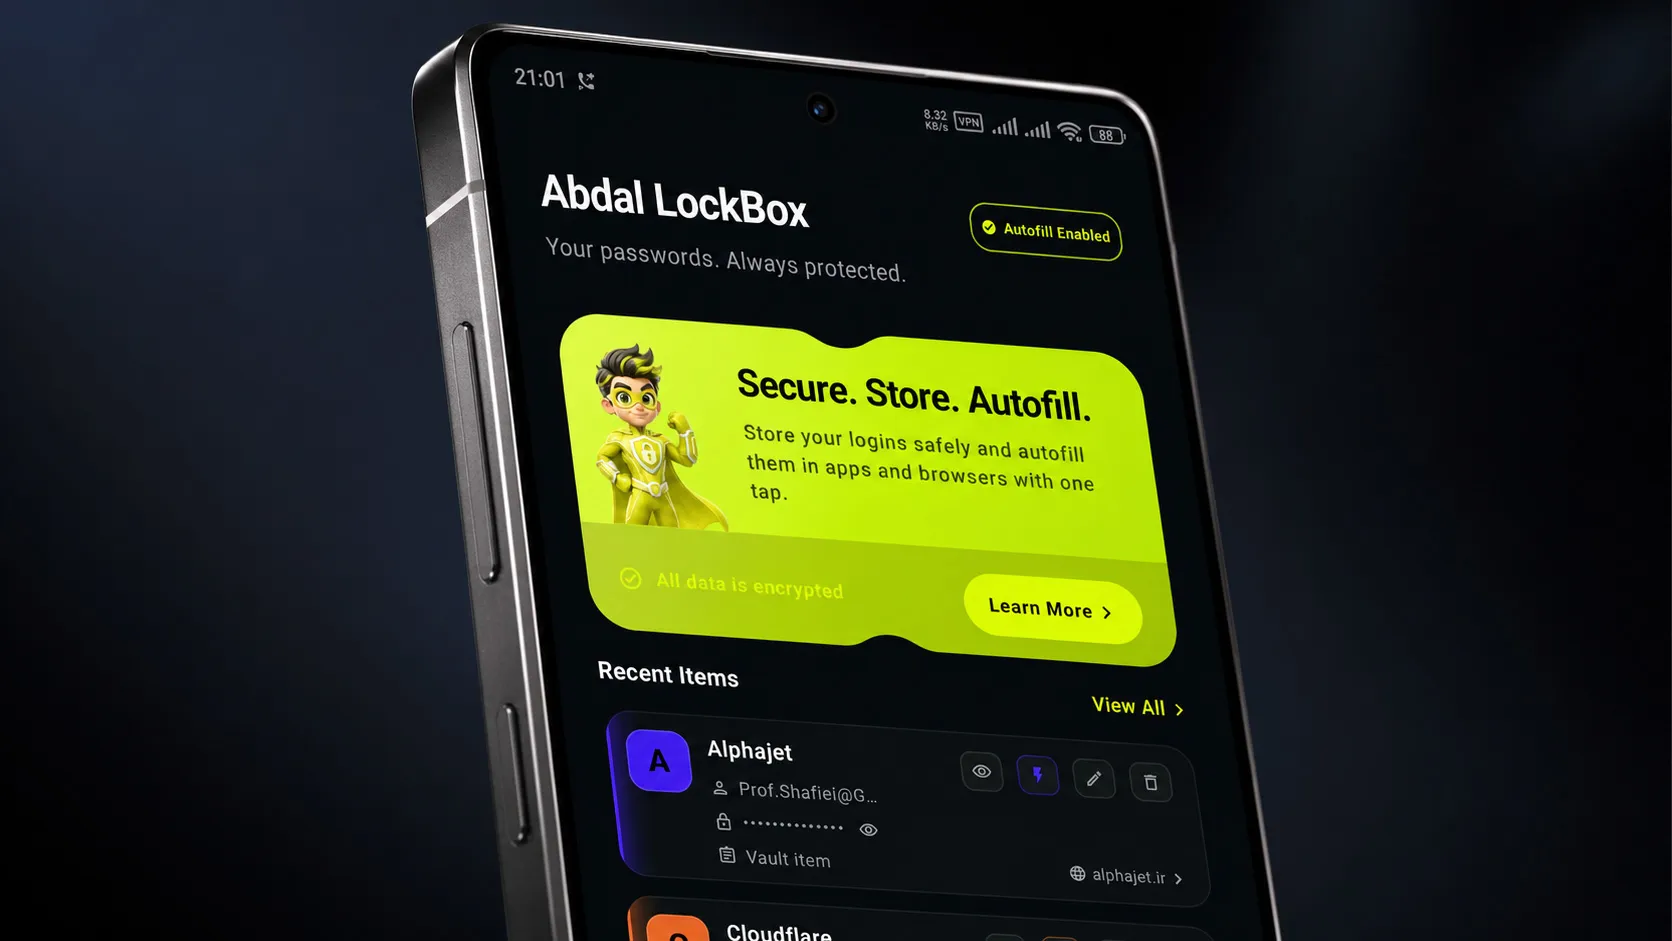
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
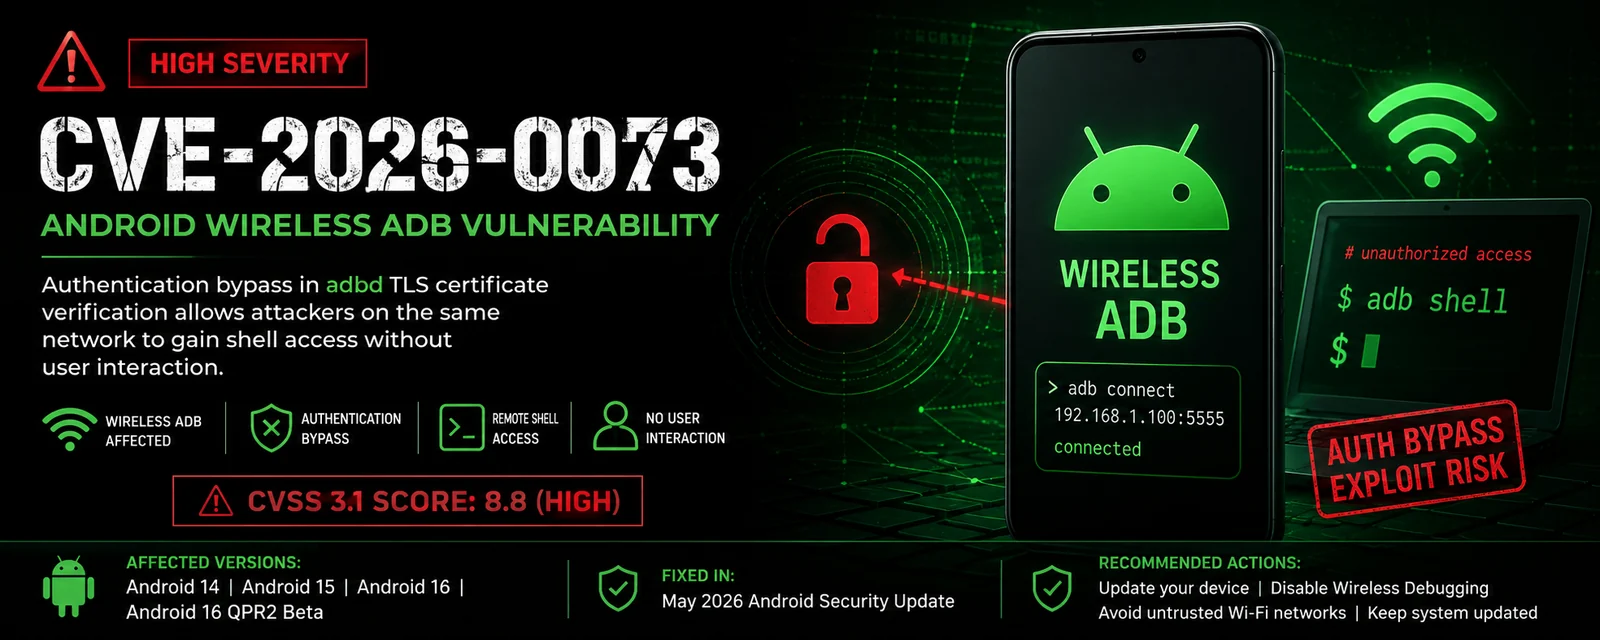 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…
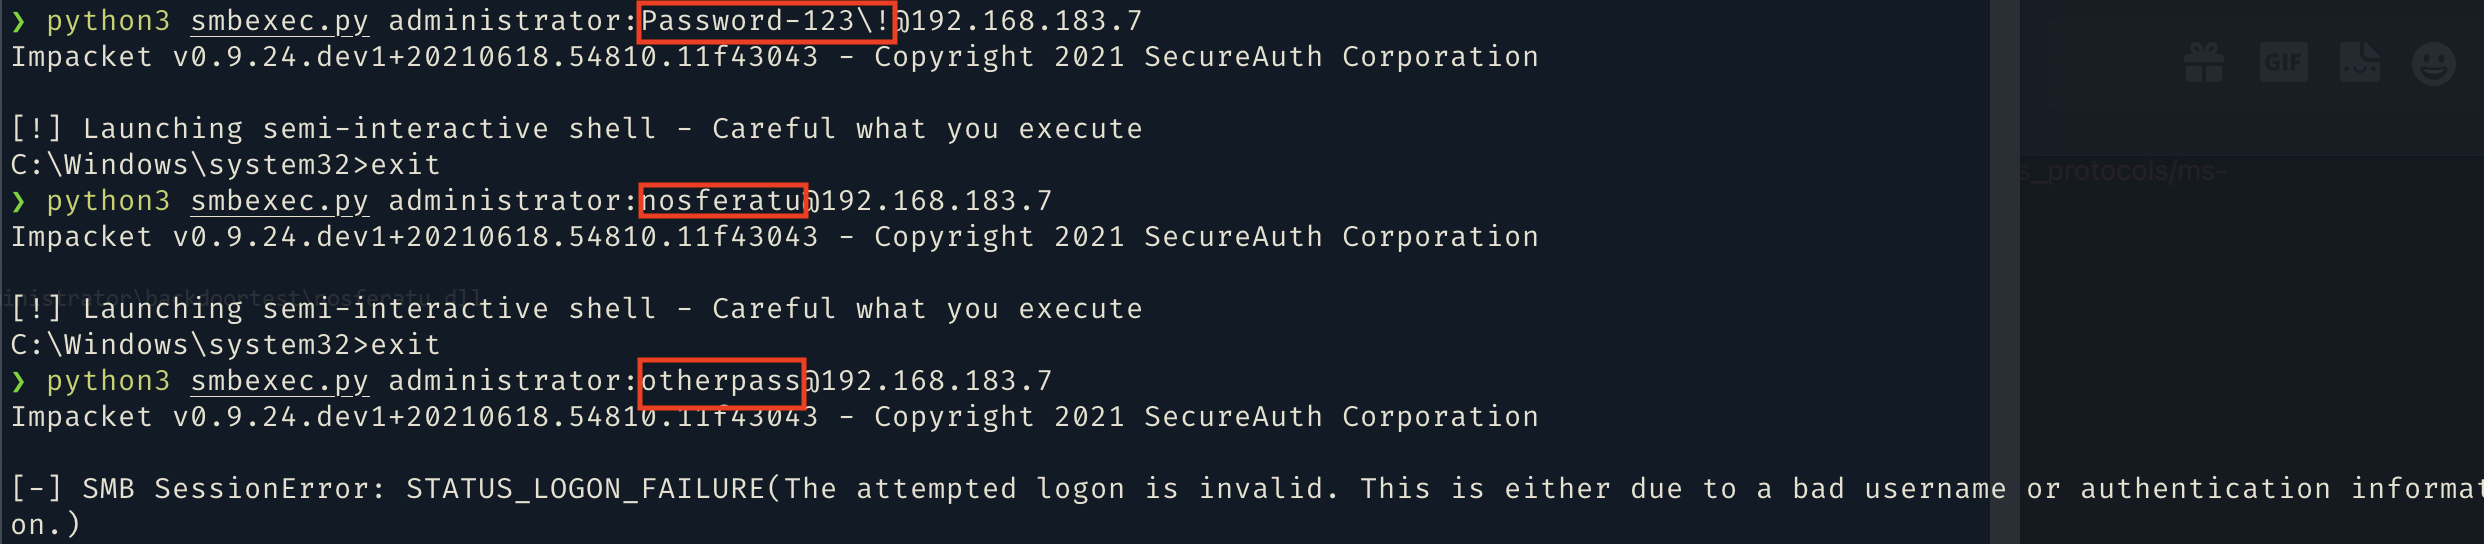 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 greenwolf/spray
A Password Spraying tool for Active Directory Credentials by Jacob Wilkin(Greenwolf)
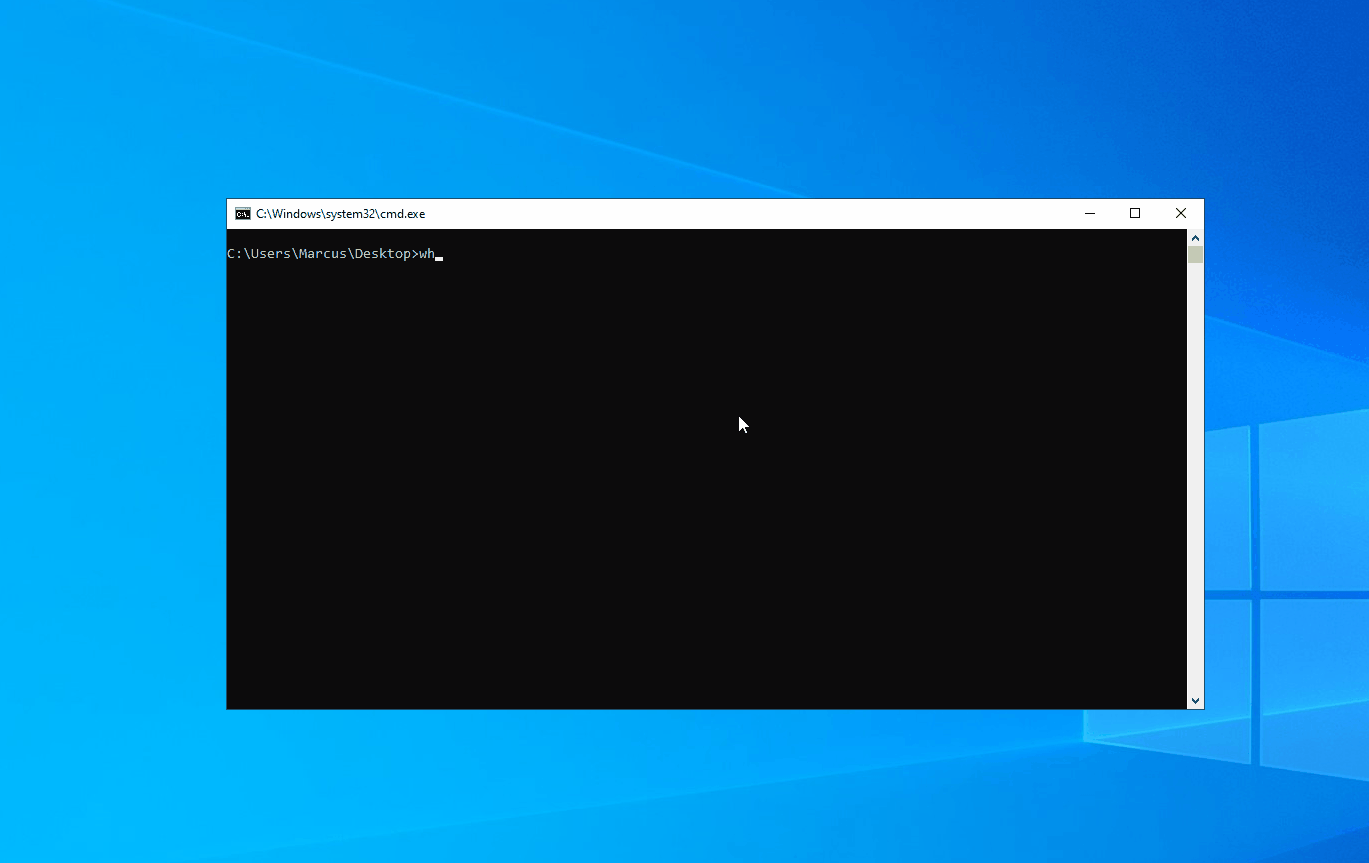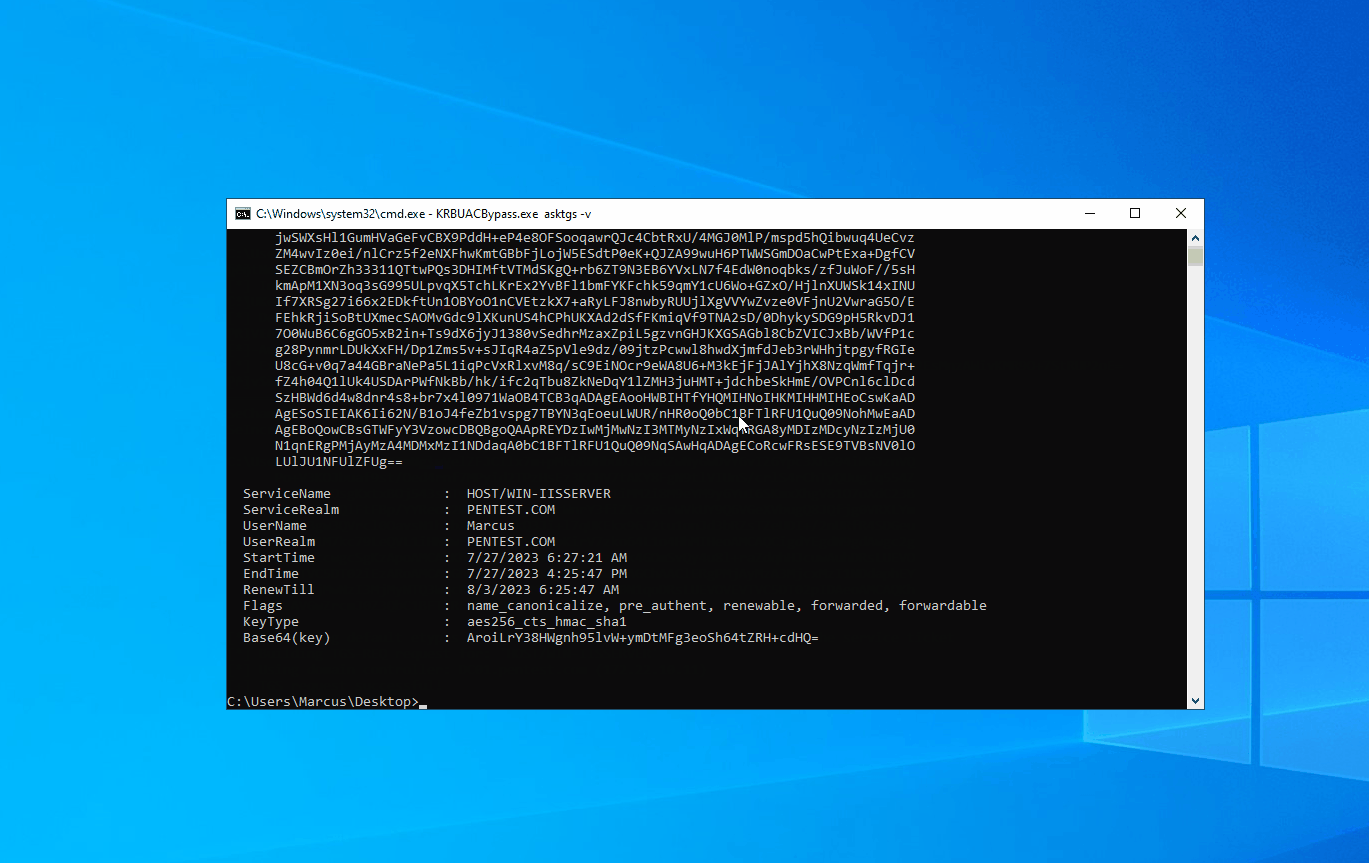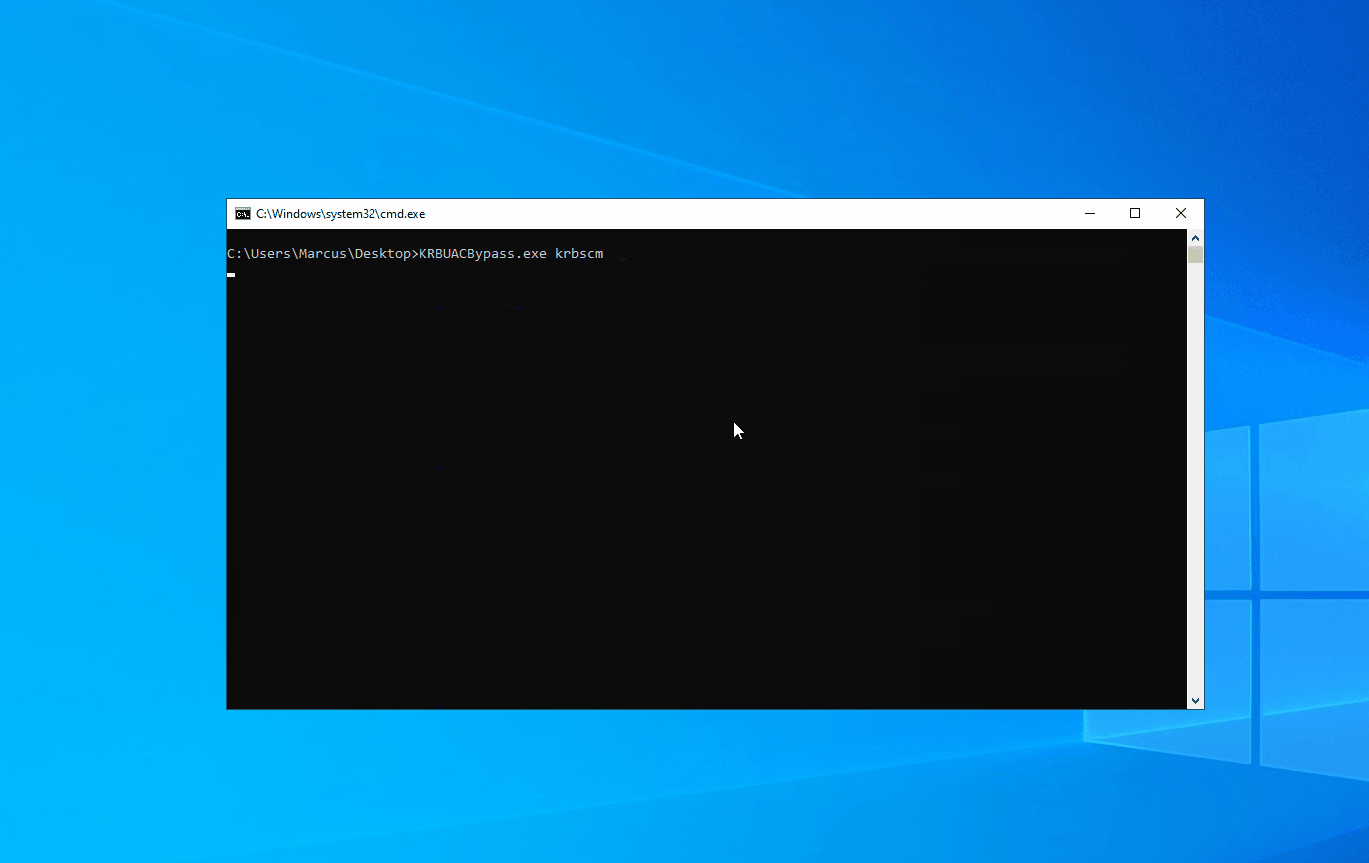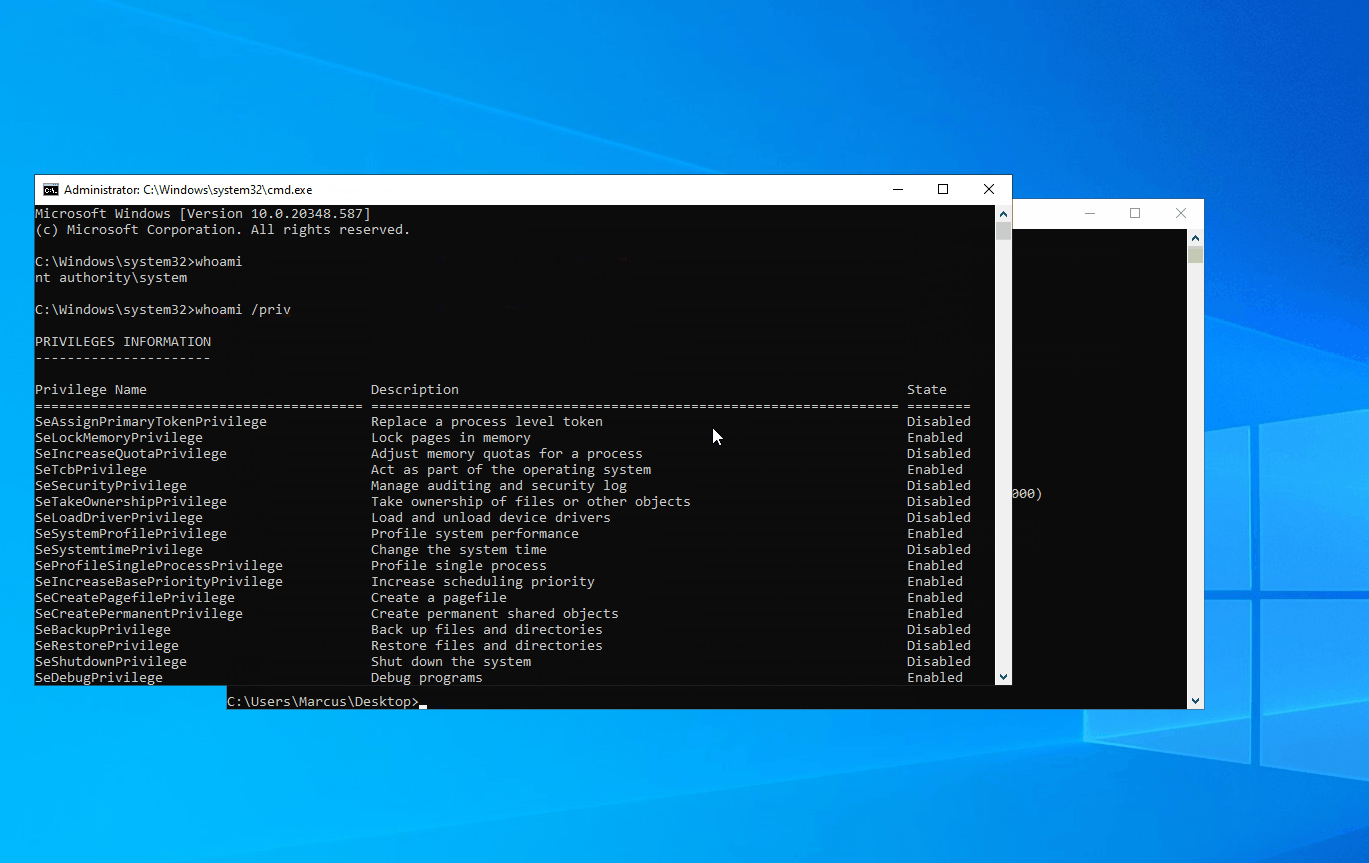 wh0amitz/krbuacbypass
Abuses Kerberos tickets to bypass Windows UAC and gain SYSTEM privileges by injecting a fake MachineID into service tickets, leveraging the tgtdeleg…
 secnigma/cve-2021-3560-polkit-privilege-esclation
Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…
 retrymp3/openbsd-privilege-escalation
Script that automates the process of escalating privileges on openbsd system (CVE-2019-19520) by exploiting the xlock binary and againing it's sgid…
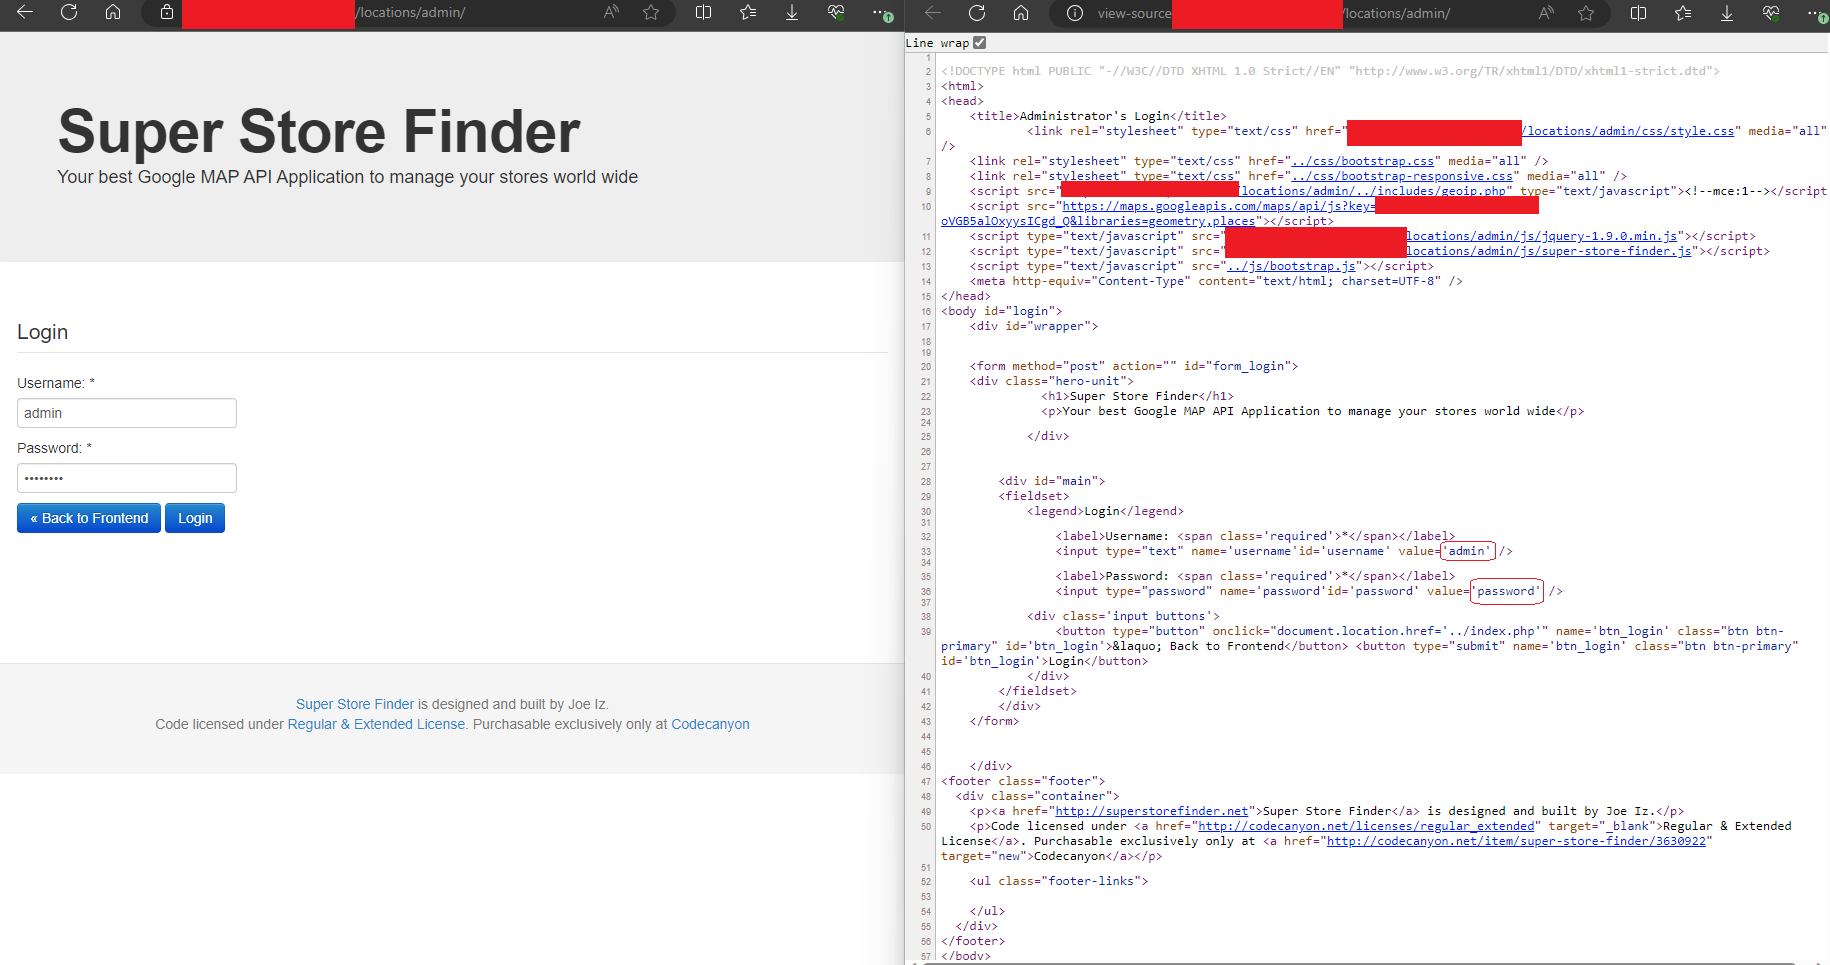 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 aakashtyal/session-persistence-after-enabling-2fa-cve-2025-60425
Detailed vulnerability report on Nagios Fusion session persistence after enabling 2FA, including CVE-2025-60425, affected versions, mitigation…
 ahamedyaseen03/cve-2025-60375
CVE-2025-60375 — Authentication bypass / incorrect access control in PerfexCRM < 3.3.1 (admin login)
 bypazs/cve-2023-26984
An issue in the password reset function of Peppermint v0.2.4 allows attackers to access the emails and passwords of the Tickets page via a crafted…
 wtn-arny/cve-2024-37085
Python exploit for CVE-2024-37085, an authentication bypass in domain-joined ESXi hypervisors, enabling unauthenticated shell upload and full…
 giovannidispoto/cve-2017-13872-patch
Exploit for CVE-2017-13872 that escalates privileges by changing the root password on vulnerable systems. Requires execution and provides new root…
 wtn-arny/vmware-esxi
CVE-2024-37085 unauthenticated shell upload to full administrator on domain-joined esxi hypervisors.
 notitssixtyn3in/cve-2025-4162028
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162028) in Copilot, enabling unauthorized account access via user ID…