

CVE-2023-46449
 sajaljat/cve-2023-46449
Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…
authenticationeducationmisconfiguration+3
sajaljat/cve-2023-46449Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 stefandorresteijn/cve-2021-39409
Admin account registration in Online Student Rate System
 julesbsz/cve-2024-10924
POC for CVE-2024-10924 written in Python
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.
 elastic/silhouette
Keep it secret, keep it safe
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
 7ragnarok7/cve-2026-19607
Documents CVE-2026-19607, an improper authentication flaw in Keycloak allowing username takeover via third-party identity broker registration, with…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.

 boltgolt/howdy
🛡️ Windows Hello™ style facial authentication for Linux
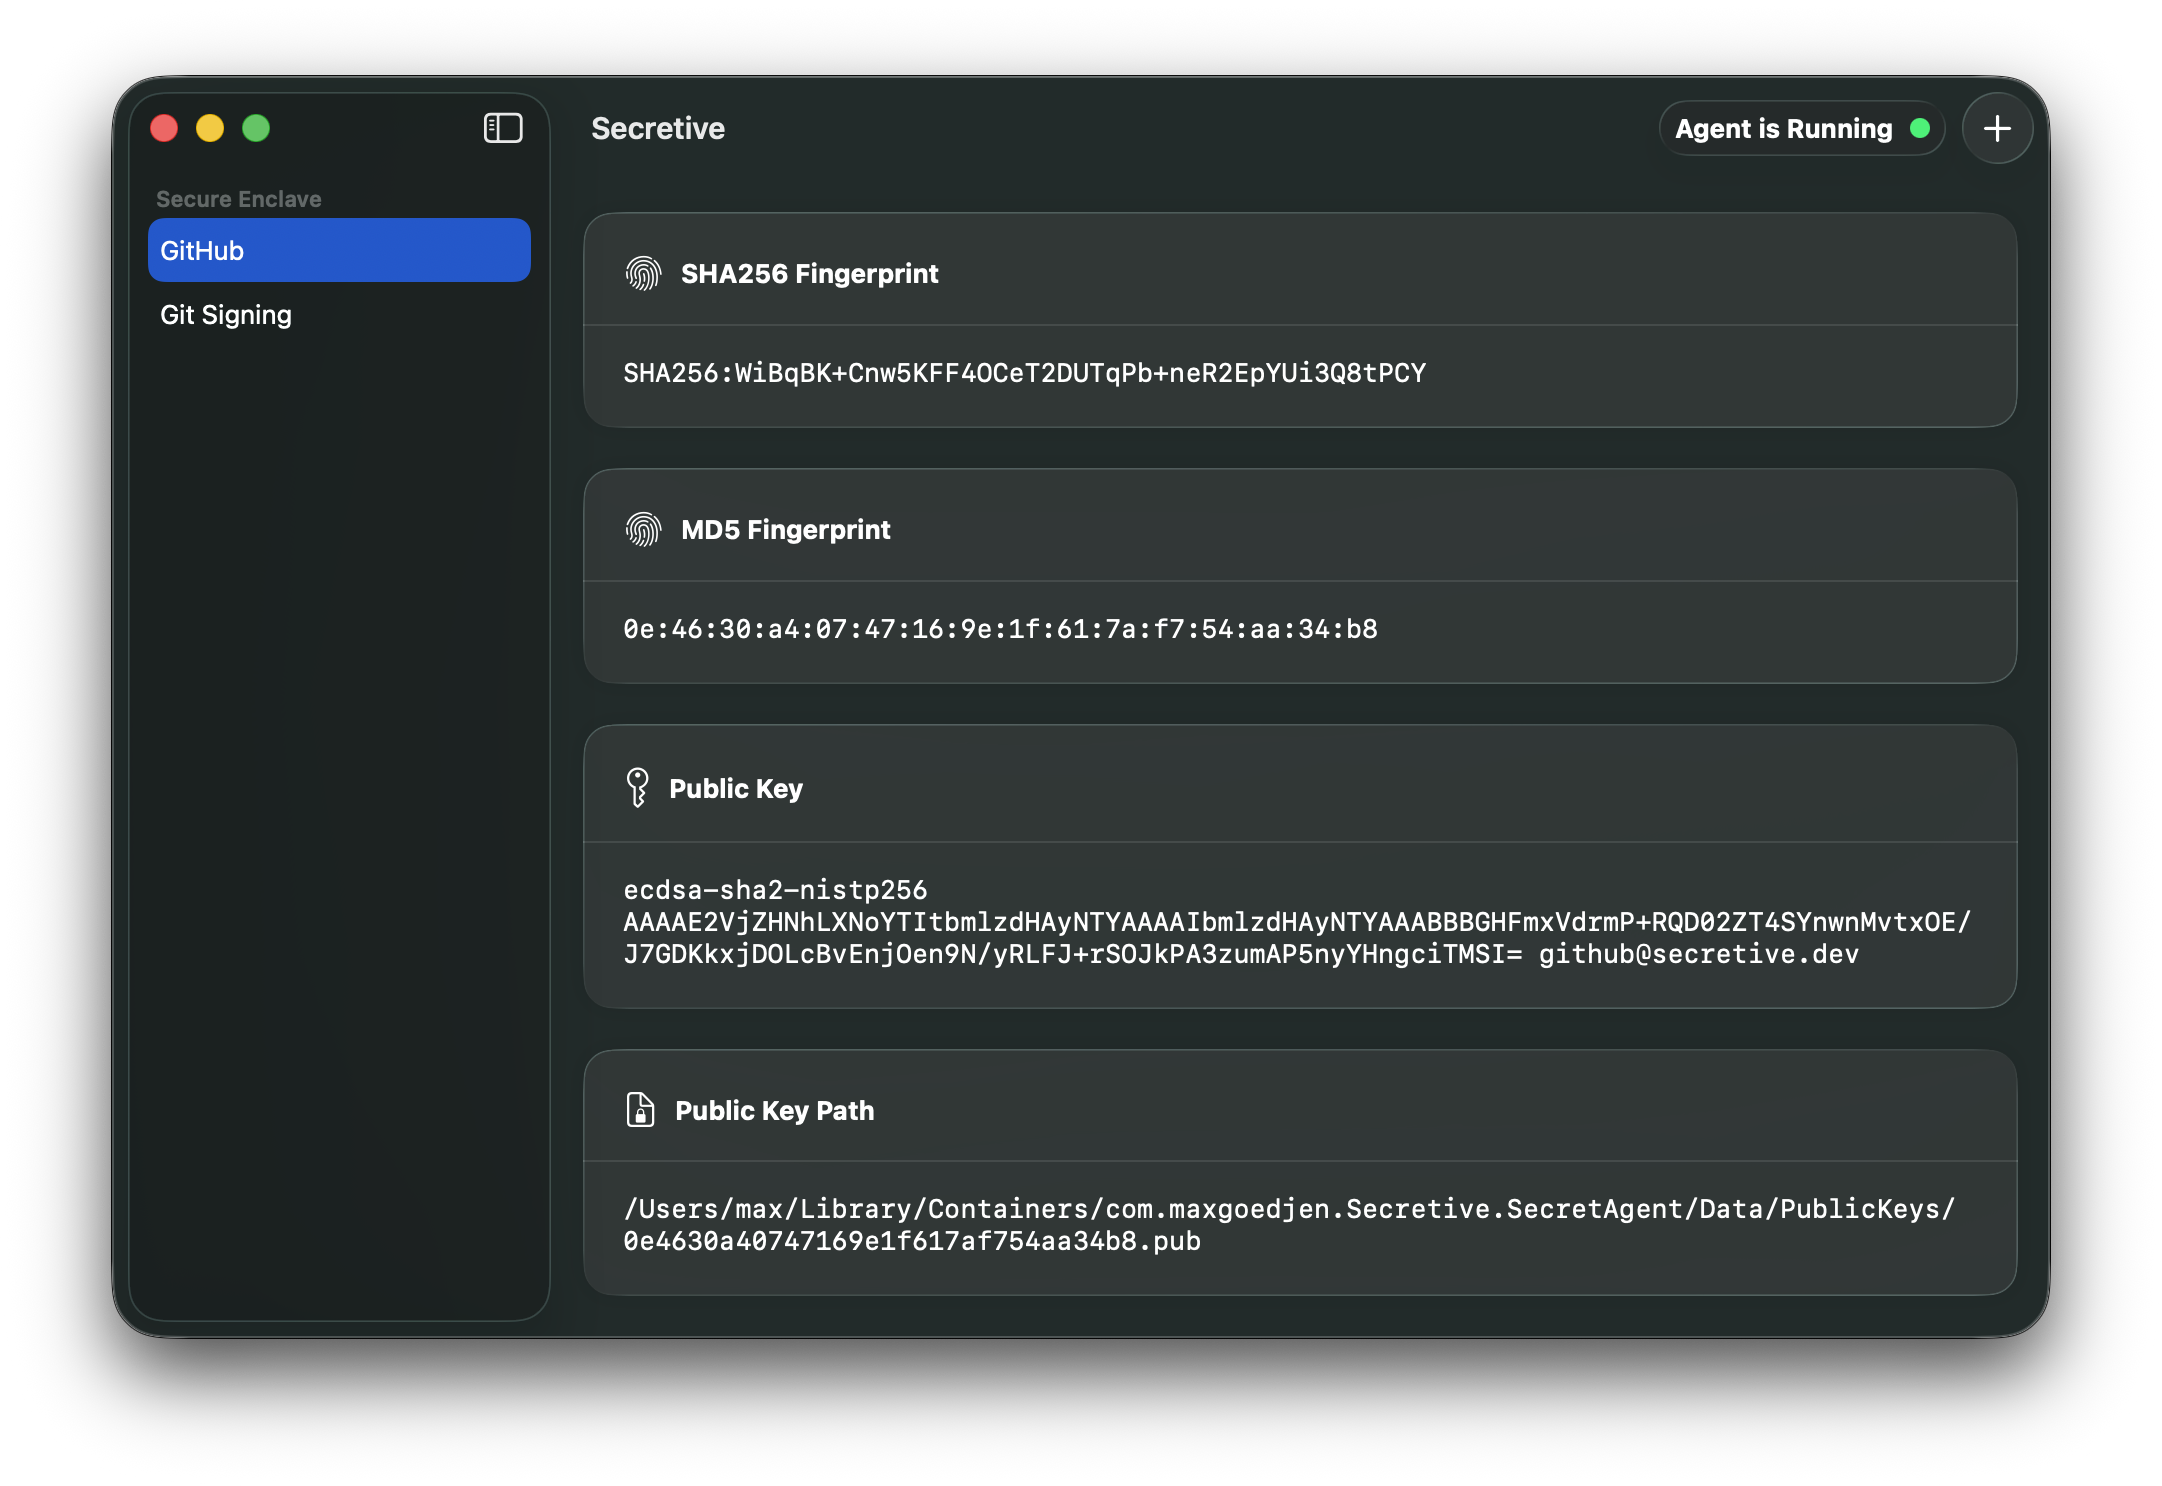 maxgoedjen/secretive
Protect your SSH keys with your Mac's Secure Enclave
 legrandin/pycryptodome
A self-contained cryptographic library for Python