
 7ragnarok7/cve-2026-19607
Documents CVE-2026-19607, an improper authentication flaw in Keycloak allowing username takeover via third-party identity broker registration, with proof-of-concept exploitation steps.

This repository documents the vulnerability details and an exploit for CVE-2026-19607, discovered and responsibly reported by Anurag Mondal (7Ragnarok7) on 8th August, 2026.
A flaw was discovered in Keycloak (versions <= 26.7.14, 26.4.16, and 26.6.7) in which an attacker can register using an email address that matches the username of any existing user when coming from a third-party login broker / IDP.
The above behaviour will allow the attacker to take over the username of a victim account if the username is set as an email ID, and lock out the associated user from their account. All authentication attempts using the victim's username will fail.
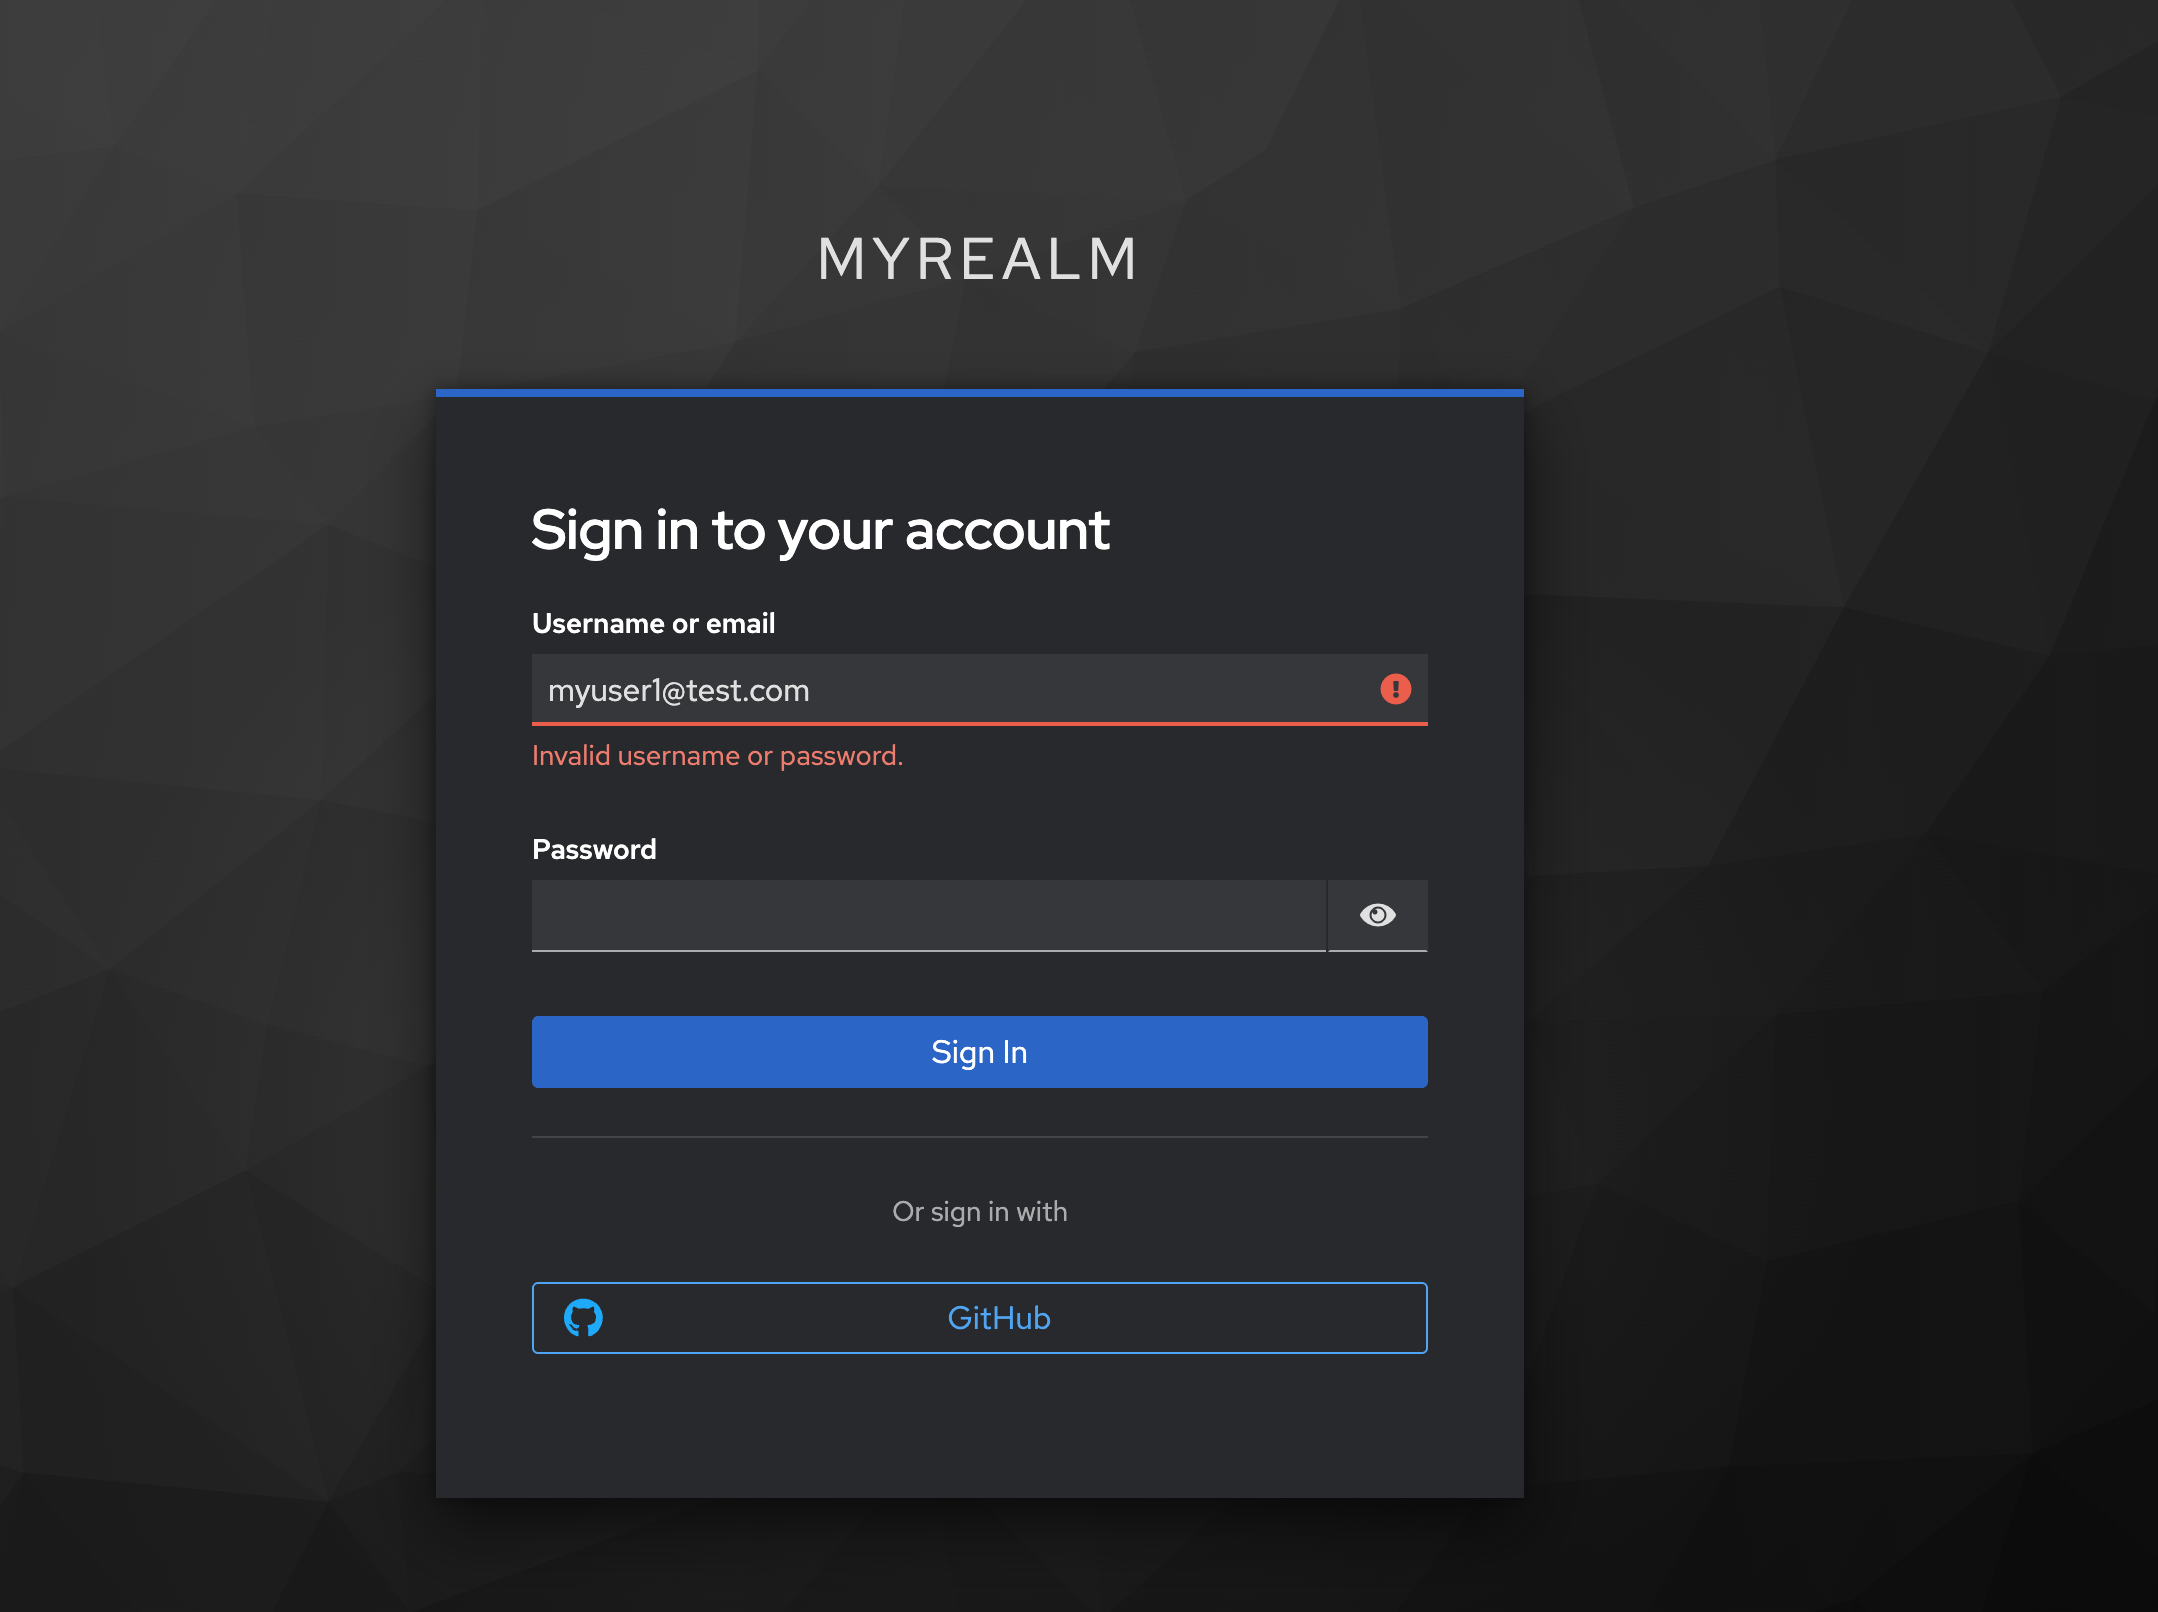
The Following is a proof of concept video which demonstrates the vulnerability details along with exploitation steps:






