CVE-2024-4573-Mitigation-Script

Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…

Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…

Python helper to scan Fortinet web management for CVE-2026-24858 SSO authentication bypass and optionally send explicit payloads with user…

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths

Penetration tests guide based on OWASP including test cases, resources and examples.

Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset

Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…

Python-based detection artifact generator for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520,…

A Nuclei template to detect CVE-2025-29927 the Next.js authentication bypass vulnerability

Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)

Banner Web Tailor and Banner Enterprise Identity Services Vulnerability Disclosure

Detection artifact generator for Check Point VPN IKEv1 certificate-authentication bypass (CVE-2026-50751). Validates gateway exposure and…

Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…

Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…

Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.

PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…

Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…

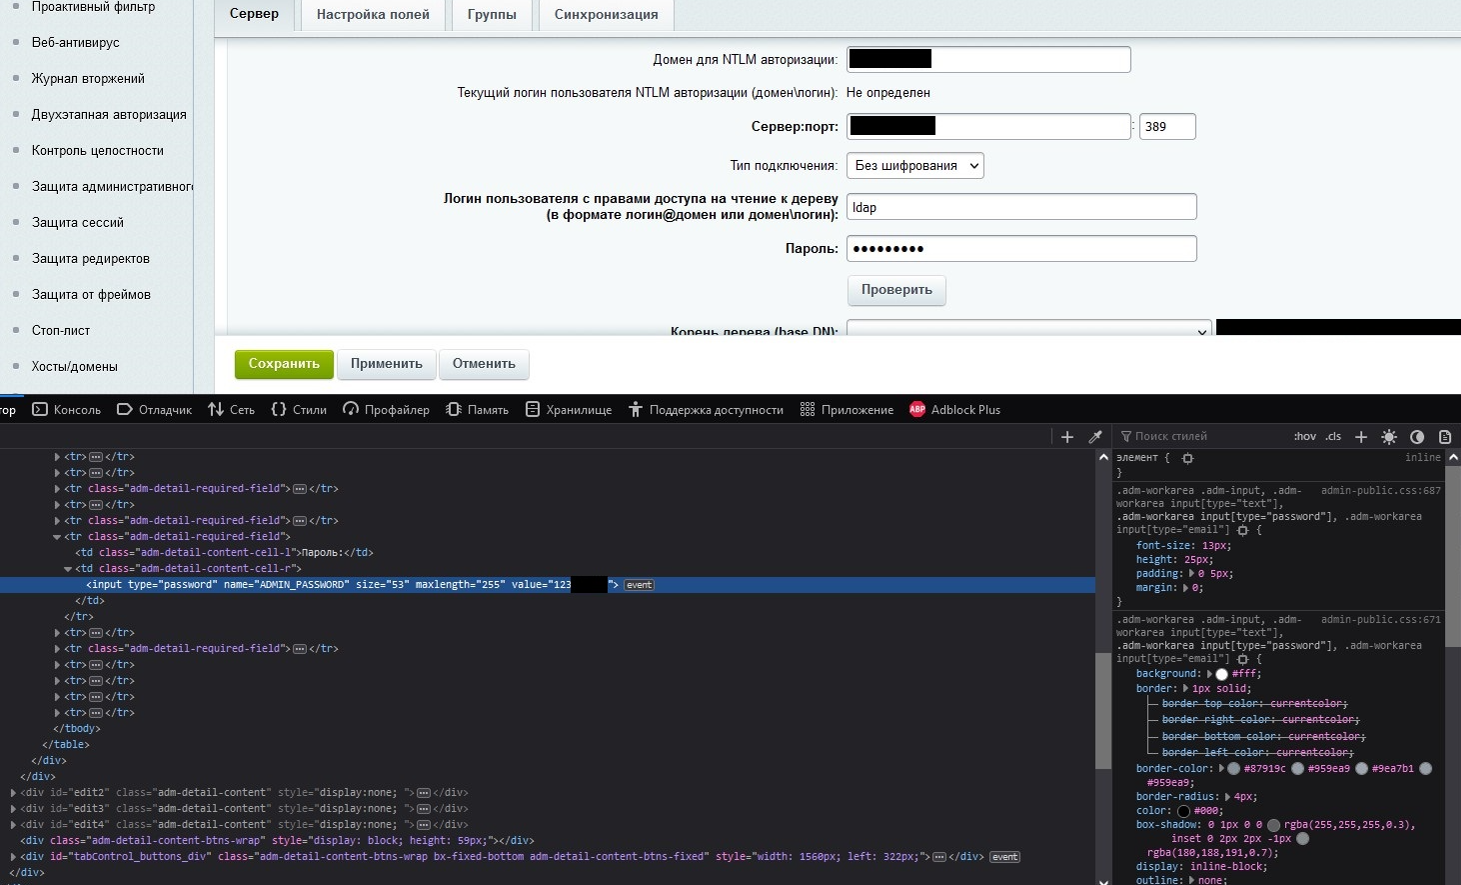
Bitrix Vulnerability CVE-2022-43959

check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949