
nextjs-vulnerable-app
 strobes-security/nextjs-vulnerable-app
CVE-2025-29927 lab
authenticationeducationlabs-practice+3
6
strobes-security/nextjs-vulnerable-appCVE-2025-29927 lab
 horkimhab/cve-2026-psa-2026-00043-1
Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…

 k3ystr0k3r/cve-2025-57819
CVE-2025-57819 - FreePBX Unauthenticated Remote Code Execution (RCE)

 saladin0x1/cve-2025-53770
Proof-of-concept exploit toolkit for SharePoint ToolPane RCE (CVE-2025-53770) with scanner, payload analysis, and multiple exploitation methods for…
 biitts/cve-2026-46490-samlify-saml-attribute-injection
CVE-2026-46490 — samlify <2.13.0 SAML AttributeValue XML injection -> signed-assertion privilege escalation. Self-contained PoC, verified e2e.
 hsw109/cve-2018-10933
Education purpose for CVE-2018-10933
 aykhan32/cve-2026-51788
Detailed CVE-2026-51788 advisory for a DoS vulnerability in cleverange_auth v0.1.10, with technical analysis, CVSS scoring, and mitigation guidance…
 ademto/wordpress-cve-2024-10924-pentest
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation…
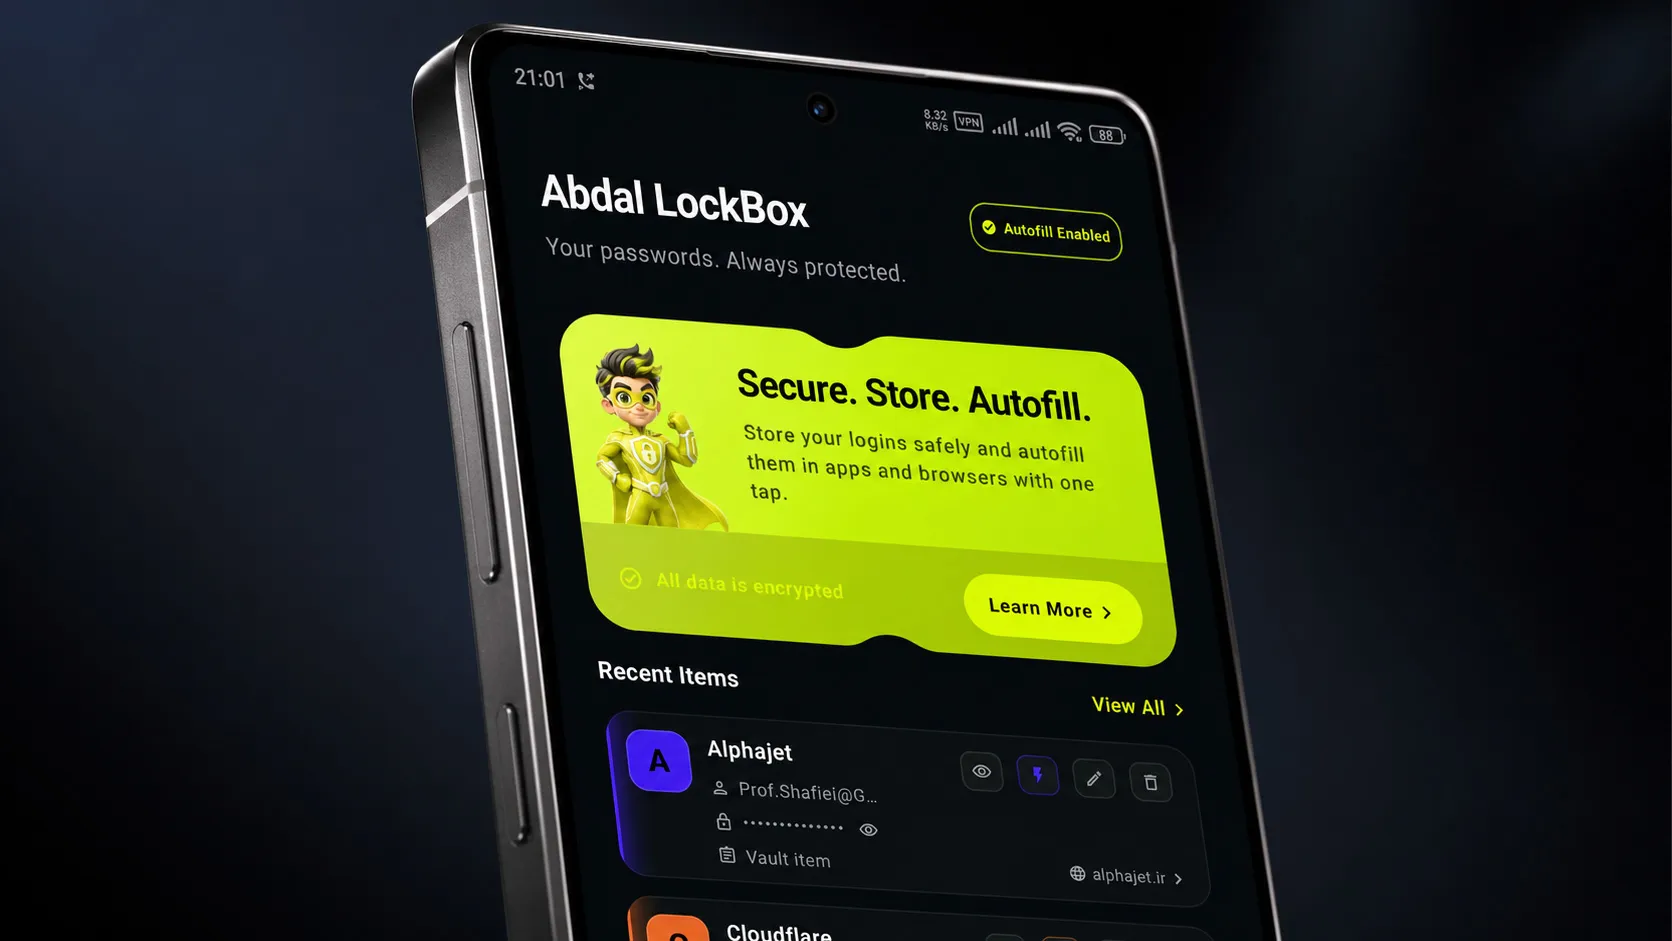
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
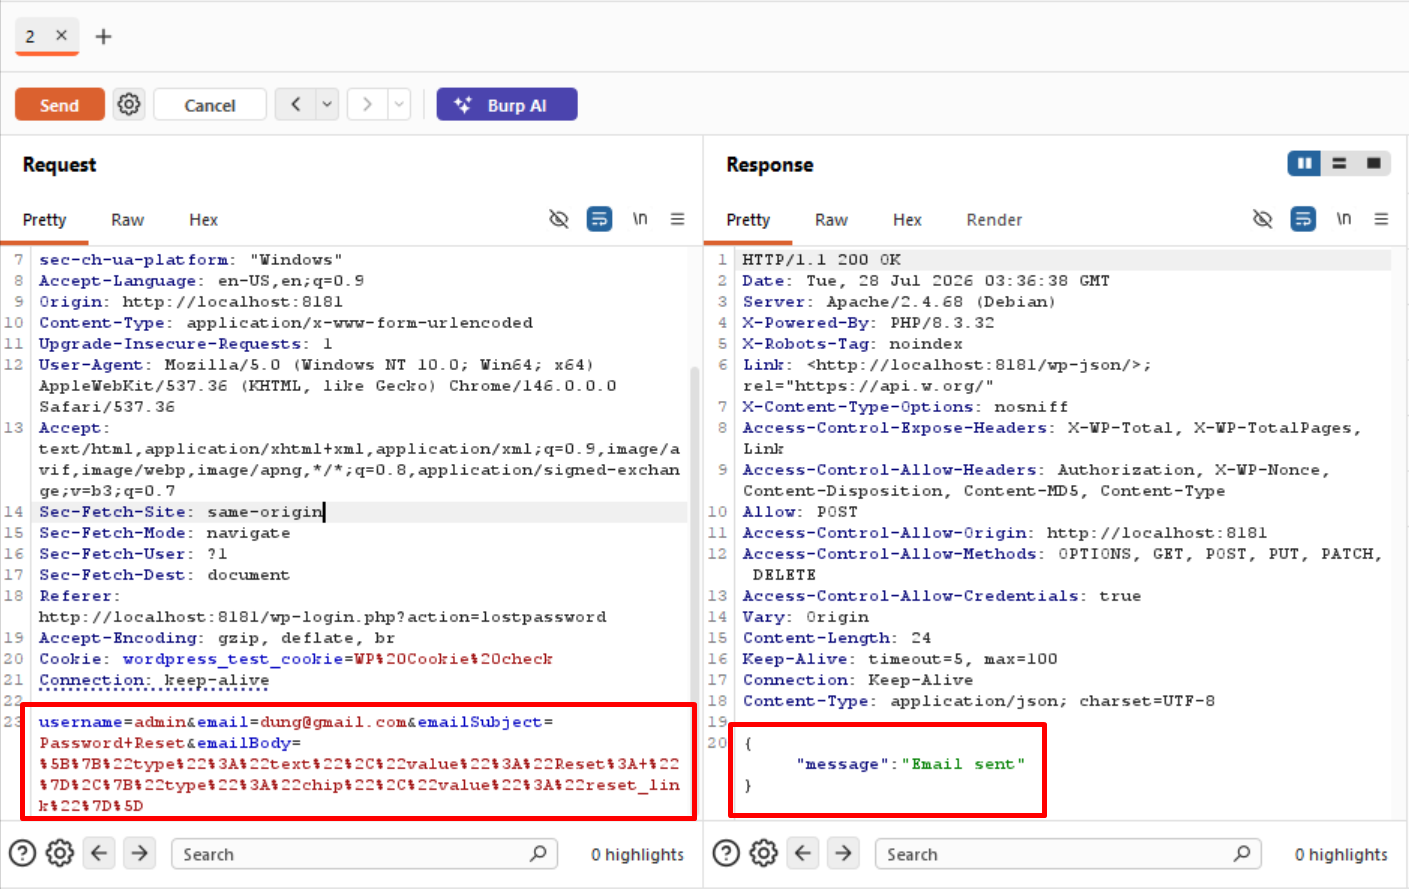 dungsocool/cve-2026-8206
CVE-2026-8206: Kirki Customizer Framework - Unauthenticated Account Takeover (CVSS 9.8)
 biitts/cve-2026-56782-gorse-auth-bypass
CVE-2026-56782 — Gorse <0.5.10 unauthenticated DB dump/restore (admin_api_key fail-open). Lab + PoC, verified e2e.

 0xdaeras/flowise-cve-2025-58434-chain-59528
FlowiseAI CVE-2025-58434 & CVE-2025-59528 exploit PoC, demonstrating unauthenticated ATO via reset token leakage, followed by authenticated RCE.…
 flaviupopescu/cve-2022-28986
A Insecure direct object references (IDOR) vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 yucaerin/cve-2025-4322
Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
 swapnildeshpande/cve-2025-29927-lab
Reproduction lab for CVE-2025-29927 — Next.js middleware authorization bypass (CVSS 9.1)