
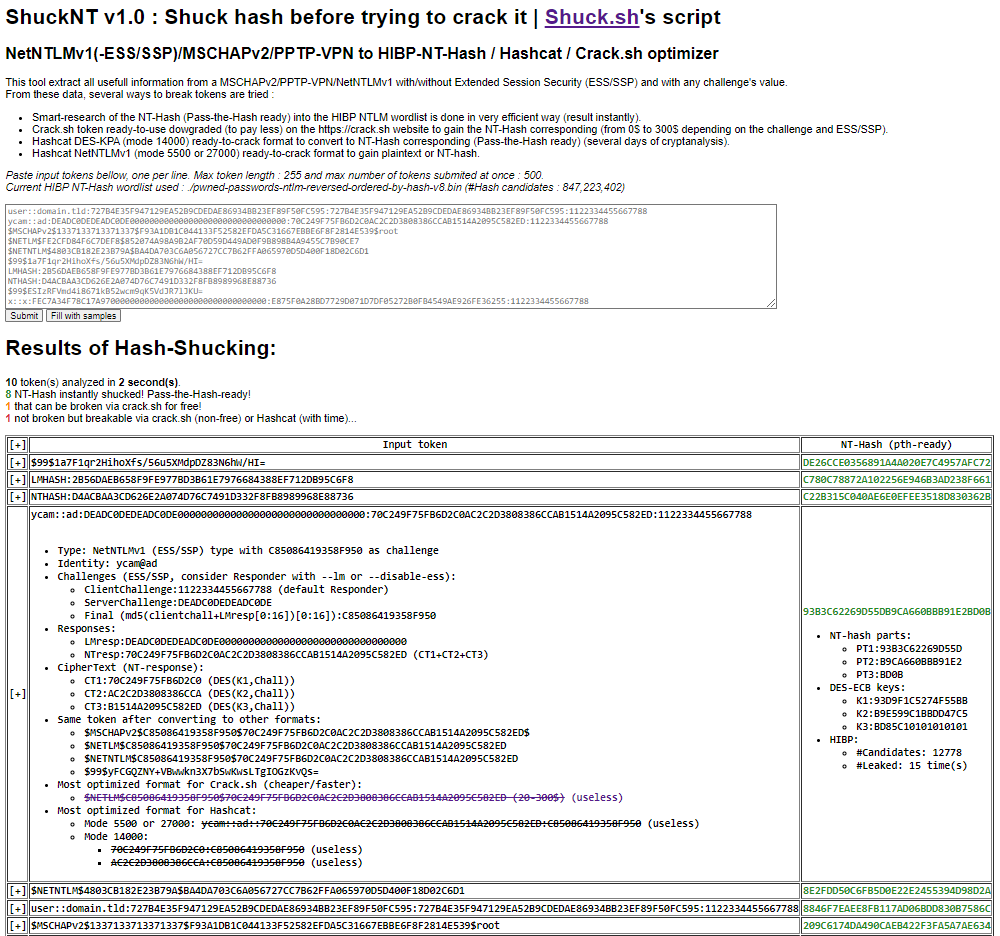
ShuckNT
 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
authenticationcryptographyhash-analysis+3
78
yanncam/shuckntShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 rickgeex/proxylogon
ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the…
 omgrant/ft9201-libfprint
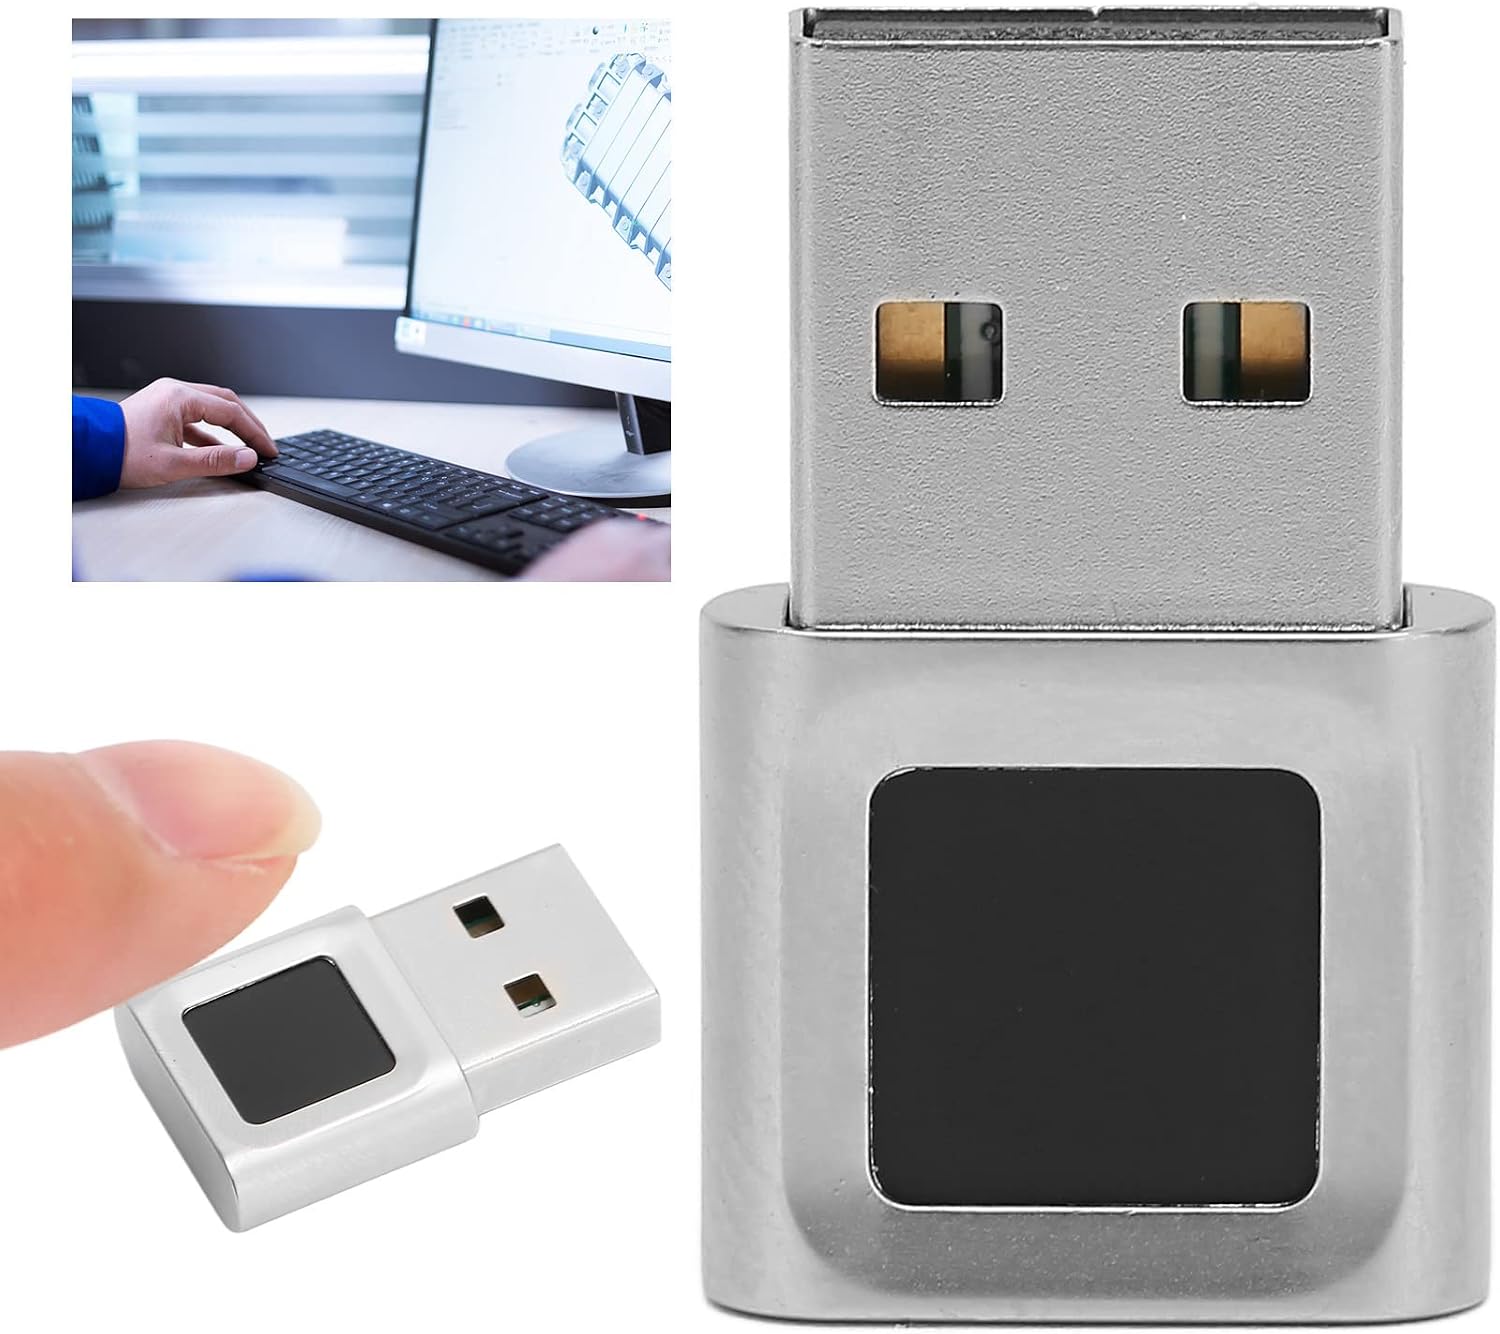
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
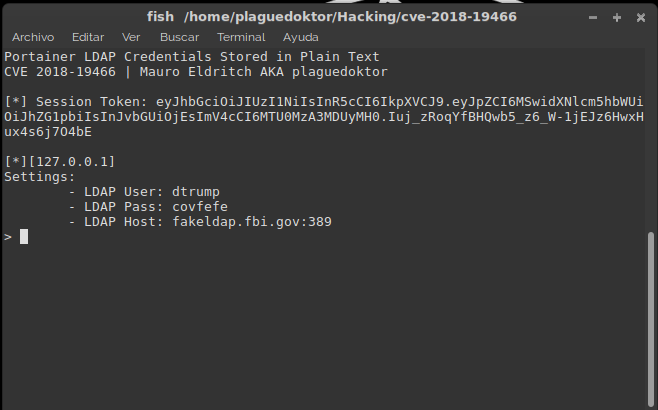 mauroeldritch/lempo
LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
 absholi7ly/cve-2026-24858-forticloud-sso-authentication-bypass
CVE-2026-24858 FortiCloud Single Sign On (SSO) a factory default enabled feature once you register any FortiGate/FortiManager/FortiAnalyzer …
 exfil0/cve-2025-59718-poc
Fortinet announced two closely related authentication‑bypass vulnerabilities on 9 December 2025. Both flaws involve improper verification of…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 gotr00t0day/cve-2024-4040
Exploit for CrushFTP SSTI vulnerability (CVE-2024-4040) enabling unauthenticated file read, authentication bypass, and remote code execution on…
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 und3sc0n0c1d0/cve-2022-40684
Utilities for exploiting vulnerability CVE-2022-40684 (FortiOS / FortiProxy / FortiSwitchManager - Authentication bypass on administrative interface).
 thaysolis/cve-2024-29296
CVE-2024-29296 - User enumeration on Portainer CE - 2.19.4
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 captain-v-hook/poc-for-cve-2021-38540-
Missing Authentication on Critical component CVE-2021-38540
 notareaperbutdr34p3r/kerberos_cve-2022-33679
Python exploit for CVE-2022-33679 targeting Kerberos authentication to perform privilege escalation on Windows domain controllers via RC4 session key…