

CVE-2026-34910-PoC
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
api-security-testingauthenticationexploitation+3
14
boreas37/cve-2026-34910-pocCVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 cappricio-securities/cve-2020-27838
CVE-2020-27838 - KeyCloak - Information Exposure
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 cappricio-securities/cve-2023-27524
Apache Superset - Authentication Bypass
 cappricio-securities/cve-2022-21500
Oracle E-Business Suite <=12.2 - Authentication Bypass
 cappricio-securities/cve-2023-5089
Defender Security < 4.1.0 - Protection Bypass (Hidden Login Page)
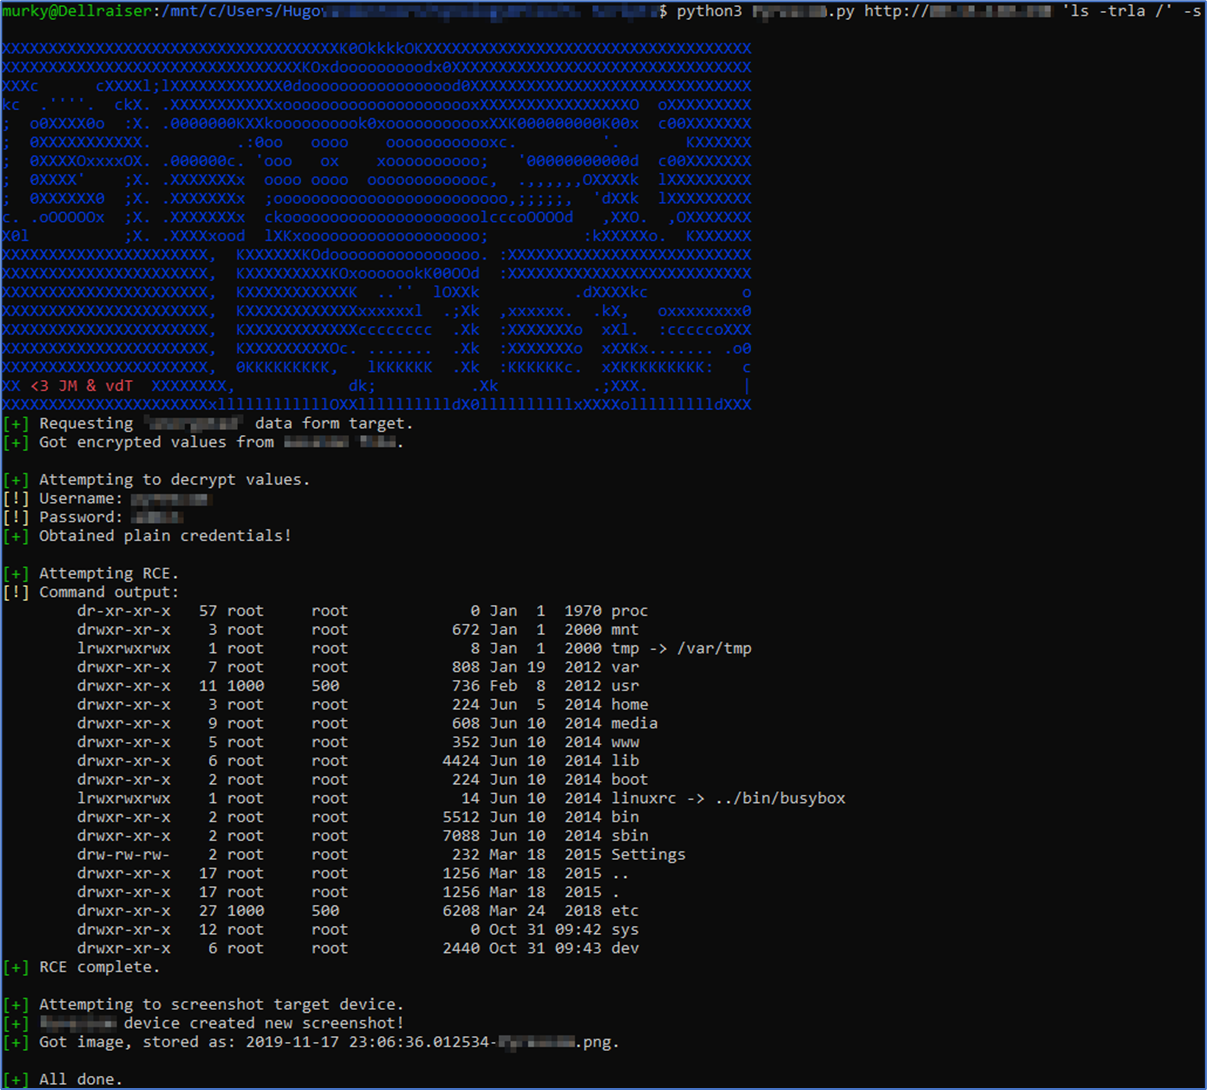 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 mayyhem/maestro
Abusing Azure services over C2
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 lutfifakee-project/cve-2026-41940
cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
 havocframework/modules
Modules used by the Havoc Framework
 0xf4n9x/cve-2022-46169
CVE-2022-46169 Cacti remote_agent.php Unauthenticated Command Injection.
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
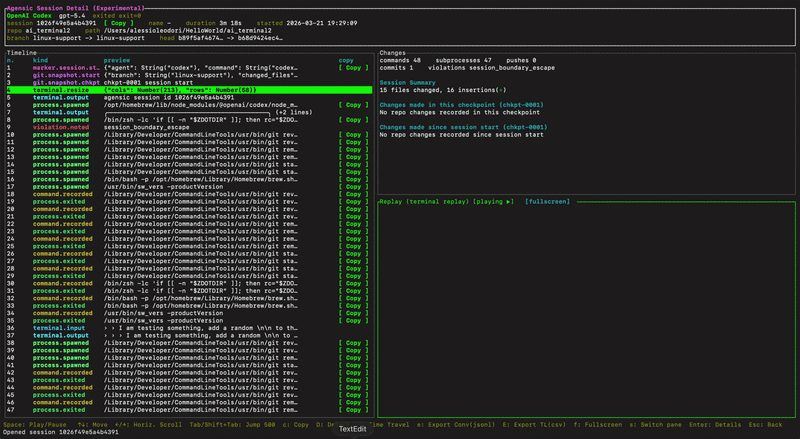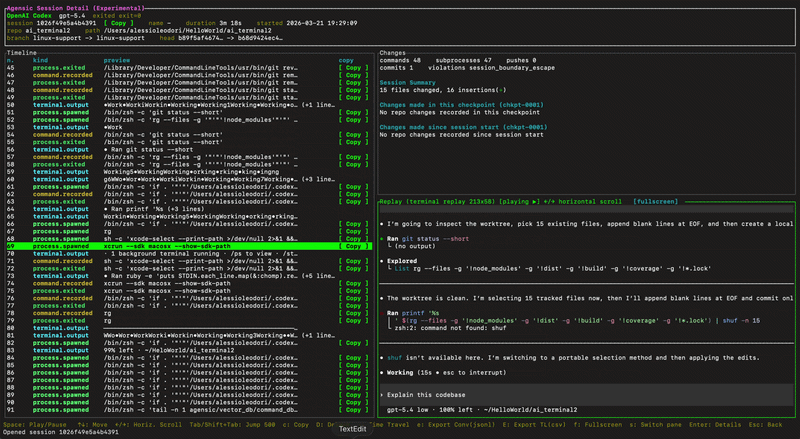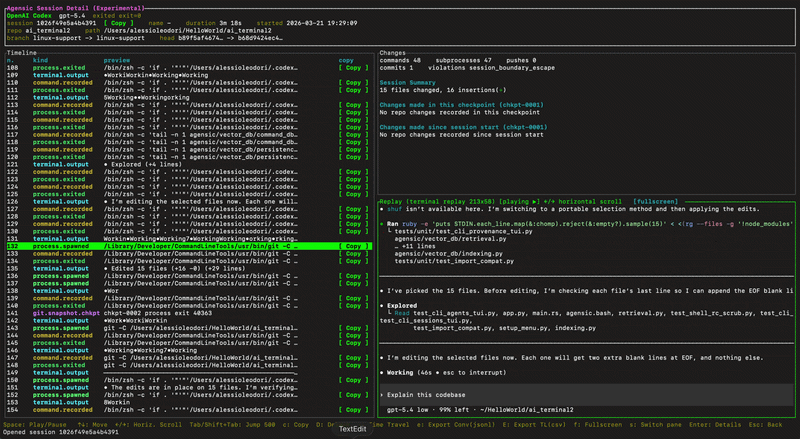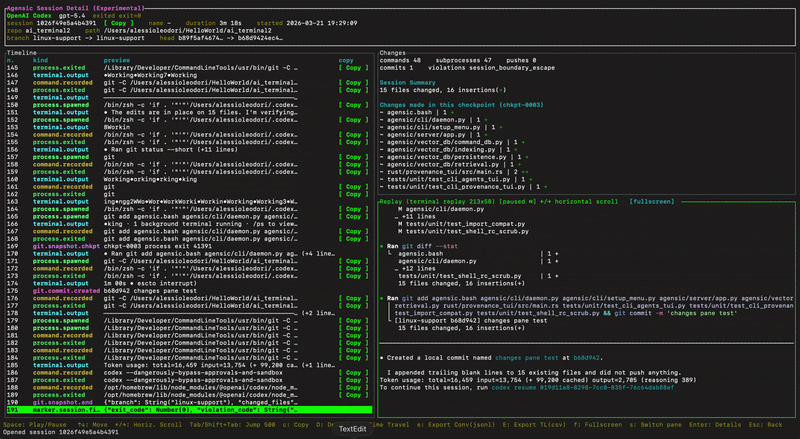 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…